cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

Weak eMudhra Certificate Keys Prompt Browser Blocks and Software Updates

Eight eMudhra intermediate certificates had weak private keys that could be recovered by testing 256 values, enabling forged trusted certificates. eMudhra revoked them, and browser and software vendors issued protections and updates; misuse has not been evidenced.

Oct 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

PHP schedules emergency patches for two critical flaws after details reportedly leak

PHP plans to release patches October 21 for two critical flaws. Researchers say they are remote code execution vulnerabilities affecting PHP versions 5–8, but PHP has not disclosed technical details; no in-the-wild exploitation has been observed.

Oct 20, 2026
Vulnerability & Exploit · unit42.paloaltonetworks.com

Ransomware Operators Exploit PAN-OS GlobalProtect Authentication Bypass

Unit 42 reports active exploitation of PAN-OS CVE-2026-0257 by ransomware operators, with some attackers pivoting from VPN gateways to virtualization systems. It advises checking GlobalProtect logs and applying mitigations or upgrades.

Oct 19, 2026
Vulnerability & Exploit · securityweek.com

Siemens Software Center DLL Vulnerability Exploited in ClickFix Campaign

Attackers exploited a Siemens Software Center DLL-loading flaw in a ClickFix campaign. Siemens released version 4.0.9.8 to fix it and says the malicious package did not come through its distribution channels.

Oct 19, 2026
Vulnerability & Exploit · rapid7.com

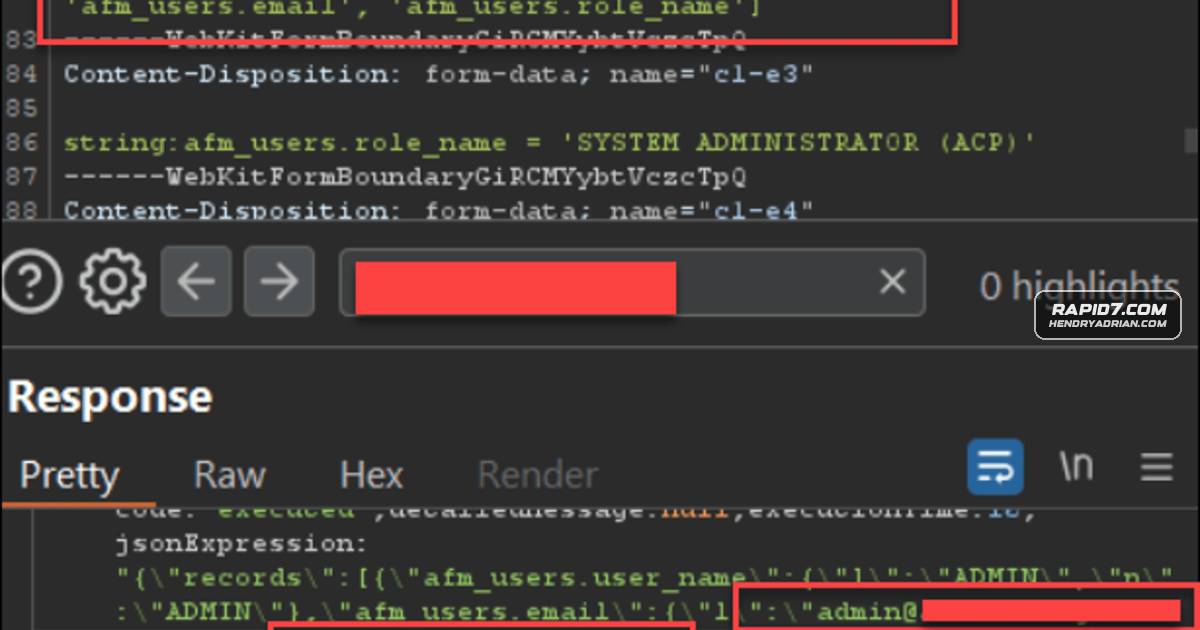
Rapid7 Details Three Eptura Archibus Flaws Enabling Authentication Bypass, Database Reads and RCE

Rapid7 disclosed three Eptura Archibus flaws: a DWR authentication bypass, database read access and an unrestricted upload that can enable remote code execution. Archibus 2025.02 or later is recommended.

Oct 19, 2026
Vulnerability & Exploit · securityweek.com

Drupal Patches Two Critical Core Flaws With Potential Unauthenticated RCE Paths

Drupal patched five vulnerabilities, including two critical flaws with potential unauthenticated RCE paths through contributed modules. No in-the-wild exploitation was reported; users should update affected Drupal and module versions.

Oct 19, 2026
Vulnerability & Exploit · rapid7.com

Critical BeyondTrust Remote Support Authentication Bypass Exploited in the Wild

BeyondTrust confirmed two Remote Support compromises involving CVE-2026-102764, an authentication bypass affecting versions 26.2.3 and earlier. A patch is available; organizations should patch urgently and investigate for prior compromise.

Oct 19, 2026
Vulnerability & Exploit · securityweek.com

Plex Exploit Chain Used Against Vulnerable Servers a Day After Disclosure

Attackers used the publicly released Plex2Shell exploit against a vulnerable honeypot a day after disclosure, running code without valid credentials and dropping an XMRig miner and proxy software. Plex had already shipped fixes and urged users to upgrade.

Oct 19, 2026
Vulnerability & Exploit · thehackernews.com

Unpatched Broadcom Wi-Fi Flaw Allows Root Code Execution on Routers Within Radio Range

Researcher Quentin Kaiser says a Broadcom WPS flaw lets attackers within Wi-Fi range read router memory or run code as root without credentials. Affected routers have no deployed fix; millions of devices may be vulnerable, though some listed models are unconfirmed.

Oct 19, 2026
Vulnerability & Exploit · socradar.io

Drupal Patches Two Critical RCE Vulnerabilities in Core and Entity List

Drupal patched two critical RCE flaws affecting core Field UI and the Entity List module. Exploitation requires vulnerable functionality exposed through integrations; no in-the-wild exploitation was confirmed as of October 19, 2026.

Oct 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

F5 Releases Out-of-Band Patches for Critical NGINX Vulnerabilities

F5 issued out-of-band patches for three critical NGINX vulnerabilities that could enable denial-of-service or code execution under non-default configurations. The article also outlines mitigations; F5 has not flagged the flaws as exploited in the wild.

Oct 19, 2026
Vulnerability & Exploit · cyfirma.com

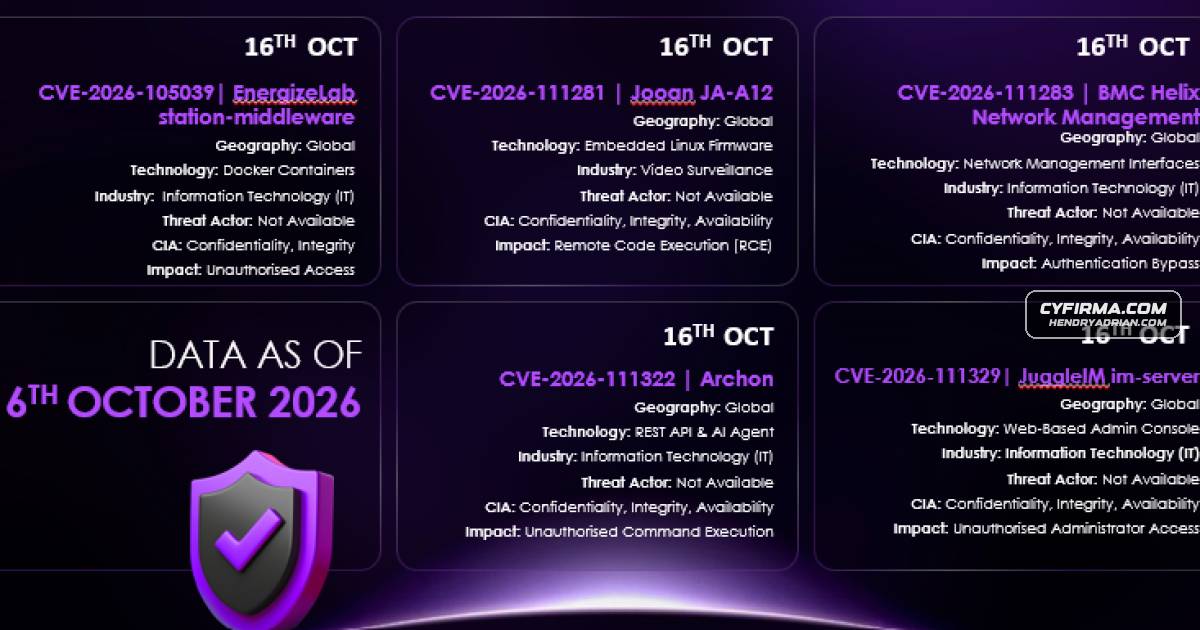
CYFIRMA Flags Five High-Risk Vulnerabilities in Fortnightly Exploit Radar

CYFIRMA highlights five vulnerabilities affecting EnergizeLab, Jooan cameras, BMC Helix, Archon, and JuggleIM, including authentication bypass, remote command execution, and credential exposure. It recommends patching where available and restricting access.

Oct 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Exploit Critical SiteGuard WAF Command-Injection Flaw

CVE-2026-106931, a critical command-injection flaw in SiteGuard Server Edition’s statistics feature, is being exploited. Affected versions can allow root or SYSTEM command execution; administrators should preserve diagnostic evidence before applying fixes.

Oct 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Drupal patches two critical remote code execution flaws

Drupal patched two critical RCE flaws affecting supported versions. Some exploitation paths require contributed modules or custom code and may need no authentication. Administrators should update Drupal core and Entity List or uninstall Field UI as a mitigation.

Oct 17, 2026
Vulnerability & Exploit · rapid7.com

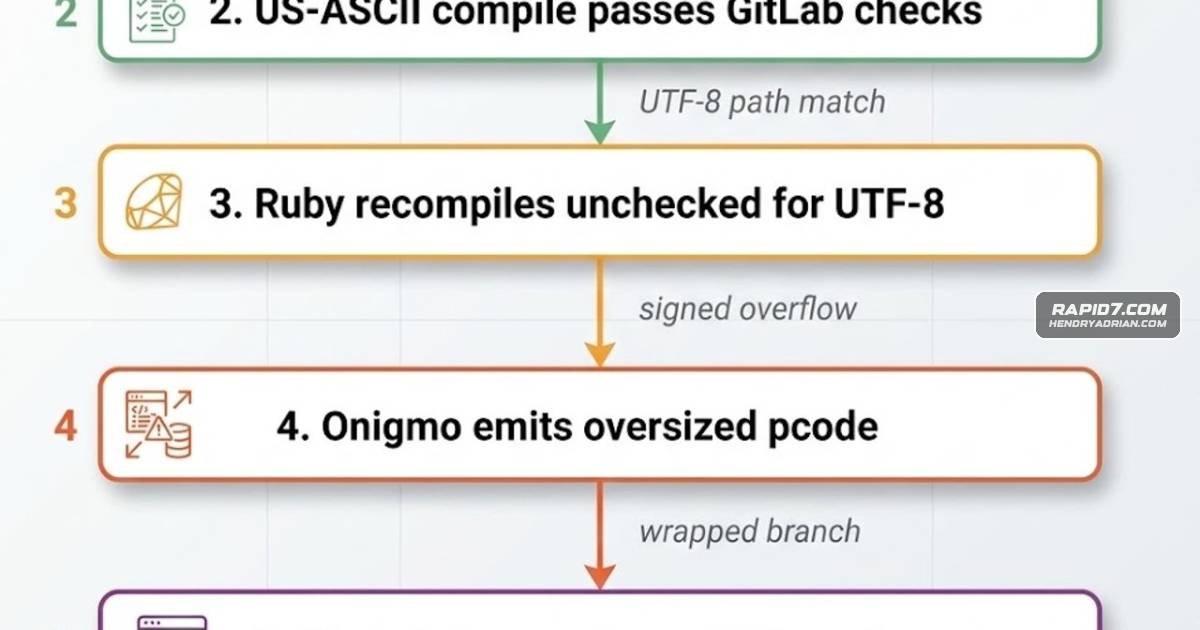
GitLab CI/CD Integer Overflow Enables Command Execution; Fixed Versions Released

Rapid7 demonstrated command execution as GitLab’s git account via CVE-2026-97229. The exploit requires a malicious configuration and path in a public project; GitLab patched affected releases, and no in-the-wild exploitation was reported at disclosure.

Oct 16, 2026
Vulnerability & Exploit · socprime.com

BeyondTrust Remote Support Zero-Day Exploited in Espionage Campaign

BeyondTrust says suspected China-linked actor ARMORY CASTLE exploited CVE-2026-102764 in Remote Support appliances. The article details the attack and recommends patching affected self-hosted systems and investigating appliances exposed while vulnerable.

Oct 16, 2026
Vulnerability & Exploit · socprime.com

Critical Linux Kernel Flaw Enables Guest-to-Host Escape in Controlled Tests

CVE-2026-99999 (PwnEscape) lets guest-controlled packets disclose host memory and may enable host compromise. Root execution was demonstrated only in researchers’ lab; update and reboot affected host kernels.

Oct 16, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Two Actively Exploited Vulnerabilities to KEV Catalog

CISA added Fortinet CVE-2025-61624 and BeyondTrust CVE-2026-102764 to its KEV Catalog based on active exploitation. Federal agencies must prioritize remediation under BOD 26-04; CISA urges all organizations to prioritize KEV vulnerabilities.

Oct 16, 2026
Vulnerability & Exploit · cisa.gov

CISA Urges Immediate Patching of Actively Exploited BeyondTrust Remote Support Vulnerability

CISA says attackers are exploiting CVE-2026-102764, an authentication bypass in BeyondTrust Remote Support versions 26.2.3 and earlier. It urges affected self-hosted users to patch, investigate for compromise, and rotate stored credentials.

Oct 16, 2026
Vulnerability & Exploit · securityweek.com

China-Linked APT Exploited BeyondTrust Remote Support Flaw as a Zero-Day

Mandiant and Google GTIG say China-linked Armory Castle exploited CVE-2026-102764 in BeyondTrust Remote Support from August, using webshells and a tunneler. BeyondTrust patched affected versions; SaaS customers have been updated, while some self-hosted users must patch.

Oct 16, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Patches More Than 30 Vulnerabilities, Including Two Dozen Office RCE Flaws

Microsoft patched more than 30 vulnerabilities, including two dozen high-severity Office RCE flaws; some could be triggered through the Preview Pane. Microsoft said none were exploited as zero-days.

Oct 16, 2026
Vulnerability & Exploit · thehackernews.com

China-Linked Group Exploited BeyondTrust Remote Support Zero-Day

BeyondTrust says Armory Castle exploited CVE-2026-102764 on one self-hosted Remote Support appliance in August 2026. SaaS patches were applied by October 9; affected self-hosted customers should install the designated patch or upgrade.

Oct 16, 2026
Vulnerability & Exploit · socradar.io

BeyondTrust Patches Critical Remote Support Zero-Day Exploited by Suspected Espionage Actor

BeyondTrust says attackers exploited CVE-2026-102764 against two Remote Support appliances before a patch was released. The article details the suspected actor’s post-exploitation activity, affected versions, remediation, and hunting guidance.

Oct 16, 2026
Vulnerability & Exploit · zscaler.com

Attackers Exploit Critical NetScaler Flaw for Unauthenticated Code Execution

Citrix confirmed active exploitation of CVE-2026-88771, a critical unauthenticated RCE flaw in NetScaler ADC and Gateway. Zscaler observed log poisoning, command execution, fingerprinting, web-shell attempts, and delivery of a FreeBSD implant.

Oct 16, 2026
PreviousPage 19 of 65 Next
© 2026 cyber.hendryadrian.com