Unpatched Broadcom Wi-Fi Flaw Allows Root Code Execution on Routers Within Radio Range
Summary
Researcher Quentin Kaiser says a Broadcom WPS flaw lets attackers within Wi-Fi range read router memory or run code as root without credentials. Affected routers have no deployed fix; millions of devices may be vulnerable, though some listed models are unconfirmed.
Key points
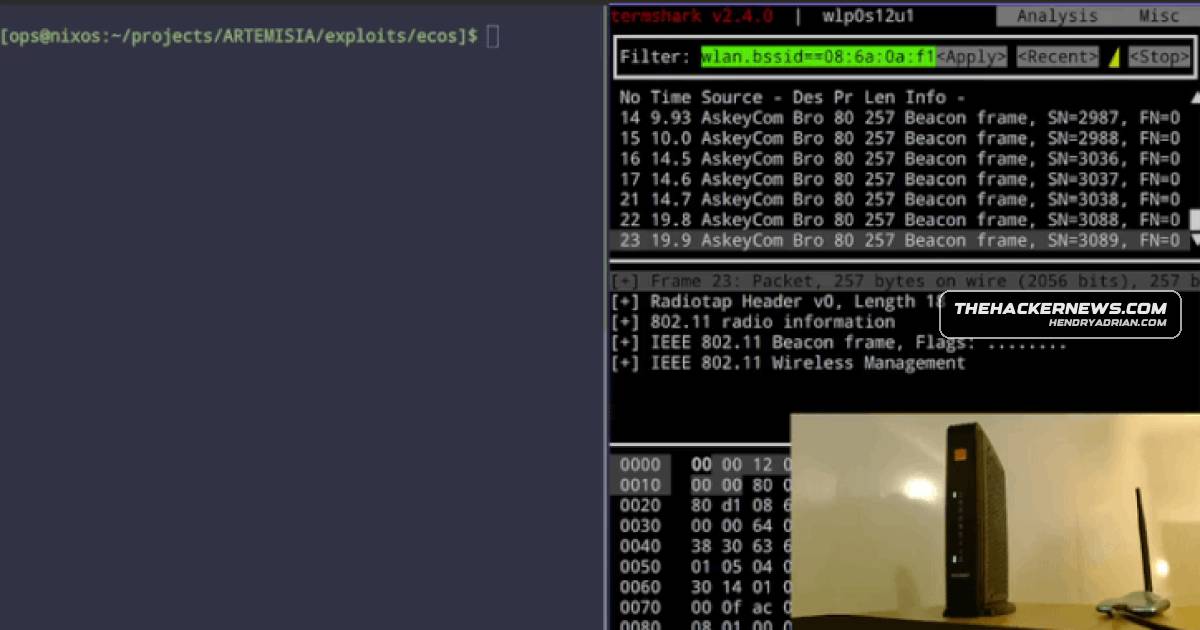
- Kaiser demonstrated the flaw on gateways from Orange Belgium and Proximus: one exploit extracted a stored Wi-Fi password, while another opened a reverse shell over Wi-Fi.
- The flaw affects Broadcom WPS code that mishandles fragmented setup messages, allowing crafted messages to corrupt router memory.
- Kaiser says the attack requires no login or network password, and he has no evidence of real-world exploitation.
- Older eCos-based chip families BCM3380, BCM3383 and BCM33834 have no usable fix, according to Kaiser; newer Linux-based families may be fixable if manufacturers switch Wi-Fi software.
- Kaiser estimates millions of devices may be affected. Some entries on his broader device list are unconfirmed or flagged only as likely vulnerable, and provider counts are rough estimates.
- There is no CVE or patch. Kaiser says Broadcom knew about the issue by 2018, shipped an incomplete fix, and recommended switching to hostapd.
- Kaiser offers YARA rules and a live access-point checking script for triage; he cautions that a match is not confirmation, and says replacement is the practical option for devices that cannot be fixed.
Article Details
- Vulnerability Types
- Memory corruption caused by mishandling fragmented WPS setup messages
- Affected Versions
- Broadcom BCM3380
- Broadcom BCM3383
- Broadcom BCM33834
- Broadcom BCM3390
- Broadcom BCM65xx
- Broadcom BCM68xx
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- unavailable
- Workarounds
- For newer Linux-based models, device makers could switch to the hostapd Wi-Fi software package.
- Replace affected gear that will not be fixed.
People
Vendors
BroadcomA flaw in Broadcom's Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed onOrange BelgiumAgainst an Orange Belgium gateway, the Askey TCG3000 read the Wi-Fi password (the PSK) from the router's stored settings, sent it back over the air, and then joined the network with it.ProximusAgainst a Proximus gateway, the Sagemcom-built BBOX3V+, the exploit opened a reverse shell, a remote command line, carried over Wi-Fi frames, so no outside server was needed.VOOIn Belgium, Kaiser found the flaw present and exploitable on gateways from three of the four big providers: Proximus, Orange Belgium and VOO. A fourth, Telenet, may be affected too, but he could not test one.
Products
Askey TCG3000Against an Orange Belgium gateway, the Askey TCG3000 read the Wi-Fi password (the PSK) from the router's stored settings, sent it back over the air, and then joined the network with it.BCM3380The vulnerable chips fall into two families: older eCos-based models (the BCM3380, BCM3383 and BCM33834), where he found no usable fix and calls the bug a permanent "forever day," meaning a flaw that will never beBCM3383The vulnerable chips fall into two families: older eCos-based models (the BCM3380, BCM3383 and BCM33834), where he found no usable fix and calls the bug a permanent "forever day," meaning a flaw that will never beBCM33834The vulnerable chips fall into two families: older eCos-based models (the BCM3380, BCM3383 and BCM33834), where he found no usable fix and calls the bug a permanent "forever day," meaning a flaw that will never beBCM3390day," meaning a flaw that will never be patched on those devices, and newer Linux-based models (the BCM3390, BCM65xx and BCM68xx), which could be fixed if their makers switch Wi-Fi software.BCM65xxmeaning a flaw that will never be patched on those devices, and newer Linux-based models (the BCM3390, BCM65xx and BCM68xx), which could be fixed if their makers switch Wi-Fi software.BCM68xxflaw that will never be patched on those devices, and newer Linux-based models (the BCM3390, BCM65xx and BCM68xx), which could be fixed if their makers switch Wi-Fi software.hostapdan incomplete fix in 2018, then told customers to switch to a different Wi-Fi software package, called hostapd, rather than relying on the fix. On the older eCos chips, he says, no working fix was ever shipped, which