
CYFIRMA Flags Five High-Risk Vulnerabilities in Fortnightly Exploit Radar
Summary
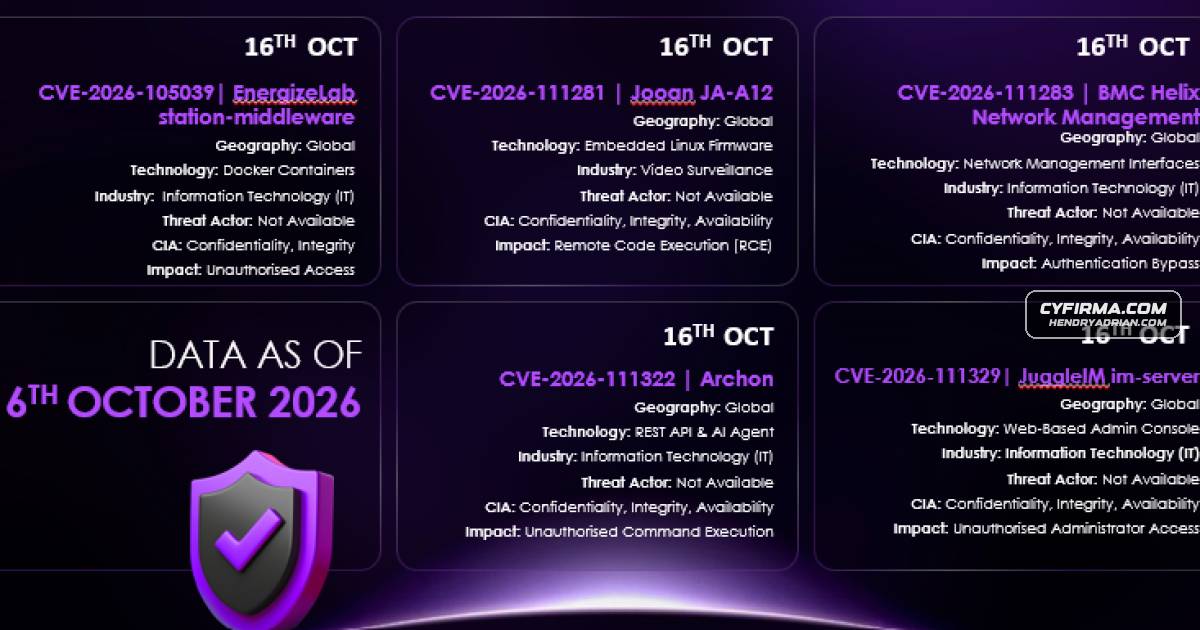
CYFIRMA highlights five vulnerabilities affecting EnergizeLab, Jooan cameras, BMC Helix, Archon, and JuggleIM, including authentication bypass, remote command execution, and credential exposure. It recommends patching where available and restricting access.
Key points
- The report lists five vulnerabilities, with reported CNA CVSS scores ranging from 9.0 to 9.8.
- EnergizeLab station-middleware versions 1.6.5–1.8.2 may expose AI provider keys and allow configuration and data changes; no vendor-fixed release is identified.
- Affected Jooan JA-A12 firmware may permit unauthenticated remote root command execution; no vendor-fixed release is identified.
- BMC Helix Network Management versions before 26.3.01 may allow authentication bypass and administrator access; version 26.3.01 is listed as fixed.
- Archon versions 0.2.13–0.11.1 may allow unauthenticated command execution through its API; no vendor-fixed release is identified.
- JuggleIM im-server versions 1.8.16 or earlier may be exposed to unauthorized access through default administrator credentials; no vendor-fixed release is identified.
- CYFIRMA advises applying available updates, changing default credentials, rotating exposed secrets, limiting access to trusted networks, and monitoring for suspicious activity.
Article Details
- Vulnerability Types
- Missing role checks
- Authentication bypass
- Remote command execution
- Default credentials
- Severity
- CVSS 9.0–9.8 (CNA)
- Affected Versions
- EnergizeLab station-middleware 1.6.5–1.8.2
- Jooan JA-A12 firmware 009_20171107 and 05.02.31.105
- BMC Helix Network Management before 26.3.01
- Archon 0.2.13–0.11.1
- JuggleIM im-server 1.8.16 and earlier
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- partial
- Workarounds
- For EnergizeLab station-middleware, enforce role-based access controls on administrative APIs and limit API access to trusted networks.
- For Jooan JA-A12, change default credentials, restrict remote access, and isolate cameras on a dedicated network.
- For BMC Helix Network Management, restrict management-interface access and review SAML SSO and local administrator authentication.
- For Archon, enable authentication for all /api/* endpoints and restrict API access to trusted networks.
- For JuggleIM im-server, replace default administrator credentials and restrict access to admin console port 8090.
CVE
CVE-2026-105039EnergizeLab · station-middlewareCVE-2026-105039 – EnergizeLab station-middlewareCVE-2026-111281Jooan · JA-A12CVE-2026-111281 – Jooan JA-A12 IP cameraCVE-2026-111283BMC Helix · BMC Helix Network ManagementCVE-2026-111283 – BMC Helix Network ManagementCVE-2026-111322coleam00 · ArchonCVE-2026-111322 – ArchonCVE-2026-111329juggleim · JuggleIMCVE-2026-111329 – JuggleIM im-server
Products
ArchonArchon: Yes, if you use versions 0.2.13 through 0.11.1.BMC Helix Network ManagementBMC Helix Network Management: Yes, if you use an on-premises version before 26.3.01 with SAML SSO configured.EnergizeLab station-middlewareEnergizeLab station-middleware: Yes, if you use versions 1.6.5 through 1.8.2.Jooan JA-A12CVE-2026-111281 – Jooan JA-A12 IP cameraJuggleIM im-serverJuggleIM im-server: Yes, if you use version 1.8.16 or earlier.