SneakyChef Uses SFX RARs to Deliver SugarGh0st RAT in Government-Targeting Campaign
Summary
Talos reports that SneakyChef expanded SugarGh0st RAT operations across EMEA and Asia, using government-themed lures and a new SFX RAR infection chain that drops malware and establishes logon persistence.
Key points
- Talos observed SneakyChef activity dating to August 2023, with suspected government targets across EMEA and Asia.
- Lures impersonated government agencies and included scanned documents, conference materials, and official-looking forms.
- A newly identified infection chain uses an SFX RAR executable to drop a decoy document, DLL loader, encrypted SugarGh0st payload, and malicious VB script.
- The VB script sets HKCU\Environment\UserInitMprLogonScript to launch update.dll with regsvr32.exe at user logon.
- The loader decrypts SugarGh0st RAT and injects it into a process.
- Talos observed continued use of an older command-and-control domain through mid-May and a newer domain reported in the campaign.
- Talos assesses with medium confidence that the operators are likely Chinese-speaking; it identifies Snort and ClamAV detections and other defensive coverage.
Article Details
- Attack Vectors
- Malicious SFX RAR files execute a script that drops a decoy document, a DLL loader, encrypted SugarGh0st, and a malicious VBScript into the victim’s user-profile temporary folder, then runs the VBScript.
- A malicious VBScript establishes persistence by writing a command to HKCU\Environment\UserInitMprLogonScript; at logon, the command launches update.dll using regsvr32.exe.
- The update.dll loader reads and decrypts the SugarGh0st RAT from authz.lib and injects it into a process.
- Earlier infection chains used malicious RAR files containing an LNK file and were likely delivered via phishing email.
- Defensive Notes
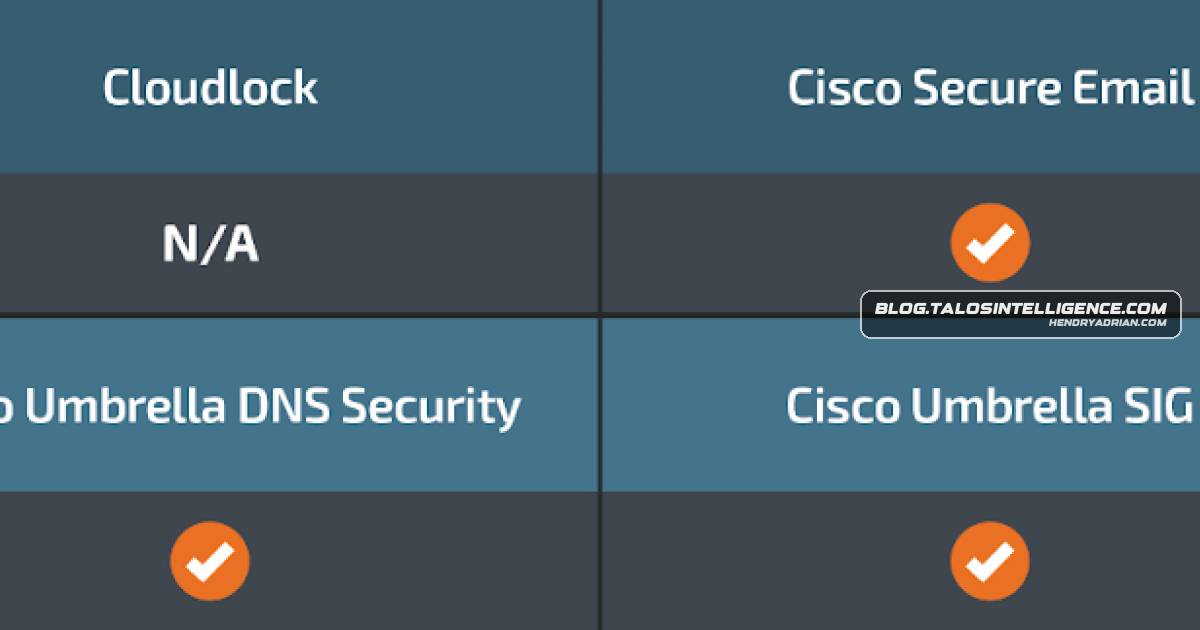
- The article recommends Cisco Secure Endpoint, Cisco Secure Web Appliance, Cisco Secure Email, Cisco Secure Firewall, Cisco Secure Malware Analytics, Umbrella, Cisco Duo, Snort, and ClamAV protections.
- The article lists ClamAV detections for SugarGh0st-related files and provides Snort SID 62647.
- The article says Cisco Secure Endpoint users can use Orbital Advanced Search to check endpoints with threat-specific OSqueries.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | account[.]drive-google-com[.]tk | C2 domain used by SugarGh0st samples. |
| DOMAIN | account[.]gommask[.]online | Domain reported by Proofpoint as used by SugarGh0st. |
MITRE ATT&CK
People
Threat Actors
Malware
Gh0st RAToperators are likely Chinese-speaking based on their language preferences, the usage of the variants of Gh0st RAT — a popular malware among various Chinese-speaking actors — and the specific targets, which includes theRamnitWin.Loader.Ramnit-10014943-1 SpiceRATaffairs of various countries and other government entities. Talos also discovered another RAT dubbed “SpiceRAT” used in the campaign. Read the corresponding research here.SugarGh0stSneakyChef espionage group targets government agencies with SugarGh0st and more infection techniques
Vendors
CiscoCisco Talos recently discovered an ongoing campaign from SneakyChef, a newly discovered threat actor using SugarGh0st malware, as early as August 2023. ClamAVClamAV detections are also available for this threat: ProofpointRecently, Proofpoint researchers reported a SugarGh0st campaign targeting an organization in the U.S. involved in artificial intelligence across academia, the private technology sector, and government services,Yahoo!Cisco Talos would like to thank the Yahoo! Paranoids Advanced Cyber Threats Team for their collaboration in this investigation.
Products
Adaptive Security ApplianceNext-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat. Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network. Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here. Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here. Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisCisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products. Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks. Meraki MXFirewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat. Orbital Advanced SearchCisco Secure Endpoint users can use Orbital Advanced Search to run complex OSqueries to see if their endpoints are infected with this specific threat. For specific OSqueries related to this threat, please follow theSnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. Snort SID for this threat is 62647. Threat Defense VirtualCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisUmbrellathe C2 domain account[.]drive-google-com[.]tk, consistent with their previous campaign. Based on Talos’ Umbrella records, resolutions to the C2 domain were still observed until mid-May.
Tools
Countries
AngolaMinistry of Foreign affairs of Angola IndiaMinistry of Foreign affairs of India KazakhstanMinistry of Foreign affairs of Kazakhstan LatviaMinistry of Foreign affairs of Latvia Saudi ArabiaEmbassy of the Kingdom of Saudi Arabia in Abu Dhabi South KoreaIn the newly discovered campaign, we observed a wider scope of targets spread across countries in EMEA and Asia, compared with previous observations that mainly targeted South Korea and Uzbekistan. TurkmenistanMinistry of Foreign affairs of Turkmenistan United StatesUzbekistanIn the newly discovered campaign, we observed a wider scope of targets spread across countries in EMEA and Asia, compared with previous observations that mainly targeted South Korea and Uzbekistan.
Industries
Academiaa SugarGh0st campaign targeting an organization in the U.S. involved in artificial intelligence across academia, the private technology sector, and government services, highlighting the wider adoption of SugarGh0stGovernmentSneakyChef espionage group targets government agencies with SugarGh0st and more infection techniquesTechnologytargeting an organization in the U.S. involved in artificial intelligence across academia, the private technology sector, and government services, highlighting the wider adoption of SugarGh0st RAT in targeting various