cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2500 articles

Threat Research · hunt.io

Hunt.io Details Gamaredon DNS Patterns and ShadowPad-Linked Infrastructure

Hunt.io researchers describe Gamaredon’s short-TTL, rotating DNS infrastructure and a separate server cluster linked to a ShadowPad backdoor, detailing its delivery chain, shared certificate clues, and indicators of compromise.
Apr 8, 2025
Threat Research · huntress.com

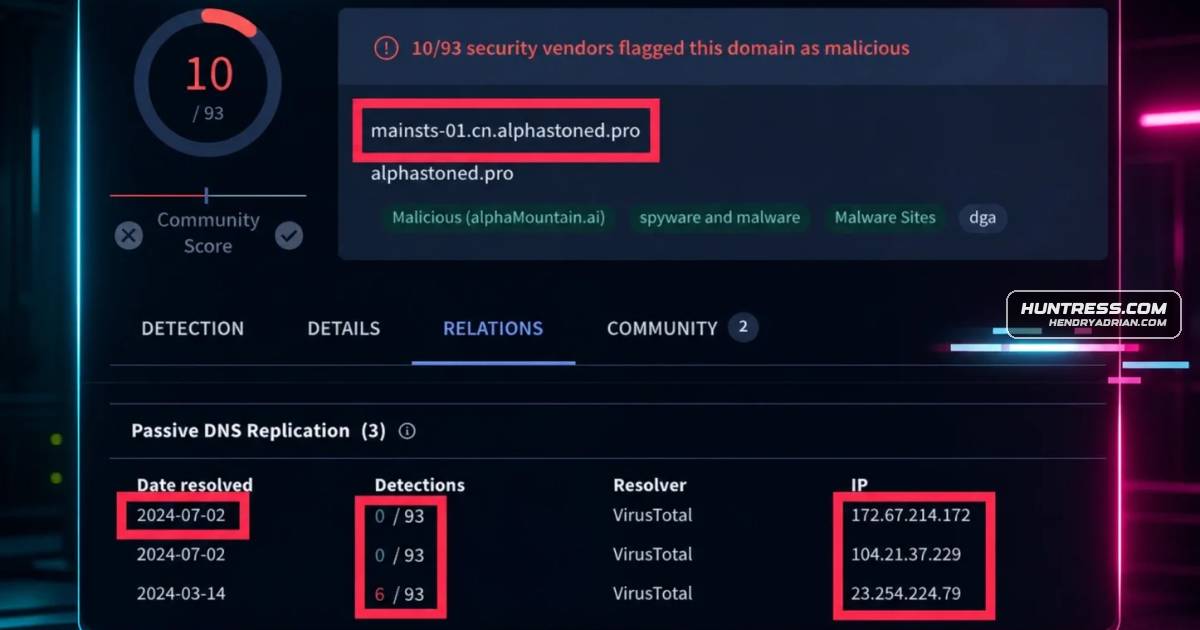
Huntress Details CrushFTP CVE-2025-31161 Exploitation and Post-Exploitation Activity

Huntress observed in-the-wild exploitation of CrushFTP’s CVE-2025-31161 authentication bypass, followed by backdoor-account creation and deployment of RMM tools and malware. Affects versions 10.0.0–10.8.3 and 11.0.0–11.3.0; patched in 10.8.4+ and 11.3.1+.

Apr 4, 2025
Threat Research · hunt.io

ClickFix Pages Deliver Lumma and CryptBot, Steal Zoho Credentials

Hunt.io researchers used behavioral queries to identify ClickFix pages delivering Lumma and CryptBot, harvesting Zoho credentials, and staging PowerShell payloads. The article details their techniques, infrastructure, indicators, and defensive recommendations.

Apr 3, 2025
Threat Research · aquasec.com

Researchers Detail Campaign Using Brute-Force Attacks to Hijack Tomcat Servers

Aqua researchers detail a campaign that brute-forces Tomcat management consoles, installs JSP backdoors, steals SSH credentials, and deploys Windows and Linux payloads for persistence, lateral spread, and cryptomining.

Apr 2, 2025
Threat Research · hunt.io

Russian-Speaking Actor Uses Cloudflare Phishing Pages to Deliver Pyramid C2 Malware

Researchers detail a phishing campaign using Cloudflare Pages and Workers, search-ms links, and disguised LNK files to install malware. The infection reports victims’ IP addresses through Telegram and establishes persistence while communicating with Pyramid C2.

Apr 1, 2025
Threat Research · wiz.io

CPU_HU Campaign Uses Exposed PostgreSQL Servers to Deploy Fileless Cryptominers

Wiz describes JINX-0126’s use of weakly credentialed exposed PostgreSQL servers to deploy fileless XMRig-C3 miners. Pool statistics suggest the campaign may have affected over 1,500 machines.

Mar 31, 2025
Threat Research · threatfabric.com

Crocodilus Android Banking Trojan Steals Credentials, OTPs and Crypto Wallet Seed Phrases

ThreatFabric analyzes Crocodilus, an Android banking Trojan that uses Accessibility features, overlays and remote control to steal credentials, OTPs and crypto wallet seed phrases. Early campaigns targeted Spain and Turkey.

Mar 28, 2025
Threat Research · cloudsek.com

Clickflix Phishing Campaign Targets YouTube Creators With Lumma Stealer

A campaign impersonates brands in partnership emails to lure YouTube creators into a Clickflix flow that runs malicious PowerShell and delivers Lumma Stealer, which targets browser credentials, cookies, and cryptocurrency wallets.

Mar 25, 2025
Threat Research · wiz.io

IngressNightmare Flaws Enable Unauthenticated RCE in Kubernetes Ingress NGINX

Wiz researchers detailed four Ingress NGINX flaws that can enable unauthenticated RCE and access to Kubernetes secrets. They reported more than 6,500 publicly exposed clusters; fixes are available in versions 1.12.1 and 1.11.5.

Mar 24, 2025
Threat Research · bitdefender.com

Researchers Detail 331 Malicious Google Play Apps That Bypassed Android 13 Protections

Bitdefender researchers analyzed a campaign of at least 331 Google Play apps with more than 60 million downloads. The apps bypassed Android restrictions to hide, launch ads, and direct users to phishing attempts; 15 were still available when the research ended.

Mar 18, 2025
Threat Research · hunt.io

Rust Loaders Deliver Cobalt Strike Cat in Intrusions Targeting South Korean Organizations

Researchers found evidence of intrusions against South Korean organizations using reconnaissance tools, SQL injection, and Rust- and MinGW-compiled loaders to deploy Cobalt Strike Cat and Marte shellcode. Logs showed two compromised hosts beaconing.

Mar 18, 2025
Threat Research · wiz.io

Compromised reviewdog GitHub Action Exposed CI Workflow Secrets

Wiz says reviewdog/action-setup@v1 was briefly compromised, injecting code that exposed CI secrets in workflow logs. Coinbase confirmed an unsuccessful attempt to compromise coinbase/agentkit; Wiz recommends auditing runs and rotating exposed secrets.

Mar 17, 2025
Threat Research · blog.talosintelligence.com

Cisco Talos Details How Attackers Abuse CSS to Evade Email Filters and Track Recipients

Cisco Talos describes observed phishing and spam campaigns that use CSS to hide content from email filters and track recipients’ actions, preferences, and device details, and recommends filtering and email privacy proxies.

Mar 13, 2025
Threat Research · hunt.io

Researchers Find Rebranded File Management Panel on JSPSpy Servers

Hunt researchers found a web-based file management panel called Filebroser on two of four servers hosting JSPSpy web shells. They describe the infrastructure and share HTTP indicators and page titles defenders can use to track related activity.

Mar 11, 2025
Threat Research · huntress.com

Huntress Reconstructs Intrusion Involving Veeam Exploitation and Suspected VPN Access

Huntress reconstructs an intrusion involving a successful account brute-force attack, credential theft through an unpatched Veeam service, WinRM lateral movement and persistence. VPN compromise is suspected, but telemetry was incomplete.

Mar 10, 2025
Threat Research · blog.talosintelligence.com

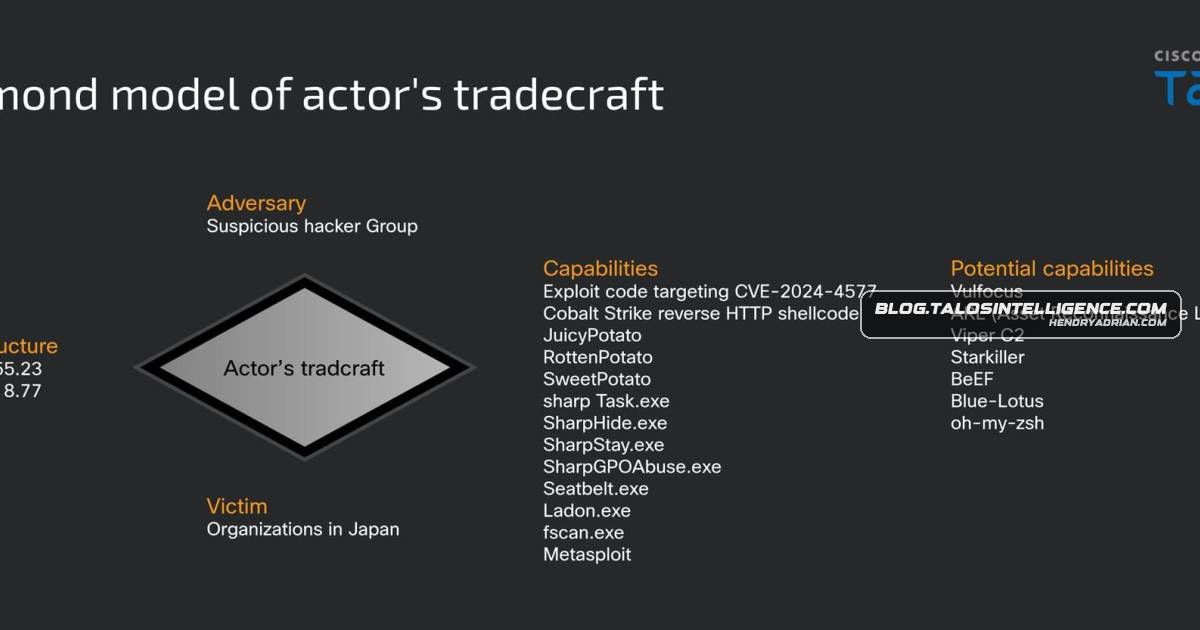
Attackers Exploit PHP-CGI Flaw to Target Organizations in Japan

Talos describes attacks targeting organizations in Japan since January 2025. The unknown attacker exploited CVE-2024-4577 for access, then used Cobalt Strike and other tools for persistence, lateral movement, and credential theft.

Mar 6, 2025
Threat Research · hunt.io

EFF Impersonators Target Albion Online Players With Stealc and Pyramid C2 Malware

A campaign targeting Albion Online players used fake EFF messages and decoy documents to deliver Stealc and Pyramid C2 malware. Researchers detail its execution chain, credential theft, and 11 related servers linked by shared SSH keys.

Mar 4, 2025
Threat Research · huntress.com

Huntress Details RedCurl-Linked Intrusions at Three Organizations in Canada

Huntress investigated three intrusions at organizations wholly or partly in Canada, linking activity to RedCurl through malware, infrastructure and tradecraft. Attackers used scheduled tasks, Python reverse proxies and cloud storage for suspected exfiltration.

Mar 3, 2025
Threat Research · blog.talosintelligence.com

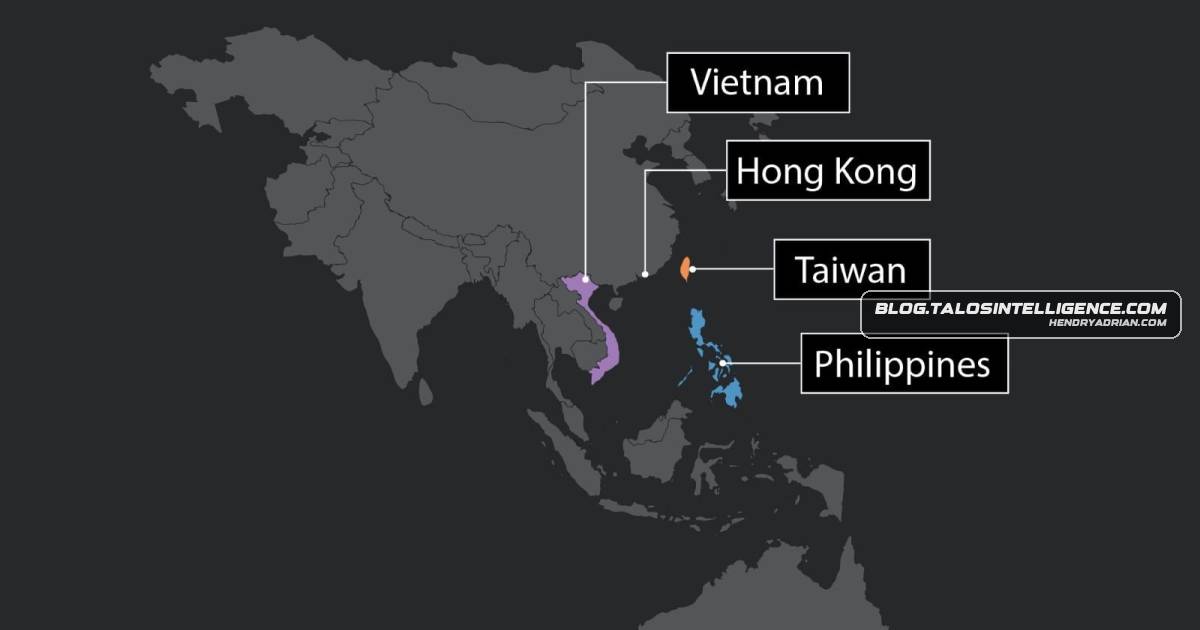
Lotus Blossom Uses Sagerunex Backdoor Variants and Cloud Services in Espionage Campaigns

Cisco Talos attributes campaigns targeting government, manufacturing, telecommunications and media organizations to Lotus Blossom, detailing Sagerunex variants that use Dropbox, Twitter and Zimbra for command and control.

Feb 27, 2025
Threat Research · darktrace.com

Darktrace Details Lynx Ransomware Tactics and a Customer Network Compromise

Darktrace analyzes Lynx ransomware’s tactics and a December 2024 customer compromise involving lateral movement, suspected stolen admin credentials, data exfiltration, AnyDesk use, and SMB-based file encryption.

Feb 27, 2025
Threat Research · hunt.io

SSL Certificate Analysis Uncovers 77 Servers Linked to Joker Android Malware

Researchers traced Joker Android malware infrastructure by pivoting on reused SSL certificates, identifying 77 linked Alibaba-hosted servers and malicious APKs. The malware can steal SMS and device data and enroll victims in premium services.

Feb 27, 2025
Threat Research · hunt.io

LightSpy Expands Surveillance Capabilities with Facebook and Instagram Data-Collection Commands

Researchers found LightSpy command-list entries for extracting Facebook and Instagram database files, a previously unreported core version, Windows surveillance plugins, and exposed administration endpoints across its infrastructure.

Feb 20, 2025
Threat Research · hunt.io

Backdoored Signal, LINE and Gmail Installers Target Chinese-Speaking Users

Fake software download pages targeting Chinese-speaking users distribute backdoored Windows executables that modify Windows Defender settings and connect to suspected command-and-control infrastructure.

Feb 18, 2025
Threat Research · wiz.io

Wiz Details NVIDIA Container Toolkit Flaw Enabling Host Escape

Wiz Research details CVE-2024-0132, a TOCTOU flaw in NVIDIA Container Toolkit that can let a container-image controller mount the host filesystem and escape isolation. NVIDIA says version 1.17.4 fixes it and a patch bypass, CVE-2025-23359.

Feb 11, 2025
PreviousPage 93 of 105 Next
© 2026 cyber.hendryadrian.com