Huntress Finds Attackers Reused Tactics in CrushFTP and CentreStack Intrusions
Summary
Huntress compared intrusions exploiting CrushFTP and CentreStack/Triofox, finding shared infrastructure and tools despite different file-transfer methods. In some incidents, security tools detected and quarantined files before further activity.
Key points
- Huntress observed CrushFTP and CentreStack/Triofox exploitation in April 2025, with the same source IP, 2.58.56.16, appearing in activity involving both products.
- In CrushFTP incidents, logs showed files d3d11.dll and the Mesh Agent installer transferred from the source IP. Windows Defender quarantined d3d11.dll before analysts observed it loading.
- Some Mesh Agent installations were configured to connect to rtb[.]mftadsrvr[.]com:2087.
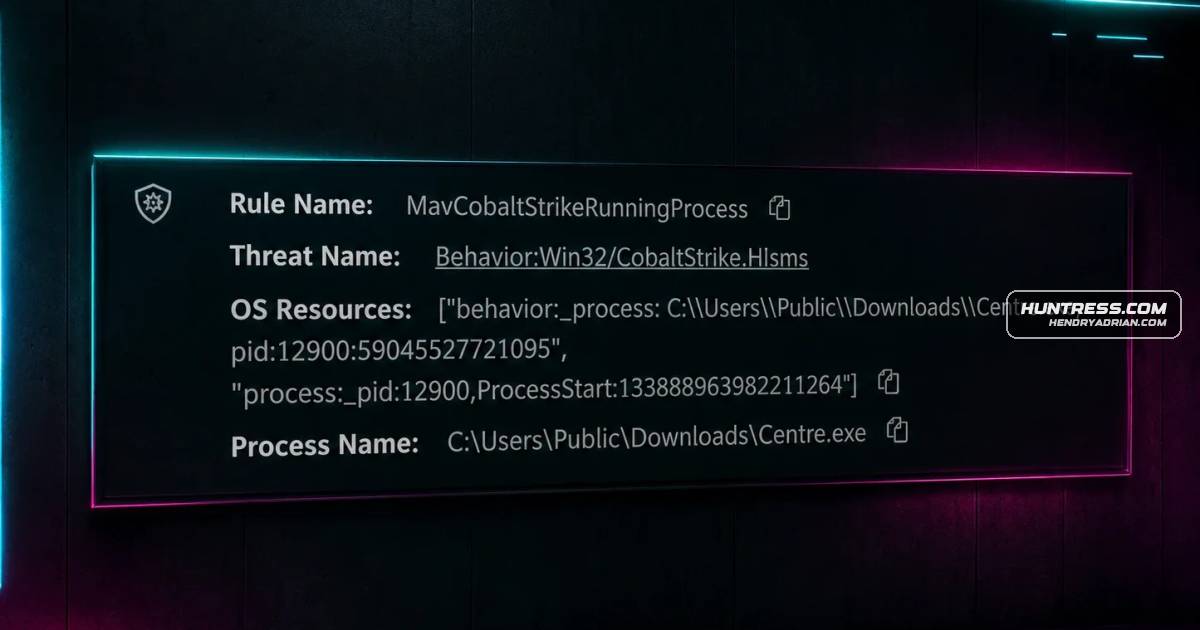
- In CentreStack/Triofox incidents, attackers used base64-encoded PowerShell commands to download files, including Centre.exe, which Defender detected as Cobalt Strike and quarantined.
- Huntress found that Centre.exe, identified as the Wallpaper Engine Launcher, referenced d3d11.dll in its import table, indicating it was intended to sideload the DLL.
- Huntress suggests the attacker may have changed file-transfer methods after earlier incidents were contained; it also observed an incident where initial access was gained on an endpoint without its agent installed.
- Huntress recommends maintaining an asset inventory, reducing attack surface, patching and configuring necessary applications, and deploying monitoring and response capabilities across endpoints.
Article Details
- Attack Vectors
- Exploitation of CVE-2025-31161 in CrushFTP for initial access.
- Exploitation of the Gladinet CentreStack and Triofox vulnerability, CVE-2025-30406, for initial access.
- Use of base64-encoded PowerShell commands to download files to compromised endpoints.
- Attempted DLL side-loading: Centre.exe referenced d3d11.dll in its import table and was intended to load the DLL.
- Defensive Notes
- Huntress recommends inventorying physical and virtual assets, installed applications, and their versions.
- Reduce the attack surface by removing unnecessary applications, patching and properly configuring required applications, and installing monitoring, detection, and response capabilities on all endpoints.
- In the reported incidents, Windows Defender detected and quarantined d3d11.dll and a process identified as Cobalt Strike; monitored endpoints were isolated.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | rtb[.]mftadsrvr[.]com | Endpoint configured as the Mesh Agent connection destination. |
| IPV4 | 196[.]251[.]85[.]31 | Reported threat-actor source of tool downloads. |
| IPV4 | 2[.]58[.]56[.]16 | Reported threat-actor source IP used in CrushFTP and CentreStack incident activity. |
MITRE ATT&CK
T1059.001 · PowerShellThe actor used base64-encoded PowerShell commands to download files to endpoints.T1190 · Exploit Public-Facing ApplicationThe incidents began with exploitation of CrushFTP and Gladinet CentreStack/Triofox vulnerabilities to gain initial access.T1574.002 · DLL Side-LoadingCentre.exe referenced d3d11.dll and was described as intended to side-load the malicious DLL.
CVE
CVE-2025-30406CVE-2025-31161 Auth Bypass and Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the Wild blog was published.CVE-2025-31161On 4 April 2025, the CrushFTP CVE-2025-31161 Auth Bypass and Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the Wild
Malware
Vendors
CrushFTPOn 4 April 2025, the CrushFTP CVE-2025-31161 Auth Bypass and Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the WildGladinetBypass and Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the Wild blog was published.
Products
CrushFTPOn 4 April 2025, the CrushFTP CVE-2025-31161 Auth Bypass and Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the WildGladinet CentreStackand Post-Exploitation blog was published, and on 14 April 2025, the CVE-2025-30406 - Critical Gladinet CentreStack & Triofox Vulnerability Exploited in the Wild blog was published.Mesh Agentbetween the two; specifically, IOCs such as the 2.58.56[.]16 IP address, installation of the Mesh Agent RMM, and the d3d11.dll file.Wallpaper EngineFile version information included within the Centre.exe file indicates that it’s the Wallpaper Engine Launcher, originally named “launcher.exe”.Windows DefenderIn both incidents, the d3d11.dll file was detected and quarantined by Windows Defender, as illustrated in Figure 1.