Fake AI Installers Deliver CyberLock and Lucky_Gh0$t Ransomware, Destructive Numero Malware
Summary
Cisco Talos details three threats disguised as AI tool installers: CyberLock and Lucky_Gh0$t ransomware, and Numero, which disrupts Windows interfaces. The installers spread through fake sites, search results, and a malicious ChatGPT-themed package.
Key points
- CyberLock was delivered through a fake NovaLeads AI website promoted in search results; its .NET loader runs an embedded PowerShell ransomware script.
- CyberLock encrypts selected files on C:, D: and E: drives, demands $50,000 in Monero, and uses cipher.exe to overwrite free disk space. Talos found no evidence of data-exfiltration functionality.
- Lucky_Gh0$t, a Yashma variant, was bundled in a fake ChatGPT 4.0 installer alongside legitimate AI tools. It encrypts files under approximately 1.2 GB and replaces larger files with content containing a single character.
- Numero impersonates the InVideo AI installer and repeatedly runs malware that alters Windows desktop interface elements, rendering systems unusable.
- Talos observed these threats distributed through fraudulent installers and channels including SEO-poisoned search results and messaging platforms.
- Talos lists Snort and ClamAV detections and says customers can use Cisco security products to detect or block the threats.
Article Details
- Attack Vectors
- Fake AI tool websites promoted through SEO manipulation to appear prominently in search results.
- Fraudulent installers distributed through platforms such as Telegram and social media messengers.
- CyberLock delivered in a ZIP archive containing a .NET loader with an embedded PowerShell ransomware script.
- Lucky_Gh0$t delivered in a self-extracting ZIP installer disguised as a ChatGPT installer.
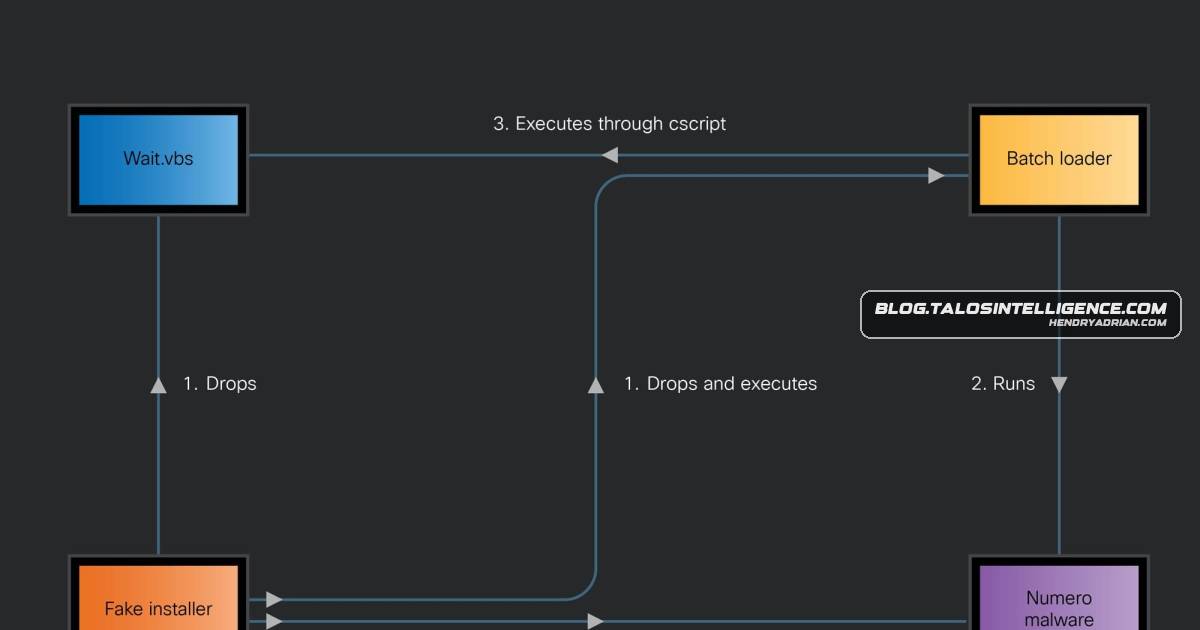
- Numero delivered in a fake InVideo AI installer containing a Windows batch file, VB script, and malware executable.
- Defensive Notes
- Verify software sources and rely on reputable vendors before downloading AI tools.
- Cisco Talos recommends using its listed security products to detect or block the threats; Snort and ClamAV detections are also listed.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | novaleadsai[.]com | Fake AI solution website used to distribute the CyberLock loader. |
cyberspectreislocked@onionmail[.]org | Email address given to CyberLock victims for ransom communication. |
MITRE ATT&CK
T1036 · MasqueradingThe installers impersonate AI products; Lucky_Gh0$t is named dwn.exe to resemble Microsoft's dwm.exe.T1059.001 · PowerShellCyberLock is a PowerShell ransomware script embedded in a .NET loader and executed on the victim's system.T1059.003 · Windows Command ShellNumero's dropped Windows batch file repeatedly launches the malware and restarts it.T1059.005 · Visual BasicNumero's batch-file execution flow runs a dropped VB script through cscript.T1204.002 · Malicious FileThe malware runs after victims launch the counterfeit AI installer or archive.T1485 · Data DestructionNumero corrupts desktop windows, and Lucky_Gh0$t deletes original files larger than 1.2 GB after replacing their contents with a single character.T1486 · Data Encrypted for ImpactCyberLock and Lucky_Gh0$t encrypt victim files for ransom.T1490 · Inhibit System RecoveryLucky_Gh0$t deletes volume shadow copies and backups; CyberLock also uses cipher.exe /w to hinder recovery of deleted files.
People
Malware
ChaosLucky_Gh0$t ransomware is yet another variant of the Yashma ransomware, which is the sixth iteration of the Chaos ransomware series, featuring only minor modifications to the ransomware binary. CyberLockCisco Talos has discovered new threats, including the ransomware CyberLock, Lucky_Gh0$t, and a newly-discovered malware we call “Numero,” all of which masquerade as legitimate AI tool installers. Lucky_Gh0$tCisco Talos has discovered new threats, including the ransomware CyberLock, Lucky_Gh0$t, and a newly-discovered malware we call “Numero,” all of which masquerade as legitimate AI tool installers. NumeroCisco Talos has discovered new threats, including the ransomware CyberLock, Lucky_Gh0$t, and a newly-discovered malware we call “Numero,” all of which masquerade as legitimate AI tool installers. YashmaLucky_Gh0$t ransomware is yet another variant of the Yashma ransomware, which is the sixth iteration of the Chaos ransomware series, featuring only minor modifications to the ransomware binary.
Vendors
Products
Adaptive Security ApplianceNext-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat. ChatGPTLucky_Gh0$t ransomware as fake ChatGPT installer Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network. Cisco Secure AccessCisco Secure Access is a modern cloud-delivered Security Service Edge (SSE) built on Zero Trust principles. Secure Access provides seamless transparent and secure access to the internet, cloud services or privateCisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here. Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here. Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisCisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products. Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device. Cisco Secure Web ApplianceCisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them. ClamAVClamAV detections are also available for this threat: Firewall Management CenterAdditional protections with context to your specific environment and threat data are available from the Firewall Management Center. InVideo AImalware in the wild that we call “Numero,” designed to imitate the AI video creation tool installer, InVideo AI. InVideo AI is an online platform widely used for marketing videos, social media content, explainerMeraki MXFirewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat. Microsoft WindowsThe newly-identified destructive malware, Numero, affects victims by manipulating the graphical user interface (GUI) components of their Windows OSs, rendering systems completely unusable. SnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. StealthwatchCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device. Stealthwatch CloudCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device. Threat Defense VirtualCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisThreat GridCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products. UmbrellaUmbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network.
Tools
cipher.exe8. Sample blog post header wallpaper. Finally, CyberLock uses the living-off-the-land binary (LoLBin) ‘cipher.exe’ with the ‘/w’ option to erase free space on the victim's hard drive partitions, hindering forensicIDAevades analysis by checking the process handles of various malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debuggerImmunity debuggerdebuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. ImportRECtools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. OllyDbghandles of various malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. reshackermalware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. Rock debuggerx32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. scyllaof various malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. windbgvarious malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. x32debuggerthe process handles of various malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger. x64 debuggerby checking the process handles of various malware analysis tools and debuggers including IDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and RockZeta debuggerIDA, x64 debugger, x32debugger, ollydbg, scylla, windbg, reshacker, ImportREC, Immunity debugger, Zeta debugger and Rock debugger.
Industries
B2B salesmalware, dubbed “Numero.” The legitimate versions of these AI tools are particularly popular within the B2B sales domain and the technology and marketing sectors, indicating that individuals and organizations in thesemarketingversions of these AI tools are particularly popular within the B2B sales domain and the technology and marketing sectors, indicating that individuals and organizations in these industries are particularly at risk ofTechnologyThe legitimate versions of these AI tools are particularly popular within the B2B sales domain and the technology and marketing sectors, indicating that individuals and organizations in these industries are