
Analysis Details MacSync macOS Stealer’s ClickFix Delivery and Data-Theft Chain
Summary
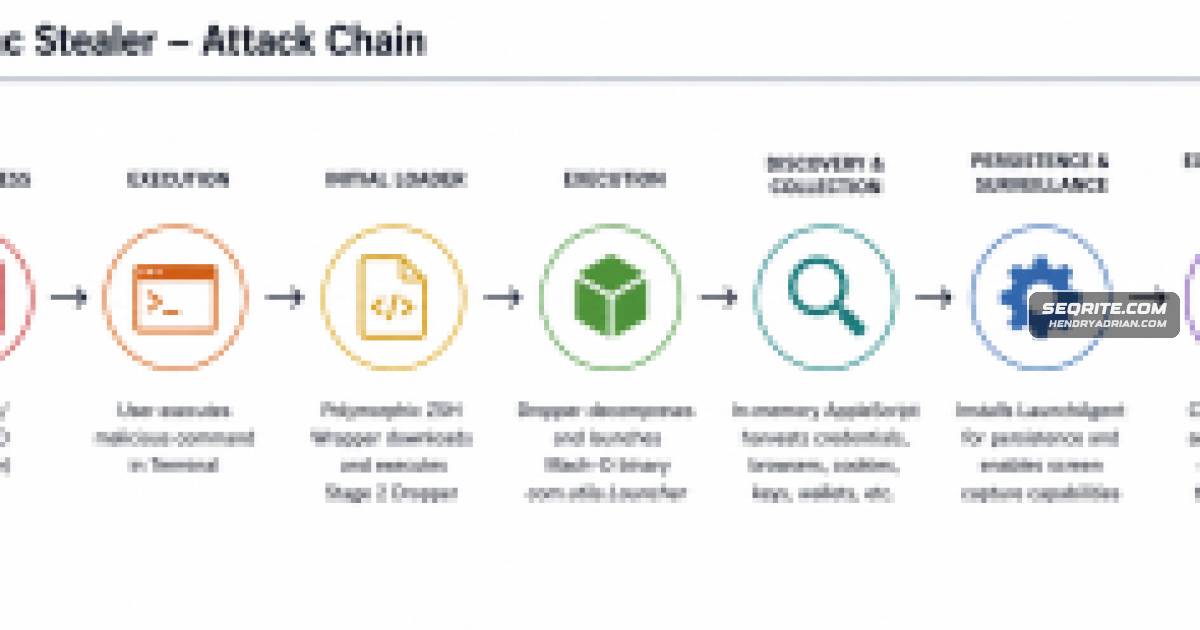
Seqrite analyzes MacSync, a macOS MaaS stealer delivered through ClickFix lures and malvertising. The report details its native Mach-O stager, in-memory AppleScript payload, credential theft, persistence, and chunked exfiltration.
Key points
- MacSync is described as a commercial macOS stealer and remote-access stager distributed mainly through ClickFix social engineering and search malvertising, rather than software exploits.
- The 64-bit Mach-O stager detaches from the terminal, suppresses output, and uses single-byte XOR obfuscation to conceal strings and runtime endpoints.
- It fetches AppleScript over HTTPS and pipes it directly to osascript, avoiding an intermediate script file.
- The payload targets Keychain data, browser cookies, SSH keys, messaging sessions, credentials, and cryptocurrency wallet data.
- The reported attack chain includes LaunchAgent persistence and a helper that requests macOS Screen Recording permissions.
- Stolen data is archived, divided into 10 MB chunks, and uploaded using HTTP PUT with retry logic; temporary files are removed after successful transfer.
- The article says campaigns use independently managed delivery setups and cautions that current evidence does not link all campaigns to one actor or establish that MacSync infrastructure operates directly under ClearFake.
Article Details
- Attack Vectors
- ClickFix lures and search-engine malvertising trick macOS users into copying and running Terminal commands, often presented as software installers, CAPTCHA checks, download errors, or troubleshooting prompts.
- The shell wrapper launches a native Mach-O stager, which retrieves a remote AppleScript payload and pipes it to /usr/bin/osascript for in-memory execution.
- The malware collects credentials and other data, including Keychain contents, browser cookies, SSH keys, Telegram sessions, and cryptocurrency wallet data.
- A subsequent Mach-O component can establish persistence through ~/Library/LaunchAgents/ and exfiltrate the collected archive in 10 MB chunks using HTTP PUT.
- The stager uses XOR-obfuscated strings, runtime endpoint construction, daemonization, and suppressed terminal output to hinder analysis and detection.
- Defensive Notes
- The article identifies SHA-256 9ff32f7c0108e9d27a3b491edf04827b6ca025f44db68aeadc44eeb97c9aab11, MD5 9678f71ea4cccbc3d511dc8d7f24b113, and SHA-1 59508d071661ea70fa5fcbe6f9e2fb72506e57df as hashes of the native Mach-O stager.
- The article identifies the C2 domains drivinguber.com, asia.newsinweb.com, and usa.newsinweb.com, and names newsinweb.com as the fallback root domain.
- The article describes LaunchAgents persistence, use of /tmp/osalogging.zip and /tmp/.httpcode, and cleanup of these temporary files after successful upload.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | drivinguber[.]com | Primary C2 domain used by the MacSync stager. |
| DOMAIN | newsinweb[.]com | Fallback C2 root domain used by MacSync. |
| HOSTNAME | asia[.]newsinweb[.]com | Regional fallback C2 endpoint identified for MacSync. |
| HOSTNAME | usa[.]newsinweb[.]com | Regional fallback C2 endpoint identified for MacSync. |
| MD5 | 9678f71ea4cccbc3d511dc8d7f24b113 | MD5 hash of the MacSync native Mach-O stager sample. |
| SHA1 | 59508d071661ea70fa5fcbe6f9e2fb72506e57df | SHA-1 hash of the MacSync native Mach-O stager sample. |
| SHA256 | 9ff32f7c0108e9d27a3b491edf04827b6ca025f44db68aeadc44eeb97c9aab11 | SHA-256 hash of the MacSync native Mach-O stager sample. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe stager uses single-byte XOR obfuscation to conceal strings, endpoints, headers, and paths.T1030 · Data Transfer Size LimitsThe malware divides the collected archive into 10 MB chunks for transfer.T1048.003 · Exfiltration Over Unencrypted Non-C2 ProtocolThe malware uploads archive chunks using HTTP PUT requests.T1059.002 · AppleScriptThe stager pipes a remote AppleScript payload into /usr/bin/osascript for execution.T1059.004 · Unix ShellThe infection chain uses shell commands, including curl and zsh, to launch stages.T1070.004 · File DeletionAfter successful upload, the malware removes /tmp/.httpcode and /tmp/osalogging.zip.T1071.001 · Web ProtocolsThe stager communicates with C2 over HTTPS using custom request headers.T1105 · Ingress Tool TransferThe stager downloads remote AppleScript modules from its C2 server.T1204.002 · Malicious FileClickFix lures trick victims into copying and running commands in Terminal.T1539 · Steal Web Session CookieThe stealer collects browser session cookies.T1543.001 · Launch AgentThe RAT persists by placing a malicious plist in ~/Library/LaunchAgents/.T1552.004 · Private KeysThe stealer collects SSH keys.T1555.001 · KeychainThe AppleScript payload accesses macOS Keychain data and stored credentials.T1560.001 · Archive via UtilityCollected data is bundled into /tmp/osalogging.zip before exfiltration.T1562.001 · Disable or Modify ToolsThe stager redirects standard input, output, and error streams to /dev/null.
Malware
Vendors
Products
GatekeeperIt uses a modular, multi-tier execution strategy to bypass Apple Gatekeeper, XProtect, and endpoint detection and response (EDR) tools while keeping a minimal footprint on disk.macOSMacSync Stealer is a macOS information-stealing MaaS operation that uses ClickFix lures, malvertising, and multi-stage native Mach-O loaders to evade Apple defenses.XProtectIt uses a modular, multi-tier execution strategy to bypass Apple Gatekeeper, XProtect, and endpoint detection and response (EDR) tools while keeping a minimal footprint on disk.
Tools
Countries
Australiashare of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.CanadaStates accounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.Franceaccounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.Germanyshows the United States accounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.Indiaof detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.JapanUnited States accounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.Netherlandsfollowed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.Singaporefor the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.United Kingdomtelemetry shows the United States accounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and NordicUnited StatesAugust 2026 telemetry shows the United States accounting for the largest share of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic