Multiple State-Aligned Threat Actors Rapidly Adopt BlueMoon Chrome and Windows Exploit Chain
Summary
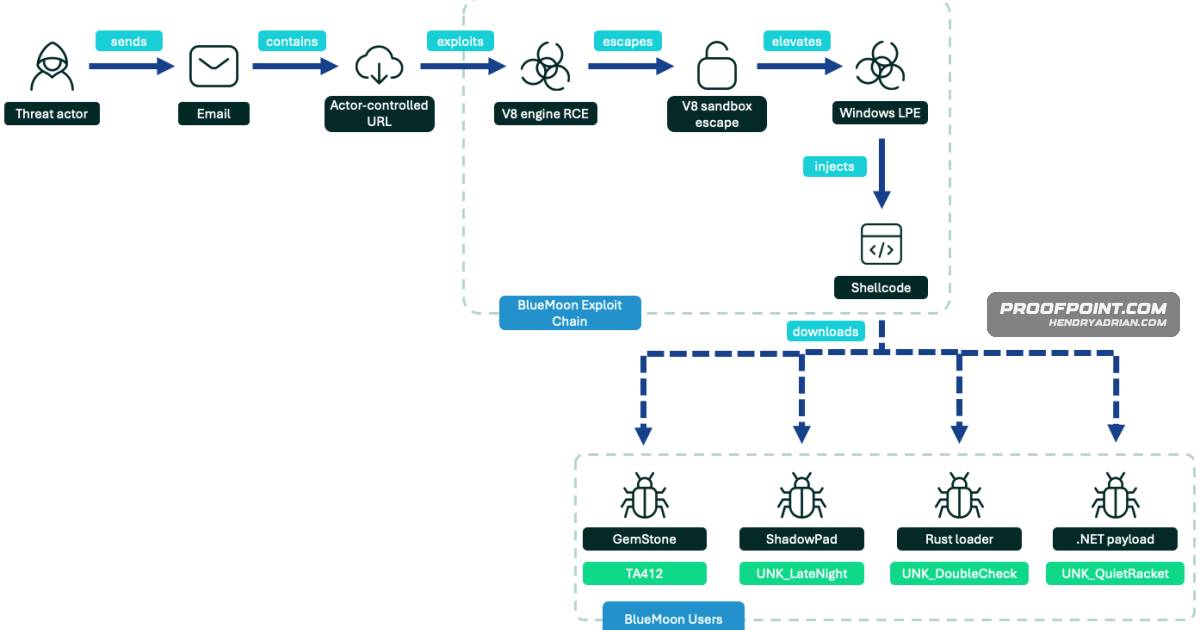
Proofpoint details BlueMoon, an exploit kit chaining Chrome and Windows vulnerabilities that multiple espionage-focused actors used in spearphishing campaigns. The report covers its exploit mechanics, payloads, targets, and detection opportunities.
Key points
- Proofpoint observed four espionage-motivated actor clusters using BlueMoon from late August through September 2026; most activity was assessed to have a suspected China nexus.
- The chain exploits Chrome/Chromium vulnerabilities CVE-2026-85046 and CVE-2026-87491, then uses Windows kernel LPE CVE-2026-85880 to escape the renderer process on selected older Windows builds.
- The Chrome vulnerabilities were patch-gap zero-days: upstream fixes were public before they reached stable browser releases, creating an opportunity for exploit development.
- BlueMoon was delivered through targeted spearphishing links. Observed payloads included GemStone, a browser extension used for surveillance and credential theft, ShadowPad, and other loaders or malware.
- Proofpoint found artifacts consistent with possible AI-assisted development, but said no single indicator conclusively establishes AI involvement.
- Defenders can hunt for the process chain chrome.exe → cmd.exe → curl.exe → msgbox.exe, listed scheduled-task and registry artifacts, and the published ET rules and YARA rule.
Article Details
- Attack Vectors
- Targeted spearphishing links led to actor-controlled pages hosting the exploit kit, often followed by redirects to legitimate websites.
- Lures included internship inquiries, conference outreach, vaccination registration, and aerospace business and quotation requests. Some recipients received rapport-building messages before the exploit link.
- The browser exploit chain combined a V8 type-confusion vulnerability and V8 sandbox escape with a Windows kernel privilege-escalation vulnerability affecting older builds.
- The kernel exploit supported builds 17763, 19041–19045, 20348, and 22000, substantially limiting eligible targets.
- Post-exploitation shellcode injected into the parent browser process to download and execute payloads outside the renderer sandbox.
- Payload delivery included malicious browser-extension installation, DLL-sideloading chains, encrypted payloads loaded into memory, and scheduled-task persistence.
- Defensive Notes
- Hunt for the distinctive default process tree chrome.exe -> cmd.exe -> curl.exe -> msgbox.exe.
- Check for ChromeUpdate.exe or msgbox.exe dropped into %TEMP%.
- Look for scheduled tasks named EdgeCore_AutoUpdate, MicrosoftEdgeUpdatesTaskMachine, Avpcheckup, and GeForceService.
- Check Chrome sessionStorage for the key v8ctf_exp_attempt.
- Hunt for the mutex Dataupcheckinfo.
- Investigate persistence-related writes to HKCU\SOFTWARE\Classes\CLSID\{5D4CFCB7-222C-4CA3-96B6-1F8195FBBB4B}\InprocServer32.
- The supplied MAL_BlueMoon_ExploitKit YARA rule matches three or more listed exploit-code or shellcode markers, including Base64 variants.
- ET rules 2071919–2071924 cover exploit loaders and outbound beacons; rules 2071996–2072001 cover browser-extension registration, heartbeat, ingestion, screenshots, command polling, and command results.
- Both browser vulnerabilities were already fixed in public upstream code but remained unpatched in stable browser releases during the observed activity; upstream fixes alone did not establish downstream protection.
- The extension installer forged valid Secure Preferences HMACs and super_mac values, so those integrity checks did not prevent the observed malicious extension installation.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | airindia[.]fit | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | airliquide[.]lol | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | airproducts[.]ink | UNK_LateNight BlueMoon exploit-delivery domain. |
| DOMAIN | apollohospitals[.]fit | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | attcdn[.]com | TA412 exploit-delivery and payload-download domain. |
| DOMAIN | aurexdefense[.]online | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | bosch-sensortec[.]site | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | brianwilli[.]com | Actor-controlled UNK_DoubleCheck payload-download domain. |
| DOMAIN | checrity[.]com | ShadowPad C2 domain listed in the indicator table. |
| DOMAIN | cyclokinetics[.]online | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | elixnovorem[.]com | UNK_QuietRacket C2 domain. |
| DOMAIN | emcore[.]ink | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | epsilonsystems[.]net | UNK_LateNight BlueMoon exploit-delivery domain. |
| DOMAIN | fracons[.]com | C2 domain used by UNK_DoubleCheck's second-stage payload. |
| DOMAIN | getaiexo[.]com | UNK_QuietRacket C2 domain. |
| DOMAIN | haloengines[.]net | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | jetoptera[.]co | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | joinmacket[.]com | UNK_QuietRacket BlueMoon exploit-delivery infrastructure listed as an indicator. |
| DOMAIN | lindes[.]ink | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | msbenefit[.]com | TA412 exploit-delivery and payload-download domain. |
| DOMAIN | openlumakora[.]com | UNK_QuietRacket BlueMoon exploit-delivery infrastructure listed as an indicator. |
| DOMAIN | precipart[.]ink | UNK_LateNight BlueMoon exploit-delivery domain. |
| DOMAIN | rocketlabusa[.]ink | UNK_LateNight BlueMoon exploit-delivery domain. |
| DOMAIN | secboxes[.]com | TA412 exploit-delivery and payload-download domain. |
| DOMAIN | silvustechnologies[.]online | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | smxtech[.]xyz | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | sncorp[.]fit | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | spectrolab[.]fit | UNK_LateNight BlueMoon exploit-delivery domain. |
| DOMAIN | tcomlp[.]online | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
| DOMAIN | velodynaity[.]com | UNK_QuietRacket C2 domain. |
| DOMAIN | worldview[.]fit | Suspected UNK_LateNight BlueMoon delivery domain based on shared IP resolution. |
dewiinpermata@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
ditjenpajakri2026@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
faizus123@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
faizus123@proton[.]me | UNK_QuietRacket phishing sender address listed as an indicator. | |
firda[.]kemkes@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
jeannifer[.]suryajaya@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
laylowthiago@gmail[.]com | UNK_LateNight phishing sender address listed as an indicator. | |
mariedubois1917@outlook[.]com | UNK_LateNight phishing sender address listed as an indicator. | |
radhikadas07@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
reallifetalktv2@gmail[.]com | UNK_LateNight phishing sender address listed as an indicator. | |
siti[.]nurhaliza2026@outlook[.]com | UNK_QuietRacket phishing sender address listed as an indicator. | |
susan[.]thomas[.]90@outlook[.]com | UNK_LateNight phishing sender address listed as an indicator. | |
zfg[.]rc[.]420@gmail[.]com | UNK_LateNight phishing sender address listed as an indicator. | |
| HOSTNAME | 1a062f4982564d6d19a76884ce8bcbb6[.]r2[.]cloudflarestorage[.]com | Specific Cloudflare R2 bucket used by the Rust loader to download a second DLL-sideloading set. |
| HOSTNAME | asianstudies[.]secboxes[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | black-flower-9250[.]v93xdd5g[.]workers[.]dev | UNK_QuietRacket second C2 channel; no payloads were observed served from it. |
| HOSTNAME | daoahueb[.]workers[.]dev | UNK_QuietRacket payload-download hostname. |
| HOSTNAME | data[.]attcdn[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | dns[.]elixnovorem[.]com | TXT lookup hostname whose encrypted record resolved to UNK_QuietRacket payload infrastructure. |
| HOSTNAME | dns[.]getaiexo[.]com | TXT lookup hostname used by UNK_QuietRacket's recurring C2 loop. |
| HOSTNAME | dns[.]velodynaity[.]com | UNK_QuietRacket C2 TXT lookup hostname listed as an indicator. |
| HOSTNAME | eduac[.]workers[.]dev | UNK_QuietRacket exploit-delivery, download, and C2 hostname. |
| HOSTNAME | evidence[.]msbenefit[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | extension-management-portal[.]centerfjdr658[.]workers[.]dev | GemStone browser-extension C2 hostname. |
| HOSTNAME | extension-management-portal[.]kmjukilo-lkjh[.]workers[.]dev | GemStone browser-extension C2 hostname. |
| HOSTNAME | homepage[.]brianwilli[.]com | UNK_DoubleCheck DLL-sideloading payload-download hostname. |
| HOSTNAME | mailtbox[.]workers[.]dev | UNK_DoubleCheck BlueMoon delivery infrastructure listed as an indicator. |
| HOSTNAME | materials-project[.]secboxes[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | ms[.]checrity[.]com | ShadowPad HTTPS C2 hostname used in UNK_LateNight activity. |
| HOSTNAME | project[.]secboxes[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | publish[.]openlumakora[.]com | UNK_QuietRacket BlueMoon exploit-delivery hostname. |
| HOSTNAME | recommendation-letter[.]secboxes[.]com | TA412 BlueMoon exploit-page hostname. |
| HOSTNAME | royal-surf-a2e2[.]daoahueb[.]workers[.]dev | Served encrypted HTML containing an in-memory .NET payload that established UNK_QuietRacket persistence. |
| HOSTNAME | v93xdd5g[.]workers[.]dev | UNK_QuietRacket C2 hostname listed as an indicator. |
| HOSTNAME | vncdc[.]mailtbox[.]workers[.]dev | UNK_DoubleCheck BlueMoon delivery hostname. |
| HOSTNAME | wcce[.]joinmacket[.]com | UNK_QuietRacket BlueMoon exploit-delivery hostname. |
| HOSTNAME | yhv41nji[.]workers[.]dev | UNK_QuietRacket BlueMoon exploit-delivery hostname. |
| IPV4 | 79[.]133[.]56[.]90 | Fallback ShadowPad C2 server. |
| SHA256 | 295fc584f75e94108c9be945977db33ed80421f5d374eab188587c911dffd915 | UNK_LateNight msgbox.exe ShadowPad loader. |
| SHA256 | 353b5bd2780c1b0c07c1283d83cf16cf1e9ec226c17b2d09d56848893f9d98ee | GemStone background.js malicious extension service worker. |
| SHA256 | 3594ad58fb6217fafe9839e53999a90608c2e9f335fa20aece3d53f8c0802726 | UNK_DoubleCheck SysPr.prx encrypted payload blob. |
| SHA256 | 3ec3151d8d1278ed966941ac89ea495ef6a80c70613dd9138cc85fc28c9df432 | UNK_DoubleCheck krita.dll infection-chain artifact. |
| SHA256 | 6e6378d8d404166da89d982e80bc52e19a3f677201258dec1775f100a027a92d | Malicious artifact listed in the UNK_DoubleCheck indicator table; individual filename not disclosed. |
| SHA256 | 779b3e1a470e589d492b99154ba11622fbaebb19b3de694f660c725411b7096d | TA412 driver-html.js BlueMoon exploit JavaScript. |
| SHA256 | 7d6f6dcb17a423bdd7715f8a4e34f2939501a761bc9bf7aa005f805ef1f82288 | TA412 ChromeUpdate.exe or msgbox.exe extension installer. |
| SHA256 | 8453c42904b7b2fea5671b7bff06b2d937632ae29545fd11bc13095627a2805f | UNK_QuietRacket Indostartupexpo.js BlueMoon exploit JavaScript. |
| SHA256 | 87b6b24c06f99900a8aa579caedee1e402015884c925a98dcfb0fb38dfa2de22 | UNK_QuietRacket GFExperienceUpdate.dll malicious loader. |
| SHA256 | a4a6a04d85eca8d584d939d2437c85a4f291207d8042f2ec002838e336b72ef5 | UNK_LateNight Index.js BlueMoon exploit JavaScript. |
| SHA256 | ac6806c89e294f390838cb07c015dabec1c8ada06ce5161a0ad50b8a72828141 | UNK_DoubleCheck calibre-launcher.dll infection-chain artifact. |
| SHA256 | ac6bbc4b1f1c62e308781329183a46e18f454c27e66bffa09f343b53ac622b69 | UNK_DoubleCheck font-01.js BlueMoon exploit JavaScript. |
| SHA256 | b34802a646fc4a8f07ffa09a5fda8bf7327446b22e3d7bb5163dafa1e2a8bb2b | UNK_QuietRacket Loader.js BlueMoon exploit JavaScript. |
| SHA256 | bc7d24f5cf8937b334966201bdcce8ca9bab6ec5889d40a399d4094dcad73360 | UNK_LateNight mctsetup64.dll infection-chain artifact. |
| SHA256 | e950d03c58d49e28e31df8afeefca1f3b3d2cd6b697c40adfee1a4f6fe18f004 | TA412 dist.zip malicious browser-extension archive. |
| SHA256 | f3c64014221a58f3fde88e562662dbd5a1b3dd2b59c86e9e2bc5cb8f671664e7 | UNK_QuietRacket GFExperienceUpdate.dll malicious loader. |
| SHA256 | ff1b49aaec994f4c11f2c9331e739abb4bc3d6abf66ec50ce99709fba35d782b | TA412 ChromeUpdate.exe or msgbox.exe extension installer. |
| URL | hxxps[:]//1a062f4982564d6d19a76884ce8bcbb6[.]r2[.]cloudflarestorage[.]com/datago/krita[.]dll | Specific cloud-hosted DLL URL for UNK_DoubleCheck's second DLL-sideloading set. |
| URL | hxxps[:]//1a062f4982564d6d19a76884ce8bcbb6[.]r2[.]cloudflarestorage[.]com/datago/krita[.]exe | Specific cloud-hosted executable URL for UNK_DoubleCheck's second DLL-sideloading set. |
| URL | hxxps[:]//1a062f4982564d6d19a76884ce8bcbb6[.]r2[.]cloudflarestorage[.]com/datago/SysPr[.]prx | Specific cloud-hosted payload blob URL for UNK_DoubleCheck's second DLL-sideloading set. |
| URL | hxxps[:]//api-prod[.]secboxes[.]com/download | TA412 payload download URL listed in the indicator table. |
| URL | hxxps[:]//app[.]eduac[.]workers[.]dev/Service | UNK_QuietRacket DLL-sideloading pair download URL. |
| URL | hxxps[:]//app[.]eduac[.]workers[.]dev/Updateac | UNK_QuietRacket DLL-sideloading pair download URL. |
| URL | hxxps[:]//download[.]secboxes[.]com/dist[.]zip | TA412 malicious extension archive download URL. |
| URL | hxxps[:]//evidence[.]msbenefit[.]com/msgbox[.]exe | TA412 post-exploitation installer download URL. |
| URL | hxxps[:]//homepage[.]brianwilli[.]com/d/{wint[.]exe,calibre-launcher[.]dll,85rY[.]dat,SysPr[.]prx} | Literal curl URL expression used by UNK_DoubleCheck to download four infection-chain files. |
| URL | hxxps[:]//homepage[.]brianwilli[.]com/d/85rY[.]dat | UNK_DoubleCheck infection-chain artifact download URL. |
| URL | hxxps[:]//homepage[.]brianwilli[.]com/d/calibre-launcher[.]dll | UNK_DoubleCheck DLL-sideloading payload download URL. |
| URL | hxxps[:]//homepage[.]brianwilli[.]com/d/SysPr[.]prx | UNK_DoubleCheck encrypted payload blob download URL. |
| URL | hxxps[:]//homepage[.]brianwilli[.]com/d/wint[.]exe | UNK_DoubleCheck DLL-sideloading executable download URL. |
| URL | hxxps[:]//project[.]secboxes[.]com/ChromeUpdate[.]exe | TA412 post-exploitation installer download URL. |
| URL | hxxps[:]//recommendation-letter[.]secboxes[.]com/ChromeUpdate[.]exe | TA412 post-exploitation installer download URL. |
| URL | hxxps[:]//small-union-7018[.]daoahueb[.]workers[.]dev/ | UNK_QuietRacket DLL-sideloading pair download URL. |
| URL | hxxps[:]//snowy-block-ae0a[.]daoahueb[.]workers[.]dev/ | UNK_QuietRacket DLL-sideloading pair download URL. |
| URL | hxxps[:]//zki0y83[.]msbenefit[.]com/feed | TA412 download URL listed in the indicator table. |
MITRE ATT&CK
T1016.001 · Internet Connection DiscoveryGemStone queried public IP identification services to incorporate the victim's public IP into its registration identifier.T1027 · Obfuscated Files or InformationBlueMoon variants encoded or obfuscated components; subsequent payloads used XOR, AES, RC4, Base64, and ChaCha20.T1036 · MasqueradingGemStone masqueraded as an AI-powered browsing companion by Google Gemini.T1040 · Network SniffingThe ShadowPad payload was reported to sniff network traffic.T1041 · Exfiltration Over C2 ChannelGemStone exfiltrated keystrokes, cookies, storage entries, navigation events, and session metadata through its C2 ingest endpoint, with screenshots uploaded separately.T1053.005 · Scheduled TaskPersistence used scheduled tasks including EdgeCore_AutoUpdate and GeForceService.T1055 · Process InjectionBlueMoon wrote executable code into the parent browser process and started a remote thread; the ShadowPad loader also injected decrypted contents into processes such as wmpnetwk.exe.T1056.001 · KeyloggingGemStone injected a recorder that captured keydown, input, change, and paste events across eligible tab frames.T1059.003 · Windows Command ShellPost-exploitation commands used cmd.exe to invoke curl and run downloaded executables.T1068 · Exploitation for Privilege EscalationThe kernel exploit enabled SeDebugPrivilege in the renderer token using CVE-2026-85880.T1070.004 · File DeletionThe UNK_LateNight loader immediately overwrote its TMP payload file after reading and decrypting it.T1071.001 · Web ProtocolsGemStone used HTTP C2 endpoints, and ShadowPad beaconed over HTTPS using a binary C2 protocol.T1071.004 · DNSUNK_QuietRacket repeatedly retrieved encrypted TXT records through DNS-over-HTTPS to resolve its C2 infrastructure.T1082 · System Information DiscoveryThe reconnaissance DLL collected Windows version and build information and the kernelbase.dll build version to gate exploitation.T1105 · Ingress Tool TransferBlueMoon downloaded operator-provided executables, and subsequent loaders fetched malicious extensions and additional payload sets.T1112 · Modify RegistryThe UNK_LateNight chain stored a payload copy in the registry, and UNK_DoubleCheck wrote a CLSID InprocServer32 key for persistence.T1113 · Screen CaptureGemStone captured the visible tab on command or when monitored keywords were found.T1140 · Deobfuscate/Decode Files or InformationLoaders decrypted encrypted TMP and SysPr.prx payloads and decoded encrypted HTML content before execution.T1176.001 · Browser ExtensionsTA412 installed GemStone as a malicious Chromium browser extension by rewriting browser preferences with forged integrity values.T1203 · Exploitation for Client ExecutionBlueMoon exploited V8 type confusion and a V8 sandbox escape after recipients opened exploit-delivery links.T1539 · Steal Web Session CookieGemStone's CAPTURE_COOKIES command collected cookies from every accessible cookie store.T1562.001 · Disable or Modify ToolsShadowPad unhooked 20 network-monitoring functions to remain stealthy.T1566.002 · Spearphishing LinkAll four clusters sent targeted phishing emails containing links to BlueMoon exploit pages.T1574.002 · DLL Side-LoadingUNK_LateNight, UNK_DoubleCheck, and UNK_QuietRacket delivered DLL-sideloading pairs.T1620 · Reflective Code LoadingBlueMoon reflectively loaded reconnaissance and kernel-exploit DLLs; UNK_QuietRacket also loaded a decrypted .NET assembly into memory.
CVE
CVE-2026-85046targets three vulnerabilities: a type-confusion vulnerability in Chromium’s V8 JavaScript engine (CVE-2026-85046), a V8 sandbox escape (CVE-2026-87491), and a Windows kernel Local Privilege Escalation (LPE)CVE-2026-85880a Windows kernel Local Privilege Escalation (LPE) zero-day present in older Windows builds (assigned CVE-2026-85880), which is used to escape the renderer process.CVE-2026-87491vulnerability in Chromium’s V8 JavaScript engine (CVE-2026-85046), a V8 sandbox escape (CVE-2026-87491), and a Windows kernel Local Privilege Escalation (LPE) zero-day present in older Windows builds
People
Threat Actors
APT31Listed as an alternate name for TA412, the China-aligned actor that delivered GemStone through BlueMoon.TIDE CASTLEListed as an alternate name for TA412, the China-aligned actor that delivered GemStone through BlueMoon.UNK_DoubleCheckSuspected espionage-motivated cluster targeting a Vietnamese manufacturing entity from 2026-09-02 through a compromised government sender and a Rust loader chain. Proofpoint did not attribute it to a specific country.UNK_LateNightProofpoint's temporary designation for a China-aligned espionage cluster using BlueMoon from 2026-09-02 against US aerospace companies to deliver ShadowPad.UNK_QuietRacketSuspected China-aligned espionage cluster using BlueMoon from 2026-09-03 against government, consulting, and financial organizations in Indonesia and Singapore, delivering unnamed custom malware.
Malware
Vendors
CloudflareThe observed GemStone samples contacted a Cloudflare Worker domain for C&C.GoogleProofpoint Threat Research would like to thank Google Threat Intelligence Group (GTIG), Microsoft Threat Intelligence Center (MSTIC), and Volexity for their collaboration.MicrosoftProofpoint Threat Research would like to thank Google Threat Intelligence Group (GTIG), Microsoft Threat Intelligence Center (MSTIC), and Volexity for their collaboration.
Products
BraveThe installer then enumerates installed Chromium-family browsers, specifically Google Chrome, Microsoft Edge, Brave, and Vivaldi.ChromiumThe exploit chain targets three vulnerabilities: a type-confusion vulnerability in Chromium’s V8 JavaScript engine (CVE-2026-85046), a V8 sandbox escape (CVE-2026-87491), and a Windows kernel Local Privilege EscalationGoogle ChromeProofpoint identified four espionage-motivated threat actors employing a new exploit kit that chains multiple Chrome browser and Microsoft Windows vulnerabilities.Microsoft Edgevulnerabilities present in the latest stable versions of Chrome and Chromium-based browsers (such as Microsoft Edge), it was paired with a Windows LPE vulnerability present only in older Windows builds.Microsoft WindowsProofpoint identified four espionage-motivated threat actors employing a new exploit kit that chains multiple Chrome browser and Microsoft Windows vulnerabilities.Mozilla Firefoxis the ShadowPad backdoor that unhooks 20 network monitoring functions to remain stealthy, steals Firefox profile data, sniffs network traffic, and beacons over HTTPS to ms.checrity[.]com using a binary C&CServer 2019Windows 10 1809 (Oct 2018 Update) / Server 2019VivaldiThe installer then enumerates installed Chromium-family browsers, specifically Google Chrome, Microsoft Edge, Brave, and Vivaldi.Windows 10Windows 10 1809 (Oct 2018 Update) / Server 2019Windows 11Windows 11 21H2 (initial release)Windows Server 2022Windows Server 2022
Tools
Countries
ChinaThe first observed cluster using the BlueMoon exploit kit was the China-aligned threat actor TA412 (JungleBamboo, Violet Typhoon, APT31, TIDE CASTLE) on 28 August 2026.IndonesiaUNK_QuietRacket activity targets Singapore and Indonesia to deliver unknown custom malwareSingaporeUNK_QuietRacket activity targets Singapore and Indonesia to deliver unknown custom malwareUnited StatesBeginning on 28 August 2026, TA412 repeatedly targeted a small number of non-governmental organizations (NGOs), mining companies, and physical commodity trading firms in the United States using the BlueMoon exploit kit.Vietnam
Industries
AerospaceChina-aligned UNK_LateNight targets US aerospace to deliver ShadowPad backdoor using BlueMoonConsultingthreat actor that Proofpoint tracks as UNK_QuietRacket used BlueMoon in activity targeting government, consulting, and financial sector organizations in Indonesia and Singapore.Defense industrial baseThe phishing emails were themed around Business-to-Business (B2B) and Request for Quotation (RFQ) inquiries specifically related to the US defense industrial base.Financial ServicesProofpoint tracks as UNK_QuietRacket used BlueMoon in activity targeting government, consulting, and financial sector organizations in Indonesia and Singapore.GovernmentTA412 is a China-aligned state-sponsored threat actor previously indicted by the US government in 2024 for conducting economic espionage, transnational oppression, and foreign intelligence gathering on behalf of China’sManufacturingUNK_DoubleCheck targets Vietnamese manufacturing company with Rust loader infection chainMiningInitial adopter TA412 targets US NGOs, mining, and physical commodity trading organizations with BlueMoonNon-governmental organizationsBeginning on 28 August 2026, TA412 repeatedly targeted a small number of non-governmental organizations (NGOs), mining companies, and physical commodity trading firms in the United States using the BlueMoon exploit kit.Physical commodity tradingInitial adopter TA412 targets US NGOs, mining, and physical commodity trading organizations with BlueMoon