
CVE-2026-50610 Lets Standard Users Gain SYSTEM on Acer Devices
Summary
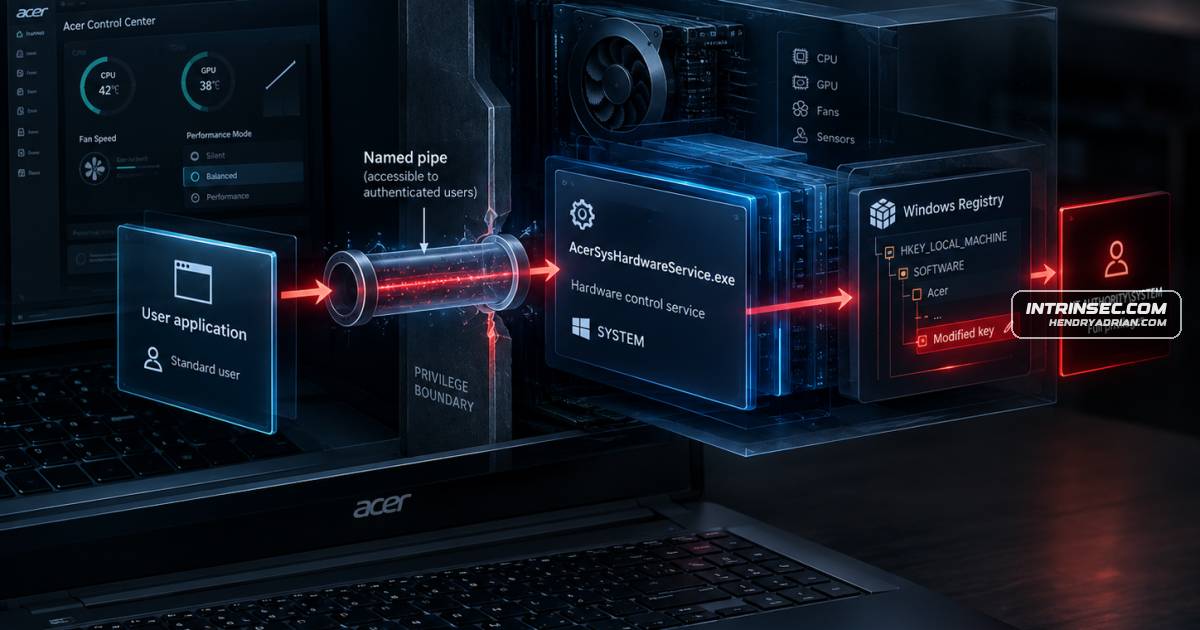
A technical investigation reports that Acer System Monitor’s SYSTEM service accepts commands from standard users over a named pipe, enabling arbitrary registry writes and local privilege escalation to SYSTEM.
Key points
- The article identifies AcerSysHardwareService.exe, used by NitroSense and PredatorSense, as the vulnerable SYSTEM service.
- The systemmonitoring_hardware_service_ named pipe allows Authenticated Users to read, write, and execute.
- The investigation reports that the service does not impersonate pipe clients or check their privileges.
- A pipe command lets an unprivileged user create or modify registry values as SYSTEM.
- The proof of concept uses the registry-write capability to configure utilman.exe to launch cmd.exe, then obtains a SYSTEM shell from the Windows login screen.
- Reported affected versions are AcerSysHardwareService.exe 1.0.1018.13 and 1.0.1019.0, in the NitroSense 5.1.361 engine; the vulnerability was privately reported to Acer in May 2026.
Article Details
- Attack Vectors
- A standard user writes commands to an Acer System Monitor named pipe that is writable by Authenticated Users; the service processes those commands as NT AUTHORITY\SYSTEM without impersonating or checking the caller’s rights.
- The vulnerable pipe allows a standard user to create or modify arbitrary registry values as SYSTEM.
- The proof of concept writes an Image File Execution Options debugger value for utilman.exe pointing to cmd.exe; launching the accessibility feature from the Windows login screen opens a SYSTEM shell before authentication.
- Defensive Notes
- The article recommends that users and defenders running NitroSense, PredatorSense, or Acer System Monitor follow the guidelines on Acer’s website; it does not specify particular remediation steps.
MITRE ATT&CK
T1059.003 · Windows Command ShellThe proof of concept launches cmd.exe as NT AUTHORITY\SYSTEM from the Windows login screen.T1068 · Exploitation for Privilege EscalationCVE-2026-50610 lets a standard user exploit the Acer System Monitor service to reach NT AUTHORITY\SYSTEM.T1112 · Modify RegistryThe proof of concept uses the vulnerable service to write an Image File Execution Options registry value as SYSTEM.T1546.012 · Image File Execution Options InjectionThe proof of concept sets a debugger for utilman.exe through Image File Execution Options, causing cmd.exe to launch when the accessibility feature is invoked.
CVE
People
Vendors
Products
Acer System MonitorOn Acer machines that is NitroSense / PredatorSense, built on a shared engine called Acer System Monitor.Microsoft Windowsa background service running as LocalSystem: the most powerful account on Windows.NitroSenseOn Acer machines that is NitroSense / PredatorSense, built on a shared engine called Acer System Monitor.PredatorSenseOn Acer machines that is NitroSense / PredatorSense, built on a shared engine called Acer System Monitor.