Research Finds Overprivileged Kubernetes Operators, Including a High-Severity IBM Flaw
Summary
Palo Alto Networks’ OperTraitor analysis found excessive permissions in Kubernetes operators, including cluster-wide secret access in IBM’s Prometurbo operator, patched under CVE-2026-6389. Researchers warn outdated OperatorHub components and agentic AI could amplify RB
Key points
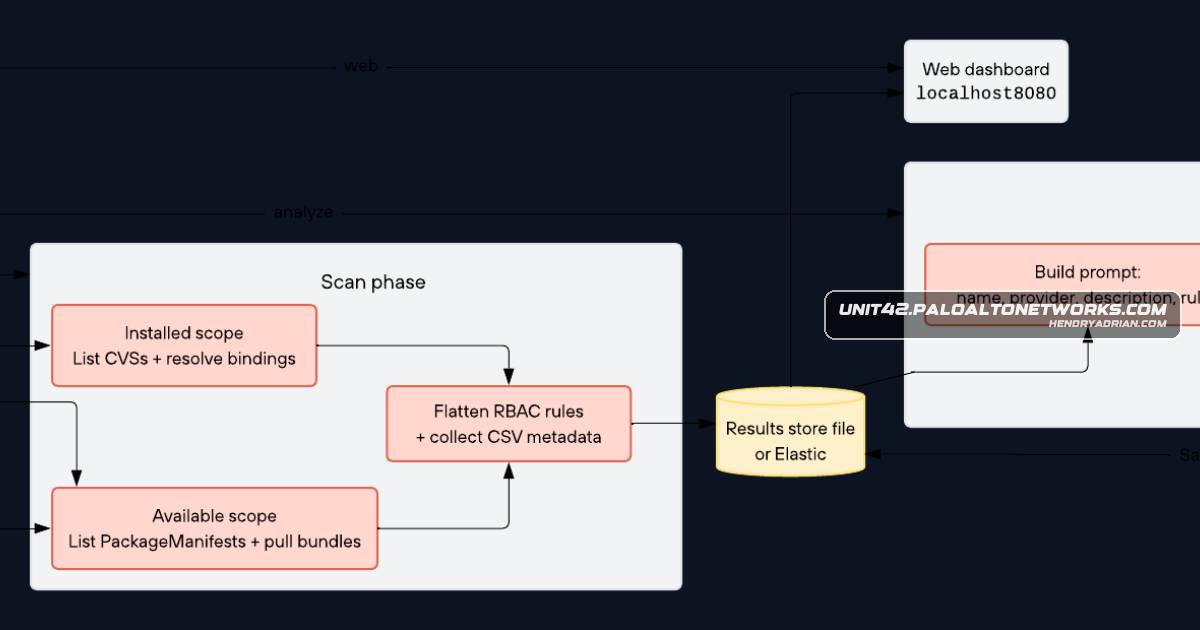
- OperTraitor analyzes operator RBAC permissions against documented functionality and assigns risk scores; the researchers found slightly over 5% of reviewed operators requested excessive privileges.
- The Prometurbo operator had cluster-wide read access to Kubernetes secrets, potentially exposing credentials and tokens across unrelated namespaces if compromised.
- IBM fixed the Prometurbo permissions and published CVE-2026-6389, rated High with a CVSS score of 8.8.
- The Datadog operator also had broad secret and RBAC permissions; Datadog explained its design rationale and documented the settings and mitigations for users.
- Researchers warn that outdated or abandoned operators in OperatorHub can remain available even when vendors publish newer versions elsewhere.
- Recommended safeguards include verifying operator sources and maintenance status, limiting permissions to required namespaces, auditing and reducing RBAC privileges, and monitoring service-account activity.
- The article warns that LLM-enabled and agentic operators could magnify the impact of excessive permissions, and recommends strict network and permission controls.
Article Details
- Attack Vectors
- A compromised Kubernetes operator could use excessive service-account RBAC permissions to access resources beyond the namespaces it manages. The article describes container image supply chain compromise, dependency vulnerabilities, and hijacking of an underlying node as possible routes to operator compromise; it does not report an observed attack.
- The Prometurbo operator's ClusterRole granted cluster-wide get, list, and watch access to secrets. If the operator were compromised, an attacker could read credentials and certificates from unrelated namespaces.
- OperTraitor flagged the Datadog operator for cluster-wide access to secrets and permissions involving ClusterRoles and ClusterRoleBindings.
- Outdated, overly permissive operators remaining available through OperatorHub and the Operator Lifecycle Manager could be deployed despite newer versions being available elsewhere.
- Defensive Notes
- IBM resolved the reported Prometurbo RBAC issue by scoping the operator's permissions more narrowly.
- Datadog explained that user-defined secret names complicate advance restriction of its operator's access; it added documentation explaining its RBAC settings and mitigations.
- Verify operator versions against vendor documentation and maintained distribution channels rather than implicitly trusting default registry listings.
- Where feasible, use namespace-scoped operators, limit ClusterRoles and ClusterRoleBindings, and audit and downscope vendor-provided RBAC manifests.
- Monitor Kubernetes Audit Logs for anomalous operator service-account behavior, including secret access in unrelated namespaces or API requests from unexpected IP addresses.
- For LLM-enhanced operators, restrict network access and limit the context and permissions provided to underlying LLMs.
CVE
Vendors
DatadogCase Study 2: The Trade-Off Between Security and User Experience (UX) (Datadog Operator)IBMUsing our tool, we identified a High-severity vulnerability (CVE-2026-6389, CVSS 8.8) in IBM's Turbonomic platformPalo Alto NetworksPalo Alto Networks customers are better protected from the threats discussed in this article through the following products:
Products
Cortex CloudCortex CloudDatadog operatorCase Study 2: The Trade-Off Between Security and User Experience (UX) (Datadog Operator)KubernetesKubernetes operators are coded to drastically reduce operational toil by acting as automated site reliability engineers.Operator Lifecycle Manageror ArtifactHub. However, their older, vulnerable versions remain easily accessible through the Operator Lifecycle Manager (OLM).OperatorHubOperTraitor ingests raw role-based access control (RBAC) configurations directly from locally installed operators and the OperatorHub catalog.Prometurbo operatorCase Study 1: Excessive Secret Access (Prometurbo Operator - IBM)TurbonomicUsing our tool, we identified a High-severity vulnerability (CVE-2026-6389, CVSS 8.8) in IBM's Turbonomic platform