cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

728 articles

Security Report · darkowl.com

DarkOwl Analysis Finds Five Darknet Market Clusters and Shifting Listing Patterns

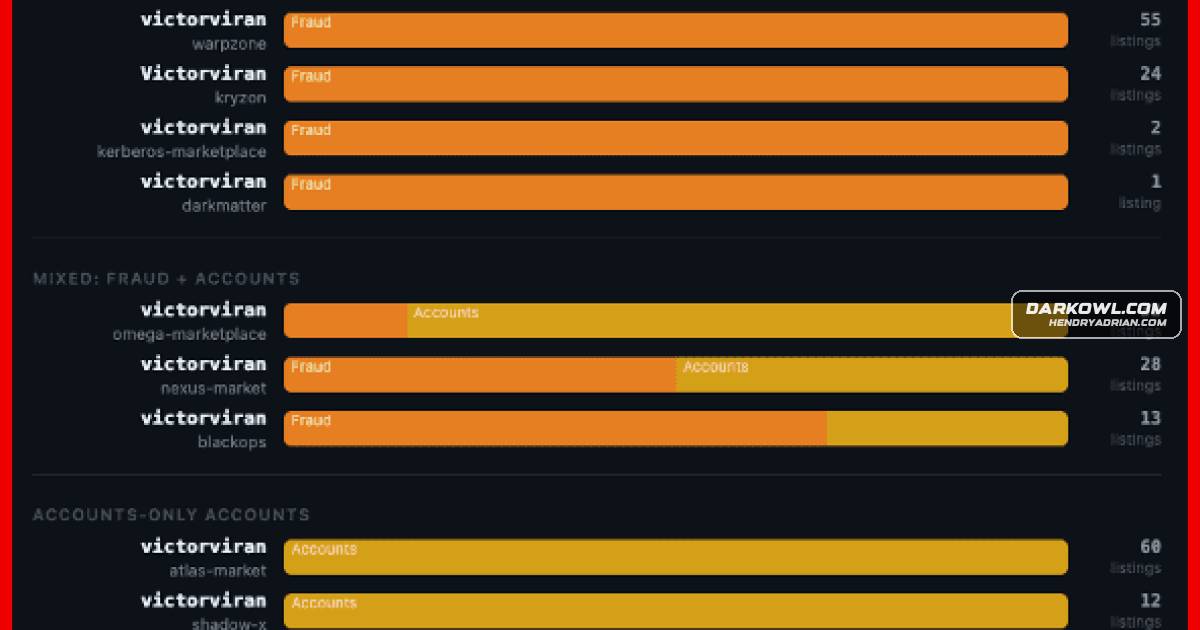
DarkOwl analyzed listings from 53 darknet markets from January to April 2026, grouping them into five profiles and tracking changes in listing mix and volume that may help investigators monitor vendor shifts and market activity.
Jun 11, 2026
Security Report · sysdig.com

Sysdig Report Warns Vulnerability Growth Is Outpacing Security Teams

Sysdig’s 2026 report says exploitable in-use vulnerabilities among its users fell 75% year over year, but vulnerability growth is outpacing teams. The article urges stronger runtime defenses and agentic AI remediation under human-set guardrails.

Jun 11, 2026
Security Report · blog.sekoia.io

Sekoia Traces APT28’s Tradecraft Evolution From X-Agent to LLM-Driven Malware

Sekoia’s TDR team reviews APT28’s tradecraft across two decades, highlighting disposable implants, compromised edge routers, cloud-based command-and-control and LameHug, whose attribution to APT28 is assessed with medium confidence.

Jun 11, 2026
Security Report · sekoia.com

APT28’s Tradecraft Evolves from X-Agent to LLM-Driven Malware

Sekoia traces two decades of APT28 operations, detailing its shift to disposable implants and compromised routers, the return of custom backdoors, and LameHug, an infostealer that uses an LLM to generate commands.

Jun 11, 2026
Security Report · darktrace.com

Darktrace Report Finds Widespread Cyber Incidents and Phishing in Sports

Darktrace’s sports-sector research reports frequent cyber incidents and elevated phishing, and highlights risks from compromised accounts, ransomware, AI use, and third-party access. It recommends visibility across IT and OT and rehearsed incident response.

Jun 11, 2026
Security Report · blog.eclecticiq.com

EclecticIQ Report Warns of Escalating Cyber Risks Amid Regional Conflicts

EclecticIQ's Q1 2026 assessment warns of persistent Chinese access to critical networks, Russian threats to European OT, and continued Iranian-aligned cyber activity, while recommending stronger edge-device, identity, OT, and supply-chain defenses.

Jun 11, 2026
Security Report · infoblox.com

Residential Proxy Traffic Appeared in 65% of Infoblox Customer Networks

Infoblox found residential-proxy-related DNS queries in over 65% of its cloud customers, rising about 25% from January 2025 to April 2026. It warns that unauthorized proxy use can expose organizations to abuse and added security workload.

Jun 9, 2026
Security Report · bleepingcomputer.com

XBOW Says Anthropic’s Mythos Preview Excels at Vulnerability Discovery

In a sponsored evaluation, XBOW says Mythos Preview performed strongly at source-code vulnerability discovery and native-code analysis, but was less reliable at exploit validation and command-safety judgments, and can be costly to run.

Jun 9, 2026
Security Report · dti.domaintools.com

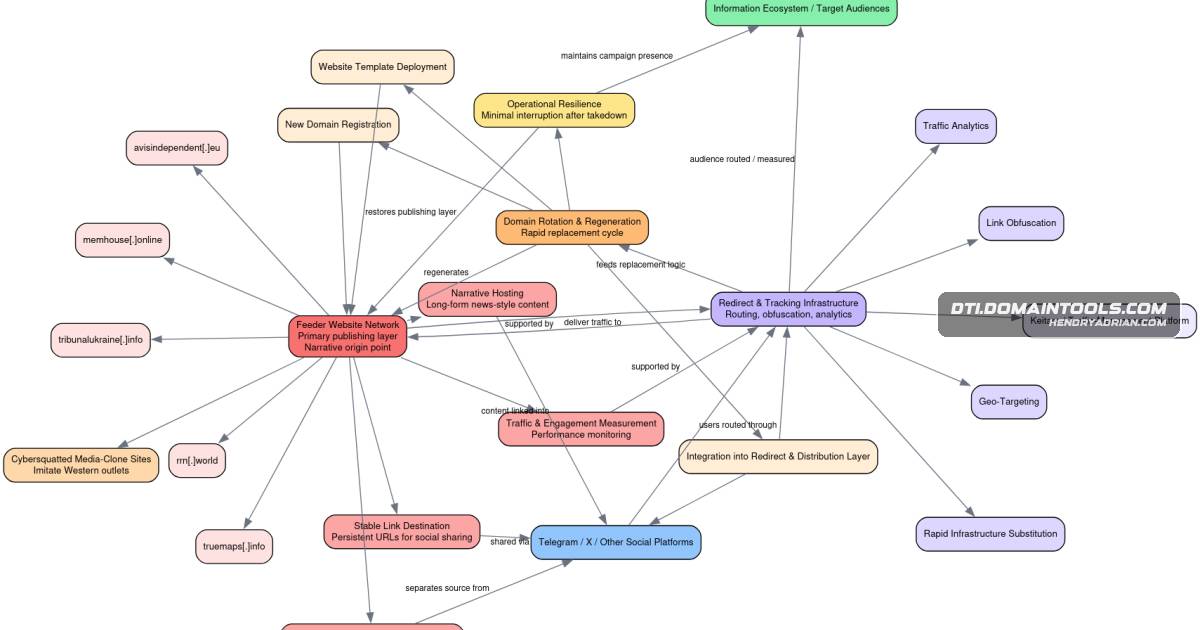
Report Details Doppelgänger’s Resilient Influence Operations and Multi-Platform Reach

A DomainTools report describes how the Russian-linked Doppelgänger network uses spoofed media sites, Telegram channels and coordinated X accounts to spread narratives, estimating typical reach of 1.5–2.7 million users per wave.

Jun 5, 2026
Security Report · securityweek.com

Adversa Finds Only 11% of 100 AI Agents Both Capable and Well-Defended

Adversa’s assessment of 100 AI agents across ten categories found only 11% both capable and well-defended, while 98% had access to private data, untrusted content and outbound actions. It recommends focusing defenses on egress, identity and irreversible actions.

Jun 3, 2026
Security Report · opensourcemalware.com

Software Supply-Chain Malware Trends: January–May 2026

An analysis of malicious-package reports through May 18, 2026, finds similar growth in npm and PyPI malware, rising account-takeover activity, and malicious ClawHub skills targeting varied groups.

Jun 3, 2026
Security Report · darkowl.com

Darknet Vendor Analysis Finds Distinct Selling Patterns and Limits of Username-Based Tracking

An analysis of 7,314 vendors across 53 darknet markets found distinct drug and fraud selling patterns and showed that usernames alone are unreliable for linking vendors across platforms.

Jun 3, 2026
Security Report · recordedfuture.com

Report Links Handala Personas to MOIS Physical Threat and Influence Operations

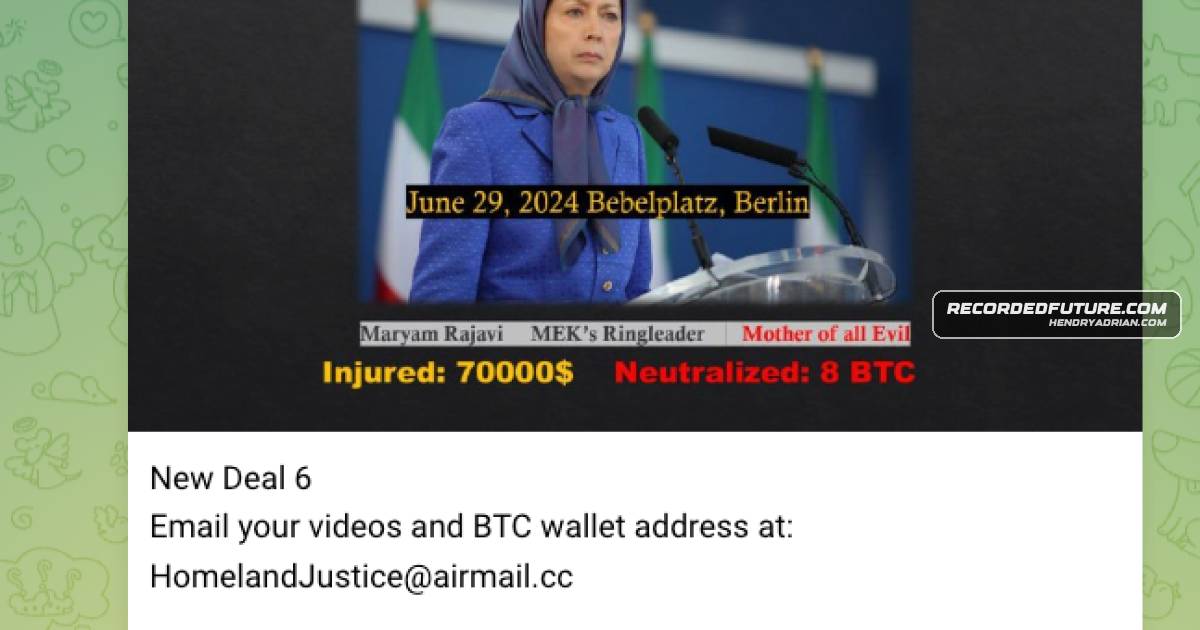
Recorded Future’s Insikt Group assesses that Iran’s MOIS likely coordinates Handala cyber, physical-threat, and influence personas, using cross-amplification to recruit proxies and target US and Israeli interests.

Jun 3, 2026
Security Report · acronis.com

Acronis Report Finds Backup Delays and Deep MSP Hierarchies Can Undermine Recovery Readiness

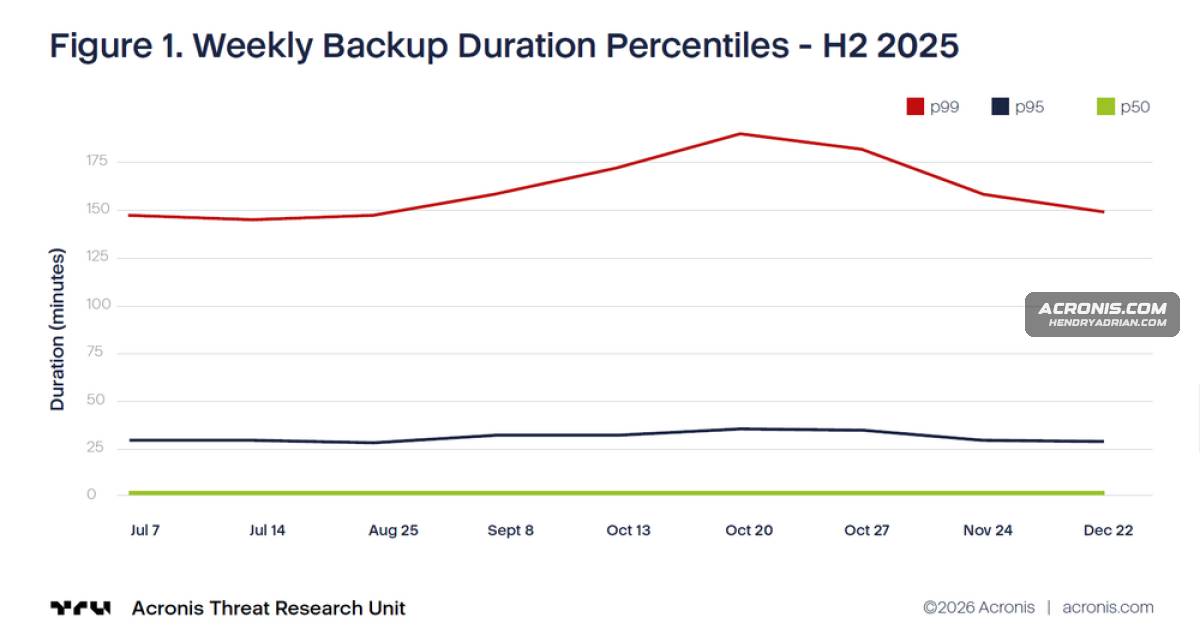
Analysis of Acronis H2 2025 telemetry finds that long backup runtimes and deeply nested MSP tenant structures can leave recovery points older than expected. It recommends measuring on-time completion, planning for runtime tails, and testing restores.

Jun 3, 2026
Security Report · securityweek.com

Two Reports Offer Competing Explanations for Cybersecurity’s Growing Crisis

A CSA survey commissioned by Miggo links security gaps to poor runtime visibility and slow vulnerability remediation. FireMon’s report instead points to weak firewall-policy oversight, including unused and undocumented rules.

Jun 2, 2026
Security Report · cyberscoop.com

Election Threats Target Campaign Systems, Not Voting Machines

Check Point’s report says election threats are focused on campaign email, fundraising platforms, and election-themed websites rather than voting systems. It cites email in 82% of malicious attacks and warns AI is making phishing and manipulated content more convincing.

Jun 1, 2026
Security Report · bleepingcomputer.com

Flare Finds DDoS-for-Hire Ads Rose Tenfold as Services Become More Commercialized

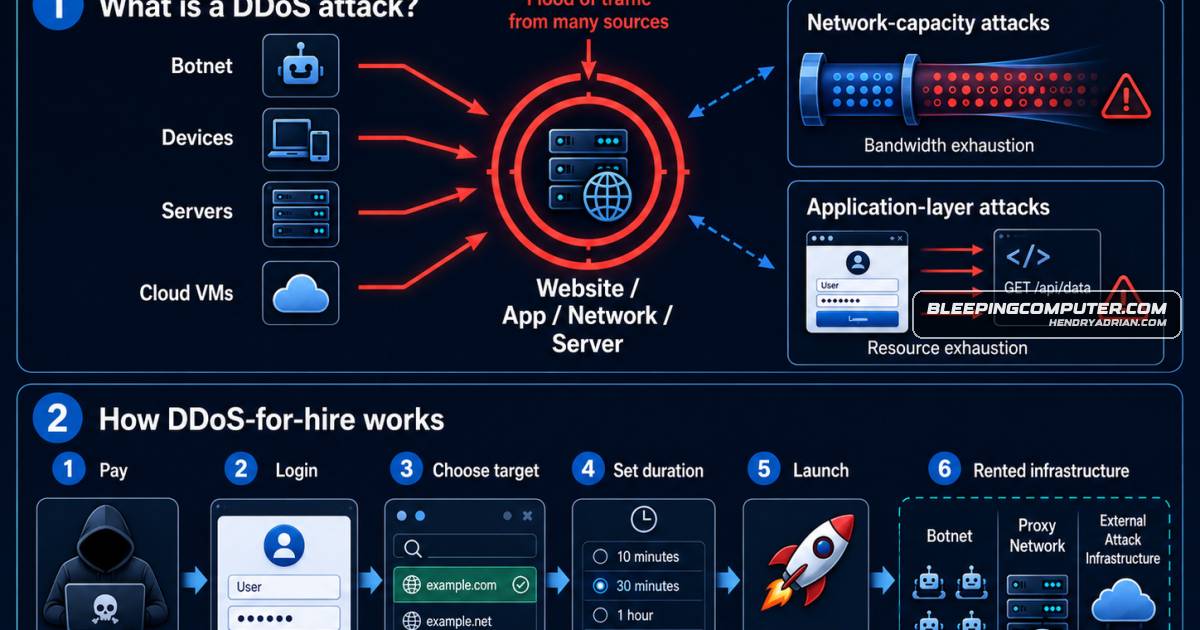
Flare compared underground DDoS activity from early 2023 and 2026, finding roughly ten times as many high-signal service ads. The ads increasingly promote packaged platforms, automation, support, pricing tiers, and reseller options.

May 29, 2026
Security Report · unit42.paloaltonetworks.com

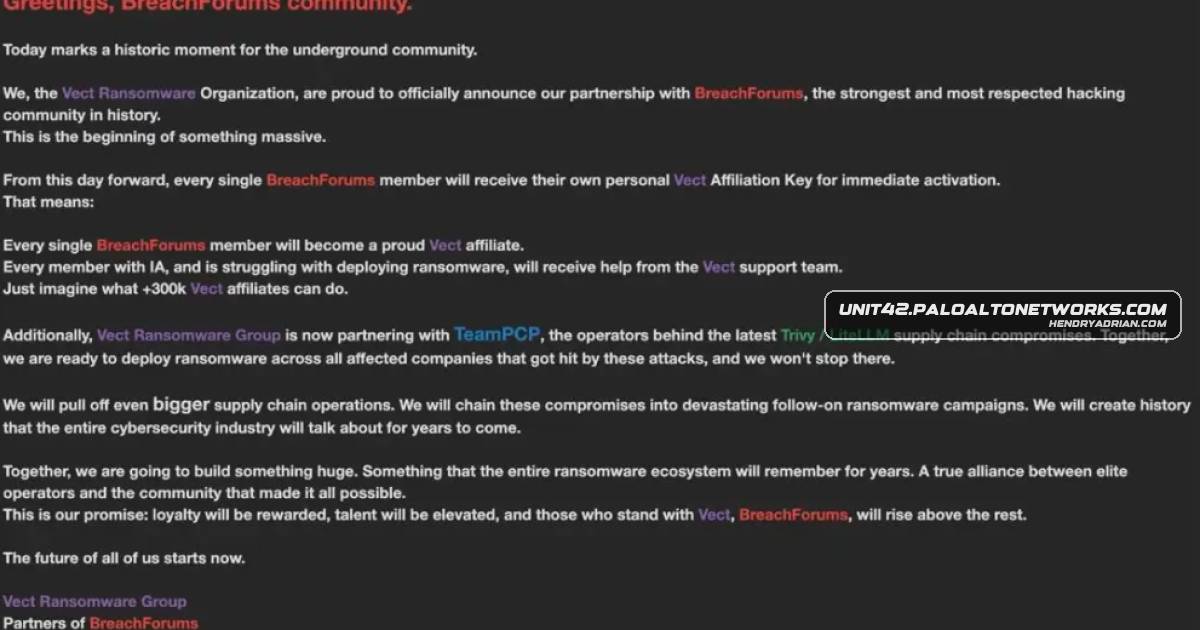
Data-Only Extortion Is Rising as Criminals Move Beyond Encryption

Unit 42 describes a shift toward data-only extortion, outlines actors’ supply-chain and vishing tactics, and recommends defenses including egress monitoring, phishing-resistant MFA, and stronger CI/CD controls.

May 28, 2026
Security Report · wiz.io

Wiz Finds Post-Quantum Cryptography Adoption Still Lagging Across Cloud and Company Systems

Wiz’s analysis finds limited post-quantum cryptography adoption across cloud services and company systems, with key exchange support more advanced than digital-signature migration.

May 28, 2026
Security Report · welivesecurity.com

ESET Report Details APT Campaigns and Threat Trends From October 2025 to March 2026

ESET’s report reviews APT activity from October 2025 to March 2026, including espionage, destructive attacks, phishing, spyware, ransomware attempts, and the compromise of the axios JavaScript library.

May 28, 2026
Security Report · proofpoint.com

Proofpoint Observes 12 2026 CVEs in Exploitation, Four Not on CISA KEV

Proofpoint telemetry observed 12 distinct 2026 CVEs in network-facing exploitation, four absent from CISA KEV as of May 15. The report says familiar opportunistic tactics persist as CVE volume and NVD enrichment backlogs complicate prioritization.

May 27, 2026
Security Report · research.checkpoint.com

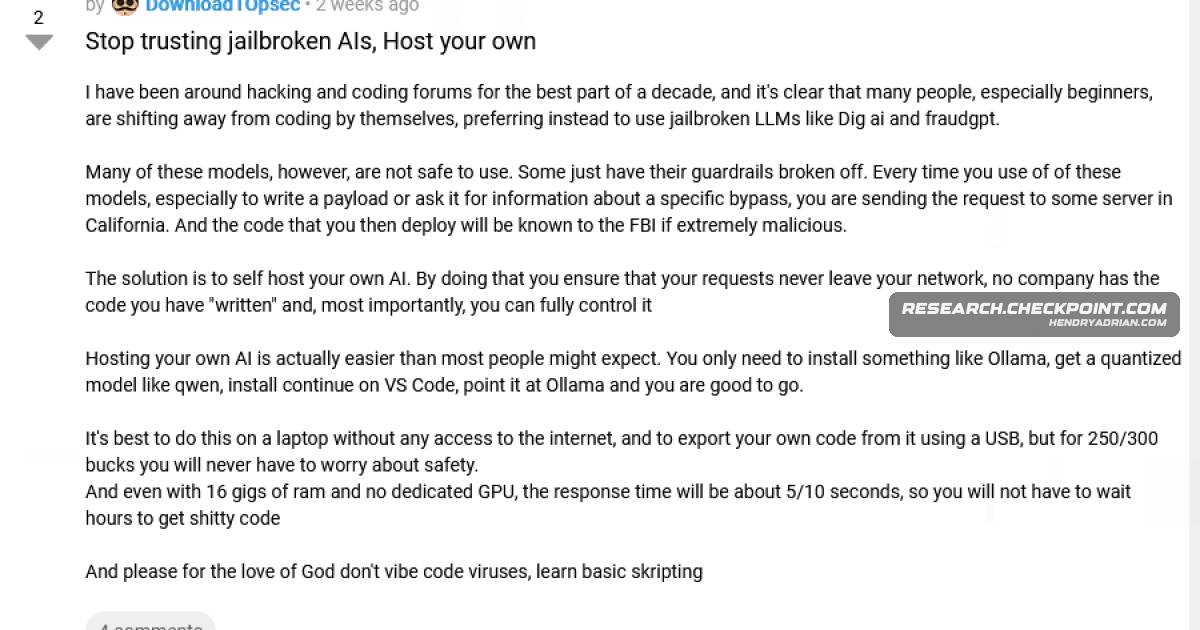
Check Point Tracks AI’s Expanding Role in Cyber Operations

Check Point Research’s March–April 2026 digest describes AI use in cyber operations, including a Mexico government breach, Bissa Scanner and EvilTokens, and faster vulnerability discovery and exploitation. It reports 3.6% of enterprise GenAI prompts posed high sensitive

May 26, 2026
Security Report · wiz.io

Wiz Report Finds SDLC Risk Concentrates in Shared Dependencies, Developer Tools and Automation

Wiz’s 2026 SDLC security report says risk increasingly propagates through shared dependencies, developer environments, CI/CD automation and AI-assisted workflows, linking application security with the broader software delivery trust chain.

May 26, 2026
Security Report · asec.ahnlab.com

April 2026 Security Threats Targeting Korean and Global Financial Firms

AhnLab's April 2026 review describes phishing and malware targeting financial firms, Telegram-based credential theft, real-world exploitation of an Inswave WGear RCE flaw, and dark-web data and access claims.

May 21, 2026
PreviousPage 23 of 31 Next
© 2026 cyber.hendryadrian.com