
Report Links Handala Personas to MOIS Physical Threat and Influence Operations
Summary
Recorded Future’s Insikt Group assesses that Iran’s MOIS likely coordinates Handala cyber, physical-threat, and influence personas, using cross-amplification to recruit proxies and target US and Israeli interests.
Key points
- Insikt Group assesses that MOIS likely uses Handala as an umbrella brand for cyber, physical-threat, and influence personas, including Handala Hack Team, HPRF, VIPEmployment, MOISIRAN, and Brave Israel.
- Cross-posting, shared recruitment links, and coordinated amplification across Telegram accounts underpin the report’s assessment that these personas are connected; the attribution remains qualified.
- HPRF claimed responsibility for an April 2026 vehicle arson in Israel. The report describes the incident as a claim and says it could not independently establish that the claim was accurate.
- VIPEmployment accounts have solicited recruits for espionage and physical attacks, while MOISIRAN and related personas have posted surveillance claims and material presented as evidence.
- The report says Handala Hack Team has claimed hack-and-leak and wiper operations against Israeli and US targets; these claims are not, by themselves, confirmation of the reported incidents.
- Recommended defenses include phishing-resistant MFA, patch and vulnerability management, network segmentation, offline backups, and tabletop exercises for physical-security teams.
Article Details
- Publisher
- Recorded Future (Insikt Group)
- Report Period
- 2024-2026 (activity described through May 2026)
- Scope
- MOIS-linked Handala personas and their cyber, physical-threat, recruitment, surveillance, and influence activity targeting US and Israeli interests.
- Sample Size
- Not disclosed
- Key Statistics
- VIPEmployment accounts posted several hundred Telegram bot links in Hebrew-language channels during the initial activity phase from August 2024 to late February 2026.
- VIPEmployment has recruited individuals in dozens of countries since 2024, according to the report.
- In August 2025, Israeli law enforcement arrested two people from Holon on suspicion of security offenses involving contact with Iranian intelligence; one was reportedly in contact with individuals linked to VIPEmployment and received cryptocurrency payments.
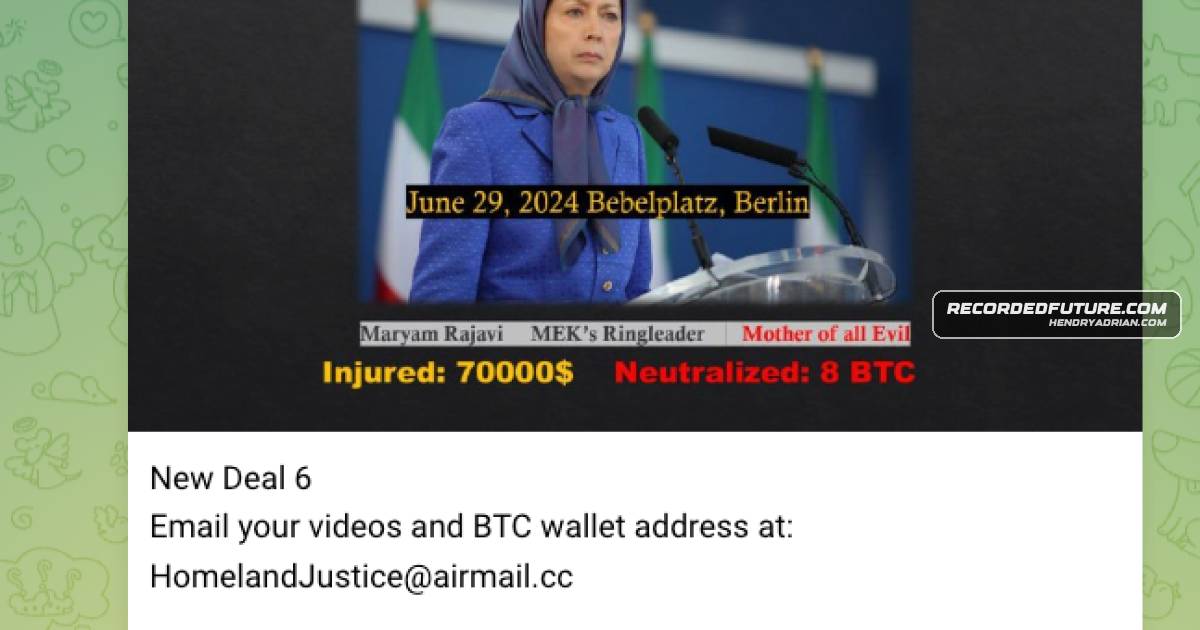
- A Street Vendor solicitation offered $70,000 for injuring MEK leaders and 1-8 Bitcoin (then estimated at approximately $65,000-$525,000) for “neutralizing” them.
- Recommendations
- Prioritize vulnerability and patch management; use virtual patching and continuous monitoring for active exploits affecting the organization's technology stack.
- Enforce phishing-resistant MFA, limit partner-network access, and monitor credential-use anomalies.
- Segment critical R&D and manufacturing networks; control outbound traffic, inspect encrypted C2 traffic, and use DLP to detect unauthorized transmissions of sensitive information.
- Maintain offline backups, harden exposed web infrastructure, validate DDoS mitigation capacity, and establish rapid workflows to verify or dismiss breach claims.
- Run physical-security tabletop exercises, review facility protections, assess vulnerabilities to sabotage and arson, and limit unnecessary publication of critical-asset layouts and security measures.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | handala-alert[.]ps | Listed as Handala Hack Team infrastructure in the report's IoC appendix. |
| DOMAIN | handala-hack[.]ps | Handala Hack Team website domain; the report says it appeared in videos accompanying an HPRF arson claim. |
| DOMAIN | handala-hack[.]tw | Listed as Handala Hack Team infrastructure in the report's IoC appendix. |
| DOMAIN | handala-redwanted[.]ps | Listed as Handala Hack Team infrastructure in the report's IoC appendix. |
| DOMAIN | handala[.]red | Listed as Handala Hack Team infrastructure in the report's IoC appendix. |
| DOMAIN | justicehomeland[.]info | Listed as a Homeland Justice website domain; the report links Homeland Justice to claimed cyberattacks and physical-threat activity. |
| DOMAIN | justicehomeland[.]org | Listed as a Homeland Justice website domain; the report links Homeland Justice to claimed cyberattacks and physical-threat activity. |
| DOMAIN | justicehomeland[.]ru | Listed as a Homeland Justice website domain; the report links Homeland Justice to claimed cyberattacks and physical-threat activity. |
MITRE ATT&CK
T1485 · Data DestructionHandala-linked personas reportedly used wiper attacks and destructive malware to damage victims' systems.T1566 · PhishingThe mitigation section identifies spearphishing-driven initial access as relevant to the reported threat activity.T1589 · Gather Victim Identity InformationThe report describes surveillance and the collection or publication of personal details about officials, personnel, and other targets.T1591 · Gather Victim Org InformationThe report describes collecting and leaking organizational information, including facility data, internal communications, and blueprints.
People
Ehud NakarIdentified as an Israeli nuclear scientist targeted in MOISIRAN's claimed surveillance; the report does not independently verify the surveillance.Isaac GertzIdentified as an Israeli nuclear scientist in an earlier alleged intimidation incident cited by the report; Handala Hack Team allegedly left a bouquet in his car.Kash PatelIdentified as a target of Handala Hack Team claimed cyber operations against US personnel; the report does not confirm a specific compromise of his accounts.Maryam RajaviNamed as an MEK leader targeted in a Street Vendor solicitation; the report documents the solicitation, not an attack against her.Seyed Yahya Hosseini PanjakiIdentified as Deputy Minister of Intelligence for Israeli Affairs; the report says Void Manticore-linked personas were associated with the MOIS Counterterrorism Division operating under him. It states he died in Israeli airstrikes in early March 2026.
Threat Actors
Banished KittenThe report explicitly lists Banished Kitten as another name for Void Manticore, which it links to hack-and-leak and wiper activity.Brave IsraelA persona that solicited paid vandalism and other physical-threat activity in Israel; Insikt Group assesses it is likely MOIS-linked and likely operated by the same threat actors as MOISIRAN.Handala Hack TeamAttributed by the report to MOIS and to Void Manticore; it has claimed hack-and-leak and wiper operations against Israeli and US targets.Homeland JusticeA Void Manticore-linked persona that has claimed cyberattacks on Albania and promoted the Street Vendor persona's physical-threat solicitations.KarmaBelowA Void Manticore-linked persona reported to have targeted the Israeli government with the destructive BiBi wiper.MOISInsikt Group assesses that MOIS likely coordinates cyber, physical-threat, and influence personas under the Handala brand; this is an attribution assessment.MOISIRANA Telegram persona that posted claims of surveillance against Israeli personnel and promoted VIPEmployment. Insikt Group assesses it likely operates under the Handala brand and broader MOIS activity cluster.Red SandstormThe report explicitly lists Red Sandstorm as another name for Void Manticore, which it links to hack-and-leak and wiper activity.Street VendorA persona that solicited physical threats against MEK leaders and facilities through a Homeland Justice-promoted Telegram channel. The report identifies “Street Vendor” as the English rendering of “Shites Rruge.”TAG-145The report explicitly lists TAG-145 as another name for Void Manticore, which it links to hack-and-leak and wiper activity.The Handala Popular Resistance FrontThe persona claimed responsibility for an arson targeting an Israeli law-enforcement official's vehicle. Insikt Group assesses it is likely attributable to MOIS.VIPEmploymentA recruitment network that solicits proxies for physical attacks and espionage against US- and Israeli-linked targets; Insikt Group assesses it is likely attributable to MOIS.Void ManticoreA threat activity cluster to which Handala Hack Team is attributed; the report says researchers and the US Department of Justice have linked it to Iran's MOIS.
Malware
Products
Countries
AlbaniaHomeland Justice focuses on targeting Iranian opposition groups, and since 2022 has claimed responsibility for several cyberattacks on Albania, which hosts the exiled Iranian opposition group Mojahedin-e-Khalq (MEK).IranIran’s MOIS has likely expanded the Handala brand to unify cyber, physical, and influence personas, including Handala Hack Team, HPRF, VIPEmployment, MOISIRAN, and Brave Israel.IsraelIran’s MOIS has likely expanded the Handala brand to unify cyber, physical, and influence personas, including Handala Hack Team, HPRF, VIPEmployment, MOISIRAN, and Brave Israel.United StatesHandala Hack Team has claimed hack-and-leak and wiper operations against Israeli and US targets, including government, security, tech, and critical infrastructure entities.
Industries
EnergyUS and Israeli law enforcement, military, and intelligence agencies and their personnel, in addition to energy, transportation, and research organizations operating in the region.GovernmentHandala Hack Team has claimed hack-and-leak and wiper operations against Israeli and US targets, including government, security, tech, and critical infrastructure entities.Law enforcementThis very likely entails heightened risks for US and Israeli law enforcement, military, and intelligence agencies and their personnel, in addition to energy, transportation, and research organizations operating in theMilitary and intelligencedetails about targets, including officials, personnel, and facilities (‘surveilled Israeli military and intelligence personnel’ and ‘shared traffic patterns and sensitive intelligence’).Researchmilitary, and intelligence agencies and their personnel, in addition to energy, transportation, and research organizations operating in the region.Technologya broad range of operations targeting Israeli leadership, government agencies, security institutions, technology companies, and critical infrastructure, including Israel’s nuclear facilities.Transportationlaw enforcement, military, and intelligence agencies and their personnel, in addition to energy, transportation, and research organizations operating in the region.