
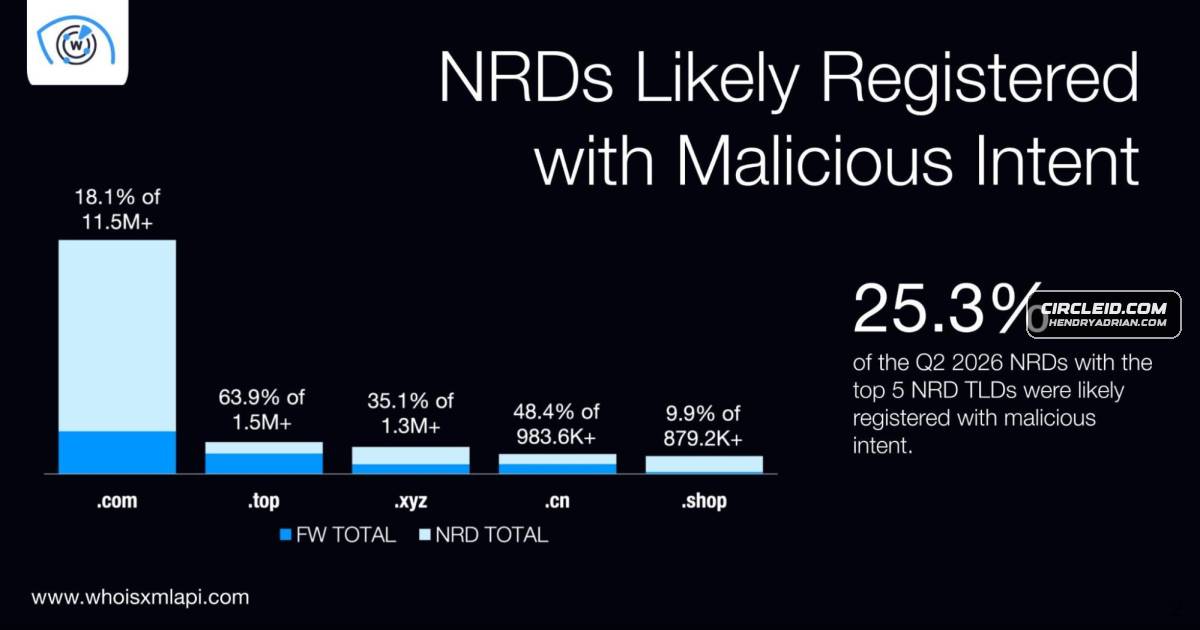
WhoisXML API Reports Q2 2026 Domain and DNS Trends
WhoisXML API analyzed Q2 2026 domain activity, reporting 30 million+ new registrations, 7.6 million+ likely malicious registrations, and increased concentration among leading MX and NS providers.
Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.
726 articles
WhoisXML API analyzed Q2 2026 domain activity, reporting 30 million+ new registrations, 7.6 million+ likely malicious registrations, and increased concentration among leading MX and NS providers.
Infoblox estimates that about 50,400 gTLD domains are re-registered daily, roughly 20% of new gTLD registrations. Old domains can retain trust and connections that threat actors may exploit.
Check Point Research reports 2,139 ransomware victims in Q2 2026, near Q1 levels, while active groups rose to 93. The top 10 groups’ share fell, and ransom payment rates continued a multiyear decline.
Recorded Future analyzed 24 crypting providers and found services combining payload obfuscation with loaders, anti-analysis, persistence, and evasion features. It recommends behavior-based detection and response instead of relying on signatures or antivirus alone.
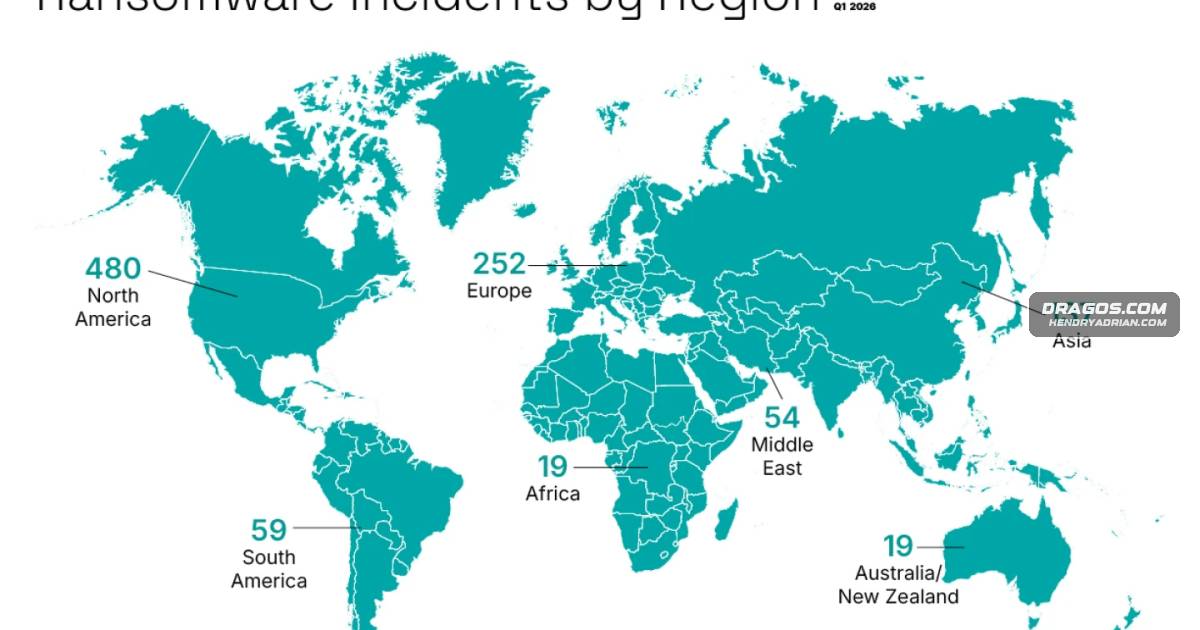
Using public victim disclosures and ransomware-group leak-site posts, Dragos identified 1,140 industrial ransomware incidents in Q2 2026, up 12% from Q1. Manufacturing was hardest hit; extortion increasingly relied on data theft, while disruption largely stemmed from IT
Team Cymru’s report analyzes Cl0p’s campaign patterns, reconnaissance, and infrastructure, and recommends stronger monitoring and controls for managed file-transfer systems.
ASEC’s July 2026 report tracks infostealer distribution and impersonation trends, including malware spread through cracks, file-sharing services, MSBuild, DLL side-loading, and phishing emails.
Cloudflare reports more than 800 network-layer DDoS attacks above 1 Tbps in Q2 2026, up over fivefold from Q1. Its H1 findings also highlight rising DNS and reflection/amplification attacks.
CloudSEK says its reconstructed dataset links more than 2,500 companies and 434,000 CI/CD pipelines to exposure from the March 2026 supply-chain attack involving LiteLLM. The figures indicate potential exposure, not confirmed compromise.
A July 2026 review of financial-sector threats reports phishing-led malware chains, credentials leaked through Telegram, dark-web data-sale claims involving financial organizations, and hacktivist DDoS claims that remain unverified.
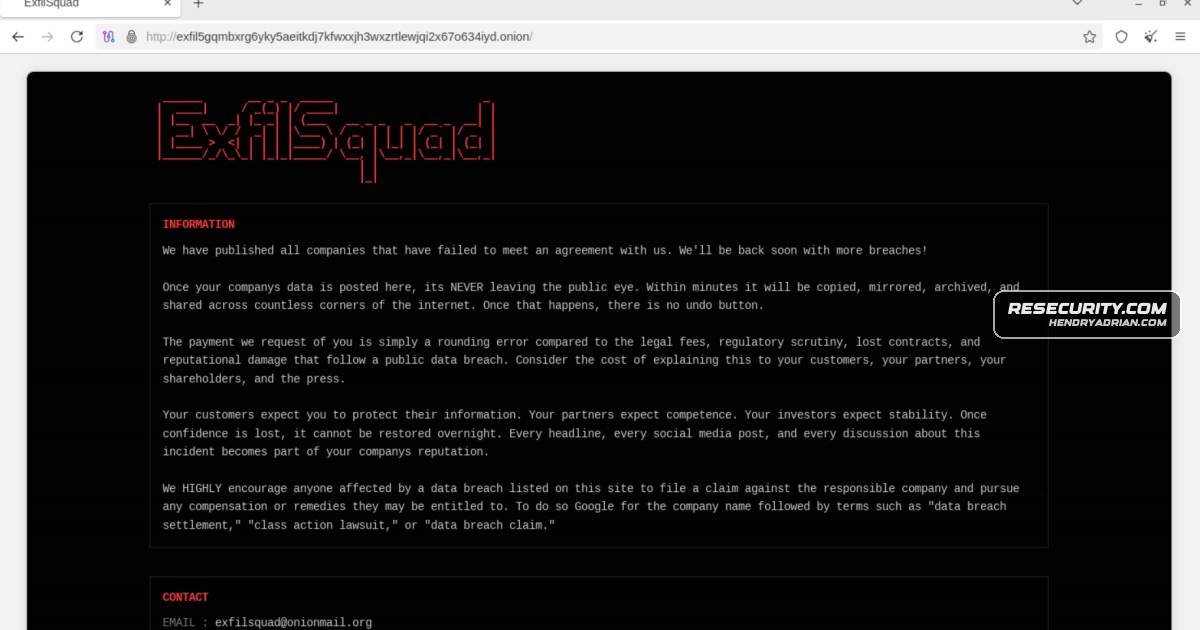
Resecurity reports that ExfilSquad claimed 13 organizations as victims and posted torrents said to contain stolen data. Its analysis found more than 50 later seeds and early activity from hosts in China and Russia, without linking those hosts to the group.
Recorded Future identified 85 high-impact vulnerabilities in July 2026; 81 were actively exploited or operationally weaponized. The report highlights exploitation across IoT, email, and enterprise systems, with 57 flaws enabling remote code execution.
Zscaler says hundreds of assessed enterprises averaged 37/100 for frontier AI readiness, citing exposed VPNs, weak AI identity controls, and broad access rules. It recommends a 90-day push on Zero Trust controls, patching, traffic inspection, and deception.
Wiz says significant cloud incidents rose 60% in H1 2026, driven by supply-chain campaigns, credential theft, and growing attacks on AI infrastructure. Its report also details extortion activity, exposures, and defensive detections.
Chainalysis estimates violent crypto attacks stole more than $30 million through mid-2026. France recorded a sharp rise in incidents, which the report links potentially to exposed personal data; on-chain flows show varying levels of attacker sophistication.

A bipartisan House investigation says China Mobile, China Unicom and China Telecom retained U.S. network footholds after FCC actions, and examines their links to Salt Typhoon and other incidents. It recommends stronger FCC powers and more cybersecurity resources.
Recorded Future warns that wider use of neurotechnology could increase risks of IP theft, data breaches, device disruption, and extortion as neurological and biometric data become more valuable and the attack surface expands.
A survey of 504 IT and security professionals found compliance demands contributed to burnout or staff turnover at 37% of organizations, while documentation work also diverted time from active security efforts.
CrowdStrike’s annual report says AI-enabled malicious activity rose 89% over the past year, with AI used against vulnerabilities, software supply chains and AI systems. It reports that 88% of vulnerabilities were weaponized through AI within 48 hours.
Darktrace’s H1 2026 report says attackers increasingly abused trusted identities, SaaS, cloud, supply chains and AI. Its customer data includes phishing and campaign trends, while investigations document infostealer activity and AI infrastructure attacks.
IBM’s 2026 Cost of a Data Breach Report says up to one-quarter of breaches are linked to AI, with average losses of $6 million. It also reports on AI-enabled attacks, defensive readiness, critical-infrastructure targeting, and ransomware extortion.
ESET's H1 2026 findings highlight malicious AI skills, PromptSpy's use of Gemini to adapt Android malware behavior, rising ClickFix and QR-code phishing, and more than 100 EDR-killer tools observed in the wild.
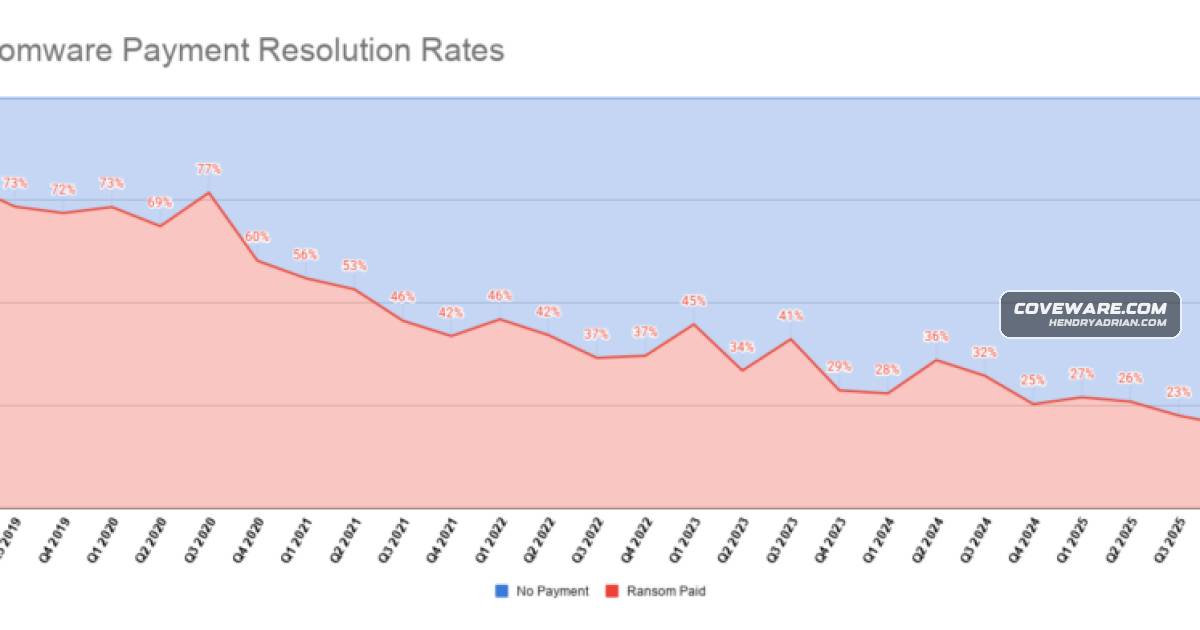
Coveware’s Q2 2026 analysis reports a 176% quarter-over-quarter rise in average ransom payments, a record-low payment rate, and continued identity-driven access. It highlights volatile post-payment outcomes and recommends hardening trusted access paths.
The Enterprise LLM Threat Atlas identifies tool and agent abuse and supply-chain attacks as leading enterprise LLM risks, alongside prompt injection, over-permissioned connectors, knowledge-base poisoning and data leakage.