
Malicious npm Package Targets Claude AI Workspace Files for Theft via GitHub
Summary
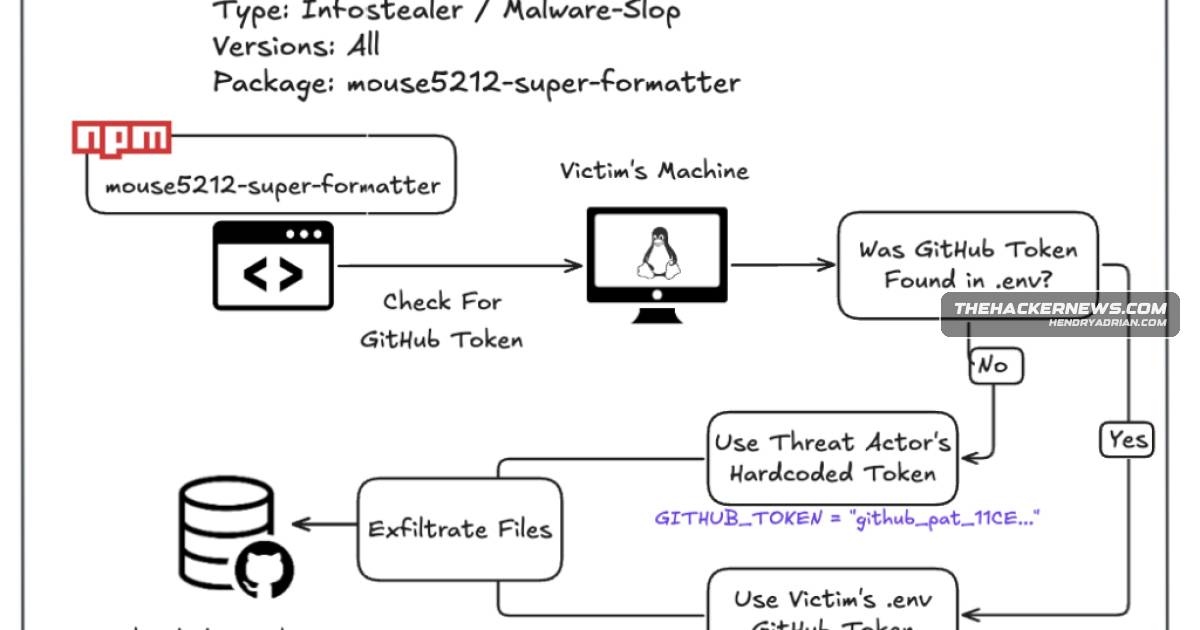
OX Security says the npm package mouse5212-super-formatter targets Claude’s /mnt/user-data files and uploads them to a threat actor’s GitHub account. It had about 676 downloads, but actual installs are unknown; the package remained available.
Key points
- OX Security says mouse5212-super-formatter targets files in /mnt/user-data, a directory used by Anthropic’s Claude AI tool.
- The package reportedly authenticates to GitHub during postinstall with a token from the victim’s environment or a hard-coded fallback.
- Researchers say it can create a repository and recursively upload files to a threat actor-controlled GitHub account, placing them in randomly named folders.
- The package disguises its activity as a sync utility and writes a fake network-connections log, according to OX Security.
- The package reportedly exposed the attacker’s private GitHub token. The linked account is no longer available.
- The package was estimated to have 676 downloads and was still available on npm; how many downloads were actual installs is unclear.
Article Details
- Event Type
- Malicious npm package carrying out information theft and exfiltration
- Impact
- The package recursively uploaded files from /mnt/user-data, a directory used by Claude, to a threat actor-controlled GitHub account. It also exposed the attacker’s private GitHub token. The package was reported as still available on npm and estimated to have been downloaded 676 times, but the number of actual installs was unclear. The linked GitHub account was no longer available.
MITRE ATT&CK
People
Malware
Vendors
Products
ClaudeA malicious npm package named “mouse5212-super-formatter” was found stealing files from Anthropic’s Claude AI workspace by uploading them to a threat actor-controlled GitHub account.GitHubA malicious npm package named “mouse5212-super-formatter” was found stealing files from Anthropic’s Claude AI workspace by uploading them to a threat actor-controlled GitHub account.npmA malicious npm package named “mouse5212-super-formatter” was found stealing files from Anthropic’s Claude AI workspace by uploading them to a threat actor-controlled GitHub account.