
GreyVibe Uses AI-Generated Lures and Custom Malware to Target Ukraine-Linked Organizations
Summary
WithSecure reports that GreyVibe, a likely Russian threat group, has targeted Ukrainian and related organizations since at least August 2025 using AI-generated lures and custom malware. Researchers say its state alignment and links to cybercrime remain uncertain.
Key points
- WithSecure discovered the activity in January and links it to a likely Russian-speaking actor based on malware language, code comments and C2 server time settings; nation-state attribution remains uncertain.
- Campaigns targeted Ukrainian military, government, civilian and business organizations through phishing, fake CAPTCHA pages and deceptive websites.
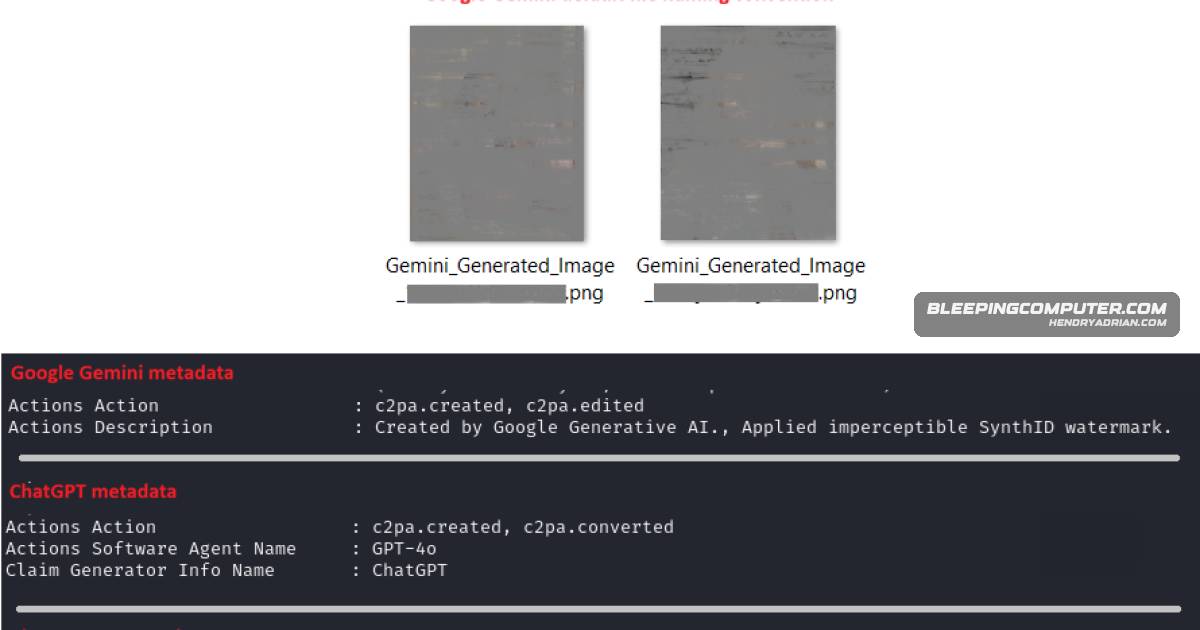
- WithSecure says the operators used ChatGPT, Ideogram AI and Google Gemini to help create realistic lures.
- LegionRelay can steal files and browser credentials, capture screenshots, collect Telegram and WhatsApp data, and set up RDP access.
- PhantomRelay is a PowerShell RAT with system fingerprinting, dynamic script loading and command-execution capabilities.
- FallSpy Android spyware collects contacts, call logs, device and network details, location, media and SIM information.
- Researchers cite cybercrime-associated PhantomRelay use, test samples uploaded to a public scanning service and cryptocurrency mining on some victim machines as possible signs of a hybrid operation.
Article Details
- Event Type
- Cyberespionage campaign using AI-generated lures, phishing, and custom malware against Ukrainian and Ukraine-related organizations.
- Impact
- The campaign targets military, government, civilian, and business organizations. Reported malware capabilities include stealing files and browser credentials, capturing screenshots, collecting Android device data and media, and setting up RDP access. Researchers say the activity may align with Russian state interests but cannot confidently classify it as a nation-state operation.
MITRE ATT&CK
T1059.001 · PowerShellLegionRelay and PhantomRelay are PowerShell-based malware; PhantomRelay also supports PowerShell command execution.T1113 · Screen CaptureLegionRelay supports screenshot capturing.T1555.003 · Credentials from Web BrowsersLegionRelay supports browser credential theft.T1566.001 · Spearphishing AttachmentPhantomMail uses spear-phishing emails to deliver malicious ZIP/RAR archives.T1566.002 · Spearphishing LinkPhantomClick campaigns use deceptive pages to lure victims into executing commands.
Threat Actors
GREYVIBEA likely Russian threat group reported to have targeted Ukrainian and Ukraine-related organizations with phishing lures and custom malware since at least August 2025. Researchers say its activity may align with Russian state interests but cannot confidently classify it as a nation-state operation.UAC-0098The article associates a unique ISO builder in early GreyVibe samples with UAC-0098, described as a group of former TrickBot members that targeted Ukraine at the start of the Russian invasion.
Malware
FallSpyIts campaigns use multiple attack chains and tools such as LegionRelay, PhantomRelay, and FallSpy, suggesting a hybrid operation that may blend state-aligned goals with cybercriminal tradecraft.LegionRelayIts campaigns use multiple attack chains and tools such as LegionRelay, PhantomRelay, and FallSpy, suggesting a hybrid operation that may blend state-aligned goals with cybercriminal tradecraft.PhantomRelayIts campaigns use multiple attack chains and tools such as LegionRelay, PhantomRelay, and FallSpy, suggesting a hybrid operation that may blend state-aligned goals with cybercriminal tradecraft.
Products
ChatGPTof these lures are notable, and WithSecure says this is the result of using multiple AI tools, including ChatGPT, Ideogram AI, and Google Gemini, to generate detailed and realistic content to support them.Google GeminiWithSecure says this is the result of using multiple AI tools, including ChatGPT, Ideogram AI, and Google Gemini, to generate detailed and realistic content to support them.Ideogram AIare notable, and WithSecure says this is the result of using multiple AI tools, including ChatGPT, Ideogram AI, and Google Gemini, to generate detailed and realistic content to support them.TelegramThe operators used fake female Telegram personas and later added WebRTC-based live calls that could capture the victim’s audio/video.WhatsAppLegionRelay supports file theft, screenshot capturing, browser credential theft, Telegram and WhatsApp data exfiltration, and RDP access setup.
Tools
DAYLIGHTThe use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance.LOOKVALJSThe use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance.LOOKVALPSThe use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance.TEASOUPThe use of AI extends to the creation of tools as well, with the researchers mentioning LOOKVALPS, LOOKVALJS, DAYLIGHT, and TEASOUP, all custom obfuscators that were likely developed with LLM assistance.
Countries
Industries
EnergyThe observed lures impersonated Ukrainian government, emergency, telecom, and energy entities.GovernmentA likely Russian threat group tracked as GreyVibe has been using AI-generated lures and a rich set of custom malware tools to target entities in the military, government, civilian, and business sectors.MilitaryA likely Russian threat group tracked as GreyVibe has been using AI-generated lures and a rich set of custom malware tools to target entities in the military, government, civilian, and business sectors.