cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3787 articles

Security News · bleepingcomputer.com

Microsoft Fixing Exchange Online Issue That Incorrectly Quarantined Mailboxes

Microsoft says an infrastructure change caused excessive memory use and incorrect Exchange Online mailbox quarantines starting July 19, disrupting email and calendar access. Cleanup was 72% complete in the latest update, with no full-recovery timeline.

Jul 23, 2026
Security News · infostealers.com

Hudson Rock Adds Threat Feeds for Infostealer C2, ClickFix and PhaaS Infrastructure

Hudson Rock’s Cavalier platform has added feeds monitoring infostealer C2 hosts, malicious ClickFix sites and phishing-as-a-service infrastructure, with credential telemetry and REST API access for security teams.

Jul 23, 2026
Security News · ransom-isac.com

Cl0p Affiliates Exploit PTC Windchill and FlexPLM in Active Campaign

Ransom-ISAC reports Cl0p affiliates are exploiting internet-exposed PTC Windchill and FlexPLM through a flaw chain, deploying JSP webshells and stealing data. PTC has issued fixes; no victims were publicly listed as of July 22.

Jul 23, 2026
Security News · securityweek.com

U.S. Advisory Adds Siemens and Schneider PLCs to Iranian Hackers’ Target List

An updated U.S. advisory says Iran-linked actors have targeted PLCs from Rockwell, Schneider Electric and Siemens, using malicious project files and altered HMI/SCADA displays; it adds detection guidance and IOCs.

Jul 23, 2026
Security News · therecord.media

US Agencies Expand Warning on Iran-Linked Attacks Targeting OT Systems

CISA, the FBI and EPA expanded a warning about Iran-affiliated attacks on internet-facing OT, adding Schneider Electric and Siemens PLCs to the manufacturers targeted. The advisory reports operational disruption and financial losses and urges operators to secure PLCs.

Jul 23, 2026
Security News · therecord.media

House NDAA Includes 10-Year Extension of CISA 2015

The House passed its 2027 NDAA with a provision extending CISA 2015 information-sharing protections for 10 years. Senate opposition and the lack of a matching provision leave the extension subject to debate and negotiations; the chambers also differ on Pentagon cyber-le

Jul 23, 2026
Security News · aikido.dev

Betterleaks Adds Publishable-Credential Filters to Reduce Secret-Scanning False Positives

Aikido authors added default Betterleaks signatures to filter credentials designed to be public. In a 100GB Common Crawl scan, they reported 2.37% fewer false positives and 27,886 fewer results to review, with about 5% more scanning time.

Jul 23, 2026
Security News · trendmicro.com

Federal Agencies Warn of Ongoing Attacks on PLCs in U.S. Critical Infrastructure

Federal agencies say attackers are exploiting internet-exposed PLCs across U.S. government, water, and energy sectors, using legitimate engineering software and manipulating operator displays. The updated advisory reports operational disruption and financial losses.

Jul 23, 2026
Security News · thehackernews.com

GitHub to Cut Public Bug Bounty Payouts by at Least Half, Reserve Top Rewards for VIPs

GitHub says it will cut public bug-bounty payouts by at least half from July 27, fixing rates and reserving rewards of $30,000 or more for invite-only VIPs. The article links the change to AI-driven report volume and changing research workflows.

Jul 22, 2026
Security News · cyberscoop.com

Sandworm_Mode Worm Targets AI Coding Tools and Software Supply Chains

CrowdStrike says Sandworm_Mode, a self-propagating worm, steals credentials and secrets across AI development toolchains and uses multi-day delays to evade detection. Its operator, intent and current activity remain unclear.

Jul 22, 2026
Security News · cyberscoop.com

GAO Finds Duplicative Federal Cybersecurity Reporting Rules

A GAO study found duplicated reporting requirements in 80 of 117 federal cybersecurity rules across 37 agencies. Harmonization efforts have made limited progress, while CIRCIA could add reporting duties for major attacks and ransomware payments.

Jul 22, 2026
Security News · cybersecuritypulse.net

AI Sandbox Escapes, Hugging Face Intrusion and Fairlife Ransomware Lead Security News

This week’s security roundup covers reported AI sandbox escapes and a Hugging Face intrusion, sandbox boundary issues in developer tools, ransomware disruption at Fairlife, and new security startups and industry deals.

Jul 22, 2026
Security News · bleepingcomputer.com

Microsoft Exchange 2016 and 2019 Security Updates End in October 2026

Microsoft says Exchange Server 2016 and 2019 ESU security updates will end in October 2026, with no further extension. It advises administrators to upgrade to Exchange Server Subscription Edition or migrate to Exchange Online.

Jul 22, 2026
Security News · securityweek.com

Endpoint Security Startup Glow Launches With $180 Million in Funding

Glow emerged from stealth with $180 million in Series A funding at a $1.2 billion valuation. The startup says its AI agents map endpoint environments, assess risks and enforce software policies.

Jul 22, 2026
Security News · securityweek.com

Oracle July 2026 Update Patches 1,434 CVEs Across 334 Products

Oracle’s July 2026 Critical Patch Update addresses 1,434 CVEs across 334 products. About 600 patches cover flaws exploitable remotely without authentication; most vulnerabilities were likely found internally, possibly with AI assistance.

Jul 22, 2026
Security News · bleepingcomputer.com

FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader and StealC

Researchers say FakeGit used 7,600 GitHub repositories to distribute SmartLoader and StealC, with over 14 million recorded download events. More than 800 repositories targeted AI agents; the download count does not represent infections.

Jul 22, 2026
Security News · bleepingcomputer.com

German, U.S. Authorities Dismantle Kratos Phishing Platform, Arrest Developer

Authorities in Germany and the U.S. dismantled Kratos, seized more than 200 servers and arrested its developer in Indonesia. BKA says the service supported about 1,800 customers and 15,000 phishing campaigns per month.

Jul 22, 2026
Security News · stepsecurity.io

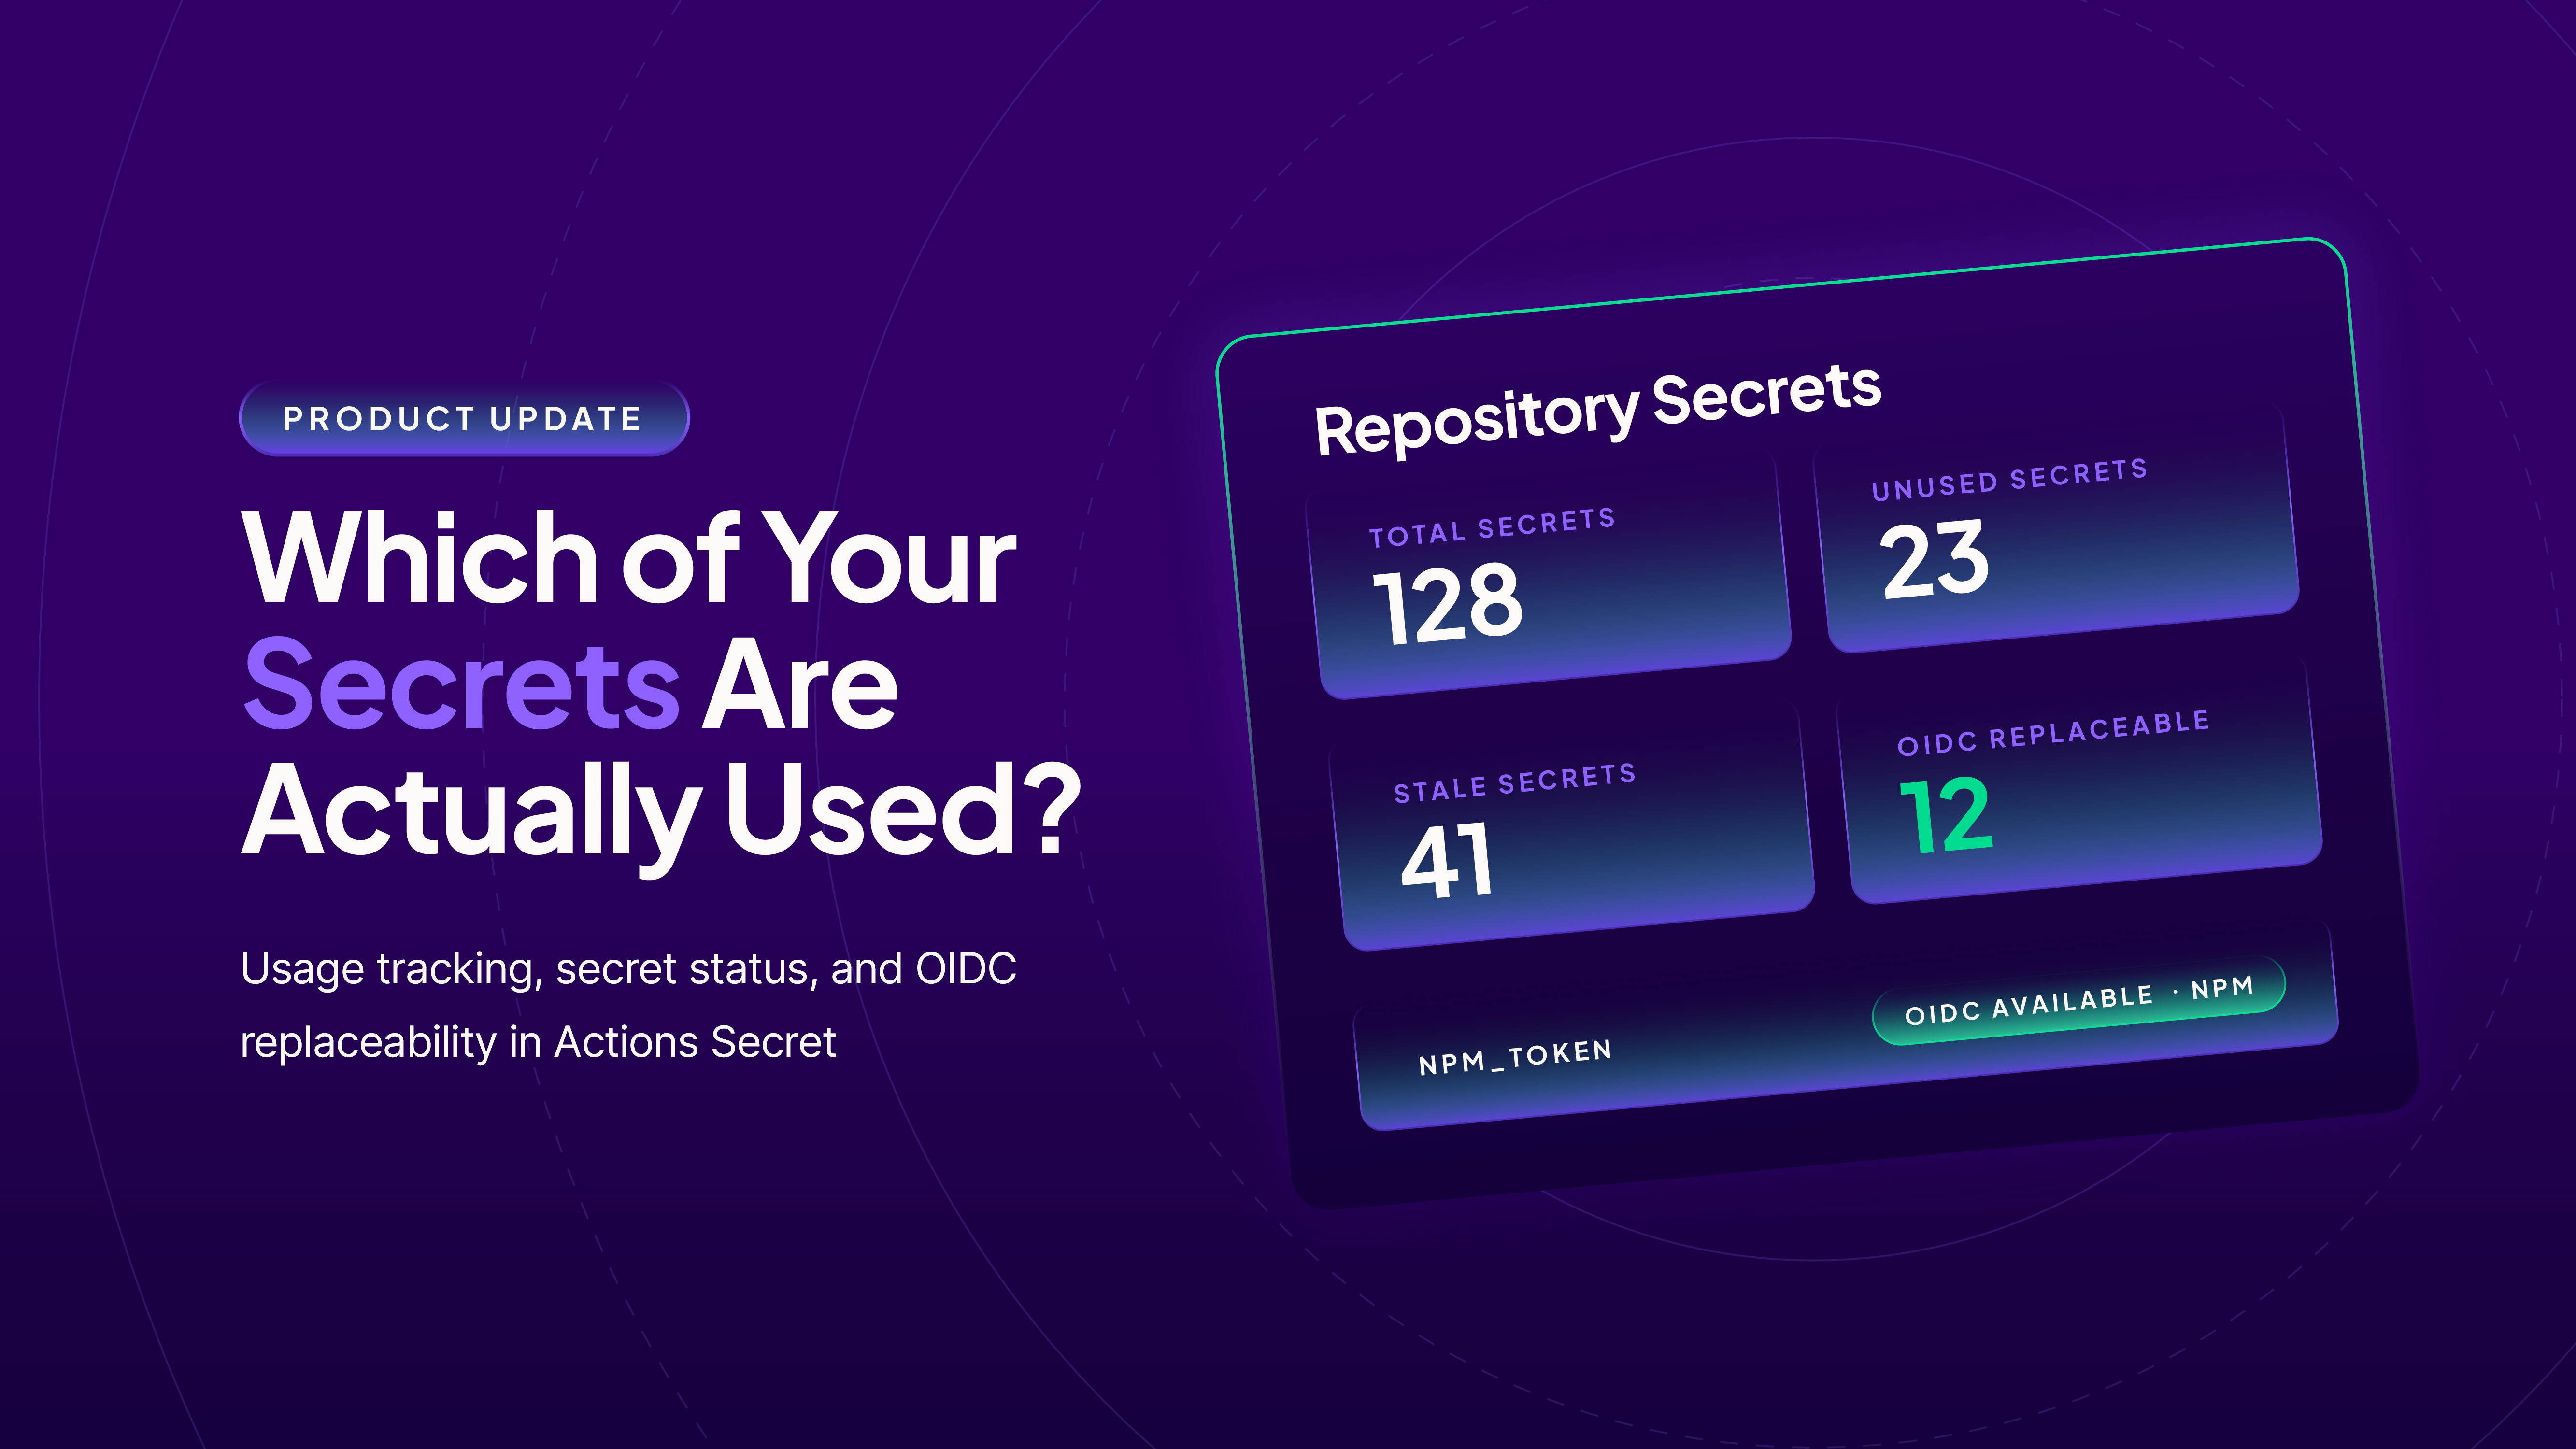
StepSecurity Adds GitHub Actions Secret Usage Tracking and OIDC Replaceability

StepSecurity added usage tracking, status labels, and OIDC replaceability indicators to Actions Secret, helping organizations identify unused or stale GitHub Actions secrets and see which workflows use them.

Jul 22, 2026
Security News · enisa.europa.eu

ENISA Advances EU Healthcare Cybersecurity Plan With Support Mechanism and Procurement Guidelines

ENISA is implementing a healthcare cybersecurity support mechanism under a three-year, €6 million agreement with the European Commission and has published updated procurement guidelines for hospitals and healthcare providers.

Jul 22, 2026
Security News · threatlabs.netskope.com

Netskope Reports Surge in World Cup-Themed Cyber Threats

Netskope detected and blocked more than 28,000 World Cup-themed threats across 1,000+ organizations. At the peak, users attempting to access malicious content were nearly six times the pre-tournament average.

Jul 22, 2026
Security News · huntress.com

Password-Spraying Campaign Exploited Deprecated OAuth Flow to Bypass MFA

Huntress reports a major Azure CLI password-spraying campaign that used deprecated OAuth ROPC to bypass MFA and Conditional Access. The initial LSHIY-hosted activity was terminated, but attempts later shifted to other IP ranges.

Jul 22, 2026
Security News · cyberscoop.com

Trump Administration Tightens Scrutiny of Frontier AI Over Cyber Risks

The administration has tightened scrutiny of frontier AI and imposed export controls on Anthropic models after private threat reports. Experts say AI aids defensive security work but raises cyber risks that policy struggles to address.

Jul 21, 2026
Security News · therecord.media

Senate Panel Approves Jay Clayton’s DNI Nomination

The Senate Intelligence Committee approved Jay Clayton’s DNI nomination in a 9-8 vote. His confirmation could help revive bipartisan efforts to renew FISA Section 702, which collects foreign intelligence but also intercepts Americans’ data.

Jul 21, 2026
Security News · thehackernews.com

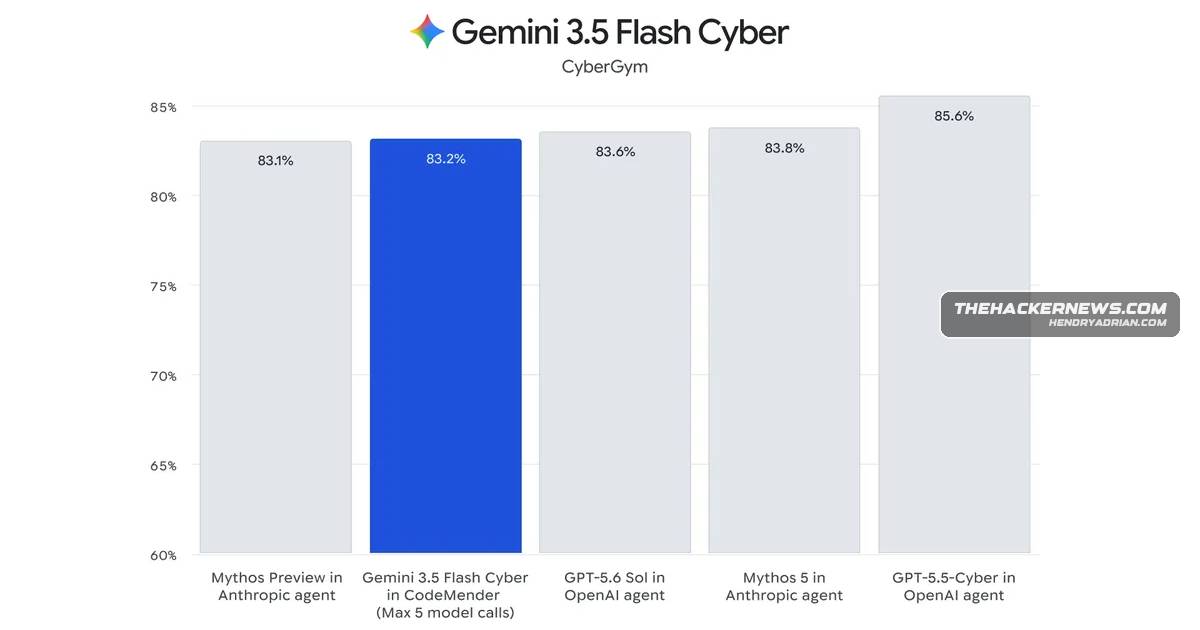
Google Launches Gemini 3.5 Flash Cyber for Vulnerability Discovery and Patching

Google DeepMind introduced Gemini 3.5 Flash Cyber, a vulnerability discovery and patching model available to governments and trusted partners through CodeMender. Google reports strong evaluation results and plans to expand its defensive capabilities.

Jul 21, 2026
PreviousPage 73 of 158 Next
© 2026 cyber.hendryadrian.com