
StepSecurity Adds GitHub Actions Secret Usage Tracking and OIDC Replaceability
Summary
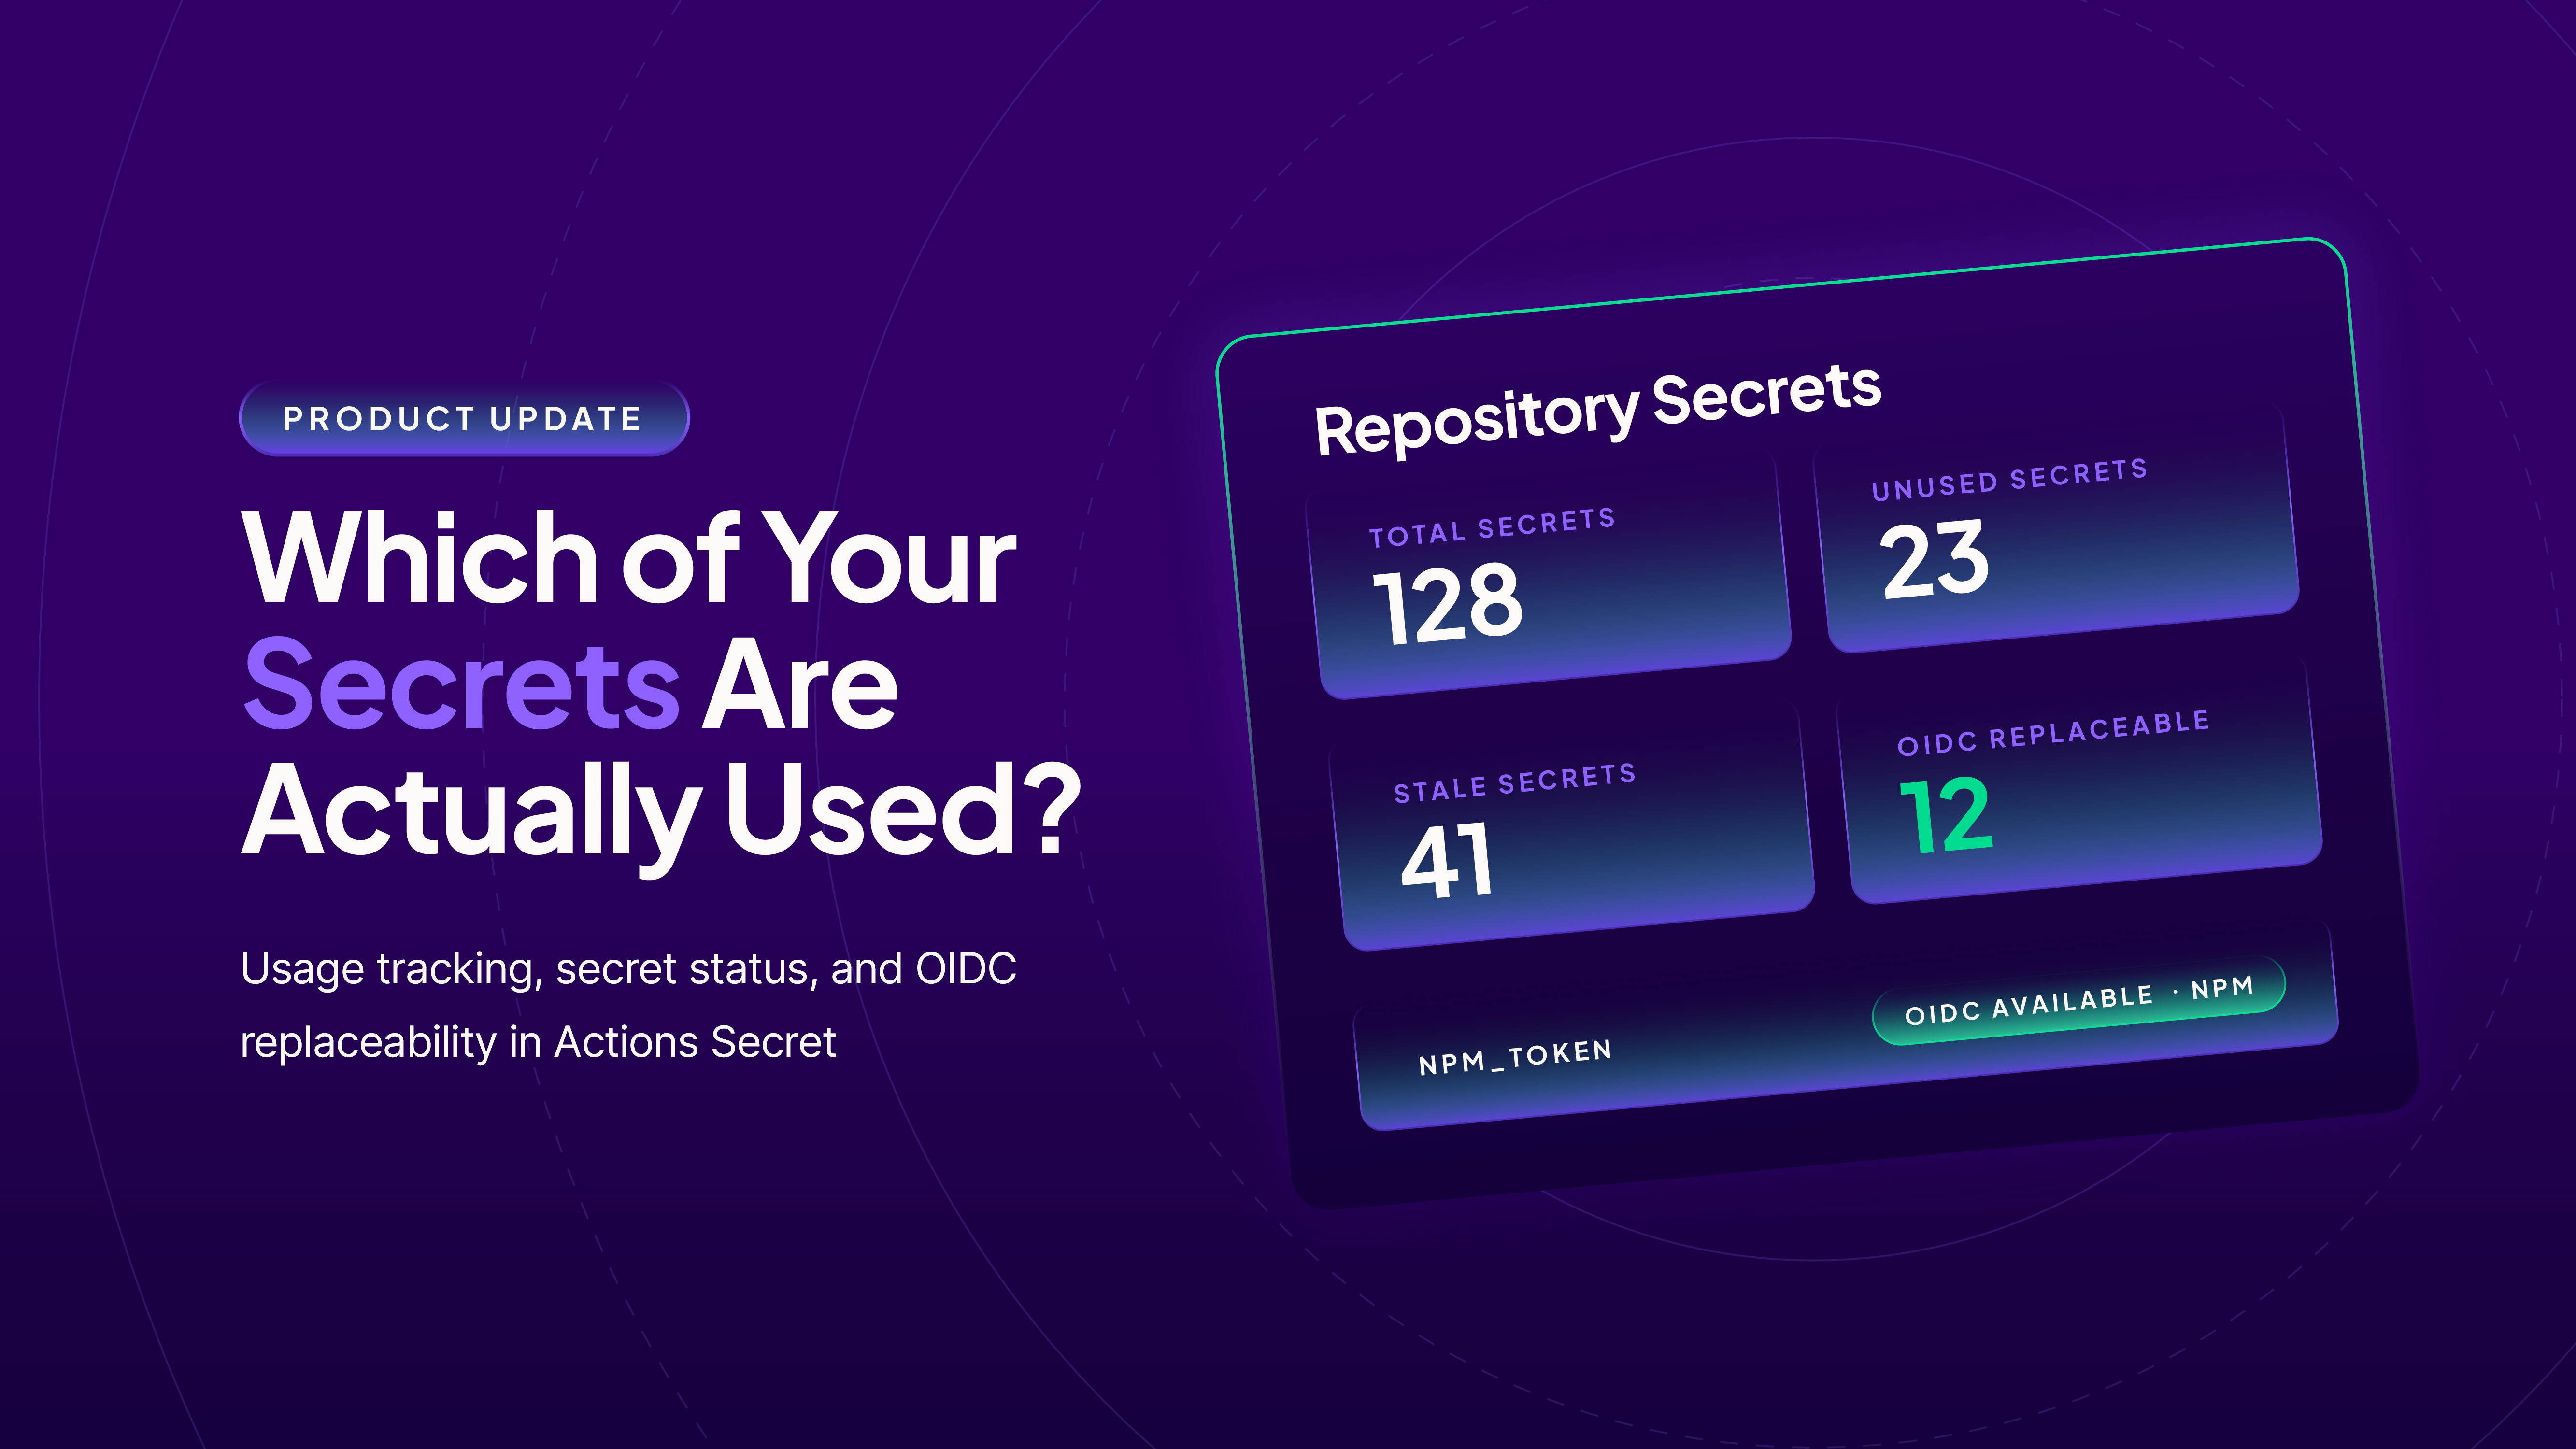
StepSecurity added usage tracking, status labels, and OIDC replaceability indicators to Actions Secret, helping organizations identify unused or stale GitHub Actions secrets and see which workflows use them.
Key points
- Actions Secret's Repository Secrets tab now classifies secrets as Active, Stale, Unused, or Unknown and shows referencing workflows and recent runs.
- The analysis covers direct, bracket and dynamic references, bulk access through toJSON(secrets), and secrets inherited by reusable workflows.
- OIDC indicators identify credentials that may be replaced with short-lived authentication, including supported cloud-provider actions and npm or PyPI publishing tokens.
- The article cautions that Unused status reflects analyzed GitHub Actions workflows; users should check whether external systems consume a secret before deleting it.
- The new capabilities are available on StepSecurity's Enterprise tier.
Article Details
- Event Type
- Security product feature announcement
- Impact
- StepSecurity added secret usage tracking, status classification, and OIDC replaceability detection to Actions Secret, helping organizations identify unused or stale GitHub Actions secrets and reduce exposure to long-lived credentials. The article cites the GhostAction campaign as having exfiltrated over 3,000 secrets across hundreds of repositories and the Megalodon campaign as having targeted secrets across 5,500 public repositories.
Malware
Vendors
GitHubacross hundreds of repositories. The Megalodon campaign ran the same play at even larger scale, targeting GitHub Actions secrets across 5,500 public repositories.StepSecurityMost teams cannot answer any of these without grepping workflow files across hundreds of repositories. The Actions Secret section in StepSecurity now answers all three from a single dashboard.
Products
Actions SecretMost teams cannot answer any of these without grepping workflow files across hundreds of repositories. The Actions Secret section in StepSecurity now answers all three from a single dashboard.GitHub Actionshundreds of repositories. The Megalodon campaign ran the same play at even larger scale, targeting GitHub Actions secrets across 5,500 public repositories.