
Google Launches Gemini 3.5 Flash Cyber for Vulnerability Discovery and Patching
Summary
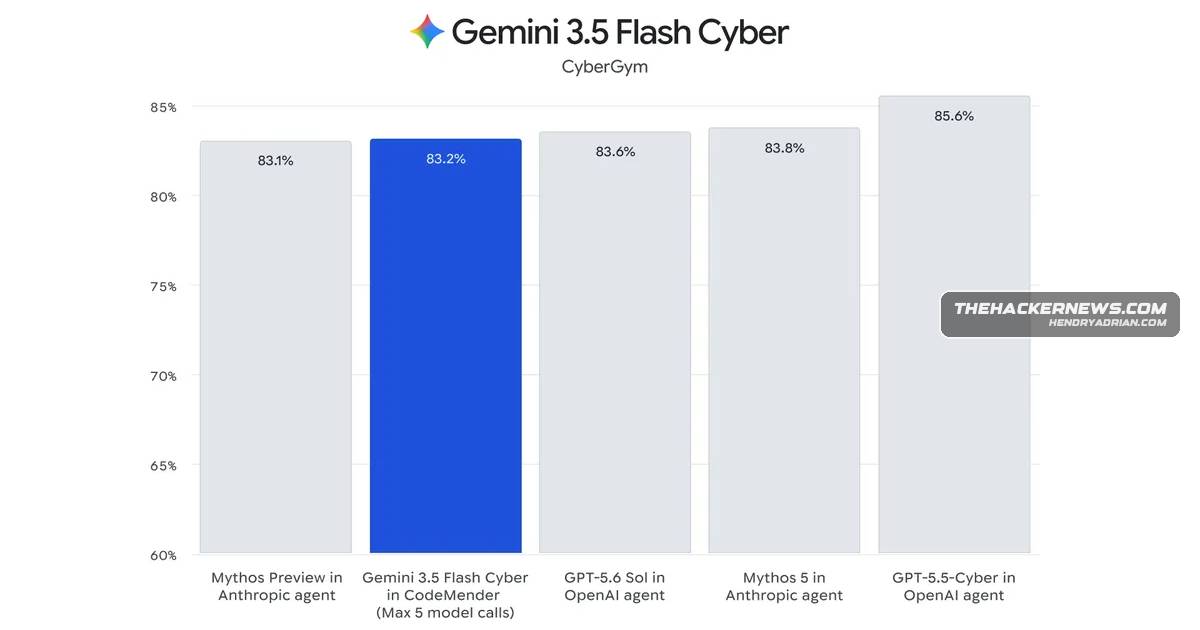
Google DeepMind introduced Gemini 3.5 Flash Cyber, a vulnerability discovery and patching model available to governments and trusted partners through CodeMender. Google reports strong evaluation results and plans to expand its defensive capabilities.
Key points
- Google DeepMind announced Gemini 3.5 Flash Cyber, designed to discover, validate, and patch software vulnerabilities through its CodeMender platform.
- The model is in a limited-access pilot for governments and trusted partners; Google says it runs only inside CodeMender, where guardrails can restrict its use to defensive functions.
- In Google's V8 JavaScript Engine evaluation, the model found 55 unique confirmed issues, compared with 47 for Gemini 3.5 Flash and 36 for Claude Opus 4.6; Google says 10 issues were found by no other model.
- Google says testing also produced a remote-code-execution exploit that bypassed standard mitigations, including ASLR and W^X.
- DeepMind says it plans to add red-teaming features and end-to-end enterprise defense capabilities.
Article Details
- Event Type
- Launch of a cybersecurity-focused AI model in a limited-access pilot
- Impact
- Google DeepMind says Gemini 3.5 Flash Cyber can discover, validate, and patch software vulnerabilities through CodeMender. The pilot is limited to governments and trusted partners. In Google DeepMind evaluations, it found 55 unique confirmed issues in the V8 JavaScript Engine, compared with 47 for Gemini 3.5 Flash and 36 for Claude Opus 4.6; the company also said it produced a reliable remote-code-execution exploit that bypassed standard mitigations. The model’s dual-use capabilities raise misuse concerns, which Google says it seeks to address through restricted access and CodeMender guardrails.
People
Vendors
Products
CodeMenderGoogle DeepMind has launched Gemini 3.5 Flash Cyber, a specialized AI model designed to rapidly discover, validate, and patch vulnerabilities through the CodeMender platform.Gemini 3.5 Flash CyberGoogle DeepMind has launched Gemini 3.5 Flash Cyber, a specialized AI model designed to rapidly discover, validate, and patch vulnerabilities through the CodeMender platform.Gemini Enterprise Agent PlatformGoogle said it’s separately bringing CodeMender’s foundational capabilities directly to customers with generally available Gemini models through the Gemini Enterprise Agent Platform.