cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3588 articles

Security News · malwarebytes.com

Norway Fines Xandr $9.6 Million Over Sharing Grindr Users’ Sensitive Data

Norway’s privacy regulator fined Xandr about $9.6 million for sharing information that could reveal Grindr users’ sexual orientation through ad auctions without verifying valid consent.
Oct 13, 2026
Security News · securityweek.com

Anthropic Says AI Worms Could Soon Self-Replicate Across IoT Devices

Anthropic researchers tested whether AI models could run and replicate across unfamiliar IoT hardware. One model reached all eight emulated devices in four of five runs; the team says no fully autonomous replicator exists yet.

Oct 13, 2026
Security News · cyble.com

TOKEN2049 Side Event Faces Unverified Claims of Remote-Access Software Pressure

A Singapore police report and social media posts allege organizers of a TOKEN2049 side event pressured attendees to install remote-access software. Authorities have not confirmed the report, and no compromise or financial loss is established.

Oct 13, 2026
Security News · thehackernews.com

Preinstalled Android Malware Turns Low-Cost Phones Into Residential Proxies

Bitdefender says the Midnight Mimosa malware is preinstalled in firmware on some MediaTek-based Android phones, enabling covert app installation, ad fraud and residential-proxy use. Removing it may require firmware-level cleanup.

Oct 13, 2026
Security News · iru.com

Iru AI Adds CIS Benchmark-Based Recommendations for Windows Update Settings

Iru AI can recommend and apply Windows Update settings based on CIS benchmarks or Microsoft defaults. Administrators can preview and adjust recommendations, ask follow-up questions, and approve changes before they take effect.

Oct 13, 2026
Security News · crowdstrike.com

Microsoft’s October 2026 Patch Tuesday Fixes 1,413 Vulnerabilities, Including an Exploited Zero-Day

Microsoft’s October 2026 updates address 1,413 vulnerabilities, including one exploited zero-day, two publicly disclosed flaws and 75 Critical vulnerabilities. The analysis highlights high-impact issues across Windows, Office, Outlook and other products.

Oct 13, 2026
Security News · crowdstrike.com

FBI and CrowdStrike Disrupt U.S. Laptop Farms Used by FAMOUS CHOLLIMA

The FBI and CrowdStrike disrupted U.S. laptop farms used by FAMOUS CHOLLIMA to support fraudulent hires at American companies. The group’s operations continue, and the article lists indicators to help identify suspect job applicants.

Oct 13, 2026
Security News · reversinglabs.com

AI Agents Exposed 13,000+ Internal Screenshots in Public GitHub Repositories

Glow researchers found AI agents exposed more than 13,000 internal screenshots in public GitHub repositories across 300+ organizations, often through developers’ personal accounts. Images included customer records, tokens and internal system details.

Oct 13, 2026
Security News · bleepingcomputer.com

Anthropic Warns Small AI Models Could Soon Self-Replicate Across IoT Devices

Anthropic says small AI models may soon be capable of spreading across IoT devices, but its experiments did not demonstrate a fully autonomous worm. The company recommends stronger IoT defenses.

Oct 13, 2026
Security News · darkreading.com

Anthropic Research Demonstrates Potential for AI Models to Spread Across IoT Devices

Anthropic tested AI models’ ability to spread a payload across Android devices, finding GLM-5.2 could reach most nodes under highly favorable conditions. The study did not demonstrate a practical, self-replicating AI worm.

Oct 13, 2026
Security News · darkreading.com

North Korean Hackers Use Spear-Phishing to Seek Ukraine War Intelligence

Researchers say North Korean-linked actors are spear-phishing Ukrainian government, policy and academic targets for intelligence on the war, military casualties and prisoners. Attacks use reply-baiting and malicious LNK files disguised as PDFs.

Oct 13, 2026
Security News · cyberscoop.com

FTC Sues Companies Accused of Defrauding Sextortion Victims

The FTC alleges Dmitry Belkin and 12 businesses took at least $60 million from sextortion victims while fabricating evidence and failing to deliver promised services. The agency is seeking to bar them from operating.

Oct 13, 2026
Security News · cyberscoop.com

DOJ Charges 14 in Alleged North Korean Remote-Work Scheme, Seizes 187 Computers

The DOJ charged 14 people and seized about 187 computers in an alleged North Korean remote-work scheme involving stolen identities, U.S. laptop farms and more than 70 companies. The FBI also warned that the scheme is evolving.

Oct 13, 2026
Security News · bleepingcomputer.com

Windows 11 24H2 Home and Pro Stop Receiving Security Updates

Microsoft says Windows 11 24H2 Home and Pro reached end of support on October 13, 2026. Their October update was the last; Microsoft advises upgrading to Windows 11 26H2.

Oct 13, 2026
Security News · bleepingcomputer.com

Microsoft Releases Windows 10 KB5126657 Extended Security Update

Microsoft released Windows 10 KB5126657 for Enterprise LTSC and ESU users. It includes October 2026 Patch Tuesday fixes, ReFS security controls, other fixes, and ongoing Secure Boot certificate deployment; some USB audio issues remain unresolved.

Oct 13, 2026
Security News · cyberscoop.com

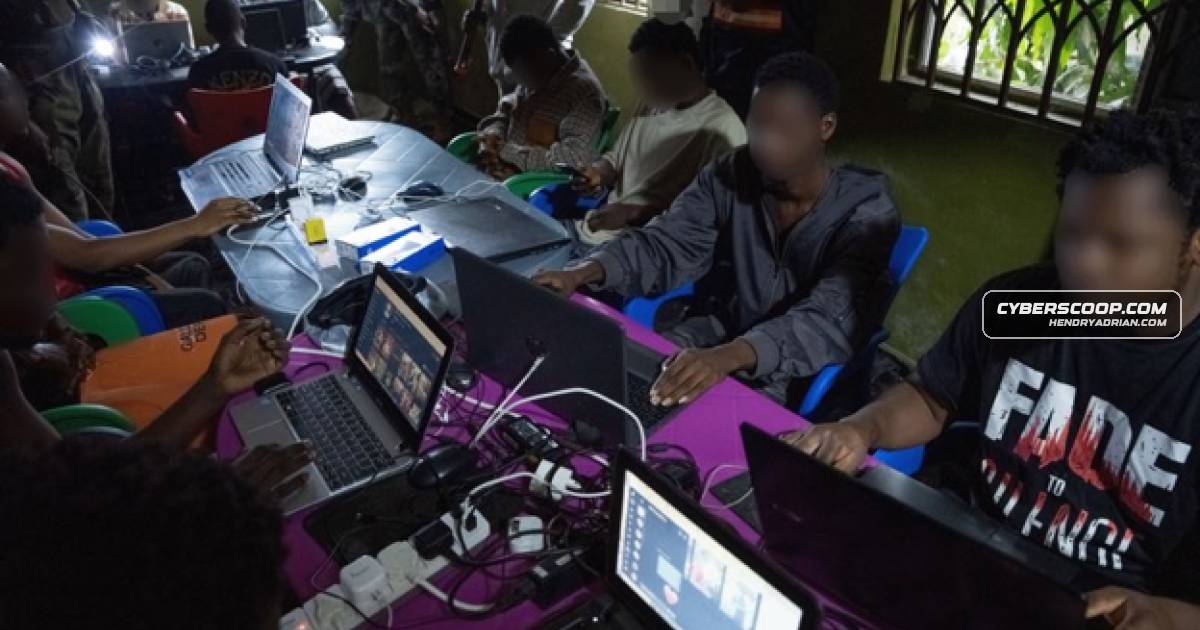
International Operation Targets West African Scam Networks, Nets 28 Arrests

A joint international operation targeting scam networks in West Africa resulted in 28 arrests, 117 trafficking victims rescued, and more than 3.7 million accounts, groups, and pages taken down.

Oct 13, 2026
Security News · aws.amazon.com

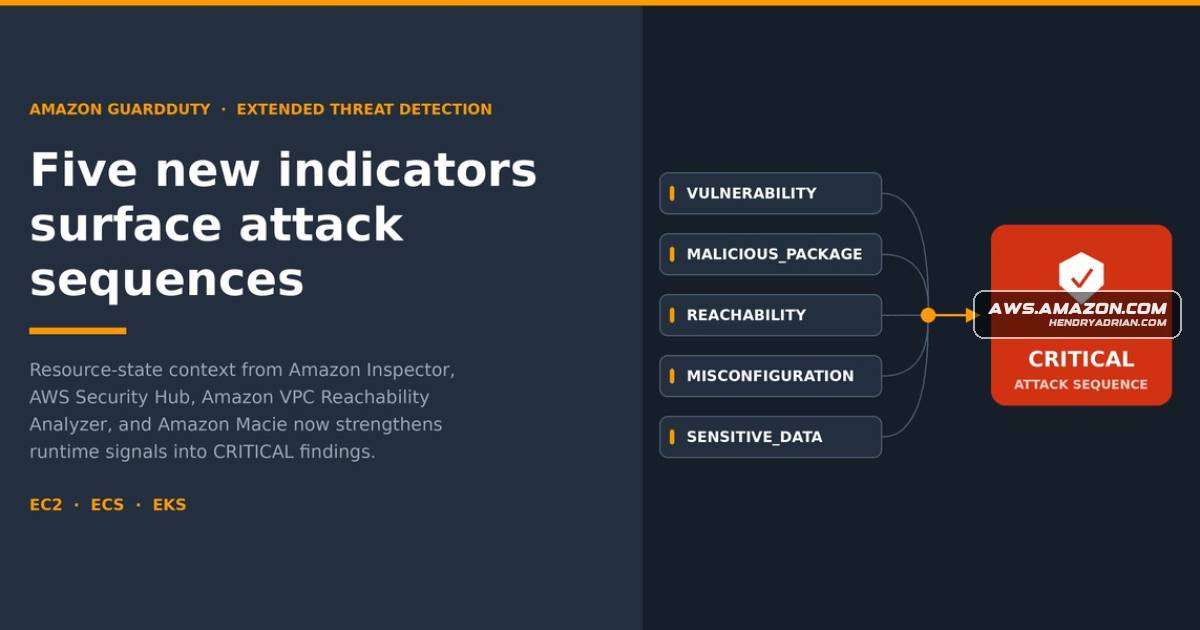
AWS Adds Five Risk Indicators to GuardDuty Extended Threat Detection

AWS says GuardDuty Extended Threat Detection began adding five indicator types to attack-sequence findings on May 20, 2026, correlating runtime signals with vulnerability, package, reachability, misconfiguration, and sensitive-data context.

Oct 12, 2026
Security News · proofpoint.com

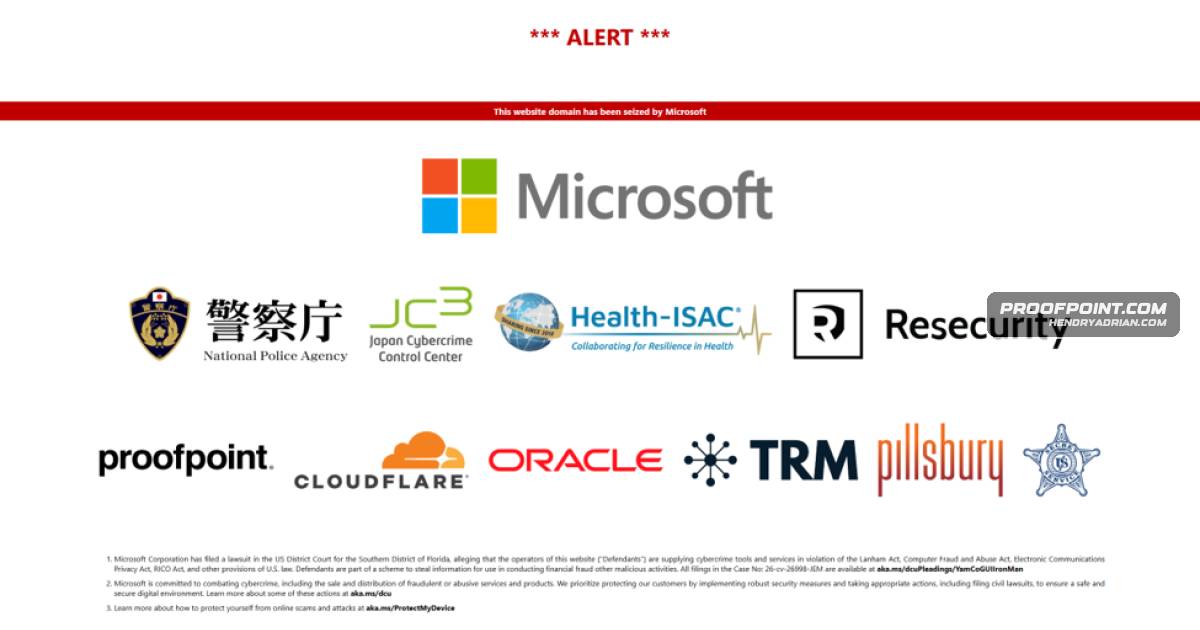
Microsoft-Led Action Disrupts Phishing Kits Targeting Japanese Organizations

Microsoft and partners disrupted infrastructure supporting Chinese-speaking phishing operations, including CoGUI, CoAceV and CoFish_Ws. The kits targeted Japanese organizations with credential and payment-data lures.

Oct 12, 2026
Security News · thehackernews.com

Weekly Cybersecurity Recap Highlights Exploited Atlassian Flaw and Other Threats

The weekly roundup reports active exploitation of a critical Atlassian Data Center file-access flaw and lists numerous security vulnerabilities, while noting broader concerns about malware, ransomware services, and system security.

Oct 12, 2026
Security News · socradar.io

SOCRadar and Torq Integrate Threat Intelligence with Automated Security Response

The SOCRadar–Torq integration sends threat-intelligence alarms to Torq for AI-assisted enrichment and configurable response workflows, with case updates written back to SOCRadar.

Oct 12, 2026
Security News · securityweek.com

IonQ to Acquire Zero-Trust Security Firm Elisity for Up to $1.3 Billion

IonQ agreed to acquire zero-trust security company Elisity for up to $1.3 billion. The companies plan to add cryptographic inventory and risk data to Elisity’s platform to help organizations prioritize post-quantum upgrades.

Oct 12, 2026
Security News · netskope.com

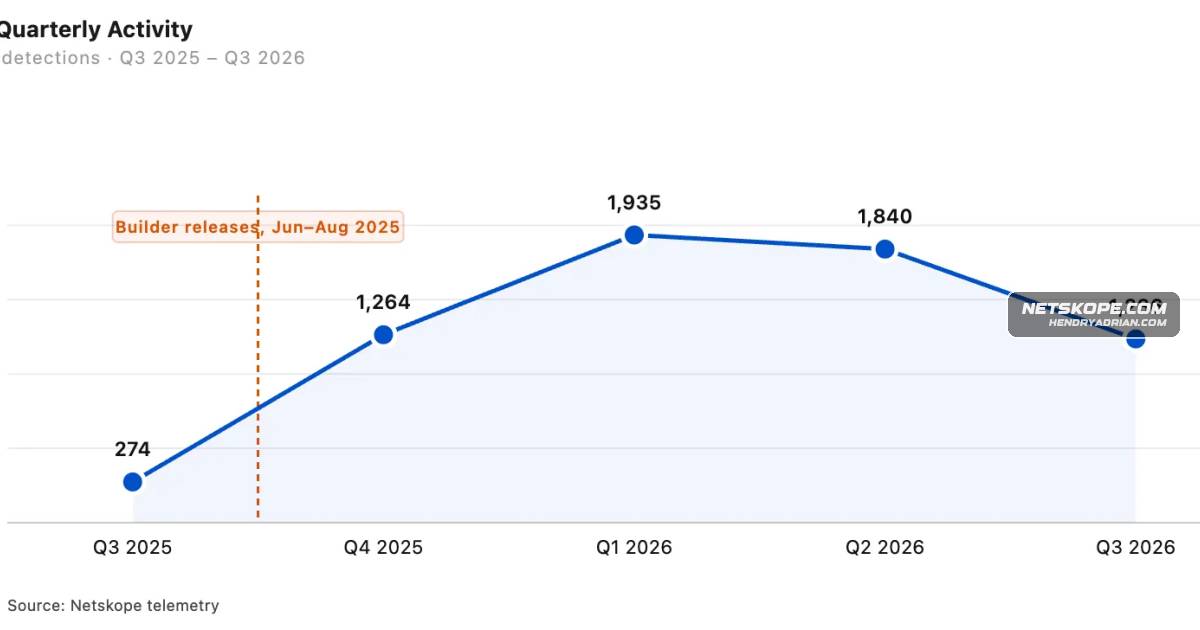
XWorm Activity Surges as Four Versions Operate Concurrently

Netskope reports four XWorm versions operating concurrently and 1,236 detection events across more than 100 customer organizations in Q3 2026, a fourfold increase from Q3 2025.

Oct 12, 2026
Security News · sekoia.com

Sekoia Launches Service to Monitor Criminal Sources for Exposed Credentials

Sekoia Digital Risk monitors criminal forums, stealer logs, and other sources for exposed organizational credentials, sessions, and data, combining those findings with Sekoia threat intelligence to help security teams investigate and respond.

Oct 12, 2026
Security News · securityweek.com

Leader of Cybercrime Money-Mule Network Pleads Guilty in US

Oleg Korniev, a leader of the Your Mule Cashout network, pleaded guilty to helping launder cybercriminals’ proceeds through money mules. The network allegedly recruited over 15,000 US residents and laundered at least $10 million stolen from bank accounts.

Oct 12, 2026
PreviousPage 25 of 150 Next
© 2026 cyber.hendryadrian.com