Microsoft-Led Action Disrupts Phishing Kits Targeting Japanese Organizations
Summary
Microsoft and partners disrupted infrastructure supporting Chinese-speaking phishing operations, including CoGUI, CoAceV and CoFish_Ws. The kits targeted Japanese organizations with credential and payment-data lures.
Key points
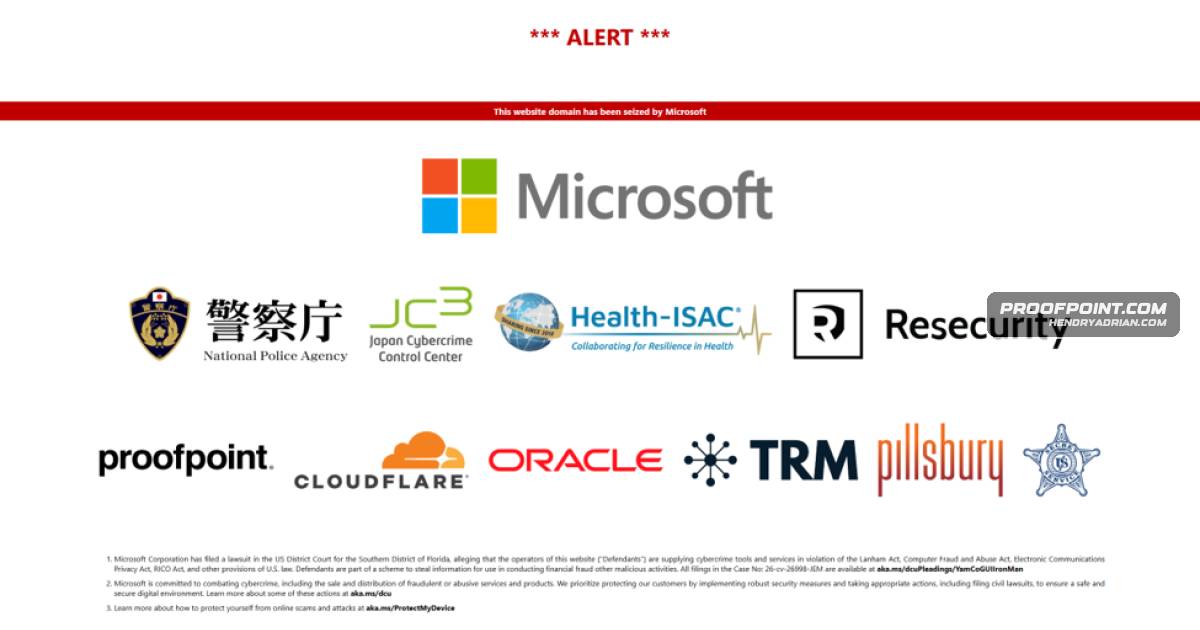
- Microsoft and Health-ISAC filed a civil lawsuit against YAM Store actors and associated individuals; seized domains were redirected.
- Proofpoint supported the action with threat data on CoGUI, CoAceV and CoFish_Ws campaigns and a declaration for the lawsuit.
- The related kits impersonated 66 brands and used roughly 17,000 domains, according to Proofpoint.
- Proofpoint says it detects and blocks more than 100 million monthly email messages targeting organizations with CoGUI.
- Most observed campaigns targeted Japan, particularly financial services and healthcare organizations, to steal credentials and payment data.
Article Details
- Event Type
- Disruption and civil lawsuit targeting Chinese-speaking phishing operations and supporting infrastructure.
- Impact
- The action targeted CoGUI, YAM Store, and Iron Man-related infrastructure, including domains used to enable phishing and fraud. The campaigns stole credentials and payment data and sent hundreds of millions of malicious messages. Proofpoint says the disruption is likely to cause operational friction and affect the efficacy of the phishing operations.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| URL | hxxps[:]//kenandy[.]shop/paidy/ubmisionsjp/ | CoGUI phishing URL identified as an example of the kit's campaign infrastructure. |
| URL | hxxps[:]//lygyaou[.]com/9AioLNhtdi.kumamoto-city.jp | CoGUI phishing URL identified as part of a URL pattern shared across the phishing kits. |
| URL | hxxps[:]//new-app-haixing[.]com/1DWSd1DeDf.kumamoto-city.jp | CoFish_ws phishing URL identified as part of a URL pattern shared across the phishing kits. |
| URL | hxxps[:]//paidy[.]farradae[.]com/paidy/ubmissionsjp | CoAceV phishing URL identified as an example of the kit's campaign infrastructure. |
| URL | hxxps[:]//ylhgkj[.]com/BCuXkTPfKZ.kumamoto-city.jp | CoAceV phishing URL identified as part of a URL pattern shared across the phishing kits. |
MITRE ATT&CK
Threat Actors
Countries
AustraliaThe vast majority of tracked CoGUI/CoAceV/CoFish_Ws campaigns impact Japan, with a few impacting the United States of America, Australia, and Italy.ItalyThe vast majority of tracked CoGUI/CoAceV/CoFish_Ws campaigns impact Japan, with a few impacting the United States of America, Australia, and Italy.JapanCoGUI and related infrastructure was disrupted in collaboration with private and public partners including Proofpoint, Microsoft, Japan Cybercrime Control Center (JC3), Resecurity, Cloudflare, Oracle, and TRM Labs.United StatesThe vast majority of tracked CoGUI/CoAceV/CoFish_Ws campaigns impact Japan, with a few impacting the United States of America, Australia, and Italy.
Industries
EducationAccording to our email threat data, the most frequently impacted business sectors are Financial Services and Healthcare, with Government, Education, and Manufacturing rounding out the top five impacted sectors.Financial ServicesAccording to our email threat data, the most frequently impacted business sectors are Financial Services and Healthcare, with Government, Education, and Manufacturing rounding out the top five impacted sectors.GovernmentAccording to our email threat data, the most frequently impacted business sectors are Financial Services and Healthcare, with Government, Education, and Manufacturing rounding out the top five impacted sectors.HealthcareAccording to our email threat data, the most frequently impacted business sectors are Financial Services and Healthcare, with Government, Education, and Manufacturing rounding out the top five impacted sectors.ManufacturingAccording to our email threat data, the most frequently impacted business sectors are Financial Services and Healthcare, with Government, Education, and Manufacturing rounding out the top five impacted sectors.