
SOCRadar and Torq Integrate Threat Intelligence with Automated Security Response
Summary
The SOCRadar–Torq integration sends threat-intelligence alarms to Torq for AI-assisted enrichment and configurable response workflows, with case updates written back to SOCRadar.
Key points
- SOCRadar sends every alarm and incident to Torq; customer-configured workflows determine which cases trigger actions.
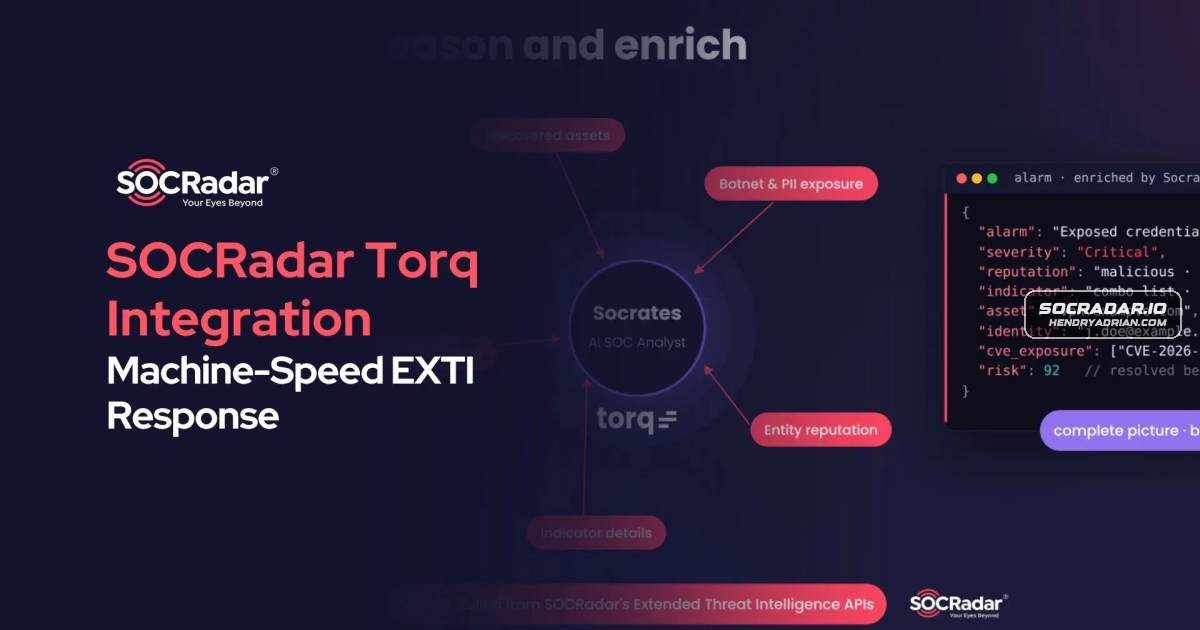
- Torq’s Socrates AI SOC Analyst can enrich investigations with entity reputation, indicator details, CVE intelligence and discovered-asset context, subject to SOCRadar API entitlements.
- Configured workflows can rotate credentials, revoke sessions, block indicators, initiate takedowns and open cases.
- Torq can write alarm status, severity, assignee, tags and comments back to SOCRadar.
- A described example workflow checks exposed credentials against an identity provider, resets passwords, revokes sessions, opens a case and updates the SOCRadar alarm.
Article Details
- Event Type
- Integration launch connecting SOCRadar Extended Threat Intelligence with Torq for AI-assisted enrichment and automated security response.
- Impact
- SOCRadar alarms and incidents are sent to Torq, where Socrates enriches investigations with reputation, indicator, CVE, and discovered-asset context. Configured workflows can rotate credentials, revoke sessions, block indicators, submit takedown requests, and open cases; updates are written back to SOCRadar. Enrichment depends on customers’ SOCRadar API entitlements, and response actions depend on configured workflows.
Vendors
Products
SOCRadar Extended Threat IntelligenceSOCRadar Extended Threat Intelligence continuously monitors the Surface, Deep and Dark Web alongside your organization’s external attack surface, correlating findings into prioritized alarms and incidents.SocratesSocrates, Torq’s AI SOC Analyst, enriches every SOCRadar alarm with reputation, indicator, CVE and discovered-asset context before an analyst is involved.