
Europol-Led Operation Disrupts Tycoon 2FA Phishing Service, Taking Down 330 Domains
Summary
A coordinated law enforcement and industry operation dismantled Tycoon 2FA, a subscription AiTM phishing service, taking down 330 domains. Researchers and vendors linked it to tens of millions of phishing emails and large-scale account takeover attempts.
Key points
- A coordinated operation involving law enforcement and security companies took down 330 domains used for Tycoon 2FA phishing pages and control panels.
- The subscription phishing service used adversary-in-the-middle techniques to capture credentials, MFA codes, and session cookies.
- Europol said the platform generated tens of millions of phishing emails monthly and facilitated unauthorized access to nearly 100,000 organizations.
- Intel 471 linked Tycoon 2FA to more than 64,000 phishing incidents; Microsoft said it blocked over 13 million related malicious emails in October 2025.
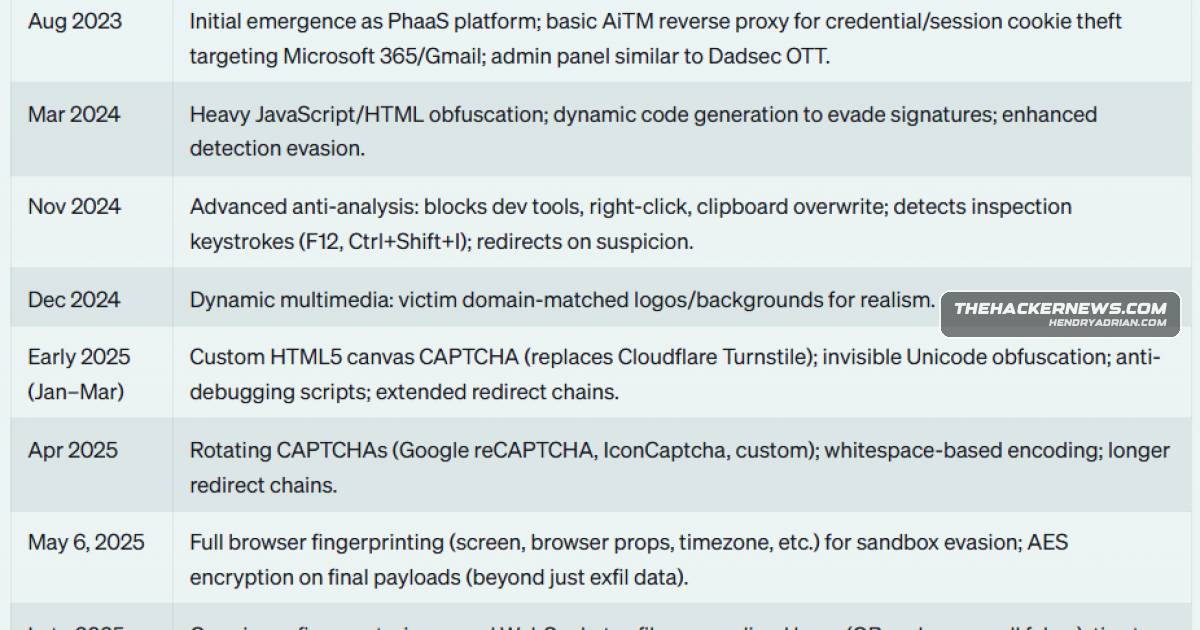
- The service used techniques including browser fingerprinting, anti-bot screening, obfuscation, and short-lived domains that often lasted 24 to 72 hours.
- Proofpoint said attackers used compromised email accounts to distribute Tycoon 2FA links in a technique called ATO Jumping.
Article Details
- Event Type
- Coordinated law enforcement and private-sector disruption of the Tycoon 2FA phishing-as-a-service platform.
- Impact
- The operation took down 330 domains used for phishing pages and control panels. Tycoon 2FA was linked to more than 64,000 phishing incidents, approximately 96,000 distinct victims, and unauthorized access affecting nearly 100,000 organizations. The service harvested credentials, MFA codes, and session cookies, enabling account takeovers and potential continued access after password resets.
MITRE ATT&CK
T1056.001 · KeyloggingThe kit employed keystroke monitoring to capture user input.T1111 · Multi-Factor Authentication InterceptionThe operators relayed captured MFA codes through proxy servers to authenticating services.T1539 · Steal Web Session CookieThe platform captured session cookies, which could enable continued access to accounts.T1557 · Adversary-in-the-MiddleThe service used adversary-in-the-middle techniques to intercept authentication data.T1566 · PhishingTycoon 2FA generated phishing emails to direct victims to fraudulent sign-in pages.
People
Threat Actors
Vendors
Intel 471Characterizing Tycoon 2FA as “dangerous,” Intel 471 said the kit was linked to over 64,000 phishing incidents and tens of thousands of domains, generating tens of millions of phishing emails each month.Microsoft#Tycoon2FA #MicrosoftProofpointData from Proofpoint shows that Tycoon 2FA accounted for the highest volume AiTM phishing threats.SpycloudGeographic analysis of victim log data by SpyCloud indicates that the U.S.Trend MicroTrend Micro, which was one of the private sector partners in the operation, noted that the PhaaS platform had approximately 2,000 users.
Products
Gmail“Tycoon 2FA’s platform enabled threat actors to impersonate trusted brands by mimicking sign-in pages for services like Microsoft 365, OneDrive, Outlook, SharePoint, and Gmail,” Microsoft said.Microsoft 365 Apps for Enterprise“Tycoon 2FA’s platform enabled threat actors to impersonate trusted brands by mimicking sign-in pages for services like Microsoft 365, OneDrive, Outlook, SharePoint, and Gmail,” Microsoft said.Microsoft OneDrive“Tycoon 2FA’s platform enabled threat actors to impersonate trusted brands by mimicking sign-in pages for services like Microsoft 365, OneDrive, Outlook, SharePoint, and Gmail,” Microsoft said.Microsoft SharePoint“Tycoon 2FA’s platform enabled threat actors to impersonate trusted brands by mimicking sign-in pages for services like Microsoft 365, OneDrive, Outlook, SharePoint, and Gmail,” Microsoft said.Outlook“Tycoon 2FA’s platform enabled threat actors to impersonate trusted brands by mimicking sign-in pages for services like Microsoft 365, OneDrive, Outlook, SharePoint, and Gmail,” Microsoft said.
Tools
Countries
Canada(16,901), Canada (15,272), India (7,832), and France (6,823).France(16,901), Canada (15,272), India (7,832), and France (6,823).India(16,901), Canada (15,272), India (7,832), and France (6,823).PakistanTycoon 2FA’s primary developer is alleged to be Saad Fridi, who is said to be based in Pakistan.United Kingdomhad the largest concentration of identified victims (179,264), followed by the U.K.United StatesGeographic analysis of victim log data by SpyCloud indicates that the U.S.
Industries
EducationCampaigns leveraging Tycoon 2FA have indiscriminately targeted almost all sectors, including education, healthcare, finance, non-profit, and government.financeCampaigns leveraging Tycoon 2FA have indiscriminately targeted almost all sectors, including education, healthcare, finance, non-profit, and government.GovernmentCampaigns leveraging Tycoon 2FA have indiscriminately targeted almost all sectors, including education, healthcare, finance, non-profit, and government.HealthcareCampaigns leveraging Tycoon 2FA have indiscriminately targeted almost all sectors, including education, healthcare, finance, non-profit, and government.Non-profitCampaigns leveraging Tycoon 2FA have indiscriminately targeted almost all sectors, including education, healthcare, finance, non-profit, and government.