
Microsoft Disrupts Tycoon 2FA, Seizing 330 Control Panel Domains
Summary
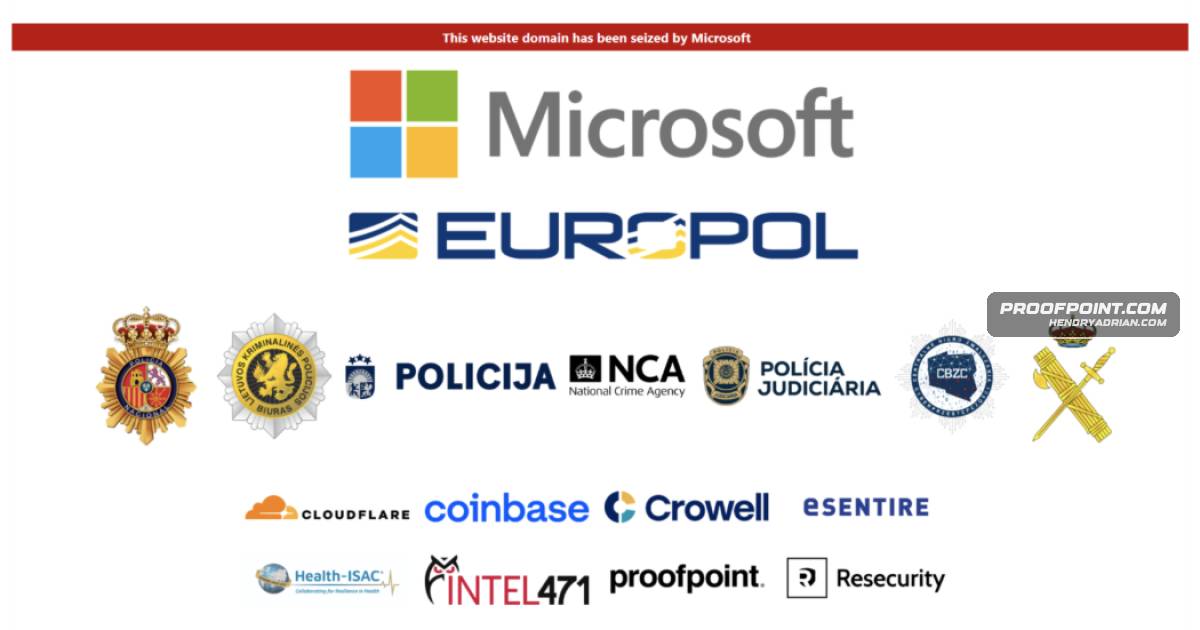
Microsoft and partners disrupted Tycoon 2FA on March 4, 2026, seizing 330 control-panel domains; Microsoft and Health-ISAC also sued its alleged creator. Proofpoint says the AiTM service stole credentials and session cookies to bypass MFA.
Key points
- Microsoft announced the disruption on March 4, 2026, and seized 330 control-panel domains associated with Tycoon 2FA.
- Microsoft and Health-ISAC filed a civil lawsuit naming alleged creator Saad Fridi and unnamed associates.
- Proofpoint describes Tycoon 2FA as an AiTM phishing service that relays credentials to legitimate services and captures Microsoft 365 and Gmail session cookies to bypass MFA.
- Campaigns used email links, QR codes, SVGs, or attachments to direct victims through a CAPTCHA to fake Microsoft or Google login pages.
- Some users employed “ATO Jumping,” using a compromised email account to distribute phishing links that appeared to come from a trusted contact.
- Proofpoint observed more than three million Tycoon 2FA-associated messages in February 2026 and called it the highest-volume AiTM phishing threat in its visibility.
- Microsoft said Tycoon 2FA enabled cybercriminals to access almost 100,000 organizations.
Article Details
- Event Type
- Disruption of the Tycoon 2FA phishing-as-a-service platform, including infrastructure seizures and a civil lawsuit.
- Impact
- Microsoft seized 330 control panel domains associated with Tycoon 2FA. The platform harvests credentials and session cookies to bypass MFA and enable account takeover. Microsoft said it had enabled cybercriminals to access almost 100,000 organizations. Successful account takeovers can expose private and business information and may enable follow-on attacks, including ransomware.
MITRE ATT&CK
T1078 · Valid AccountsSome users compromise an initial email account and use it to distribute Tycoon 2FA URLs to the account’s contacts.T1550.003 · Pass the TicketThe kit captures Microsoft 365 and Gmail session cookies, which threat actors use to bypass MFA and take over accounts.T1557 · Adversary-in-the-MiddleTycoon 2FA operates as an adversary-in-the-middle proxy, intercepting credentials and relaying them to legitimate services.T1566 · PhishingTycoon 2FA is distributed through email campaigns that lure recipients to attacker-controlled sites.T1566.001 · Spearphishing AttachmentCampaigns may use attachments, including PDFs containing QR codes, to direct recipients to Tycoon 2FA landing pages.T1566.002 · Spearphishing LinkCampaign emails may contain malicious links or QR codes that direct recipients to Tycoon 2FA landing pages.
Threat Actors
Vendors
GoogleAttackers distribute Tycoon 2FA via email campaigns using malicious links, QR codes, SVGs, and attachments that redirect victims to actor-controlled landing pages mimicking Microsoft or Google login portals.MicrosoftTycoon 2FA is a high-volume adversary-in-the-middle (AiTM) phishing-as-a-service platform that harvests credentials and Microsoft 365 and Gmail session cookies to bypass MFA and enable account takeover.ProofpointMicrosoft and a coalition of private and public partners, including Proofpoint and Europol, disrupted Tycoon 2FA infrastructure, seized 330 control panel domains, and filed a civil lawsuit naming alleged creator Saad
Products
Azure ADIn many cases, the threat actor will display a target organization’s Azure Active Directory branding to further the social engineering component and trick a user into thinking they are entering their credentials into aGmailTycoon 2FA is a high-volume adversary-in-the-middle (AiTM) phishing-as-a-service platform that harvests credentials and Microsoft 365 and Gmail session cookies to bypass MFA and enable account takeover.Microsoft 365 Apps for EnterpriseTycoon 2FA is a high-volume adversary-in-the-middle (AiTM) phishing-as-a-service platform that harvests credentials and Microsoft 365 and Gmail session cookies to bypass MFA and enable account takeover.Tycoon2FATycoon 2FA is a high-volume adversary-in-the-middle (AiTM) phishing-as-a-service platform that harvests credentials and Microsoft 365 and Gmail session cookies to bypass MFA and enable account takeover.
Countries
Canadaand Canada, with additional activities targeting many European countries including Germany, Spain, France, and the UK.Franceand Canada, with additional activities targeting many European countries including Germany, Spain, France, and the UK.Germanyand Canada, with additional activities targeting many European countries including Germany, Spain, France, and the UK.LatviaIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.LithuaniaIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.PolandIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.PortugalIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.SpainIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.United KingdomIn coordination with Europol, law enforcement in Latvia, Lithuania, Portugal, Poland, Spain and the United Kingdom carried out a seizure of infrastructure and other operational measures.United StatesThe disruption and associated civil filing in the United States Southern District of New York will have a significant impact on Tycoon 2FA operations and overall threat activity.
Industries
Educationvia compromised accounts from various industries including legal, real estate, healthcare, government, education, construction, and technology, as well as personal emails such as Gmail addresses.Governmentdistributed via compromised accounts from various industries including legal, real estate, healthcare, government, education, construction, and technology, as well as personal emails such as Gmail addresses.HealthcareTycoon 2FA distributed via compromised accounts from various industries including legal, real estate, healthcare, government, education, construction, and technology, as well as personal emails such as Gmailreal estatehas observed Tycoon 2FA distributed via compromised accounts from various industries including legal, real estate, healthcare, government, education, construction, and technology, as well as personal emails such asTechnologyvarious industries including legal, real estate, healthcare, government, education, construction, and technology, as well as personal emails such as Gmail addresses.