
MedusaLocker Claims It Targeted Karneslegal and Extracted 23 Emails
Ransomware.live records MedusaLocker’s claim that it targeted Karneslegal and extracted 23 emails; the post says it cannot confirm the information.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2814 articles
Ransomware.live records MedusaLocker’s claim that it targeted Karneslegal and extracted 23 emails; the post says it cannot confirm the information.
A ransomware.live-monitored record attributes to Spacebears a claim that Salters Propane employees’ and clients’ personal information, financial documents, and other files were exposed. The publisher says the claim is unconfirmed.

A ransomware.live monitoring record attributes a ransomware claim against German food manufacturer Tofutown to Payload. The post says operations and data availability were affected, but notes the claims are unconfirmed.
Ransomware.live lists Estrela in Brazil as a MedusaLocker victim; the group reportedly claims 11 email accounts were extracted. The post says the claim is unconfirmed.
Incransom claimed an attack on Colorado Rehabilitation and Occupational Medicine, a Colorado healthcare provider. The claim was listed on the actor's disclosure site and monitored by ransomware.live; the information is unconfirmed.

Ransomware.live records an Anubis claim that Northeast Pediatrics & Adolescent Medicine suffered a data breach exposing employee and patient information. The post says the claim is unconfirmed.
Safepay’s leak site lists eaglecrestlife[.]org, identified as operating under Bethany Lutheran Homes, as a ransomware victim. The monitoring post says the claim is unconfirmed; compromise is not independently established.
A ransomware.live monitoring record attributes a ransomware claim against dia179[.]com, a German industrial architecture and logistics facilities firm, to SafePay. The claim is unconfirmed; the record alleges vulnerability exploitation.
Ransomware.live records an unconfirmed SafePay claim targeting awo-suedost[.]de, a regional branch of Germany’s Arbeiterwohlfahrt. The post provides no independent confirmation or details about the alleged impact.
Ransomware.live lists Laughlin Nunnally Hood & Crum as a Qilin ransomware victim, citing the actor’s leak-site post. The claim is unconfirmed; the article says it cannot verify the information.
Qilin is attributed with claiming a ransomware attack against Mattatuck Industrial Scrap Metal in the US. ransomware.live recorded the claim on July 1, 2026; the post says it could not confirm the claim.
A ransomware[.]live monitoring record attributes to Qilin a claim that it attacked Dennis Waters Rental Properties in the UK, encrypted files and disrupted operations. The claim is unconfirmed.

ShinyHunters reportedly claimed Ingram Content Group failed to reach an agreement after repeated offers. The claim was monitored by ransomware.live and is unconfirmed.
A ransomware.live monitoring record attributes to ShinyHunters an unconfirmed claim that more than 21 million Fluke Corporation Salesforce records, including some PII, were compromised. The group also claims the dataset exceeds 100GB.
Ransomware.live lists Chamco, a manufacturing company, in a Qilin ransomware claim dated June 30, 2026. The post alleges compromised systems and disrupted data access, but its accuracy is unconfirmed.
Ransomware.live reports that Settra claimed to have compromised Wilfley.com, a U.S. pump manufacturer, and demanded payment. The post cites a leak-site listing but says the claim is unconfirmed.

Settra claims it disrupted Joy Construction Corp. The claim is attributed to the actor's leak page and monitored by ransomware[.]live; the article says it could not confirm the claim.

Ransomware.live reports that Settra listed City Lumber Company (clc-tn[.]com) on its leak site, claiming files were encrypted and ransom demanded. The claim is unconfirmed.
Ransomware[.]live reports that Genesis claims to have targeted Brooklyn Defender Services and demanded ransom after allegedly encrypting data. The post says the claim is unconfirmed.
A ransomware[.]live monitoring entry records an unconfirmed Play ransomware-group claim targeting Western Construction in the US on June 30, 2026. The claimed operational disruption is not independently confirmed.
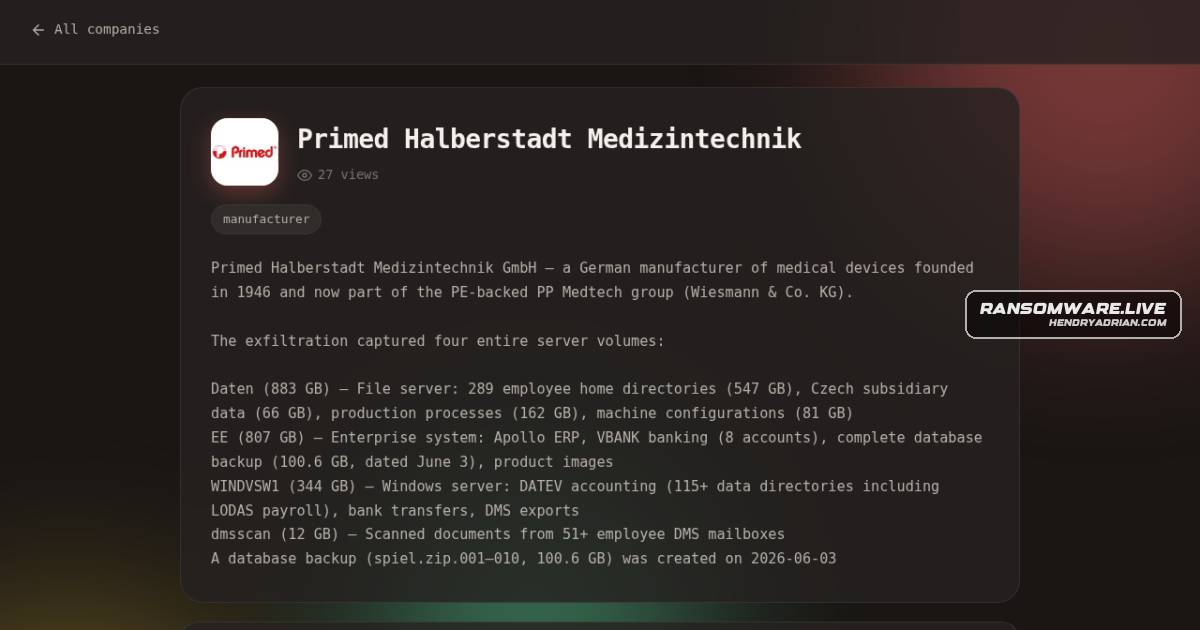
Ransomware.live reports that aurora claims to have exfiltrated four server volumes from Primed Halberstadt Medizintechnik, including employee, production, banking and accounting data. The claims are unconfirmed.
BrainCipher reportedly claims it attacked paipharma[.]com in Brazil. The monitoring post alleges unauthorized access, file encryption, service disruption and potential data exposure; the post says the claims are unconfirmed.
The Chaos ransomware group claims it holds 315 GB of Universal Plant Services’ corporate, financial and operational data and issued a “FINAL NOTICE”; the claim is unverified and attributed to ransomware.live monitoring.
Incransom claims it exposed client information, contracts, personal data, and NDA documents linked to sza[.]it in Italy. The monitoring post says the claim is unconfirmed.