
Aurora Claims Data Theft at Primed Halberstadt Medizintechnik
Summary
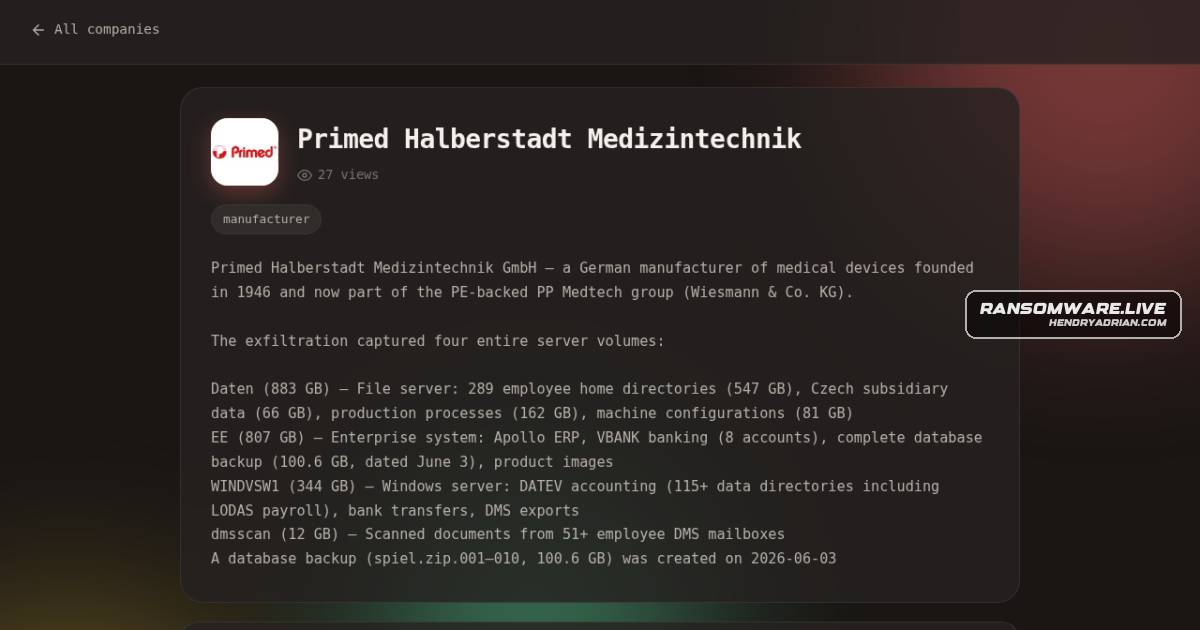
Ransomware.live reports that aurora claims to have exfiltrated four server volumes from Primed Halberstadt Medizintechnik, including employee, production, banking and accounting data. The claims are unconfirmed.
Key points
- Ransomware.live attributes the claims to aurora's leak-site post; the article says it cannot confirm their accuracy.
- The actor reportedly claims to have exfiltrated four server volumes: Daten (883 GB), EE (807 GB), WINDVSW1 (344 GB) and dmsscan (12 GB).
- The claimed data includes employee home directories, production processes, machine configurations and Czech subsidiary data.
- The post also claims the volumes contained Apollo ERP, VBANK banking records, DATEV accounting and payroll data, bank transfers, DMS exports and scanned documents.
- A 100.6 GB database backup, named spiel.zip.001–010, is reportedly dated June 3, 2026.
Article Details
- Victim
- Primed Halberstadt Medizintechnik
- Claim Date
- 2026-06-30
- Encryption Status
- Unknown; the source does not report whether systems or data were encrypted.
- Exfiltration Status
- Claimed by aurora; the source says the claim could not be confirmed.
- Exfiltrated Data
- The claim describes four server volumes containing employee home directories, Czech subsidiary data, production processes, machine configurations, Apollo ERP and VBANK banking records, DATEV accounting and payroll data, bank transfers, DMS exports, product images, and scanned documents. It also reports a database backup created on 2026-06-03.
- Exfiltrated Size
- Claimed volumes: Daten (883 GB), EE (807 GB), WINDVSW1 (344 GB), and dmsscan (12 GB). The database backup is reported as 100.6 GB and is part of the EE volume; it should not be treated as additional volume.
- Ransom Demand
- Not disclosed
- Leak Status
- The source reports a public claim on aurora's blog, but does not establish whether data was published or whether any leaked data is authentic.