

Settra Claims Orion4value.com Documents Were Encrypted
A ransomware.live record attributes to Settra a claim that documents, including financial reports, belonging to Orion4value[.]com in Germany were encrypted. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2815 articles
A ransomware.live record attributes to Settra a claim that documents, including financial reports, belonging to Orion4value[.]com in Germany were encrypted. The claim is unconfirmed.

Settra claims it accessed Petra Diamonds Limited documents, including an employee directory. The monitoring post says the claim is unconfirmed.

Ransomware.live reports that Settra listed Ilex Paysages et Urbanisme (ilex-paysages[.]com) in a ransomware claim, alleging attempted encryption and extortion involving its landscape archive and stored secrets. The publisher says it cannot confirm the claims.

A claim attributed to Settra says owensborograin.com was targeted and faced an extortion demand. The monitoring post says the claim is unconfirmed; its text includes a fragment about IRS-filed tax returns and a truncated threat.

Akira claims it will upload 31 GB of Advanced Business Systems data, including employee information and business and customer documents. The claim is unconfirmed and monitored by ransomware[.]live.
Ransomware.live lists Port Angeles Composite, a U.S. aerospace composite supplier, as a victim claimed by cmdorganization on June 30, 2026. The claim is unverified; no independent incident details are provided.
The ransomware group unsafe claims it targeted straightperformance.de and says operations and data availability were affected. ransomware.live monitored the listing; the claims are unconfirmed.
A ransomware.live monitoring post records Qilin’s unverified claim targeting Musashino University in Japan. The article says the claim cannot be independently confirmed.
Qilin claims it targeted German manufacturer Kunert Fashion with ransomware and demanded payment. The monitoring post says the claim is unconfirmed.
Ransomware.live lists Guardian Barrier Services as a victim claimed by the threeam group; the post alleges ransomware deployment and disruption to event infrastructure operations. The claim and impact are unconfirmed.
Ransomware.live records an unconfirmed Qilin claim targeting Lam Soon in Thailand. The post alleges operational and system/data access disruption, but the article provides no independent confirmation.

ransomware.live lists Boston Orthotics & Prosthetics as an Anubis target and describes a patient-data breach claim. The post says the group’s claim is unconfirmed.

A ransomware-monitoring post records an Anubis claim naming UK medical information services firm ESMS Global Limited. The post says the claim is unconfirmed and provides no independently verified incident details.
Stormous claims it breached ESHA Research/ESHA Cloud Services and stole product-development, intellectual-property, laboratory, and consumer data. The monitoring post says the group’s claims are unconfirmed.
Stormous allegedly claimed access to eogb[.]co[.]uk systems and exfiltration of financial, legal, and operational documents. The monitoring post says the claims are unconfirmed.
ransomware.live records a ransomware claim by cmdorganization against METCO Services and Metco Southeast. The post alleges operational disruption, but says the claims have not been independently confirmed.
A ransomware.live monitoring record attributes a claim against HIGUCHI USA, Inc. to Stormous. The group allegedly exposed Sage 50 backups and financial and inventory records; the post says the claims are unconfirmed.
Ransomware.live reports that Stormous claimed an attack on Japan’s higuchi-inc[.]co[.]jp, alleging access to financial statements, Sage 50 backups and operational data; the claims are unverified.
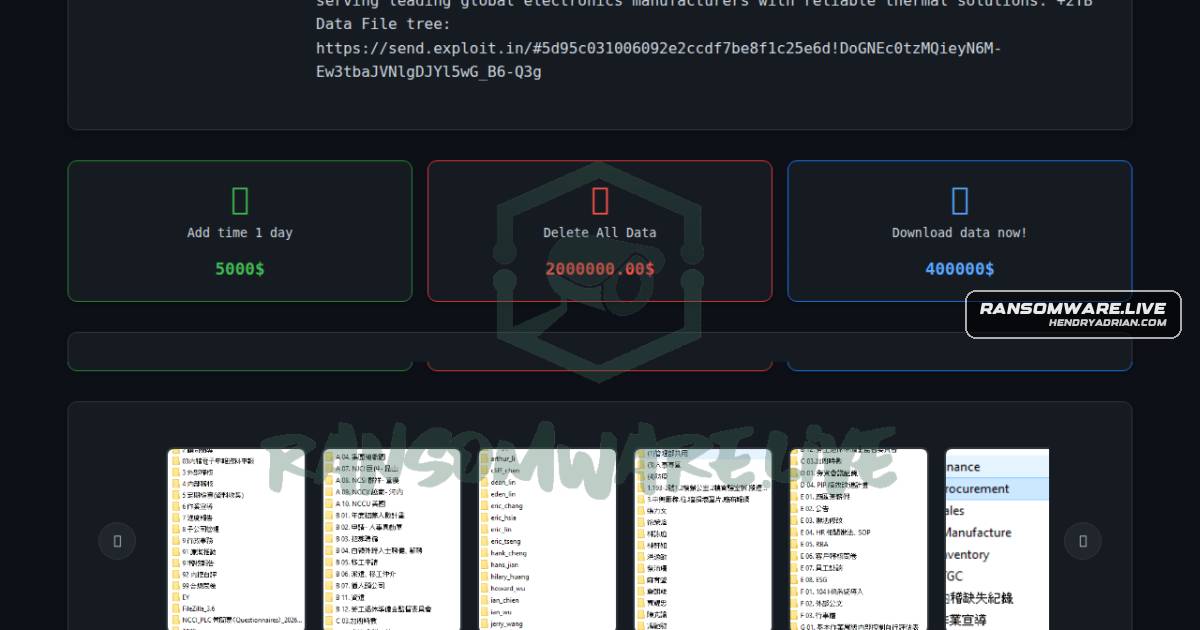
Ransomware.live lists Nidec Chaun-Choung Technology Corporation (CCIC) in Taiwan as a Blackfield ransomware-claim victim, alleging operational and data-availability impact. The post says the claim is unconfirmed.
Actor Kazu allegedly claims to have stolen personal data for 307,133 patients at WELL Health Kensington Medical Centres and demands $70,000 by July 12, 2026, threatening a public sale. The claim is unverified.
Ransomware.live lists NASCO, a U.S. agriculture and food production organization, as a Qilin ransomware victim and reports disruption to system and data access; the post says the group’s claims are unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim targeting Axionlog in the Czech Republic to Qilin. The post says the group’s claim is unconfirmed.

Ransomware.live reports that Payload claimed an attack on Villea Hotels in AttanaHo, alleging file encryption and operational disruption. The post says the claims could not be confirmed.
Ransomware.live reports that the Play ransomware group claims to have targeted J&J Gaming in the U.S.; the post says it cannot verify the claim.