
Krybit Claims DUFLO SAS as Ransomware Victim
A ransomware.live record attributes a claim against DUFLO SAS to krybit and says operations were disrupted. The post cites the actor’s blog; the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2813 articles
A ransomware.live record attributes a claim against DUFLO SAS to krybit and says operations were disrupted. The post cites the actor’s blog; the claim is unconfirmed.
Ransomware.live recorded an unverified krybit claim targeting MAJUHOME Concept in Malaysia. The post says operations were disrupted and data exposure was a risk, but provides no independent confirmation.
Ransomware.live records an unconfirmed claim by the actor “pear” naming Singapore-based CNW Electronics Pte Ltd. The post alleges operational disruption; the article provides no company confirmation.
ransomware[.]live lists Aydeniz Group (aydeniz[.]com) in Turkey as a ransomware claim by apt73. The article describes claimed disruption to systems and data but says it cannot confirm the group's claims.
A ransomware claim attributed to Blackfield names Brazilian footwear manufacturer Redeplast (redeplastrs[.]com[.]br) as a victim. The monitoring post says the claim is unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim against US draft beer service provider AC Beverage, Inc. to the actor “pear.” The post says the claim indicates business disruption, but its accuracy is unconfirmed.

EvaN47 claims to have accessed 287 GB of Libyan Ministry of Education student data and threatens to release certificates, national IDs and photos unless contacted. The allegation is unverified.

A ransomware.live monitoring record attributes to Anubis a claim involving Quest Healthcare Solutions and employee data and internal files. The claim is unconfirmed.
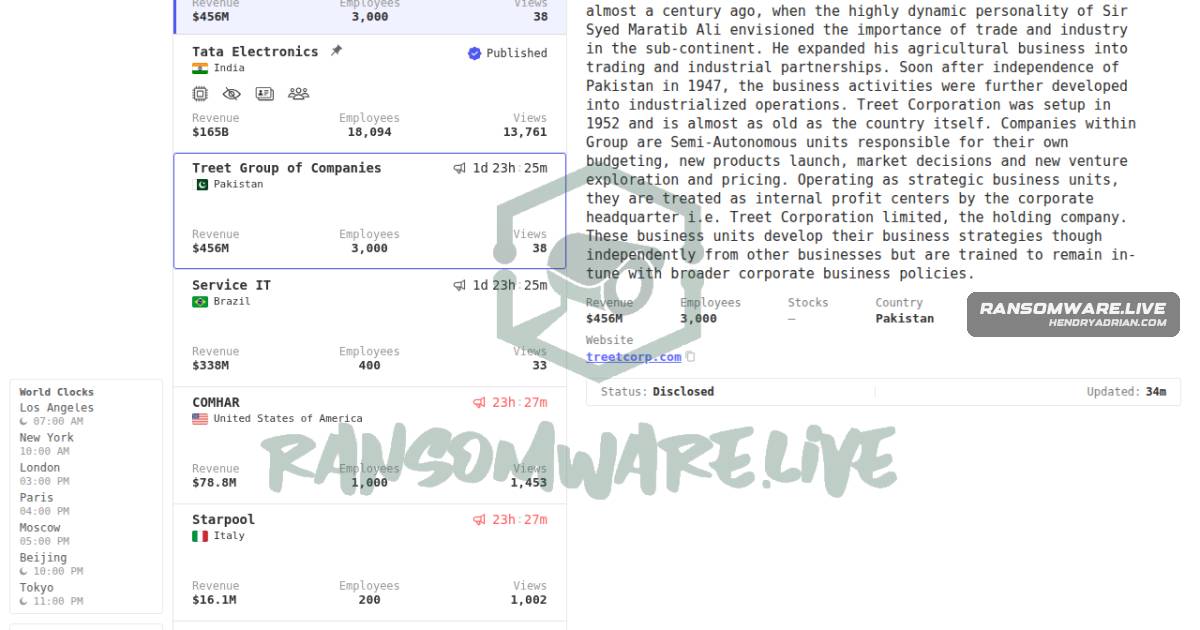
The worldleaks ransomware group listed Pakistan’s Treet Group of Companies on its leak site, according to ransomware.live monitoring. The claim is unverified; no supporting incident details or company response are provided.
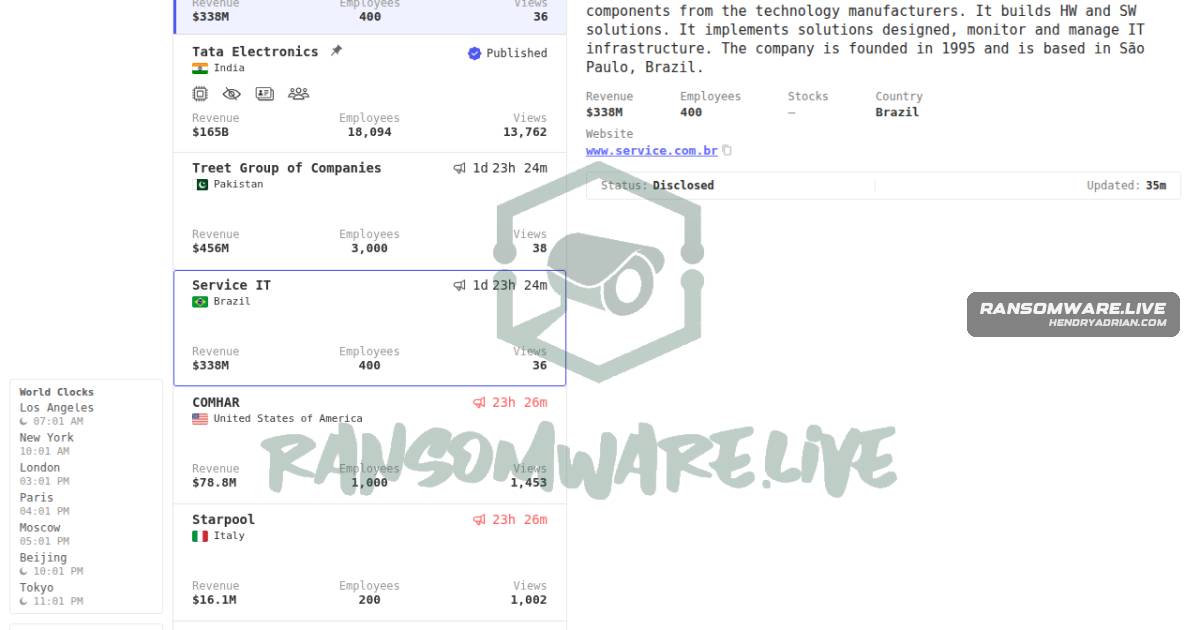
ransomware[.]live lists Service IT in Brazil as a worldleaks ransomware claim. The post cites the group’s leak site, but says the claim has not been confirmed.

A ransomware-monitoring post attributes an unconfirmed breach claim involving Swiss manufacturer Ferrum AG to the Anubis group and links it to a leak-site source.
Incransom claims it disrupted services at Oak Park, Michigan (oakparkmi[.]gov). The post was monitored by ransomware[.]live; the information is unconfirmed.
Incransom claims an incident targeting Hamilton Eye Institute, a Pennsylvania healthcare provider. The report says routine care and other services were disrupted, but the claim is unconfirmed.
Incransom claims it targeted Brazilian company Ezortea in an extortion attempt. The monitoring post says the claim is unconfirmed; it provides no independent evidence that data was encrypted, stolen, or disclosed.
Ransomware.live lists Brazilian freight and logistics provider Carvalima Transportes as a victim in an Incransom claim. The post says operations were disrupted but notes the claim is unconfirmed.
Incransom claims it targeted the City of Acworth, listed as acworth-ga[.]gov, and says data encryption disrupted municipal services. The post attributes the claim to the group but says it cannot confirm the information.
Ransomware.live reports an incransom claim that Flowers Early Learning (formerly Tri-County Head Start) was impacted by ransomware. The article says the group’s claim is unconfirmed.
Ransomware.live reports an incransom claim naming Brazil-based wholesaler Tambasa Atacadistas. The post attributes the claim to the actor’s disclosure blog and says the information has not been independently confirmed.
DarkWebInformer reports an unverified Straightonumberone listing offering alleged Grupo ATC data for $1,000 after reportedly failed ransom talks. The seller claims 23 databases totaling over 340GB include employee and partner information.
Ransomware.live lists ritavo[.]com in Austria as a ransomware target, attributing the claim to APT73. The post says the information is unconfirmed.
APT73 allegedly claims it exfiltrated guest information and internal files from Holiday Palace Hotel in Spain. The claim is attributed to the actor’s leak site and monitored by ransomware[.]live; the information is unconfirmed.
Ransomware.live reports that apt73 claimed Flazio, an Italian website-builder platform, as a victim. The claim is attributed to the group’s leak site and has not been independently confirmed.
Ransomware.live lists Pennant Hills Golf Club in Australia as a Qilin ransomware claim, citing the group's leak-site post. The claim is unconfirmed.
Ransomware.live lists Ontario legal services firm X-Copper Professional as a ransomware victim claimed by moneymessage on July 2, 2026. The post says services were disrupted, but states the claim is unconfirmed.