
BrainCipher Claims Ransomware Attack on Pai Pharma in Brazil
Summary
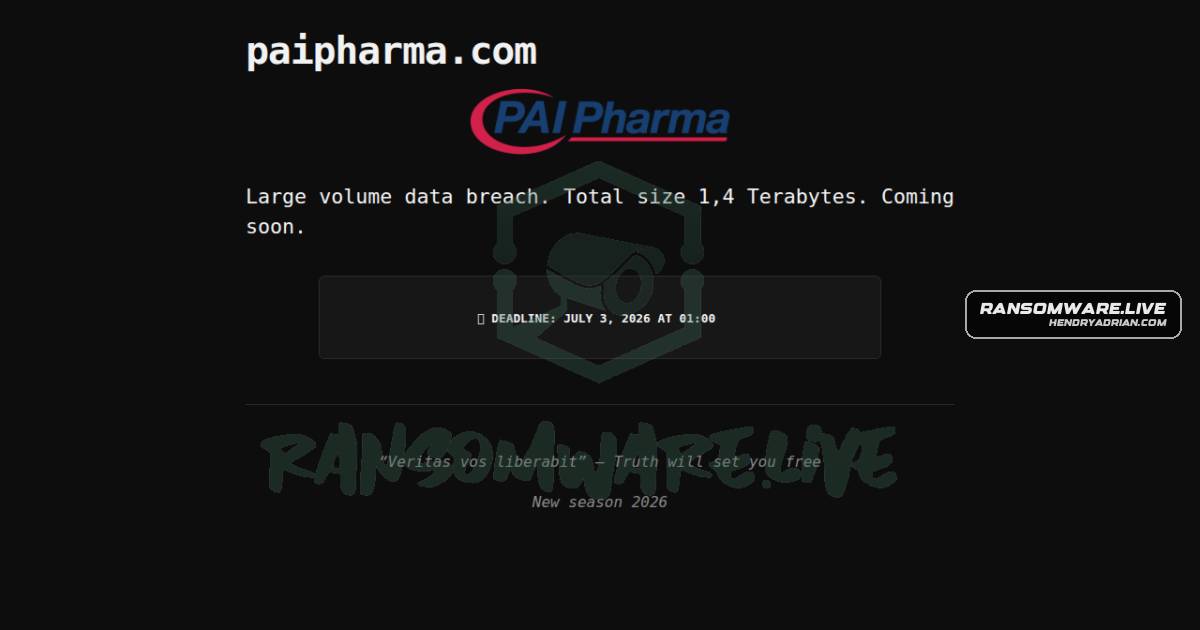
BrainCipher reportedly claims it attacked paipharma[.]com in Brazil. The monitoring post alleges unauthorized access, file encryption, service disruption and potential data exposure; the post says the claims are unconfirmed.
Key points
- The record identifies paipharma[.]com in Brazil as the alleged victim and BrainCipher as the actor.
- A BrainCipher leak-site listing is provided as the claim’s source; ransomware.live is identified as the monitoring service.
- The post alleges unauthorized access, file encryption, service disruption and potential data exposure.
- The post says it cannot confirm the group’s claims; no victim statement or independent confirmation is included.
Article Details
- Victim
- paipharma.com
- Victim Domain
- paipharma.com
- Claim Date
- 2026-06-30
- Encryption Status
- Encryption is reported as part of BrainCipher's public claim; the source cannot confirm its accuracy.
- Exfiltration Status
- Potential data exposure is mentioned, but exfiltration is not confirmed.
- Exfiltrated Data
- Potential data exposure; no specific data is identified.
- Ransom Demand
- Not disclosed
- Leak Status
- The source reports a public group claim but does not report publication of leaked data.