cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · microsoft.com

Microsoft FORGE Shares Lessons from AI-Assisted Vulnerability Research at Scale

Microsoft says its FORGE Lab helped identify Windows vulnerabilities assigned 140 CVEs and submitted 155 validated reports across 23 open-source projects. The team emphasizes scaling validation and remediation alongside AI-assisted discovery.

Oct 7, 2026
Security Insights · thehackernews.com

Why Agentic Pentesting Needs Other Validation Methods to Cover Enterprise Risk

The article says agentic pentesting can prove exploitability and chained attack paths, but its weeks-long runs and limited safe coverage leave gaps. It recommends pairing it with exploitability and security-control validation in a shared findings model.

Oct 7, 2026
Security Insights · rapid7.com

ASOS Investigates Unauthorized Customer App Notification and Possible Data Access

ASOS confirmed an unauthorized customer notification and said basic personal information may have been accessed. Attackers’ claims remain unverified; Snowflake said it had found no compromise of its platform at that point.

Oct 7, 2026
Security Insights · hornetsecurity.com

Security Awareness Best Practices for 2026: Building and Improving Your Program

A practical guide to security awareness programs recommends ongoing, role-based training, realistic phishing simulations, frequent reinforcement, easy reporting, and using program results and incident lessons to improve employee security habits.

Oct 7, 2026
Security Insights · picussecurity.com

Guide to Using Picus for NERC CIP Compliance

Picus outlines how its breach-and-attack simulation, penetration testing, exposure validation, and workflow tools can help electricity-sector entities test controls, prioritize remediation, and document evidence for NERC CIP compliance.

Oct 7, 2026
Security Insights · aikido.dev

Aikido Maps Its Security Platform to SOC 2 Type 1 and Type 2 Evidence Needs

Aikido says its security platform can generate SOC 2 evidence through continuous scanning, remediation tracking, access checks and CI/CD gates. The article contrasts Type 1 snapshot evidence with Type 2 evidence collected across an audit period.

Oct 7, 2026
Security Insights · reversinglabs.com

Why CRA Compliance Must Be Verified Against the Shipped Binary

The article argues that CRA compliance claims must be checked against shipped software, not paperwork alone, and recommends artifact-level evidence reports to identify gaps and support reporting and remediation.

Oct 7, 2026
Security Insights · zimperium.com

Crypters and Similar Techniques Can Help Mobile Malware Evade Signature-Based Detection

An Australian-led advisory warns about crypters used to evade endpoint detection. Zimperium explains that similar obfuscation techniques affect Android malware and argues for combining signature, behavioral, and AI-based detection.

Oct 7, 2026
Security Insights · aws.amazon.com

AWS Shows How Managed Services Can Improve SPIRE Security and Resiliency

AWS explains how to integrate SPIRE with managed services for SVID signing, datastore availability, certificate authority functions, trust-bundle distribution, serverless SVID storage, and fine-grained authorization.

Oct 6, 2026
Security Insights · aws.amazon.com

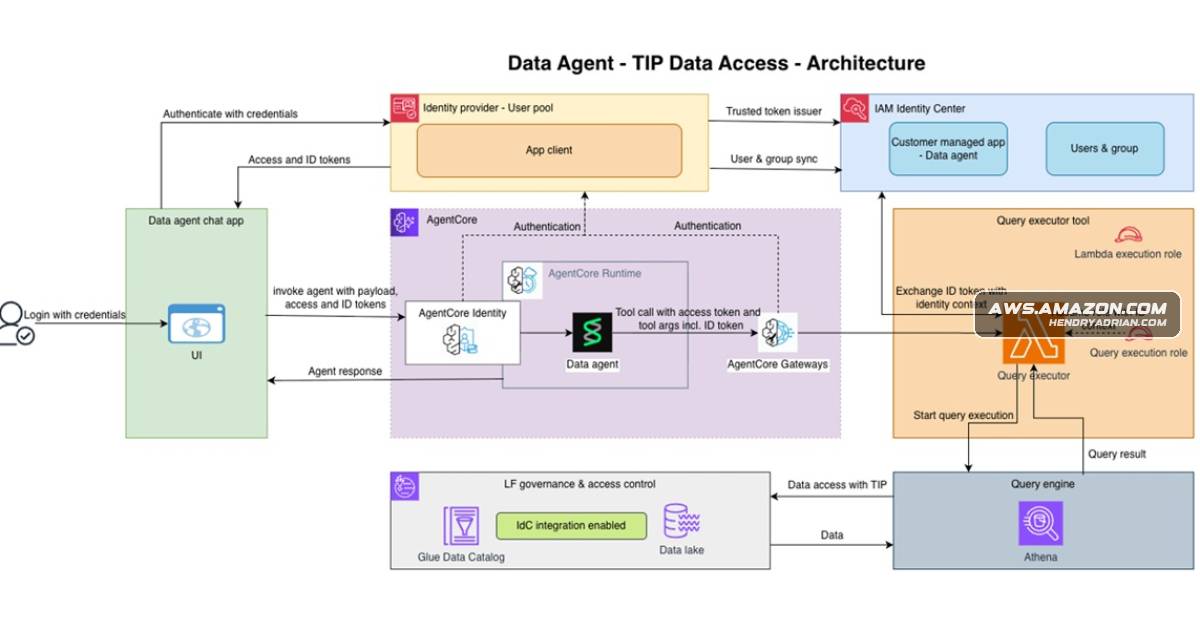
AWS Details Per-User Identity Propagation for AI Data Agents

AWS describes a Bedrock AgentCore pattern that carries users’ identity tokens in HTTP headers to Lambda, where server-side token exchange lets Lake Formation authorize Athena queries as the user while CloudTrail records the human identity; the token stays outside the AI

Oct 6, 2026
Security Insights · microsoft.com

Microsoft Urges CISOs to Rethink Vulnerability Management as AI Scales Discovery

Microsoft says AI-driven vulnerability discovery will increase patch volumes and urges CISOs to prioritize critical fixes, use scanning harnesses, and strengthen defense in depth.

Oct 6, 2026
Security Insights · darkowl.com

GDPR Applies to U.S. Dark Web Investigators Handling EU Data

The article explains how GDPR may apply to U.S.-based investigators handling EU or UK breach data, and recommends documenting a lawful basis, screening sensitive data, minimizing retention, and clarifying controller roles.

Oct 6, 2026
Security Insights · helpnetsecurity.com

U.S. Bank CISO Says Cyber Risk Requires Shared Responsibility

U.S. Bank CISO Ann Barron-DiCamillo discusses the expanding security role, the need for cross-functional partnerships, risk-reducing investment, timely incident reporting, and stronger threat intelligence sharing among banks.

Oct 6, 2026
Security Insights · sekoia.com

Sekoia: Advanced AI Could Bring More Capable Cyber Threats

Sekoia argues that AI could let attackers automate and accelerate intrusions, requiring defenses that reason and act quickly while remaining transparent, auditable, governed by people, and under organizations’ control.

Oct 6, 2026
Security Insights · helpnetsecurity.com

Cybersecurity Job Openings Span IAM, Incident Response, Cloud Security and More

A roundup of cybersecurity openings worldwide covers IAM, network defense, incident response, security architecture, product security, governance, and cloud and AI security.

Oct 6, 2026
Security Insights · iru.com

How to Create and Enforce a Mobile Device Management Policy

A practical guide to creating an MDM policy, covering device scope and ownership, enrollment, access, encryption, updates, monitoring, remote actions, enforcement, and regular review.

Oct 6, 2026
Security Insights · sysdig.com

Three AI Governance Questions Executives Should Be Able to Answer

The article proposes three questions for AI governance: how to detect agents acting against policy, identify every agent and its accountable owner, and preserve trustworthy records. It advocates correlating kernel-level activity with agent-level context for monitoring,|

Oct 6, 2026
Security Insights · jamf.com

Commercial Spyware: How It Infects Mobile Devices and What It Can Expose

An overview of commercial spyware describes how tools infect mobile devices, steal data, and evade detection, with examples including Crocodilus and Landfall. It also outlines warning signs and steps organizations can take to reduce risk.

Oct 6, 2026
Security Insights · huntress.com

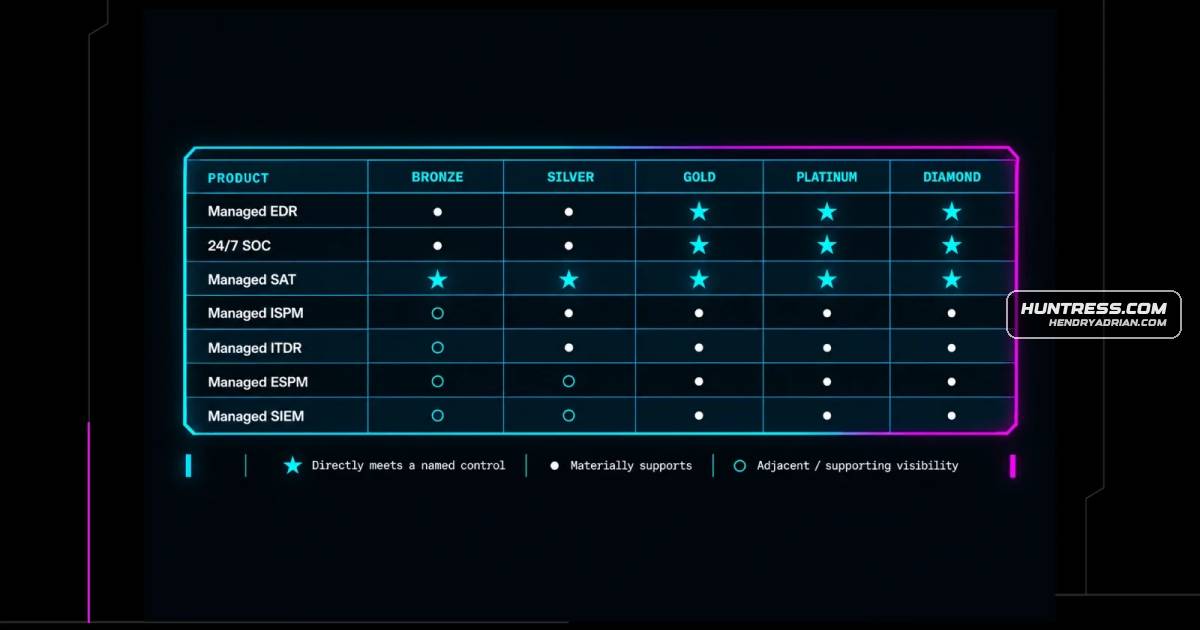
Why the SMB1001 Cybersecurity Standard Is Designed for Small Businesses

The article explains SMB1001’s five-tier cybersecurity certification for small businesses and maps how Huntress services can support some controls, while stressing that certification is awarded independently.

Oct 6, 2026
Security Insights · cyberscoop.com

Op-Ed Urges Stronger Cybersecurity for U.S. Water Systems

An op-ed argues that attacks on water systems in 12 states exposed major security gaps and calls for federal support, zero-trust architecture, safer software, and AI-enabled defenses for utilities.

Oct 5, 2026
Security Insights · picussecurity.com

Five Capabilities for Evidence-Based Exposure Management

Effective exposure management combines asset context, exploitability testing, measured control effectiveness, validated attack paths, and remediation revalidation to prioritize risk and prove that it has been reduced.

Oct 5, 2026
Security Insights · thehackernews.com

Why Security Teams Need Visibility Across the Expanding Credential Layer

As software development and AI-agent use accelerate, credentials spread across repositories, collaboration tools, and developer devices. The article argues that teams need broad discovery and context to understand exposure and prioritize remediation.

Oct 5, 2026
Security Insights · thehackernews.com

AI-Assisted Code Can Embed Flawed Trust Assumptions, a Penetration Test Shows

A penetration test found a financial-services onboarding app could issue or restore applicant access tokens based on possession of a GUID, highlighting the need for human-defined trust rules, threat modeling, and negative testing.

Oct 5, 2026
Security Insights · varonis.com

Data Access Governance Can Limit the Impact of AI-Era Attacks

The article recommends continuously discovering sensitive data, minimizing unnecessary access, governing human and non-human identities, and monitoring data-layer activity to limit exposure if an identity or AI agent is compromised.

Oct 5, 2026
PreviousPage 9 of 54 Next
© 2026 cyber.hendryadrian.com