Why the SMB1001 Cybersecurity Standard Is Designed for Small Businesses
Summary
The article explains SMB1001’s five-tier cybersecurity certification for small businesses and maps how Huntress services can support some controls, while stressing that certification is awarded independently.
Key points
- SMB1001 is a tiered cybersecurity certification standard for small and medium-sized businesses; its 2026 edition became certifiable on January 1, 2026.
- The five tiers—Bronze, Silver, Gold, Platinum and Diamond—cover technology, access, backups, policies and procedures, and education and training.
- Bronze through Gold rely on a director’s attestation; Platinum and Diamond require independent verification.
- The article argues that the tiered approach makes security requirements more achievable for smaller organizations and can support verifiable, cascading supplier assurance.
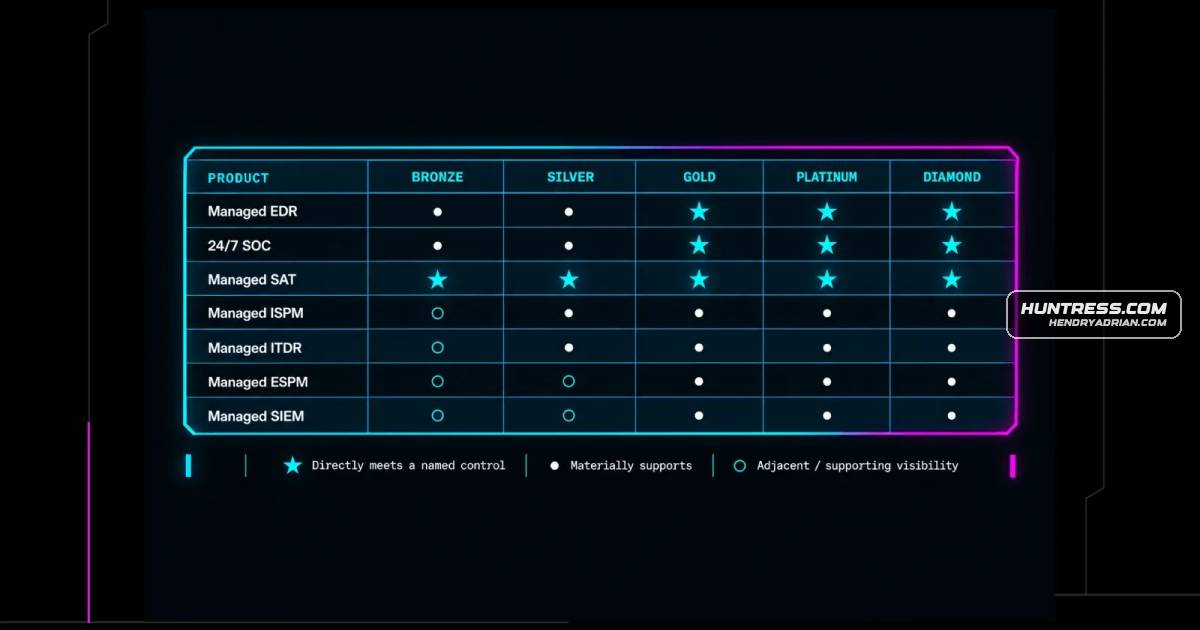
- It maps Huntress services to selected controls, including security training, endpoint protection, identity monitoring, SIEM logging and 24/7 SOC response.
- Huntress tools do not confer certification: CyberCert independently assesses and awards it, and the article does not claim that Huntress covers the full standard.
Article Details
- Topic
- SMB1001 cybersecurity certification for small and medium-sized businesses and how Huntress capabilities map to its tiers
People
Vendors
CyberCertThe standard setter isn't the certifier. DSI writes SMB1001, but CyberCert certifies against it, with independent verification organisations involved at the audited tiers. Keeping those roles apart is deliberate, andDynamic Standards Internationala tiered cybersecurity certification standard built specifically for SMBs. It's published by Dynamic Standards International (formerly Cyber Security Certification Australia), a not-for-profit standards body with anHuntressThis is where SMB1001 comes in. I've spent the last few months in the trenches with Sales Engineer Luca Gennai mapping it against Huntress.Microsoftaccounts and MFA on email. Prevention is the floor, and much of that floor sits with the MSP and with Microsoft-native tooling, which is exactly where it should sit. What changes the outcome is whether anyone is
Products
Conditional AccessISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there, it keeps watching, catching drift within minutesEntra IDFrom Silver up, identity is the real story. Managed ISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there,ExchangeSilver up, identity is the real story. Managed ISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there, itIntuneYour RMM deploys. Huntress tells you where it mattered. Patch delivery belongs with Intune, Windows Update for Business or your RMM. What we bring is the other half of the vulnerability conversation: exposure that'sManaged EDRSMB1001 wants training with proof it happened, and completion reporting that becomes your evidence. Managed EDR does the evidentiary half of the antivirus control, reporting the AV status on every managed endpointManaged ISPMFrom Silver up, identity is the real story. Managed ISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there,Managed ITDRit keeps watching, catching drift within minutes and rolling settings back if a change causes trouble. Managed ITDR sits on top of the attacks that beat the correct configuration. Managed SATManaged SAT is a direct hit here, because SMB1001 wants training with proof it happened, and completion reporting that becomes your evidence. Managed EDR does the evidentiary half of the antivirus control, reporting theManaged SIEMthe model, and always-on detection is the rare control that generates evidence simply by operating. Managed SIEM retains the log trail an assessor actually wants to examine.Microsoft Defenderreporting the AV status on every managed endpoint with richer detail and managed policy for Microsoft Defender and anything else surfaced as "Other AV." When an assessor asks you to prove AV is runningMicrosoft SharePointidentity is the real story. Managed ISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there, it keepsMicrosoft Teamsthe real story. Managed ISPM defines the target configuration across Entra ID, Exchange, SharePoint and Teams and manages Conditional Access with pre-deployment impact analysis. From there, it keeps watching,Windows Update for BusinessYour RMM deploys. Huntress tells you where it mattered. Patch delivery belongs with Intune, Windows Update for Business or your RMM. What we bring is the other half of the vulnerability conversation: exposure that's