cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · darkreading.com

Why Identity Resilience Is Essential to Cyber Resilience

The article argues that organizations need resilient identity systems to restore access to critical applications after cyber incidents. It recommends mapping identity dependencies, monitoring configuration drift, and validating recovery processes.
Oct 12, 2026
Security Insights · cyberscoop.com

AI Agent Security Depends on Inspecting the Software Supply Chain

Recent AI-agent incidents involved sandbox escapes, malicious packages and exposed systems. The author argues that isolation must be paired with inspection of downloaded and published artifacts, open security tooling, and timely disclosure.

Oct 12, 2026
Security Insights · thehackernews.com

Third-Party AI Agents Often Evade Enterprise Identity Controls, Article Warns

The article argues that many third-party AI agents bypass traditional identity controls and recommends continuous visibility into their identities, permissions, connectivity, and activity.

Oct 10, 2026
Security Insights · matthewrosenquist.substack.com

Cybersecurity Defense Must Account for Adversaries’ Goals and Capabilities

The article argues that as AI makes cyber threats more powerful, defenders must look beyond their own security posture and consider adversaries’ targets, objectives, capabilities, and likely methods.

Oct 9, 2026
Security Insights · sekoia.com

Sekoia Executive Says AI-Powered SOCs Need Context and Human Oversight

Sekoia’s Cyril Simonnet discusses how connected data, adaptable runbooks, and human judgment can make AI more useful in security operations, and urges teams to test AI claims with controlled attacks and clear evidence.

Oct 9, 2026
Security Insights · cisecurity.org

4 Ways AI Is Changing the Public Safety Threat Landscape

CIS explains how AI can lower barriers, increase the speed and scale of illicit activity, make deception more convincing, and blur threat boundaries. It recommends incorporating AI into existing public-safety planning and coordination.

Oct 9, 2026
Security Insights · reliaquest.com

ReliaQuest Promotes an AI SOC That Connects Security Operations Across Six Functions

ReliaQuest argues that AI SOC platforms should connect investigation and response, detection engineering, threat hunting, threat intelligence, IT operations, and OT. It promotes GreyMatter as an example and cites performance figures for the platform.

Oct 9, 2026
Security Insights · helpnetsecurity.com

BPFDoor’s Stealth Puts Telecom and Network-Edge Devices at Risk

Rapid7’s Christiaan Beek explains how BPFDoor silently gains access to Linux systems, why attackers target poorly monitored edge devices, and what teams can check to improve visibility.

Oct 9, 2026
Security Insights · helpnetsecurity.com

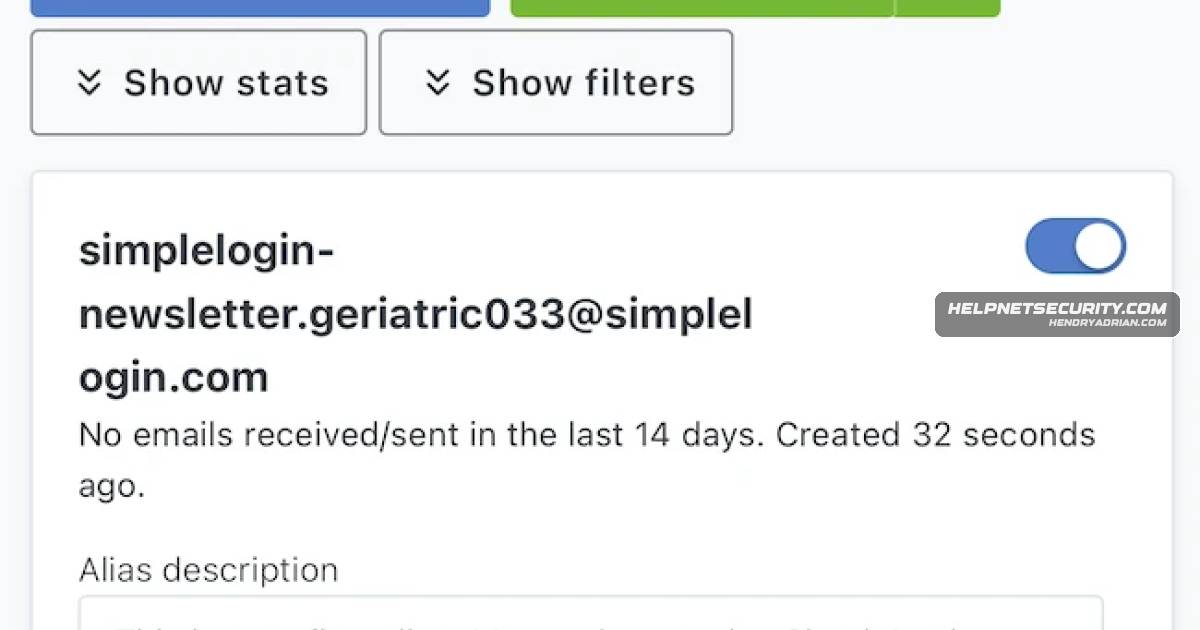
SimpleLogin Email Aliases Help Hide Your Address and Manage Unwanted Mail

A hands-on review finds that SimpleLogin forwards messages and replies through aliases, helping users conceal their primary email address. The service offers alias controls, browser extensions, mobile apps, and two-factor authentication.

Oct 9, 2026
Security Insights · aikido.dev

Six Developer Security Platforms Compared for Enterprise Teams

A buyer’s guide compares six developer security platforms across code, dependencies, cloud, runtime, governance and remediation, highlighting product-specific strengths and limits and offering criteria for enterprise evaluation.

Oct 9, 2026
Security Insights · darkreading.com

Attackers Target Executives’ Families to Reach Corporate Networks

Attackers exploit executives’ relatives through social engineering, compromised devices, and exposed personal information. The article urges families to reduce digital footprints, use strong passwords and MFA, protect against SIM swapping, and recognize scams.

Oct 9, 2026
Security Insights · bleepingcomputer.com

How to Enforce Security Boundaries for AI Agents

A Token Security-sponsored guide compares ways to keep AI agents within approved permissions, emphasizing scoped credentials and controls that can inspect or block actions wherever agents run.

Oct 9, 2026
Security Insights · darkowl.com

What Malware-as-a-Service Is and How It Enables Cybercrime

An explainer describes how Malware as a Service lets criminals rent malware and supporting infrastructure, outlines common offerings and the MaaS ecosystem, and recommends layered defenses such as EDR, MFA, patching, backups, and darknet monitoring.

Oct 8, 2026
Security Insights · securityweek.com

Why Security Awareness Training Needs a Rethink Against Modern Social Engineering

Experts say generic, infrequent awareness training struggles against evolving, AI-assisted social engineering. The article explores memory and behavior, recommending refreshed, contextual training backed by technical controls and clear processes.

Oct 8, 2026
Security Insights · cyberbuilders.substack.com

How to Secure AI Workflows Against Fraud, Data Exposure, and Misuse

The article argues that AI security must address business fraud, sensitive data exposure, and the varied authority of AI systems. It recommends starting with a high-risk workflow and clarifying what AI can access, disclose, and change.

Oct 8, 2026
Security Insights · decodedsecurity.com

Why Cybersecurity Work Is Becoming More Data-Driven

The article explains how data analysis informs cybersecurity work and shows why a detection rule with high accuracy can still generate mostly false alerts when malicious events are rare.

Oct 8, 2026
Security Insights · aikido.dev

Guide Compares Seven FedRAMP Security Tools for Federal Agencies

The guide compares seven FedRAMP security tools across code and cloud coverage, AI remediation, authorization levels, air-gapped deployment and pentesting, and explains how CISA BOD 26-04 and FedRAMP NTC-0014 affect vulnerability prioritization.

Oct 8, 2026
Security Insights · databreachtoday.com

How CMMC Contractors Can Prepare for NIST SP 800-171 Revision 3

NIST SP 800-171 Rev. 3 is not yet the CMMC Level 2 baseline. Contractors should maintain Rev. 2 readiness while mapping changes, including new requirement families, organization-defined parameters and updated assessment procedures.

Oct 8, 2026
Security Insights · sysdig.com

Why AI Agent Security Needs Runtime Controls Across the Stack

Sysdig argues that AI agents need runtime controls because prompt-based guardrails can be lost or bypassed. It outlines shared responsibilities and proposes using harness and kernel telemetry to assess actions before they complete.

Oct 8, 2026
Security Insights · cyberscoop.com

Congress Urged to Accelerate Preparation for Quantum Threats to Encryption

The article warns that future quantum computers could break current encryption and that stolen data may be decrypted later. It urges Congress to coordinate post-quantum cryptography upgrades across government and support protections for critical sectors.

Oct 8, 2026
Security Insights · crowdstrike.com

How Shared Signals Can Enable Near-Real-Time Zero Trust Access Decisions

The article explains how OpenID’s Shared Signals Framework and Continuous Access Evaluation Profile can propagate changes in account, device, and risk status so services can update access decisions without checking an identity provider on every request.

Oct 8, 2026
Security Insights · cofense.com

Cofense Outlines Five Ways to Measure Secure Behavior and Phishing Readiness

Cofense's webinar recap argues that training completion and simulation scores alone do not show phishing readiness. Its Secure Behavior Management approach combines competency measures, real-world phishing behavior, and remediation to guide improvements.

Oct 8, 2026
Security Insights · rapid7.com

Fragmented Campus Security Complicates Universities’ Compliance and Incident Response

An explainer on how fragmented, multi-campus IT can complicate universities’ security response and compliance with FERPA, GLBA, HIPAA and CMMC when regulated data is involved.

Oct 7, 2026
Security Insights · aws.amazon.com

AWS Security Professionals Share Unconventional Paths Into Cybersecurity

An AWS security communications professional profiles three people whose varied paths led to security roles, highlighting curiosity, persistence, OSINT work and hands-on learning resources.

Oct 7, 2026
PreviousPage 8 of 54 Next
© 2026 cyber.hendryadrian.com