cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · huntress.com

What Persistent Footholds Are and How Attackers Use Them

An explainer describes persistent footholds as mechanisms that re-trigger malware after interruptions, including Windows scheduled tasks and other autoruns, and explains how human threat hunters can identify malicious persistence without disrupting legitimate system or-
Apr 6, 2021
Security Insights · huntress.com

Huntress Shares Security Lessons from hack_it 2021

Huntress recaps its hack_it 2021 training event, including attacker-planning exercises, IT security lessons, and demonstrations of antivirus evasion. The sessions emphasized security awareness and defense in depth.

Mar 31, 2021
Security Insights · darkowl.com

How Fraud Operates Across the Darknet

An educational overview of darknet fraud explains traded financial and identity data, common fraud methods such as smishing and SIM swapping, and how criminals use stolen information to make purchases or move money.

Mar 4, 2021
Security Insights · huntress.com

Why Microsoft Defender Antivirus Deserves Another Look

The article argues that Microsoft Defender Antivirus can be a capable, low-cost endpoint layer, but is not a standalone solution. It highlights the lack of centralized management and visibility in the free offering.

Jan 19, 2021
Security Insights · huntress.com

Huntress Explains Its Public and Private Beta Approach

Huntress describes its beta process: private beta tests features for stability, while public beta offers opt-in access to stable features so the company can learn from customer use and feedback.

Dec 29, 2020
Security Insights · darkowl.com

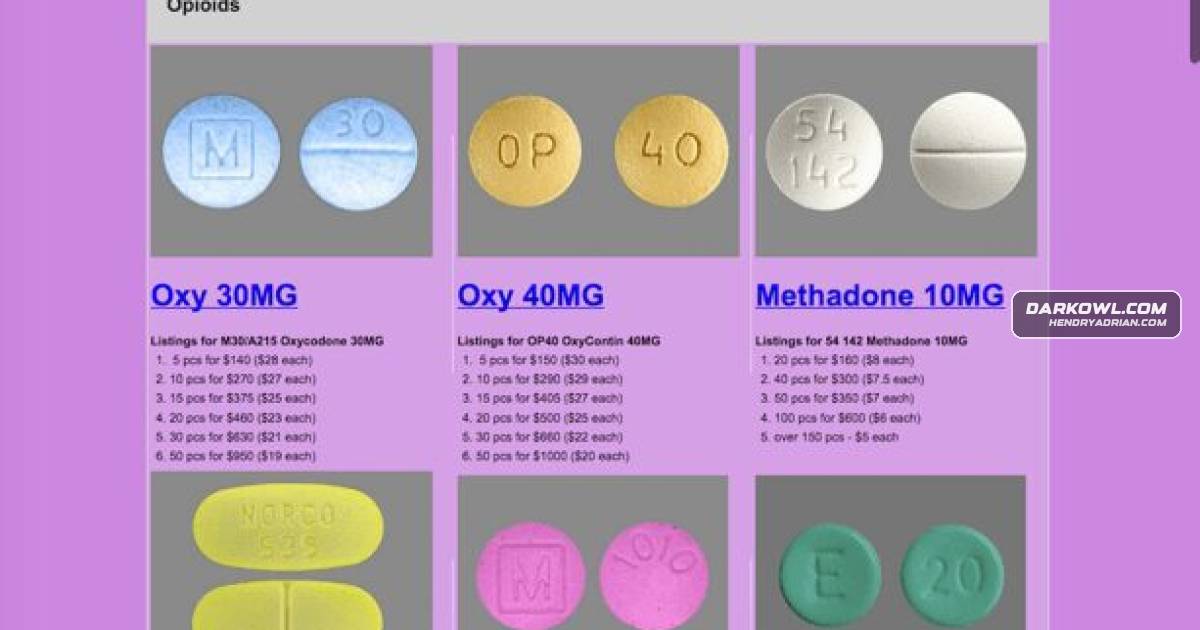
Darknet Markets Advertise Malware, Stolen Data and Other Tools for Cyber Operations

DarkOwl describes malware, credentials, personal data and other tools advertised on darknet markets, noting their potential use in cyber operations. The article also points to exposed SolarWinds credentials and earlier targeting claims.

Dec 24, 2020
Security Insights · huntress.com

Huntress Recaps Ransomware, Persistence and Evasion Tactics Seen in 2020

Huntress’s 2020 retrospective describes a shift toward high-value ransomware targets, data theft and double extortion, stealthier persistence, and changing defense-evasion techniques.

Dec 22, 2020
Security Insights · huntress.com

Cybersecurity Lessons from Huntress’ hack_it 2020 Event

Huntress recaps hack_it 2020, covering incident-response tabletop exercises, Cobalt Strike’s malleable command-and-control capabilities, and an introduction to security analysis and vulnerability research.

Oct 22, 2020
Security Insights · darkowl.com

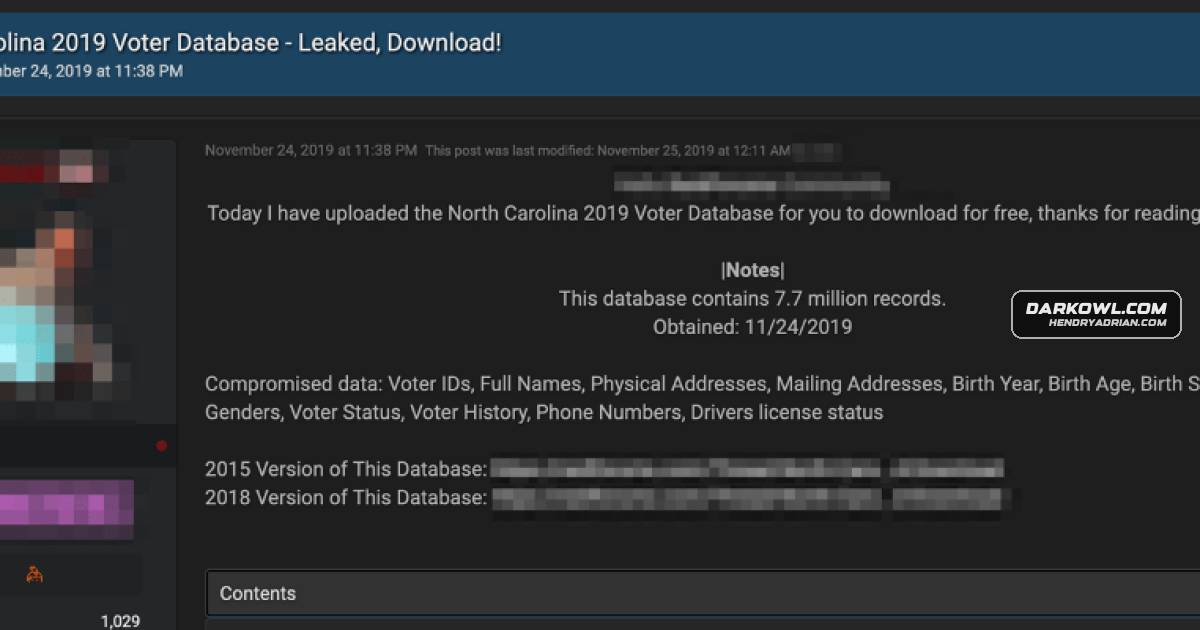
Voter Data Circulates on Darknet Forums, Raising Privacy and Targeting Concerns

DarkOwl reports voter databases shared on darknet forums and discusses how voter and donor information could be used for financial crime, intimidation, or targeted influence. It notes that some campaign-contribution data is public.

Oct 12, 2020
Security Insights · darkowl.com

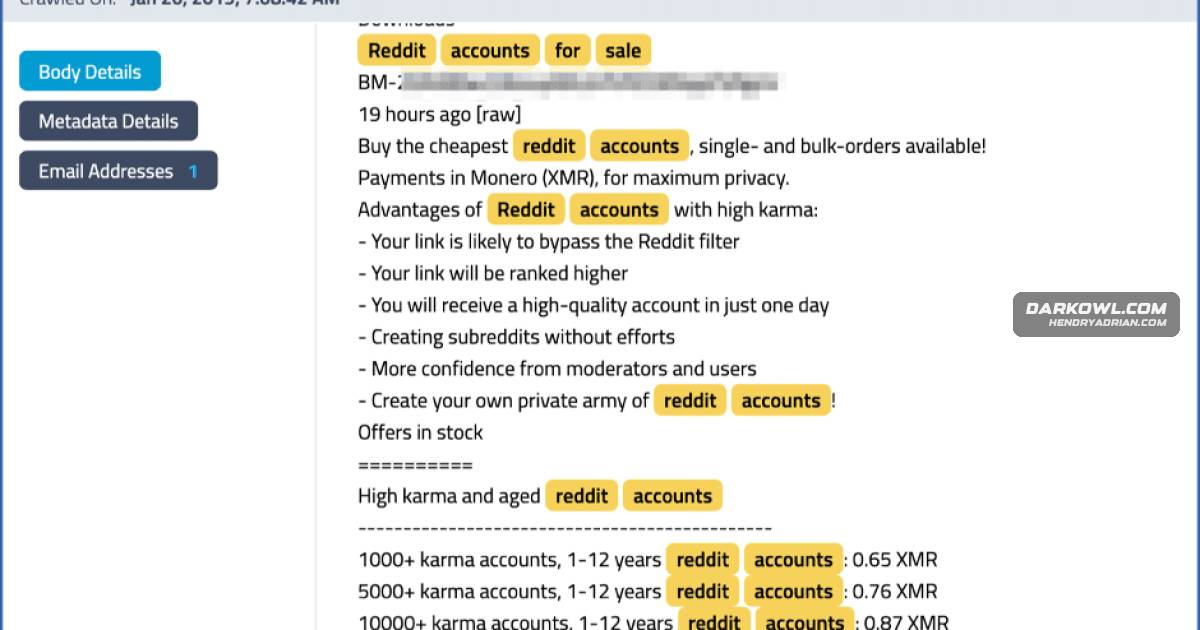
Darknet Vendors Sell Aged, Phone-Verified Social Media Accounts

DarkOwl analysts describe a market for aged and phone-verified social media accounts, credentials and engagement bots. These services can help buyers bypass security checks and support disinformation campaigns.

Sep 24, 2020
Security Insights · huntress.com

Underground Markets Make Office 365 Phishing and Credential Theft Easier to Buy

Huntress examines forum listings offering fake Office 365 login pages, phishing templates and bulk credentials, illustrating how underground services make phishing and business email compromise easier to outsource.

Sep 17, 2020
Security Insights · darkowl.com

Darknet Marketplace Amazin Market Advertises Stolen Accounts and Payment Card Data

DarkOwl’s snapshot describes Amazin Market’s listings for hacked accounts, gift card codes, payment card data and money-laundering services. It reports possible links to another market but says affiliation is unconfirmed.

Aug 21, 2020
Security Insights · darkowl.com

DarkOwl Snapshot Tracks Growth and Criminal Offerings on Infinity Market

DarkOwl reports a 76.92% rise in vendor registrations on Infinity Market since early May 2020, which offers stolen payment cards, botnet logs, and compromised food-delivery accounts. The article also describes its promotion and marketplace policies.

Jul 24, 2020
Security Insights · huntress.com

How Huntress Uses Ransomware Canaries to Detect Encryption

Huntress describes endpoint canary files that trigger alerts when changed, prompting investigation. Unique embedded QR codes may help trace canary files if they appear in exfiltrated data; the service detects ransomware but does not prevent it.

Jun 24, 2020
Security Insights · darkowl.com

DarkOwl Details Darknet Tactics Targeting Cloud Platforms

DarkOwl’s review of darknet discussions describes cloud-targeting tactics including phishing, credential stuffing, exposed API keys, SSRF, and Cloudflare bypass, alongside sales of cloud accounts and compromised access; forum claims are not independently verified.

Jun 10, 2020
Security Insights · darkowl.com

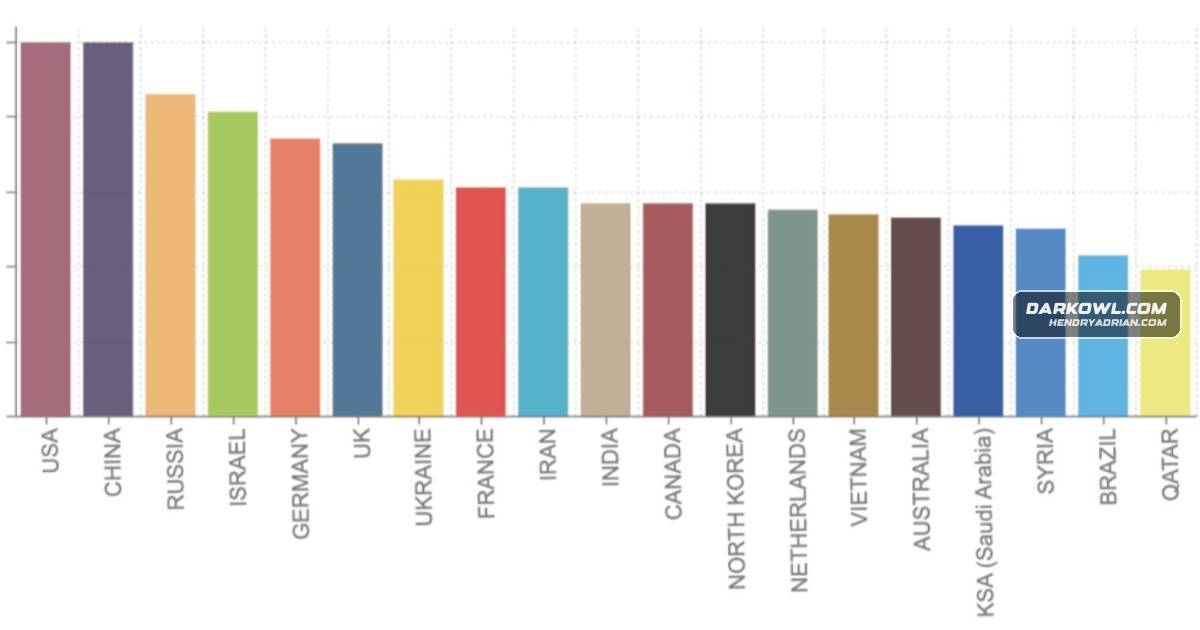
How Nation-State Actors Use the Dark Web for Espionage and Cyber Operations

DarkOwl examines how nation-state actors use the dark web for espionage, exploit acquisition, influence operations, and financial gain, and how leaked tools and proxy groups complicate attribution.

Jan 2, 2020
Security Insights · darkowl.com

Russian Darknet Marketplaces and Forums: RAMP, Hydra, MEGA and RuTor

The article surveys Russian darknet marketplaces and forums, describing vendor migration after RAMP’s closure, illicit goods and hacking software listings, and the communities’ marketplace and discussion features.

Jan 26, 2019
Security Insights · huntress.com

Testing Whether AUTOEXEC.BAT Can Still Enable Persistence on Windows

A Huntress experiment found no evidence that restoring the ParseAutoexec registry value makes Windows 7 or 10 parse AUTOEXEC.BAT. The author notes the test is not conclusive and points to registry-based persistence mechanisms still in use.

Dec 30, 2018
Security Insights · darkowl.com

Darknet Data Offers a View of Russian-Language Hacking Activity and Voter-Record Listings

DarkOwl surveys Russian-language darknet activity, citing hacking tools, credential listings and voter-record offers. It notes that many voter records are public and says there is no evidence the seller is linked to Russian government hackers.

Nov 5, 2018
Security Insights · darkowl.com

What Malware, Toolkits and Viruses Are—and How They’re Used

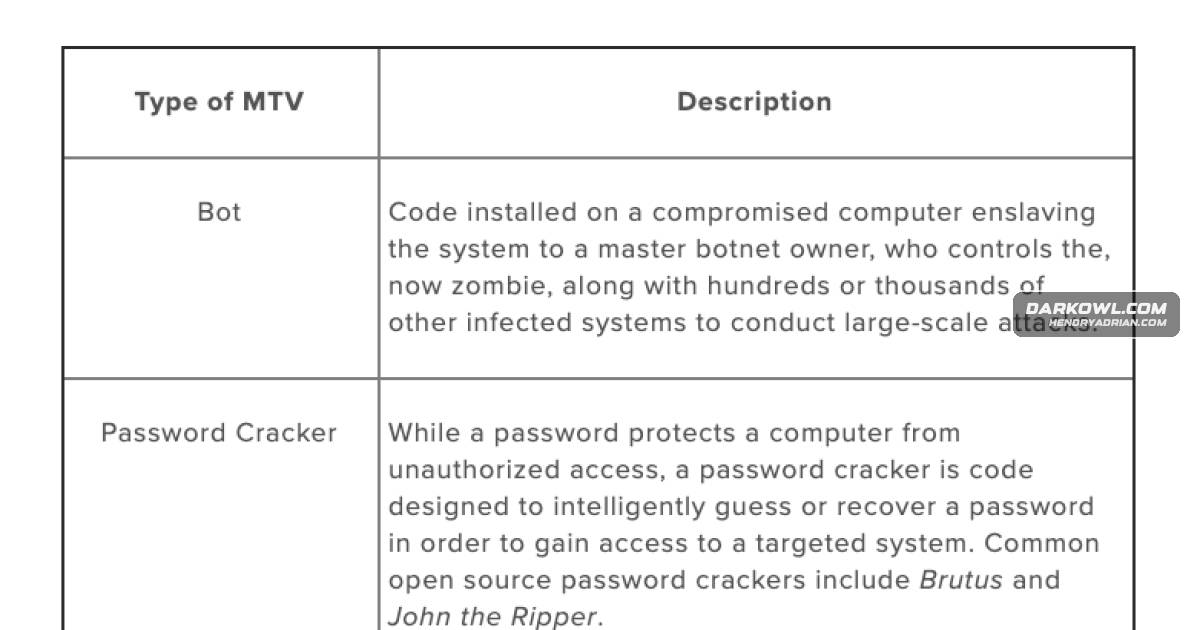
A high-level explainer introduces malware, toolkits and viruses, outlines their dual use in security testing and attacks, and summarizes malware’s history and role in gaining access to valuable data.

Oct 1, 2018
Security Insights · huntress.com

How Potentially Unwanted Programs Can Disrupt Users and Put Data at Risk

The article explains how adware, browser hijackers, and bundled software can disrupt users, redirect traffic, collect browsing data, or expose systems to more serious risks, and why response should reflect each program’s threat.

May 29, 2018
Security Insights · huntress.com

How Nested Execution Can Abuse a Trusted Windows Application

A walkthrough shows how Windows Server Essentials’ signed WseClientSvc.exe can load a .NET pass-through program that launches another executable, potentially making arbitrary execution appear to use a legitimate service.

Oct 2, 2017
Security Insights · huntress.com

Huntress Says Security Awareness Training Can Help Prevent Ransomware

The article argues that employee awareness training can help reduce ransomware risk, offering advice on suspicious emails and websites and outlining backup, payment, decryption, and reimaging options after an attack.

Jul 5, 2017
Security Insights · huntress.com

How to Troubleshoot Procmon v3.32 Driver Failures on 64-bit Windows 7

During a breach investigation, Procmon v3.32 could not load its driver on a 64-bit Windows 7 host. The team traced the certificate-validation problem to missing SHA-2 signing support and resolved it by installing KB3033929.

Apr 25, 2017
PreviousPage 54 of 54
© 2026 cyber.hendryadrian.com