cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · huntress.com

Huntress Urges Organizations to Build a More Open Cybersecurity Culture

Huntress argues that fear of embarrassment or punishment can discourage people from reporting cyber incidents, and recommends open communication, shared experiences, and engaging security awareness training.
Mar 14, 2022
Security Insights · huntress.com

How Cyber Insurance Requirements Shape SMB Security

The article explains how cyber insurers use security attestations to assess SMBs, why requirements such as EDR and RMM use can be unclear, and how CIS Controls and the NIST Cybersecurity Framework can guide security improvements.

Feb 9, 2022
Security Insights · wiz.io

Why Endpoint Security Agents Alone Fall Short in Cloud Environments

The article outlines coverage gaps, deployment burdens, vulnerabilities, supply-chain risks and attacker evasion associated with endpoint agents, and argues that agentless tools can complement them in cloud environments.

Feb 3, 2022
Security Insights · huntress.com

What Is Managed Detection and Response (MDR)?

MDR combines security technology with a managed team that hunts for threats that bypass preventive tools, investigates suspicious activity, and helps organizations respond.

Feb 1, 2022
Security Insights · huntress.com

Huntress Founders Share Cybersecurity Predictions for 2022

Huntress founders’ tongue-in-cheek 2022 predictions call for clearer security offerings, endpoint-focused protection for remote work, risk-based auto-updates and more mature SMB security operations.

Jan 18, 2022
Security Insights · wiz.io

Wiz Proposes a Shared Cloud Vulnerability Response Model

Wiz argues that cloud providers and customers need clearer shared responsibilities, with security benchmarks, threat-model change logs and a cloud vulnerability database to improve transparency and remediation.

Jan 5, 2022
Security Insights · huntress.com

Huntress Reviews 2021 Cybersecurity Trends and Lessons

Huntress reviews 2021 trends including ransomware, exposed servers, supply-chain attacks, LOLBins, incomplete remediation and alert fatigue, and shares defensive lessons such as isolating backups, enabling MFA and planning incident response.

Jan 5, 2022
Security Insights · huntress.com

Security Awareness Training Should Motivate Employees, Not Scare Them

The article argues that fear-based security training can discourage employee engagement and recommends positive, interactive learning and incentives to build security awareness and a stronger security culture.

Dec 14, 2021
Security Insights · huntress.com

How SIM Swapping Can Bypass SMS-Based Two-Factor Authentication

The article explains how SIM swapping can let attackers intercept SMS authentication codes, and recommends enabling 2FA, avoiding SMS-only authentication when possible, and educating users about MFA.

Nov 30, 2021
Security Insights · wiz.io

Wiz Calls for a Standardized Cloud Vulnerability Database, Later Launches Open CVDB

Wiz argues that cloud vulnerabilities lack consistent identifiers, notifications and remediation tracking, using AWS, OMIGOD and ChaosDB as examples. The company later says it launched the community-driven Open CVDB in June 2022.

Nov 12, 2021
Security Insights · huntress.com

Huntress Recaps Cybersecurity Lessons from hack_it 2021.2

Huntress recaps its hack_it 2021.2 training event, covering a cybercrime investigation exercise, dark-web markets, and macro-enabled phishing. Key lessons include tabletop exercises, the value of data to criminals, and how phishing campaigns pressure recipients.

Nov 2, 2021
Security Insights · huntress.com

Four Cybersecurity Awareness Tips for Year-Round Security

Huntress shares four cybersecurity awareness tips: prepare to detect and respond to threats, verify suspicious emails and links, maintain basic security practices such as patching and MFA, and look for weaknesses from an attacker’s perspective.

Oct 5, 2021
Security Insights · huntress.com

Huntress Announces hack_it 2021.2 Cybersecurity Training Event

Huntress previews its free hack_it 2021.2 event, featuring interactive sessions on threat actor tradecraft, compromised organizations, phishing, and macro-enabled malware, plus a paid Windows attack-response workshop.

Sep 29, 2021
Security Insights · huntress.com

How Hacker Tradecraft Has Evolved Toward Organized Crime and Persistence

A Huntress explainer traces changes in hacker tradecraft, from early malware and reactive defenses to organized, financially motivated groups using phishing and persistence to maintain covert access.

Aug 11, 2021
Security Insights · huntress.com

Cybersecurity Costs: Breach Risks, Security Spending, and Layered Defenses

The article explains factors that drive breach costs and argues that businesses—especially SMBs—should invest in layered security tools and human expertise rather than rely on a single product or respond only after an incident.

Aug 5, 2021
Security Insights · huntress.com

Lessons from the Kaseya VSA Supply-Chain Ransomware Attack

Huntress reviews the 2021 REvil attack through Kaseya VSA, describing its impact on MSPs and customers, key attack steps, the decryption key’s arrival, and lessons on vendor security and incident preparedness.

Jul 28, 2021
Security Insights · huntress.com

How MDR Teams Hunt for Malware on Endpoints

The article explains how managed detection and response analysts investigate endpoint persistence, including reviewing autoruns and suspicious file paths, and describes a manufacturing customer's malware incident and remediation process.

Jul 26, 2021
Security Insights · huntress.com

Experts Explain Email-Based Threats and Ways to Defend Against Them

Security experts discuss how email enables phishing and ransomware delivery, including attachment and link evasion tactics, social engineering, and defenses such as automated scanning, employee training, and reporting suspicious messages.

Jul 14, 2021
Security Insights · huntress.com

Three Steps MSPs Can Take to Reduce Cyber Risk and Liability

The article advises MSPs to maintain current asset inventories, define security responsibilities in customer contracts, and prepare incident response plans to reduce cyber risk and limit damage.

Jun 22, 2021
Security Insights · huntress.com

Raccine Uses Windows IFEO Debuggers to Disrupt Ransomware Activity

Huntress analysts found Raccine, an open-source utility that uses Windows IFEO debuggers and YARA rules to block ransomware-related commands. It can be deployed through Group Policy, but may also block legitimate activity.

Jun 8, 2021
Security Insights · huntress.com

Endpoint Protection Tools Add Layers, but None Provides Complete Security

The article compares AV, NGAV and EDR, arguing each has limitations and that organizations should assess risk, layer controls and ensure experts can act on EDR telemetry. It also promotes Huntress threat hunting for persistence.

Jun 1, 2021
Security Insights · huntress.com

A Cyber Insurance Perspective on Ransomware and Its Business Impact

A Huntress interview discusses ransomware’s business and insurance costs, changing ransom severity, and how basic security practices—such as training, closing RDP, and reviewing access—may help reduce risk.

May 25, 2021
Security Insights · darkowl.com

DarkOwl Finds More Than Two Dozen Active Darknet Imageboards

DarkOwl says it identified more than two dozen active darknet imageboards beyond 4chan and 8kun, spanning several languages. The article explains their communities, anonymity model, and relevance to investigations.

May 19, 2021
Security Insights · darkowl.com

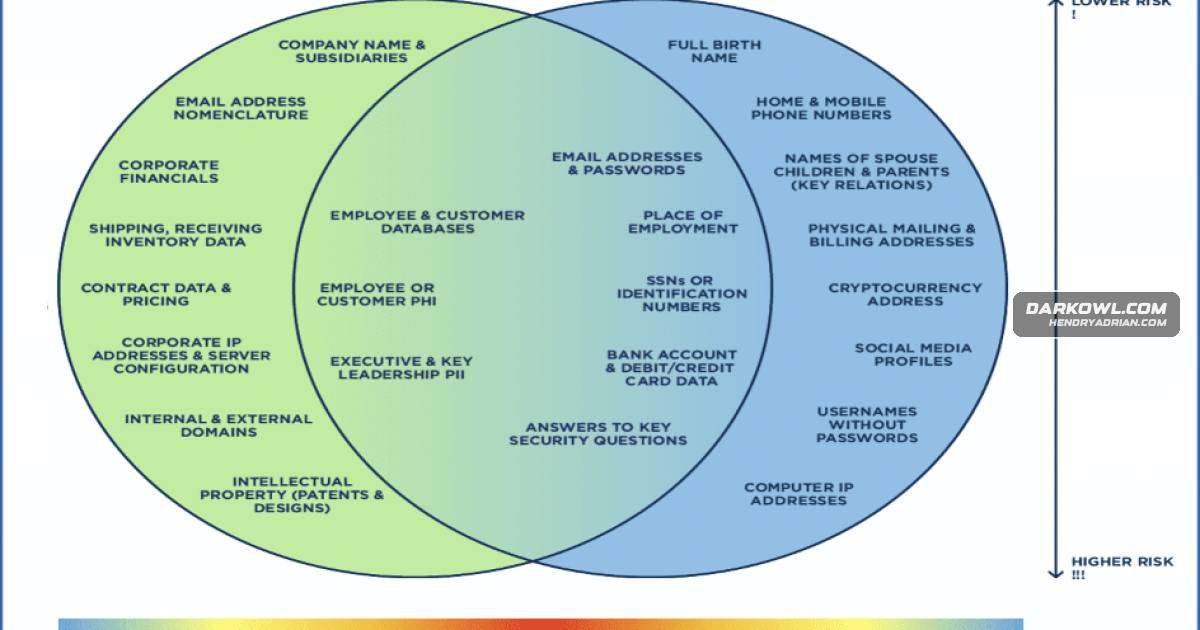
How Darknet Exposure Shapes Cyber Risk for Individuals and Organizations

The article explains how darknet exposure can raise cyber risk for individuals and organizations, covering ransomware extortion, phishing, credential stuffing and third-party exposure, along with risk factors and basic mitigations.

Apr 29, 2021
PreviousPage 53 of 54 Next
© 2026 cyber.hendryadrian.com