cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · wiz.io

Four Steps to Build a Customer-Centric Security Program

Semgrep’s Clint Gibler recommends making security a service for developers: provide self-service resources with security built in, embed staff across teams, make secure choices easy, and build capabilities that benefit the wider organization.
Mar 6, 2023
Security Insights · wiz.io

Experts Highlight API Attacks, Cloud Ransomware and Cryptomining Risks

Cloud security experts identify API attacks, ransomware and cryptomining as key risks, and discuss safeguards including strong authorization, behavioral analytics and regular staff training.

Mar 3, 2023
Security Insights · huntress.com

How EDR Collects Endpoint Telemetry and Adds Context Beyond Antivirus

The article explains how EDR collects endpoint telemetry over time to add context beyond antivirus alerts, and outlines the data and response capabilities Huntress says its managed EDR provides.

Feb 23, 2023
Security Insights · huntress.com

A Guide to macOS’s Built-In Security and Malware-Removal Tools

The guide explains how macOS tools—TCC, File Quarantine, Gatekeeper, XProtect, MRT and XProtect Remediator—control access, check downloaded apps, block malware and remediate threats, while discussing their limits and when businesses may need additional coverage.

Feb 21, 2023
Security Insights · darkowl.com

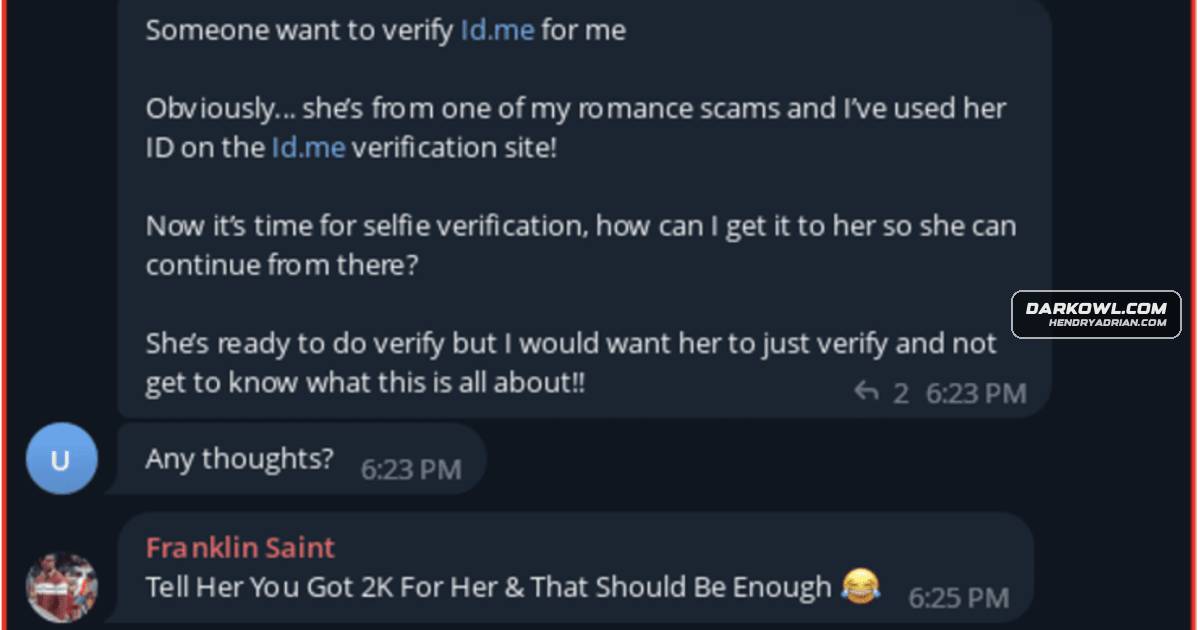
Darknet Forums Offer Romance Scam Tools, Guides and Advice

DarkOwl analysts describe how romance scams intersect with identity theft, money laundering and exploitation, and report finding scam scripts, eWhoring guides and victim discussions on darknet and adjacent platforms.

Feb 14, 2023
Security Insights · wiz.io

Security Leaders Urged to Prioritize Fundamentals Amid Budget Pressure

Security leaders discuss managing budget constraints through clear communication with executives, risk-based investment, tool consolidation, and prioritizing fundamentals such as misconfiguration fixes, vulnerability management, MFA, and network segmentation.

Feb 13, 2023
Security Insights · wiz.io

Getting Started with OPA and Rego for Cloud Security Policies

A tutorial introduces Open Policy Agent and Rego, then explains a sample policy that checks whether AWS security-group egress rules allow unrestricted access to the public internet.

Feb 2, 2023
Security Insights · darkowl.com

Darknet Networks Enable a Range of Retail Fraud and Phishing Schemes

DarkOwl describes retail fraud methods observed in underground networks, including refund schemes, POS malware, counterfeit goods, phishing sites, stolen gift cards and tactics targeting retailers and consumers.

Jan 25, 2023
Security Insights · wiz.io

How Kubernetes User Namespaces Can Reduce Container Escape Risks—and Their Limitations

Kubernetes v1.25’s alpha user namespaces can limit container-escape impact through UID remapping and safer privilege use, but kernel attack surface and workload compatibility limitations mean operators should assess fit and block unshare(CLONE_NEWUSER) with seccomp.

Jan 23, 2023
Security Insights · darkowl.com

Darknet Discussions Highlight Risks to API Security

DarkOwl describes darknet discussions and sales involving API tokens, keys, and exploitation tools, and relates them to incidents involving USPS, GitHub, Toyota, and FTX users.

Jan 12, 2023
Security Insights · huntress.com

How Malware Persists on macOS: Launch Items and Other Startup Mechanisms

Huntress explains macOS persistence mechanisms, including Launch Daemons and Agents, login hooks, cron and periodic scripts. Its agent currently monitors Launch Items, which can be used by both legitimate software and malware.

Jan 10, 2023
Security Insights · wiz.io

CISOs’ 2023 Priorities: Invest in Teams, Data and Cloud Security

CISOs interviewed by Wiz recommend strengthening collaboration and staff capabilities, protecting cloud data, investing in security data and measured innovation, and prioritizing value from existing tools.

Jan 9, 2023
Security Insights · wiz.io

How AWS Organizations Delegated Administration Can Help Security Teams

AWS delegated administration lets organizations grant member accounts limited visibility into accounts and policies or control specific SCPs. The article covers security use cases, example configurations, and risks such as self-lockout and uneven protection.

Dec 15, 2022
Security Insights · wiz.io

Wiz Introduces PEACH Framework for Assessing Cloud Tenant Isolation

Wiz presents PEACH, a framework for evaluating tenant isolation in cloud applications, with five hardening factors and remediation guidance. A ChaosDB case study illustrates how isolation gaps contributed to the Azure Cosmos DB vulnerability.

Dec 14, 2022
Security Insights · wiz.io

Five Security-Focused Talks from AWS re:Invent 2022

A roundup of five AWS re:Invent talks covers Netflix’s multi-account architecture and SDK instrumentation, zero-privilege service design, AWS’s Log4Shell response, and cloud security posture management.

Dec 9, 2022
Security Insights · wiz.io

CISOs Urged to Strengthen Incident Communication and Preparation After Uber Verdict

Following the Uber CISO conviction, security leaders share recommendations on transparency, executive coordination, incident-response planning, legal support, and organizational ethics.

Dec 8, 2022
Security Insights · darkowl.com

How Credential Stuffing Uses Combolists to Take Over Accounts

The article explains how criminals use leaked credentials, wordlists, automated checking tools, and proxies for credential stuffing, and discusses account trading and why MFA does not guarantee protection.

Dec 1, 2022
Security Insights · darkowl.com

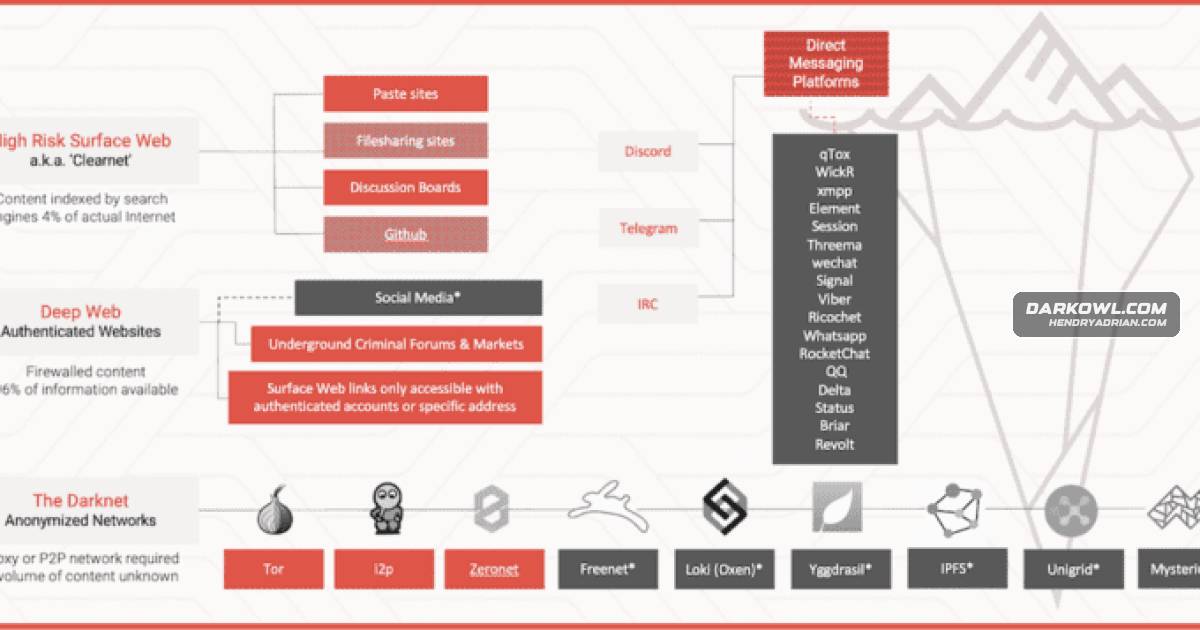
Explainer: How the Surface Web, Deep Web and Darknet Differ

An explainer distinguishes the surface web, deep web and darknet, describing how Tor, I2P, ZeroNet, Freenet, Lokinet and Yggdrasil work and why darknet terminology matters to OSINT investigators.

Nov 29, 2022
Security Insights · huntress.com

Huntress hack_it 2022 Recap Covers DLL Hijacking and Hacker Tradecraft

Huntress recaps hack_it 2022 sessions on cybercrime, AI claims in security, DLL hijacking techniques, using Process Monitor, and a live exercise involving vulnerability discovery and privilege escalation.

Nov 17, 2022
Security Insights · huntress.com

Security Hygiene Basics for MSPs: Onboarding, Automation and MFA

A Huntress article outlines cybersecurity hygiene practices for MSPs and clients, emphasizing documented onboarding, automated monitoring and alerts, security ownership, and deploying MFA.

Nov 15, 2022
Security Insights · darkowl.com

Webinar Explores How Darknet Data Can Inform API Security

DarkOwl and Corsha speakers discuss API credential risks, darknet trading and discussion of keys and exploits, and security practices including least privilege, credential rotation, revocation, and monitoring.

Nov 10, 2022
Security Insights · darkowl.com

Webinar Explores OSINT Methods for Investigating Darknet Marketplaces

A webinar transcript outlines how investigators can correlate marketplace aliases, posts, PGP keys, cryptocurrency wallets, and other online accounts to investigate vendors and illicit trade, while noting that such links are not always certain.

Nov 8, 2022
Security Insights · huntress.com

Cybersecurity Basics for SMBs: Advice for MSPs on Tools and Incident Response

A Huntress conversation with Syncro discusses cybersecurity basics for SMBs and MSPs, recommending a NIST-based approach to security tools, alert monitoring, and incident-response planning.

Oct 25, 2022
Security Insights · wiz.io

10 Security-Focused Sessions to Watch at KubeCon + CloudNativeCon North America 2022

A curated guide to KubeCon + CloudNativeCon North America 2022 sessions on Kubernetes security, cloud attack paths, policy migration, software supply chains, and integrating security testing into CI/CD.

Oct 21, 2022
PreviousPage 51 of 54 Next
© 2026 cyber.hendryadrian.com