
How Credential Stuffing Uses Combolists to Take Over Accounts
Summary
The article explains how criminals use leaked credentials, wordlists, automated checking tools, and proxies for credential stuffing, and discusses account trading and why MFA does not guarantee protection.
Key points
- Credential stuffing automatically tests exposed username-password combinations against websites to attempt account takeovers.
- Leaked credential collections and generated wordlists supply combinations for automated checking.
- The article names tools including OpenBullet and SentryMBA, and describes proxy use to make login attempts appear to come from different IP addresses.
- Criminal forums and chat channels trade validated logins and large combolists, including accounts advertised as having full access.
- MFA can reduce risk but may be bypassed through further phishing or social engineering, or techniques such as SIM swapping, according to the article.
- The article notes that exposed email accounts and personal information can support targeted efforts to obtain details needed to bypass account protections.
Article Details
- Topic
- Credential stuffing, combolist cracking, and the darknet ecosystem of credential validation tools and services
MITRE ATT&CK
Tools
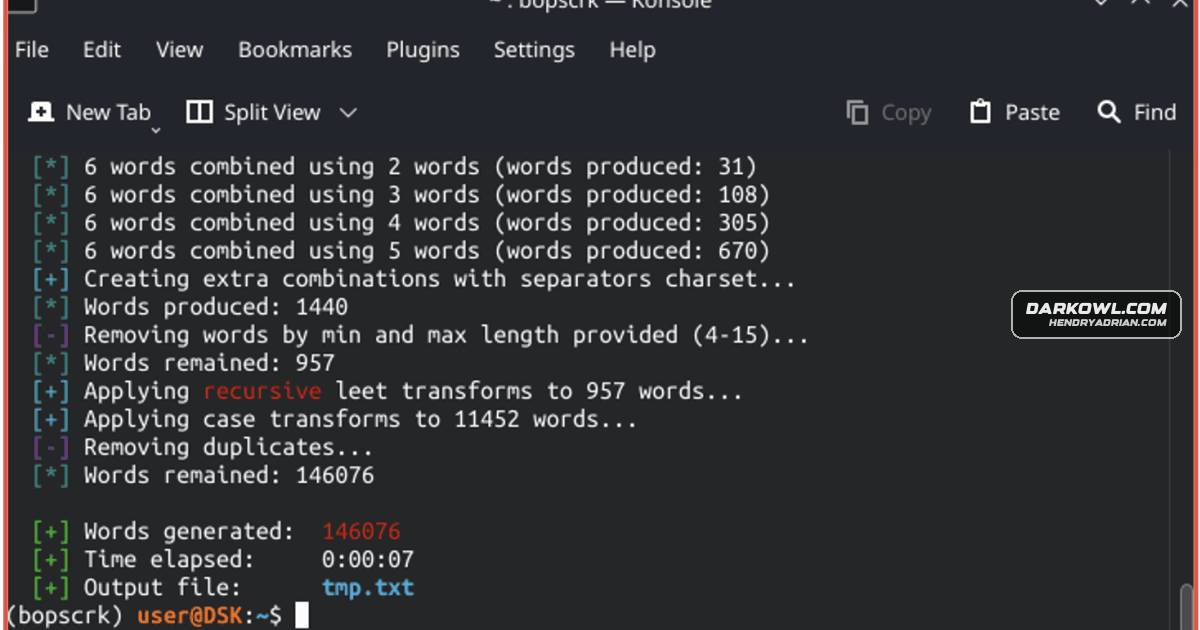
ApexOlder programs like Vertex and Apex work similarly to Sentry, but struggle to authenticate with more enhanced SSL or HTTPS secured websites.AzLiquidGoldPrograms such as AzLiquidGold, SlayerLeecher, BlackBullet, STORM and Snipr were designed by hackers with the pure intent as proxy-enabled scrapers and “combo-checkers.” Residential proxies are available for purchase forBEWGorhave observed mentions of CeWL and Pydictor on forums popular with Chinese threat actors and others like BEWGor (yes, pronounced “booger”), Crunch, and the Common User Passwords Profiler (CUPP) across other deep webBlackBulletPrograms such as AzLiquidGold, SlayerLeecher, BlackBullet, STORM and Snipr were designed by hackers with the pure intent as proxy-enabled scrapers and “combo-checkers.” Residential proxies are available for purchase forBopscrkAnother user on Telegram enthusiastically referred other channel members to a repository containing Bopscrk, advertised as a “smart and powerful” wordlist generator that combines wordlist data and personal informationBurp SuiteThere are also tools readily available like Burp Suite that support OTP-bypass attacks installed in Kali Linux.CeWLDarkOwl analysts have observed mentions of CeWL and Pydictor on forums popular with Chinese threat actors and others like BEWGor (yes, pronounced “booger”), Crunch, and the Common User Passwords Profiler (CUPP) acrossCommon User Passwords Profiler (CUPP)Chinese threat actors and others like BEWGor (yes, pronounced “booger”), Crunch, and the Common User Passwords Profiler (CUPP) across other deep web communities.CrunchPydictor on forums popular with Chinese threat actors and others like BEWGor (yes, pronounced “booger”), Crunch, and the Common User Passwords Profiler (CUPP) across other deep web communities.OpenBulletOften cybercriminals will reuse web application testing programs like OpenBullet or SentryMBA that were originally designed for good but are now coveted and circulated by cybercriminals for optimizing crime.PydictorDarkOwl analysts have observed mentions of CeWL and Pydictor on forums popular with Chinese threat actors and others like BEWGor (yes, pronounced “booger”), Crunch, and the Common User Passwords Profiler (CUPP) acrossSentryMBAOften cybercriminals will reuse web application testing programs like OpenBullet or SentryMBA that were originally designed for good but are now coveted and circulated by cybercriminals for optimizing crime.SlayerLeecherPrograms such as AzLiquidGold, SlayerLeecher, BlackBullet, STORM and Snipr were designed by hackers with the pure intent as proxy-enabled scrapers and “combo-checkers.” Residential proxies are available for purchase forSniprPrograms such as AzLiquidGold, SlayerLeecher, BlackBullet, STORM and Snipr were designed by hackers with the pure intent as proxy-enabled scrapers and “combo-checkers.” Residential proxies are available for purchase forSTORMPrograms such as AzLiquidGold, SlayerLeecher, BlackBullet, STORM and Snipr were designed by hackers with the pure intent as proxy-enabled scrapers and “combo-checkers.” Residential proxies are available for purchase forVertexOlder programs like Vertex and Apex work similarly to Sentry, but struggle to authenticate with more enhanced SSL or HTTPS secured websites.