cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · huntress.com

Identity Security Is Becoming a Third Pillar of Security Operations

The article argues that cloud adoption has made identity a distinct security-operations concern, citing Storm-0558, BEC and an Azure advisory, and urges organizations to improve visibility into third-party identity platforms.
Aug 10, 2023
Security Insights · huntress.com

What MSPs Should Know About Cyber Insurance and Security Requirements

A webinar-series recap explains how MSPs can guide clients on cyber insurance, security requirements, policy coverage, and claims, highlighting controls such as 24/7 EDR, MFA, vulnerability management, and security awareness training.

Jul 25, 2023
Security Insights · darkowl.com

How Social Media and Darknet Data Can Support Cyber Investigations

A webinar transcript explains how investigators can combine social-media and darknet data to assess threats, connect online identities, and spot phishing and disinformation risks. It includes a case example and discusses ethical challenges.

Jul 18, 2023
Security Insights · wiz.io

AWS Access Key Alternatives: Comparing OIDC, IAM Roles Anywhere, and Systems Manager Hybrid Activation

The article compares OIDC, IAM Roles Anywhere, and Systems Manager hybrid activation as alternatives to long-lived AWS access keys, outlining security trade-offs and possible improvements such as hardware-backed signing.

Jul 17, 2023
Security Insights · darkowl.com

Darknet Intelligence Analyst Explains How Investigators Use Darknet Data

A DarkOwl analyst describes darknet platforms and criminal activity, and explains how investigators can connect usernames, cryptocurrency wallets and other OSINT to examine cybercrime.

Jul 12, 2023
Security Insights · huntress.com

Huntress Says MOVEit Victim Disclosures May Reflect Delayed Cl0p Follow-Up

Huntress observed no significant MOVEit exploitation after late May 2023; later victim disclosures may reflect delayed cl0p follow-up to earlier compromises. It urges defenders to retain telemetry, monitor data flows and hunt for lingering access.

Jul 7, 2023
Security Insights · wiz.io

How Linux Rootkits Abuse LD_PRELOAD to Hide Malicious Activity

A tutorial explains how Linux rootkits use LD_PRELOAD to intercept functions and hide activity, demonstrates hiding a file by hooking readdir, and outlines methods to detect preload abuse.

Jul 5, 2023
Security Insights · wiz.io

How to Isolate Tenants in Generative AI Cloud Applications

The article applies the PEACH tenant-isolation framework to GenAI cloud apps, explaining cross-tenant risks and how interface complexity, data access, customization and architecture choices should shape isolation.

Jun 28, 2023
Security Insights · huntress.com

How macOS XProtect and XProtect Remediator Detect and Remove Malware

An explainer of macOS XProtect and XProtect Remediator describes their malware-blocking and remediation roles, logging, and limitations. The author says they may suit individual users but lack the visibility and coverage needed at scale.

Jun 28, 2023
Security Insights · darkowl.com

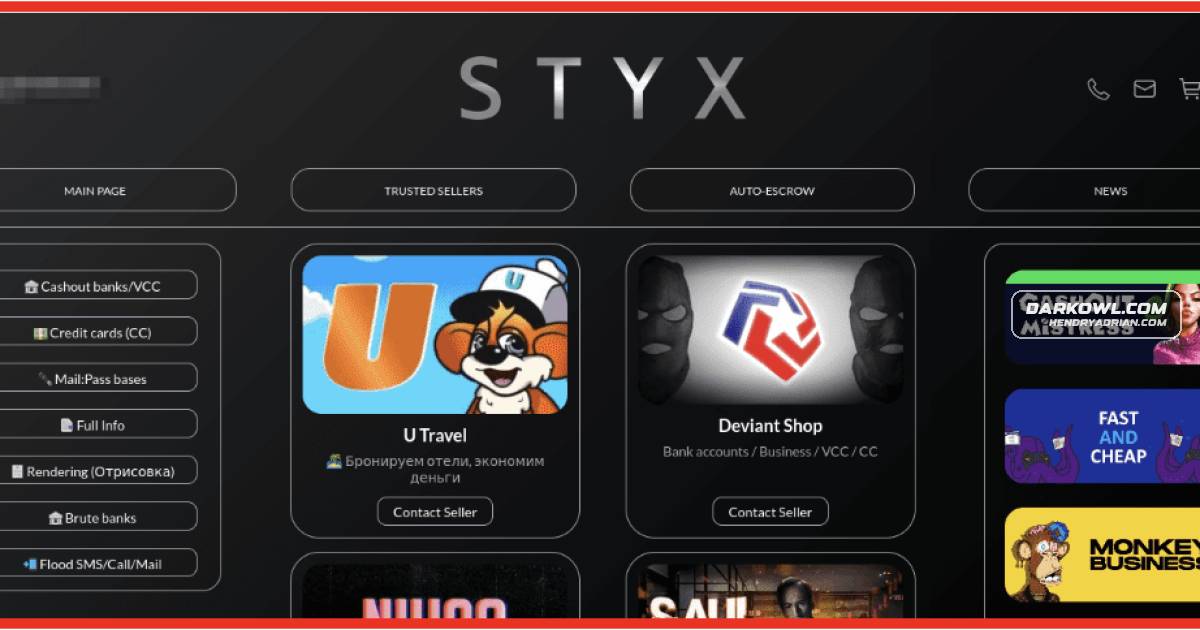
Styx Market Offers Stolen Data and Services for Financial Crime, DarkOwl Finds

DarkOwl researchers examined Styx Market, documenting listings for stolen data, account access, fraud and money-laundering services, plus vendors’ use of Telegram. They describe the marketplace as geared toward experienced cybercriminals.

Jun 21, 2023
Security Insights · wiz.io

CISOs Share Advice on Leadership, Career Choices, and Building Security Teams

Security leaders offer advice for CISOs on communicating security priorities to executives, evaluating a prospective role, and building diverse teams with varied skills and perspectives.

Jun 9, 2023
Security Insights · darkowl.com

How Dark-Web Intelligence Helps Organizations Identify Cyber Risks

A podcast discussion explains how organizations use darknet intelligence to find exposed credentials, assess threats and prioritize response, while emphasizing context, human judgment and layered security.

Jun 7, 2023
Security Insights · huntress.com

How Splunk Universal Forwarder Can Be Abused for Persistence and Remote Code Execution

A proof of concept shows how a custom Splunk app can make Universal Forwarder periodically fetch and execute PowerShell commands from a web page. The author says this abuses supported functionality, not a Splunk vulnerability.

Jun 6, 2023
Security Insights · darkowl.com

DarkOwl Examines Leak Sites Selling Stolen Data Outside Ransomware Groups

DarkOwl describes smaller leak-focused sites and Telegram channels selling leaked data, accounts and stealer logs, often outside ransomware groups. Analysts say the trend may reflect more decentralized trading; they could not verify data advertised on Unsafe.

May 23, 2023
Security Insights · huntress.com

MDM vs. RMM: Managing macOS Devices and Permissions

An overview of macOS MDM and RMM, comparing software deployment, device visibility, remote access, and costs. MDM can deploy PPPC profiles to manage TCC permissions, while RMM generally requires endpoint approval for permissions.

May 23, 2023
Security Insights · wiz.io

KubeCon Europe 2023 Highlights Practical Kubernetes Security Talks

A curated guide to KubeCon Europe 2023 talks on Kubernetes security, covering secrets, pod security migration, least-privilege containers, network policies, Zero Trust threat modeling, and managed-cluster risks.

May 11, 2023
Security Insights · darkowl.com

How Scams Differ From Fraud—and Where Phishing Fits

The article explains how scams and fraud differ, using examples such as phishing, account takeover and identity theft, and offers factors to consider when classifying financially motivated crimes.

May 9, 2023
Security Insights · huntress.com

Using CyberChef to Decode an Obfuscated AsyncRAT Loader

Huntress analysts show how they used CyberChef and regex to decode an obfuscated VBS script found persisting via a scheduled task, revealing a chain that led to an AsyncRAT loader.

May 9, 2023
Security Insights · huntress.com

How macOS Endpoint Security Gives Security Tools Visibility Into System Activity

An overview of macOS Endpoint Security explains its event monitoring and blocking capabilities, user approvals and permissions, and how event data can help security teams investigate activity and build detections.

Apr 25, 2023
Security Insights · blog.talosintelligence.com

How Attackers Use AI and Other Tools to Improve Phishing

Phishing is becoming more targeted across email, social media, SMS and phone calls. Attackers use evasion techniques and AI-generated lures, while user education, MFA, secure email gateways and DNS security can help reduce risk.

Apr 13, 2023
Security Insights · wiz.io

Gartner Outlines CNAPP Capabilities for Prioritizing Cloud Security Risk

The article summarizes Gartner’s view that integrated CNAPPs can help organizations prioritize cloud security risks, and highlights capabilities and evaluation guidance for enterprises considering them.

Apr 11, 2023
Security Insights · wiz.io

CISOs Share Lessons for Building Security Programs at Hypergrowth Companies

Security leaders discuss how fast-growing companies can prioritize security, partner with business teams, distribute accountability, and set measurable goals while balancing security with growth.

Mar 29, 2023
Security Insights · darkowl.com

How Credentials and Secrets Are Traded on the Darknet

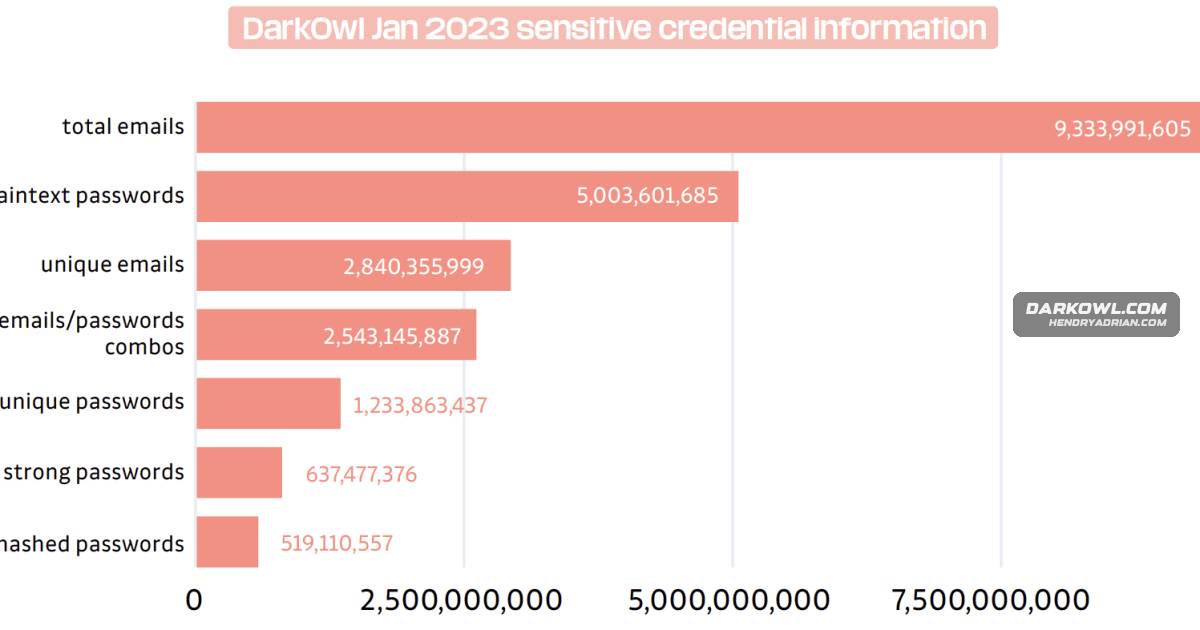
DarkOwl describes how credentials, tokens and keys are shared or sold on darknet forums, and how attackers may use them for account abuse or to gain access to corporate networks.

Mar 28, 2023
Security Insights · huntress.com

How macOS Security Prompts Affect Users and Software Deployment

An explainer on macOS notifications and security prompts, including how Ventura surfaces launch items, TCC and other permissions, and why these prompts complicate software deployment without MDM-managed PPPC profiles.

Mar 21, 2023
PreviousPage 50 of 54 Next
© 2026 cyber.hendryadrian.com