cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · darktrace.com

Darktrace Outlines Five Levels of AI Maturity for Cybersecurity Teams

Darktrace introduces a five-level framework for assessing AI use in cybersecurity, from manual operations to AI delegation. It applies across security functions and emphasizes measured outcomes, human oversight, and progressively greater autonomy.
Jul 16, 2025
Security Insights · darkowl.com

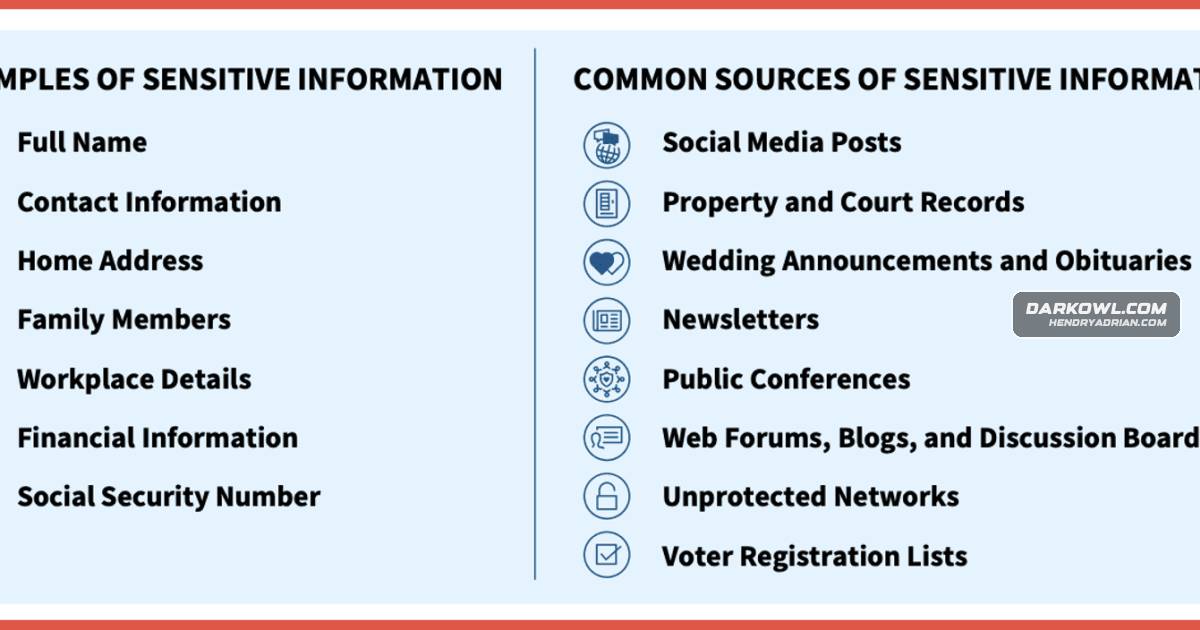
What Data Harvesting Is, How It Can Be Abused, and How to Protect Yourself

An explainer describes data-harvesting methods and legitimate and criminal uses, including credential theft and doxing, then outlines DarkOwl’s collection practices and basic steps to limit personal-data exposure.

Jul 8, 2025
Security Insights · team-cymru.com

Using Cyber Threat Intelligence to Proactively Monitor Supply Chain Risk

The article recommends shifting supplier risk management from post-breach questionnaires and underground monitoring toward proactive CTI, using passive asset discovery and NetFlow to identify exposed services, unpatched vulnerabilities and suspicious supplier-network

Jul 8, 2025
Security Insights · team-cymru.com

Team Cymru: SharePoint ToolShell Exploitation Preceded Public PoC by Three Days

Team Cymru says it observed live SharePoint ToolShell exploitation on July 18, 2025, three days before the first GitHub PoC. Its analysis argues exploitation often starts within hours of public PoC release and recommends faster patching.

Jul 8, 2025
Security Insights · hunt.io

Splunk Threat Research Lead on Threat Hunting, Detection Engineering and Living-Off-the-Land Risks

Splunk’s Jose Hernandez discusses detection engineering, threat hunting, infrastructure analysis, and efforts to help defenders address attackers’ abuse of legitimate tools.

Jul 8, 2025
Security Insights · darktrace.com

Eight Common SaaS Security Threats, from Account Takeover to Business Email Compromise

An overview of eight threats to SaaS applications and user identities—including account takeover, OAuth token abuse, insider threats, API attacks, and BEC—and the limitations of traditional defenses.

Jul 3, 2025
Security Insights · huntress.com

AI’s Cybersecurity Benefits and Risks: A Tradecraft Tuesday Recap

A Huntress webinar recap surveys how generative AI is used in social engineering and malware, as well as threat analysis and security operations, and explains why human review remains essential.

Jun 30, 2025
Security Insights · deepinstinct.com

Deep Instinct argues organizations should scan MSP updates for malware

Using a reported MSP compromise involving DragonForce ransomware as an example, Deep Instinct argues organizations should scan software and updates from trusted partners before they reach client environments.

Jun 26, 2025
Security Insights · hunt.io

How to Use URLx Queries to Hunt for Malicious URLs and Exposed Assets

A tutorial demonstrates using Hunt.io’s URLx dataset and HuntSQL queries to find potential malware payloads, phishing infrastructure, exposed sensitive files, and misconfigured assets, then enrich results with ProjectDiscovery’s httpx.

Jun 26, 2025
Security Insights · huntress.com

Practical Ways to Build and Retain a Strong Cybersecurity Team

A cybersecurity leader shares practical approaches to hiring for creativity and communication, supporting employees’ growth, recognizing their impact, and preventing burnout through boundaries and regular time off.

Jun 20, 2025
Security Insights · darkowl.com

How Crypto, Dark-Web Markets and Mixers Are Used to Launder Money

An explainer outlines how dark-web proceeds, crypto conversion services, NFTs and mixers can support money laundering, while public blockchains can help investigators trace funds. It also reviews Tornado Cash and related enforcement actions.

Jun 17, 2025
Security Insights · hunt.io

TrustedSec CTO Justin Elze on Red Teaming, Open Directories, and Offensive Security

TrustedSec CTO Justin Elze discusses red-team skills, common information leaks, open-directory hunting, security tools, AI’s role in offensive work, and how his hands-on background shapes technology leadership.

Jun 17, 2025
Security Insights · wiz.io

Wiz Fine-Tunes a Small Language Model to Detect Secrets in Code

Wiz describes fine-tuning Llama 3.2 1B for code secret detection. The model achieved 82% recall and 85.7% precision in the reported evaluation, and the company says it is in private preview.

Jun 10, 2025
Security Insights · darkowl.com

How Digital Whistleblower Platforms Use Tor and Encryption to Protect Sources

An overview of whistleblower platforms including SecureDrop, GlobaLeaks, and WildLeaks, describing how Tor, encryption, and secure submission channels can help protect sources and support anonymous reporting.

Jun 4, 2025
Security Insights · huntress.com

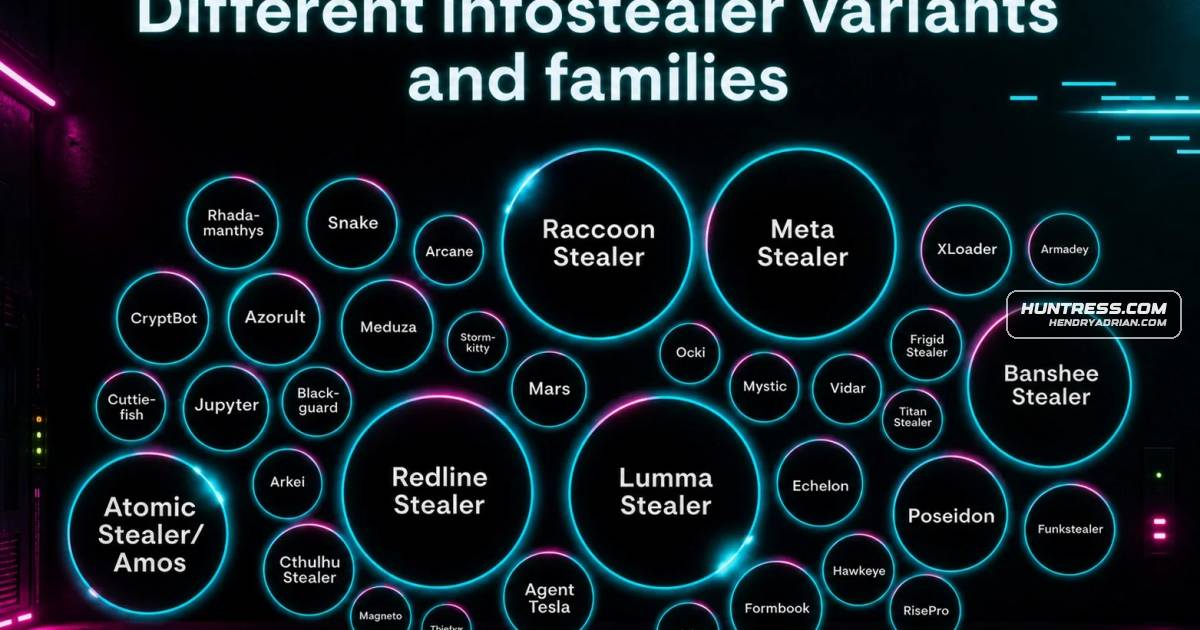
Infostealer Crash Course: How They Steal Data and Enable Further Attacks

A Huntress Tradecraft Tuesday recap explains infostealer evolution, the credentials and data they target, marketplace activity, macOS variants, recent takedowns, a detected Lumma incident, and ways businesses can reduce risk.

Jun 3, 2025
Security Insights · hunt.io

How IOC Pivoting Can Reveal Links Across Threat Actor Infrastructure

Hunt.io demonstrates how analysts can pivot from threat actor profiles and IOCs to connected infrastructure, using host details, DNS, SSH keys, network signals, and historical activity to investigate possible campaign links.

May 29, 2025
Security Insights · darktrace.com

How to Compare Email Security Solutions Using A/B Testing

A structured A/B comparison can help organizations evaluate email security solutions fairly by using equal deployment conditions, aligned configurations, consistent threat metrics, and broader criteria such as support and integrations.

May 21, 2025
Security Insights · huntress.com

Ransomware Attacks: Common Stages, Timelines and Prevention Tips

Huntress outlines ransomware attack stages and reports attackers took an average of 18 steps before deployment. It recommends early prevention, security awareness training and managed security tools.

May 15, 2025
Security Insights · darkowl.com

What Is Doxing? Risks, Consequences and Ways to Protect Yourself

Doxing is the nonconsensual public release of personal information, which can enable harassment, identity theft, stalking and threats. The article explains common impacts and recommends practical steps to limit exposure.

May 13, 2025
Security Insights · wiz.io

Wiz Introduces Cloud Incident Response CTF Challenge

Wiz introduces The ExfilCola Incident, a cloud security CTF where participants investigate a fictional data-extortion threat, trace attacker access, and determine whether a secret recipe is safe.

May 6, 2025
Security Insights · cloudsek.com

Fintech Security Scan Finds Exposed Tomcat Errors, WordPress XML-RPC Methods and SPF Misconfiguration

CloudSEK’s scan of a fintech firm’s public-facing assets found exposed Tomcat stack traces, WordPress XML-RPC methods and a misconfigured SPF record, which could aid reconnaissance and email spoofing. The article recommends limiting disclosures and unused features.

May 2, 2025
Security Insights · huntress.com

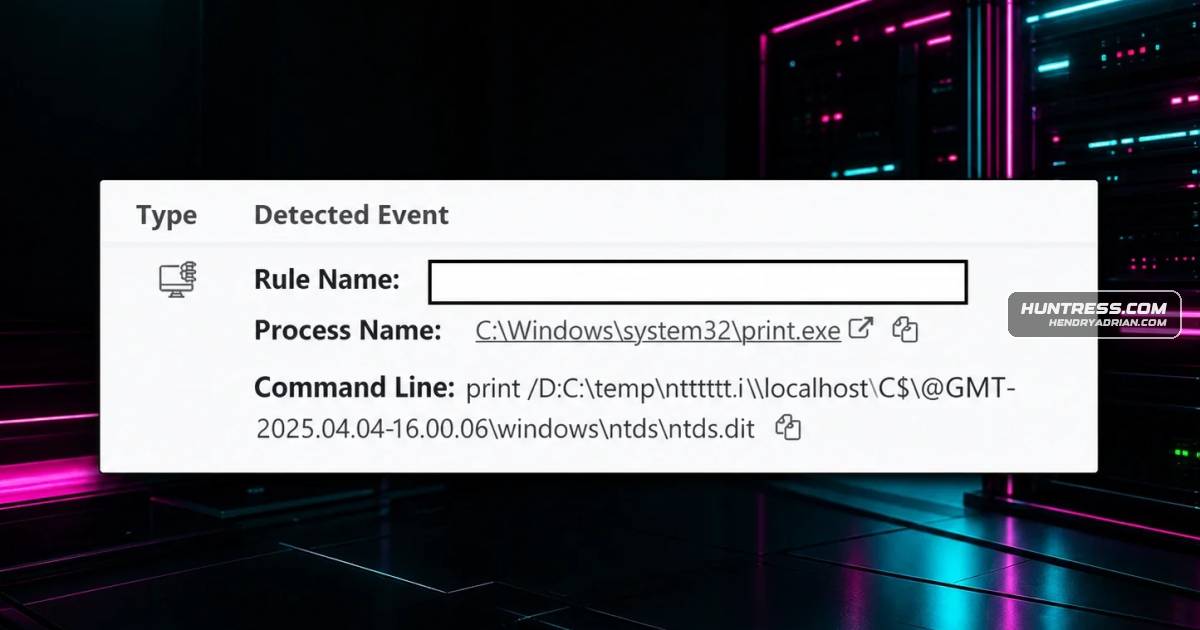
Attackers Used Windows print.exe to Copy Active Directory Credential Files from Shadow Copies

Huntress analysts observed an actor using Windows print.exe to copy NTDS.DIT, SAM, and SYSTEM files from Volume Shadow Copies. Huntress says its 24-hour telemetry search found no other print.exe credential-theft instances.

Apr 24, 2025
Security Insights · huntress.com

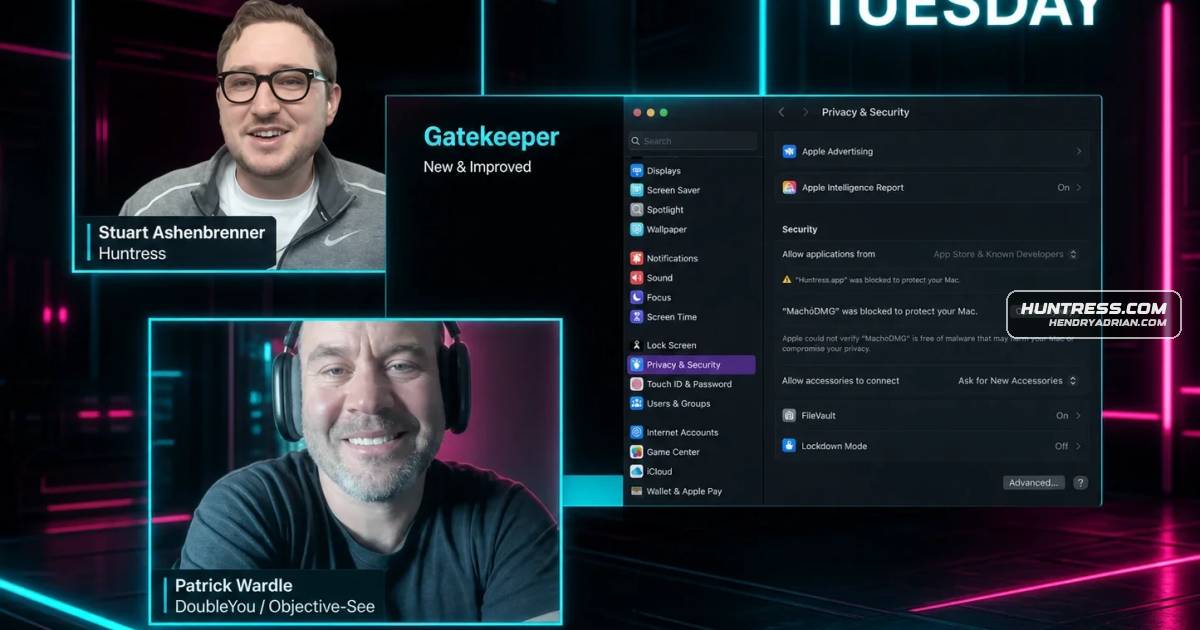
How Mac Malware Adapts to Apple’s Built-In Security Protections

A Huntress episode recap explains how macOS malware adapts to persistence controls, TCC permissions and Gatekeeper, and notes new TCC event visibility in macOS 15.4.

Apr 22, 2025
Security Insights · darktrace.com

How NDR and SASE Complement Each Other to Strengthen Network Security

The article explains how NDR and SASE provide complementary network defenses, and describes Darktrace 6.3 integrations with Zscaler and Netskope for faster response and visibility into tunneled traffic.

Apr 22, 2025
PreviousPage 43 of 54 Next
© 2026 cyber.hendryadrian.com