
Attackers Used Windows print.exe to Copy Active Directory Credential Files from Shadow Copies
Summary
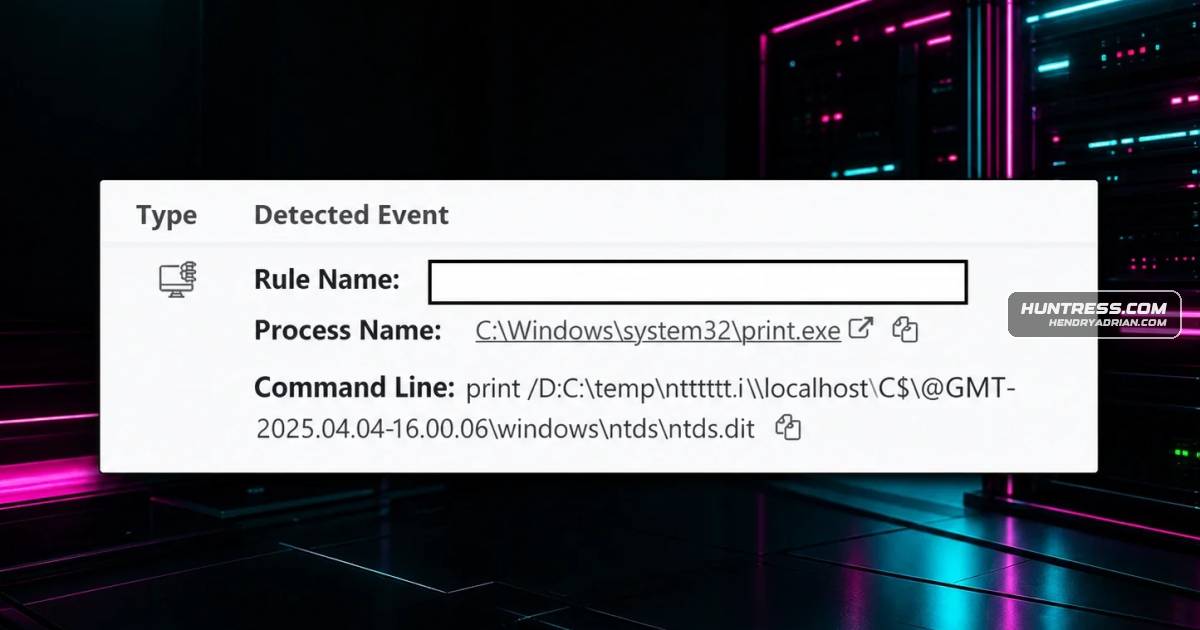
Huntress analysts observed an actor using Windows print.exe to copy NTDS.DIT, SAM, and SYSTEM files from Volume Shadow Copies. Huntress says its 24-hour telemetry search found no other print.exe credential-theft instances.
Key points
- In a customer incident, analysts observed print.exe copying NTDS.DIT, the Active Directory credential file, from a Volume Shadow Copy.
- On another server in the same environment, print.exe commands copied the SAM and SYSTEM files from a shadow copy.
- The article says the method avoids some Windows Event Log artifacts associated with attaching, copying, and detaching the database.
- Before the copying, the actor ran NetTime.exe and vssuirun.exe, which Huntress says were used to determine server time and available shadow copies.
- A search of the previous 24 hours of EDR telemetry found over 16,000 print.exe uses, which appeared legitimate; a search for credential-theft use found none.
Article Details
- Topic
- Credential theft by copying Active Directory and SAM credential files from Volume Shadow Copies using the Windows print.exe utility.