
How Huntress Uses Managed SIEM to Speed Threat Detection and Investigations
Summary
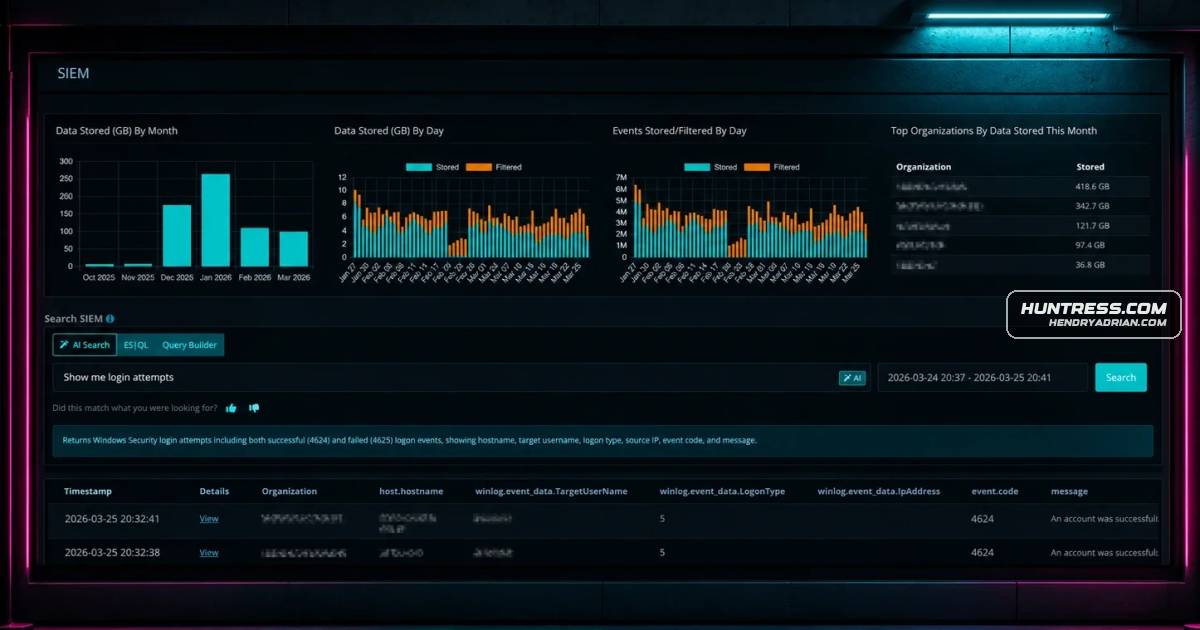
Huntress describes how its teams use Managed SIEM to investigate incidents, correlate logs, and detect threats. In one case, EDR stopped a malware infection and SIEM logs helped confirm no data was exfiltrated.
Key points
- Huntress teams use feedback from frontline defenders to shape and evaluate Managed SIEM features.
- COUNT and COUNT DISTINCT in ES|QL help analysts summarize log data to find anomalies, trends, and unusual behavior.
- In one incident, Managed EDR stopped a malware infection; firewall and endpoint logs in SIEM helped confirm no data had been exfiltrated.
- Huntress says its correlation rules connect signals across time, systems, and log sources to detect activity such as brute force attempts, reconnaissance, and lateral movement.
- The article describes SIEM working alongside EDR and ITDR to provide visibility across endpoints, identities, and infrastructure.
Article Details
- Topic
- How Huntress uses Managed SIEM and cross-team incident review to improve threat detection, investigation speed, and response.
Vendors
Products
Managed Identity Threat Detection and Response (ITDR)And when combined with Managed EDR and Managed Identity Threat Detection and Response (ITDR), Managed SIEM becomes part of a tightly integrated defense, delivering comprehensive visibility across endpoints, identities,Managed SIEMHomeBlogHow Huntress Uses Managed SIEM to Detect Faster and Hunt Smarter