cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · bleepingcomputer.com

Agentic AI Creates Identity Risks That Organizations Need to Govern

A sponsored Token Security article argues that autonomous AI agents can accumulate poorly governed identities and excessive access, increasing the risk of unauthorized actions. It recommends distinct agent identities, scoped access, ownership, lifecycle controls and rev
Jun 29, 2026
Security Insights · huntress.com

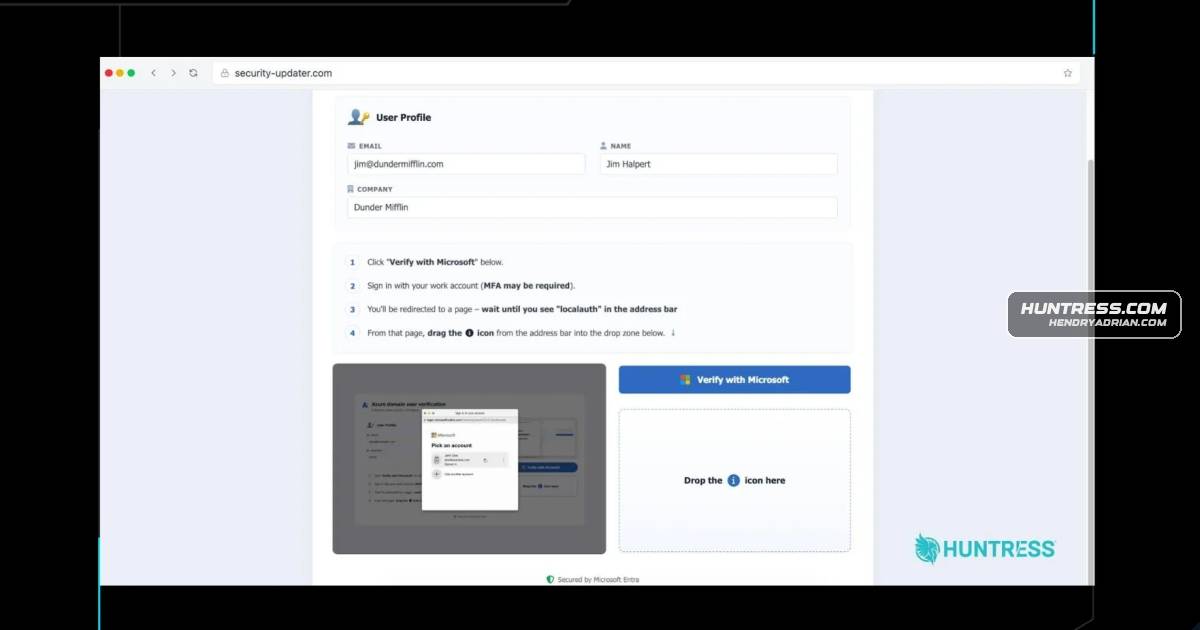
ConsentFix Uses Familiar Microsoft 365 Sign-In Steps to Steal Session Tokens

ConsentFix tricks Microsoft 365 users into dragging a localhost callback link into a browser, exposing OAuth tokens that can let attackers access email, OneDrive, Teams, and other resources without a password.

Jun 29, 2026
Security Insights · team-cymru.com

How AI Is Making Cybercrime More Efficient, Not Reinventing It

Trend AI researcher Robert McArdle says criminals adapt existing business models rather than reinventing them. AI is accelerating malware development, while agentic systems could scale fraud and make infrastructure disruption central to defense.

Jun 29, 2026
Security Insights · decodedsecurity.com

Decoded Security Marks Its First Year with Cybersecurity Courses and Study Resources

Decoded Security marks its first year with 1,304 subscribers and highlights its cybersecurity quizzes, study plans, guides, practical labs, and community, while outlining plans for more certification and career-focused learning materials.

Jun 28, 2026
Security Insights · toxsec.com

AI Agent Incident Response Needs Decision-Path Tracing

The article argues that action-only AI-agent logs leave responders unable to reconstruct decisions and context. It cites reported PocketOS, Amazon Kiro and Meta incidents and says EU AI Act Article 12 will require logging for high-risk systems from Aug. 2, 2026.

Jun 27, 2026
Security Insights · bleepingcomputer.com

A Red Teamer’s Guide to Building a GRC Agent

A sponsored walkthrough explains how GRC agents can monitor controls continuously, compare live MFA enforcement with a defined baseline, log their actions, use limited permissions, and route consequential decisions for human approval.

Jun 26, 2026
Security Insights · huntress.com

Average Data Breach Costs Reach $4.4 Million Globally, Varying by Industry and Location

An educational overview of data-breach costs says the global average is $4.4 million, with costs shaped by industry, location, attack method, and response speed. It outlines common breach causes and risk-reduction measures.

Jun 26, 2026
Security Insights · malwarebytes.com

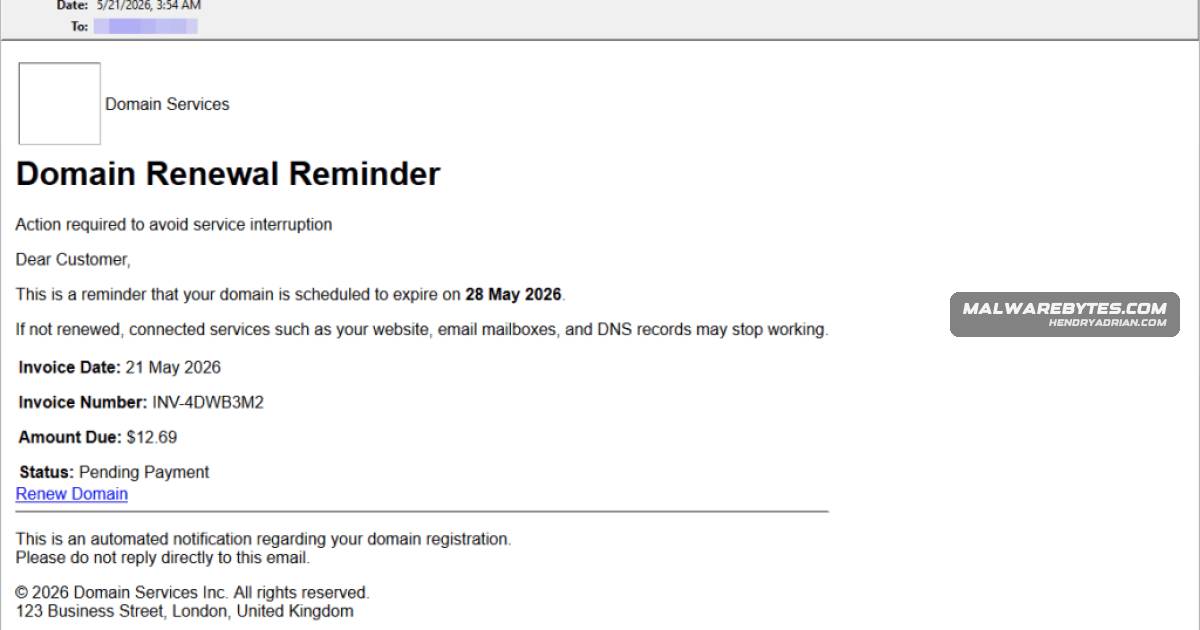
Fake Domain Renewal Scam Uses Renovarix Branding to Harvest Personal Data and Solicit Payment Details

A Renovarix-branded phishing scam uses public WHOIS/RDAP data, fake expiry warnings and countdowns to funnel domain owners through redirect sites that request personal and payment details. Verify renewals directly with your registrar.

Jun 25, 2026
Security Insights · cyberscoop.com

Opinion: Check Point VPN Exploitation Highlights Limits of Patching Alone

The article says attackers exploited CVE-2026-50751 in Check Point Remote Access VPN before disclosure, arguing that patching should be paired with investigation and endpoint defenses because attackers may already have access.

Jun 25, 2026
Security Insights · blog.talosintelligence.com

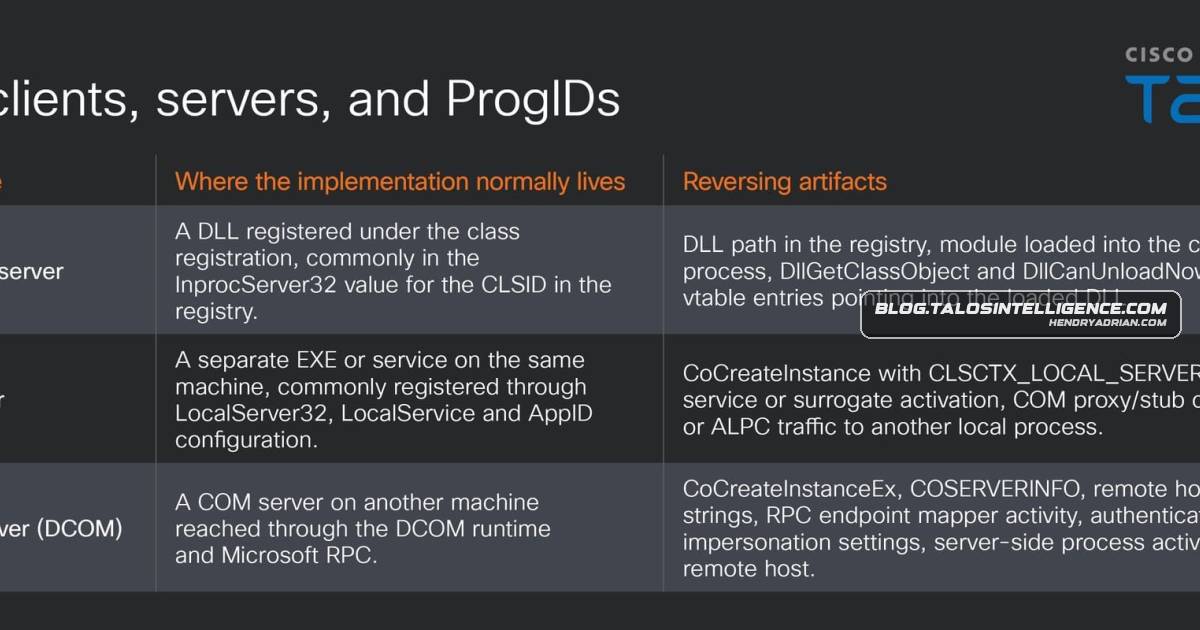
How Windows Malware Uses COM—and How Analysts Can Analyze It

Talos explains how Windows malware uses COM for functions such as persistence, execution, and data transfer, and shows how analysts can identify COM classes, interfaces, and methods in binaries.

Jun 25, 2026
Security Insights · thehackernews.com

Identity Security Must Focus on Privilege and Trusted Access, Article Argues

The article argues that enterprises should treat identity as core infrastructure, reduce standing privilege, and govern human and machine identities to limit the impact of attackers using trusted access.

Jun 25, 2026
Security Insights · huntress.com

36 Common Cyberattacks: How They Work and How to Reduce Risk

A cybersecurity guide explains 36 attack types, including malware, phishing, network attacks, and vulnerability exploitation, and recommends measures such as MFA, patching, employee training, and backups.

Jun 25, 2026
Security Insights · huntress.com

27 Major Data Breaches Reveal Common Security Failures and Lessons for Defenders

A review of 27 major data incidents highlights recurring causes—including exposed databases, weak passwords, unpatched flaws, and compromised credentials—and recommends defenses such as MFA, encryption, patching, and security awareness training.

Jun 25, 2026
Security Insights · huntress.com

How MSPs Can Identify Clients Handling DoD Controlled Unclassified Information

The guide advises MSPs to review public contract records and company indicators, then ask about DFARS clauses, DoD-marked technical data, and PIEE access to identify clients with potential CUI compliance needs.

Jun 25, 2026
Security Insights · recordedfuture.com

How Recorded Future’s Insikt Group Combines Analyst Expertise and Automation for Threat Intelligence

Recorded Future describes how Insikt Group analysts combine specialist knowledge, multilingual expertise, and automated network and multi-source analysis to identify threats, validate intelligence, and support customer and public research.

Jun 25, 2026
Security Insights · darktrace.com

Shadow AI Can Expose Enterprise Data Beyond Security Teams’ View

Employees’ use of unsanctioned AI tools can expose enterprise data beyond security teams’ visibility. The article explains why traditional controls may miss AI activity and discusses visibility, governance, and behavioral monitoring as ways to manage the risk.

Jun 25, 2026
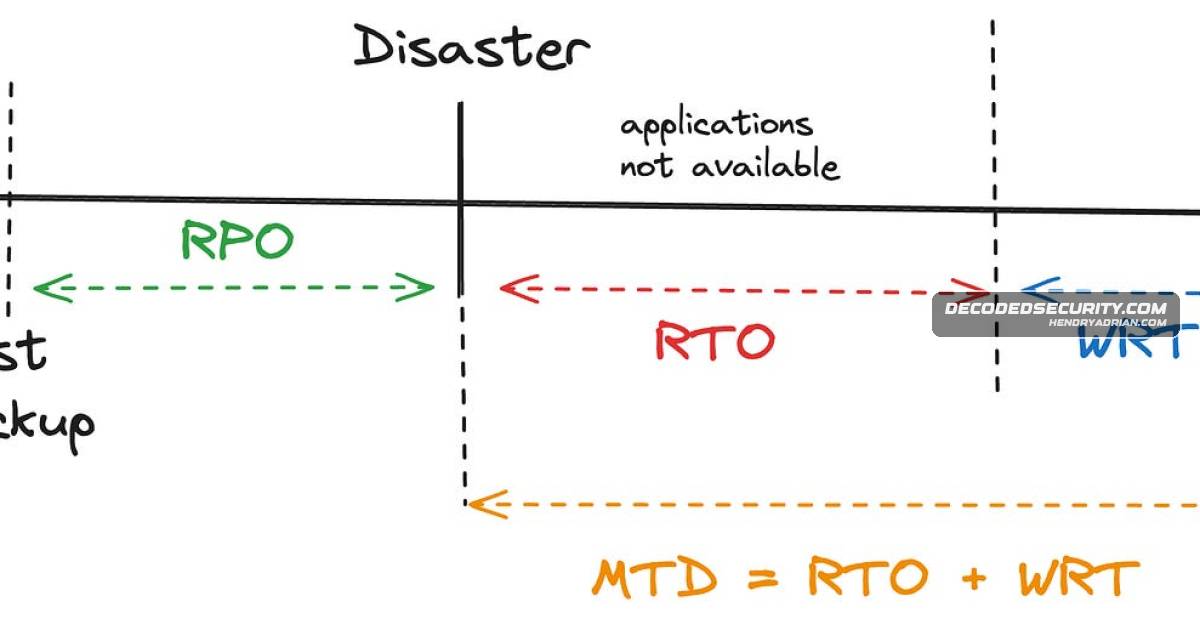
Security Insights · decodedsecurity.com

How MTD, RTO, WRT, and RPO Guide Backup Strategy

The article explains how Business Impact Analysis informs MTD, RTO, WRT, and RPO, helping organizations set recovery and data-loss targets before choosing backup methods.

Jun 24, 2026
Security Insights · securityweek.com

AI Agent Traps: How Malicious Information Can Manipulate Decisions and Actions

The article explains six ways malicious information can influence AI agents, from hidden instructions to poisoned memory, and recommends source verification, restricted permissions, monitoring and human approval for high-impact actions.

Jun 24, 2026
Security Insights · wiz.io

AI Is Reshaping Security Operations Around Continuous Context

AI can accelerate both software development and attacks, shrinking defenders’ response window. The article argues that security teams need continuous environment context, visibility across AI, workload, and cloud activity, and AI-assisted investigations.

Jun 24, 2026
Security Insights · securityweek.com

Why Agentic AI Can Make Bad Security Decisions Without the Right Context

The article examines how incomplete or stale context can lead agentic AI to make harmful security decisions, especially in SOC alert triage, and contrasts autonomous action with human-reviewed recommendations that explain their reasoning.

Jun 24, 2026
Security Insights · darktrace.com

Why Enterprise AI Prompt Security Requires Behavioral Context

Prompt language can reveal misuse or data risk, but is ambiguous on its own. The article argues that security teams should interpret prompts alongside identity, behavior, connected systems, relationships, and subsequent actions.

Jun 24, 2026
Security Insights · cybersecuritypulse.net

Why Security Hygiene Is Becoming a Strategic Priority for CISOs

A veteran CISO argues that faster vulnerability discovery and breaches through trusted integrations make recurring work—such as reviewing identities, OAuth access, secrets and third-party tools—a strategic security priority.

Jun 23, 2026
Security Insights · securityweek.com

Deep Instinct’s CISO-CIO on Combining Security and IT Leadership and AI Risks

Deep Instinct CISO and CIO Carl Froggett says combining the roles can work at smaller organizations but risks losing impartiality. He also warns that generative AI may enable more convincing cyberattacks and lower barriers for attackers.

Jun 23, 2026
Security Insights · darkowl.com

Ransomware Negotiation Tactics and Lessons From Three Real-World Cases

The article outlines steps for organizations considering ransomware negotiations, including assembling response specialists, investigating potential data theft, managing communications, and documenting exchanges. It cautions that payment offers no guarantee of recovery.

Jun 23, 2026
PreviousPage 26 of 54 Next
© 2026 cyber.hendryadrian.com