
Fake Domain Renewal Scam Uses Renovarix Branding to Harvest Personal Data and Solicit Payment Details
Summary
A Renovarix-branded phishing scam uses public WHOIS/RDAP data, fake expiry warnings and countdowns to funnel domain owners through redirect sites that request personal and payment details. Verify renewals directly with your registrar.
Key points
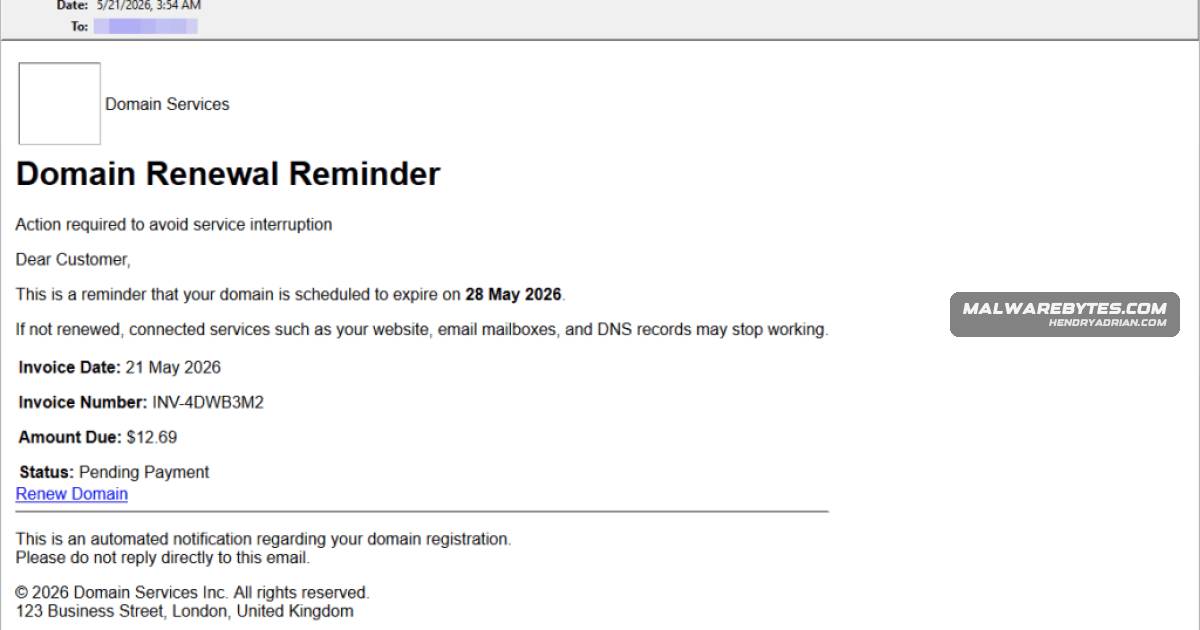
- The scam begins with fake domain-expiry emails, including polished Renovarix-branded notices; some reportedly come from ordinary Gmail addresses.
- Pages use public domain information to appear personalized, while a displayed “Registry ID” is generated locally rather than retrieved from a registry.
- False expiry warnings, countdown timers, low-price offers and pop-ups pressure visitors to act quickly.
- Clicking “Renew Now” does not renew a domain; it redirects visitors through multiple sites that request personal information and then payment details.
- Leftover “HappyPrizes” reviews and automatic population of details from the clicked link point to a recycled scam kit.
- The article advises checking renewals through the registrar directly; people who submitted card details should contact their bank or card issuer and monitor transactions.
- Listed scam-flow domains include renovarix[.]org, xe54ghj[.]com, paysuccessful[.]site, molipy8trk[.]com and topprogressstores[.]online.
Article Details
- Topic
- A fake domain-renewal phishing scam uses urgency and multiple websites to collect victims’ personal and payment information.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | molipy8trk[.]com | Redirector used in the scam flow. |
| DOMAIN | paysuccessful[.]site | Personal-data capture page in the fraudulent checkout flow. |
| DOMAIN | renovarix[.]org | Fake domain-renewal page impersonating a legitimate renewal service. |
| DOMAIN | topprogressstores[.]online | Final offer landing page in the fraudulent renewal flow. |
| DOMAIN | xe54ghj[.]com | Redirector used in the scam flow. |
MITRE ATT&CK
T1036 · MasqueradingThe pages masquerade as a legitimate domain-renewal service using professional-looking branding and registry-style information.T1204.001 · Malicious LinkThe scam flow starts when a victim clicks the renewal link.T1566 · PhishingThe scam begins with fake domain-renewal emails that lure recipients to fraudulent pages.T1583.001 · DomainsThe scam uses multiple registered domains and redirectors to host and route its fraudulent flow.