Windows SeRestorePrivilege Can Enable Three Paths to SYSTEM on a Domain Controller
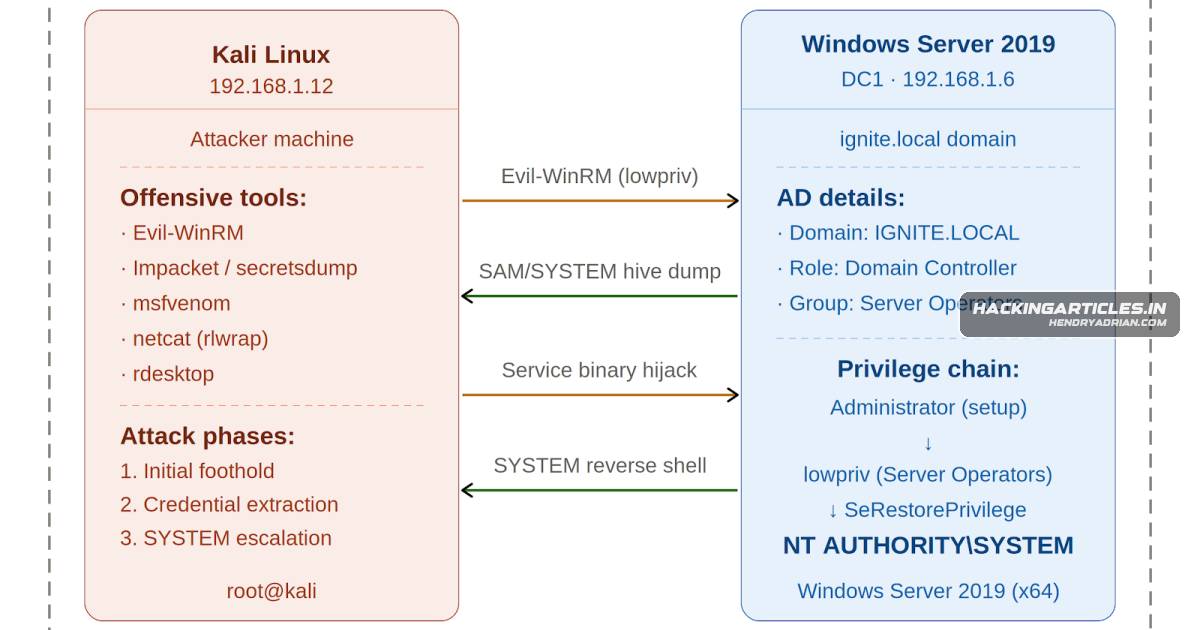
Summary
A lab walkthrough shows how Server Operators membership grants SeRestorePrivilege and SeBackupPrivilege, enabling hash extraction, service hijacking, or Utilman.exe replacement to reach SYSTEM on a Windows Server 2019 Domain Controller.
Key points
- The isolated lab uses a low-privileged domain account added to Server Operators, which receives SeRestorePrivilege and SeBackupPrivilege.
- Using SeBackupPrivilege, the account saves and exfiltrates the SAM and SYSTEM registry hives, then extracts an Administrator NTLM hash for Pass-the-Hash access.
- The walkthrough reconfigures the VMTools service to run a reverse shell as SYSTEM.
- SeRestorePrivilege is used to replace Utilman.exe with cmd.exe, enabling a SYSTEM command prompt from the unauthenticated RDP login screen.
- Recommended defenses include minimizing Server Operators membership, restricting WinRM, monitoring sensitive hive access and privilege use, and applying application control to protect system binaries.
Article Details
- Topic
- Windows privilege escalation through SeRestorePrivilege, including registry hive access, service binary hijacking, and replacement of an accessibility binary.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 192[.]168[.]1[.]12 | Attacker-controlled lab host used to receive the reverse shell callback. |
MITRE ATT&CK
T1003.002 · Security Account ManagerSAM and SYSTEM registry hives are acquired for offline credential-hash extraction.T1543.003 · Windows ServiceA Windows service is reconfigured to execute an attacker-supplied binary.T1546.008 · Accessibility FeaturesUtilman.exe is replaced so a command prompt runs as SYSTEM from the pre-authentication login screen.T1550.002 · Pass the HashThe extracted Administrator hash is used for Pass-the-Hash authentication.
Products
VMware ToolsNext, sc.exe reconfigures the VMware Tools (VMTools) Windows service so that its binPath points to the uploaded shell.Windows Server 2019This article documents three distinct privilege escalation paths that stem from a single SeRestorePrivilege-bearing account against a Windows Server 2019 Domain Controller in an isolated lab environment.
Tools
Evil-WinRMSAM/SYSTEM Hive Exfiltration via Evil-WinRM File TransferImpacketOffline NTLM Hash Extraction via Impacket secretsdumpmsfvenomWindows Reverse TCP Shellcode Generation via msfvenomnetcatIntercepting the SYSTEM-Level Reverse Shell via Netcat ListenerrdesktopRemote Desktop Protocol Session Initiation via rdesktop