Malware INFO Guide Outlines Safer Malware Investigation Workflows
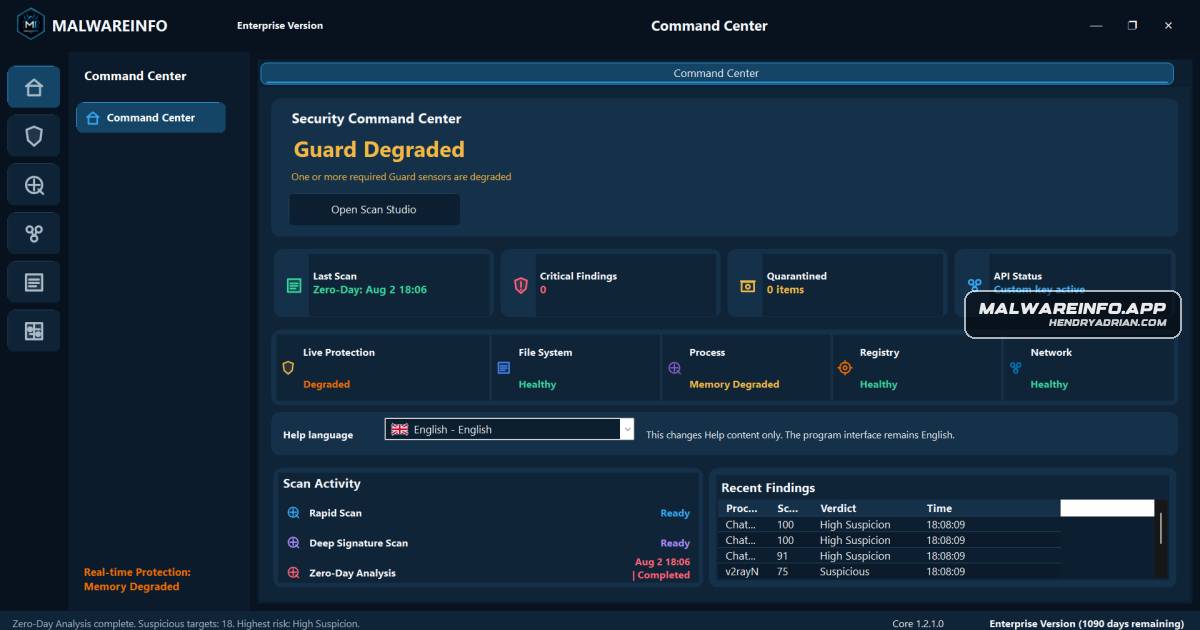
Summary
A Malware INFO guide walks analysts through malware investigation workflows, emphasizing isolated execution, evidence preservation, privacy safeguards and the limits of automated findings.
Key points
- The guide advises running unknown code only in an authorized, disposable isolated VM; bounded execution and cleanup controls are not guarantees of containment or rollback.
- It recommends preserving the original artifact, recording its SHA-256 and case context, and analyzing a controlled working copy.
- Threat Lookup does not silently upload files; complete-file uploads require deliberate user action and organizational approval.
- Scores, scan matches, reputation data and observed activity are evidence for review, not automatic malware verdicts or authority to contain a system.
- Memory captures, trace packages and exports may contain credentials, private data or malicious bytes; the guide calls for access controls and approved sharing channels.
- The guide recommends correlating process, file, registry, network and memory evidence while accounting for gaps in sensor coverage and attribution.
Article Details
- Topic
- Safe investigation workflow and feature guide for Malware INFO