cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · huntress.com

9 Practical Ways to Strengthen Endpoint Security

The article outlines nine endpoint security practices, including asset inventory, prompt patching, MFA, employee training, BYOD controls, least privilege, real-time monitoring, risk assessments, and EDR.
Jul 10, 2024
Detection & Defense · huntress.com

Healthcare Data Loss Can Threaten Patient Safety, Whether Accidental or Intentional

The article explains how lost devices, human error, and malicious insiders can expose healthcare data and put patient care at risk, and outlines safeguards including encryption, access controls, staff training, and monitoring.

Jun 26, 2024
Detection & Defense · threatfabric.com

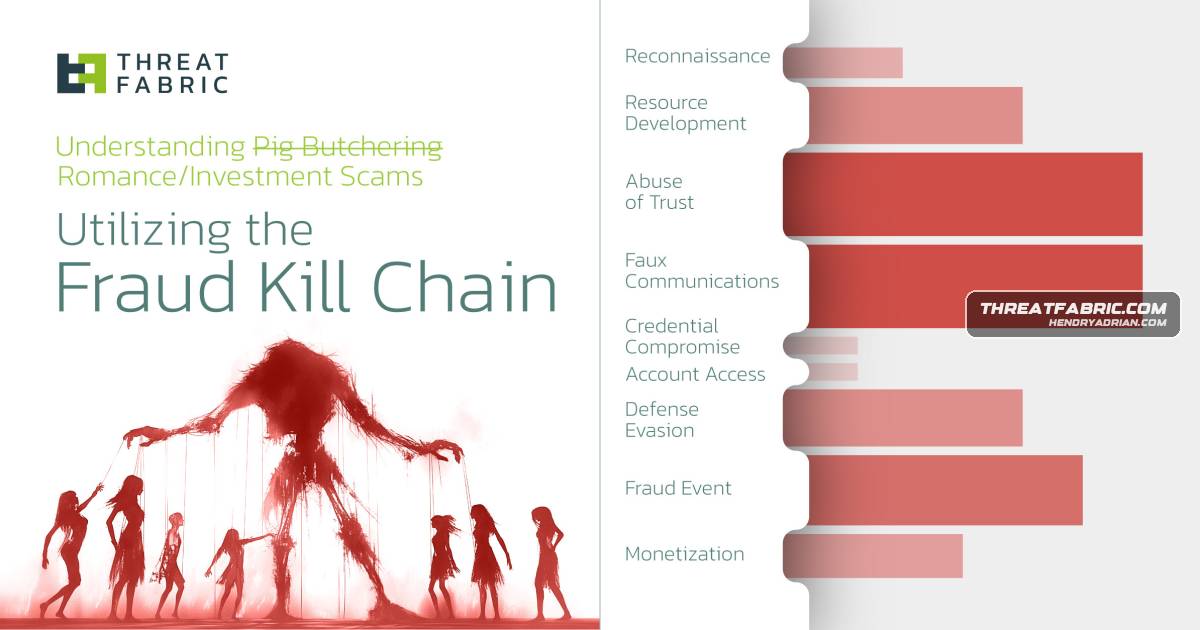
How Anti-Fraud Teams Can Detect Pig-Butchering Scams

The article maps pig-butchering scams to the Fraud Kill Chain and recommends customer-journey visibility, cross-channel monitoring, and behavioral biometrics to help anti-fraud teams identify manipulation and suspicious activity.

Jun 12, 2024
Detection & Defense · huntress.com

Tracking Threat Actors’ Habits Can Improve Early Detection

Huntress explains how recurring attacker behaviors—including reused passwords, endpoint names, Windows utilities, and RMM deployment patterns—can help defenders identify activity earlier and build higher-confidence detections.

May 30, 2024
Detection & Defense · threatfabric.com

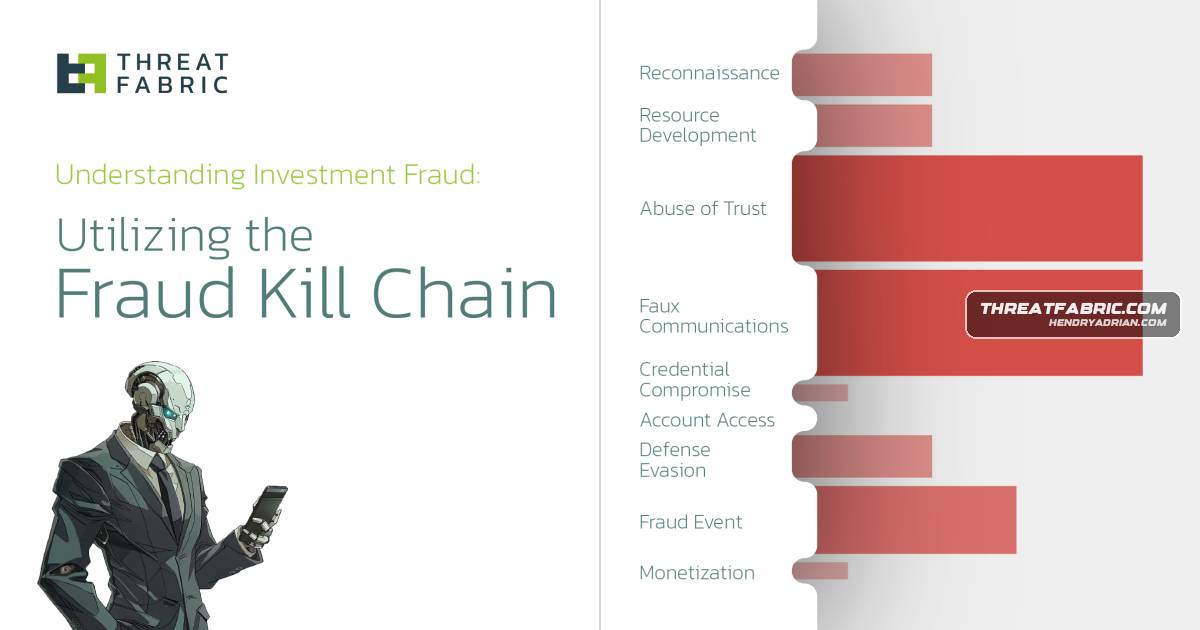
How Anti-Fraud Teams Can Detect Investment Scams Across Web and Mobile

ThreatFabric describes common investment-scam approaches and recommends monitoring full user journeys, using behavioral biometrics, and correlating device and behavioral risk across web and mobile channels.

Apr 24, 2024
Detection & Defense · hunt.io

How to Detect RedGuard C2 Redirectors Using TLS and HTTP Indicators

A practical guide to detecting RedGuard C2 redirectors using TLS certificate details, HTTP 307 responses, and redirect locations, with a query designed to catch variants that change default settings.

Apr 2, 2024
Detection & Defense · threatfabric.com

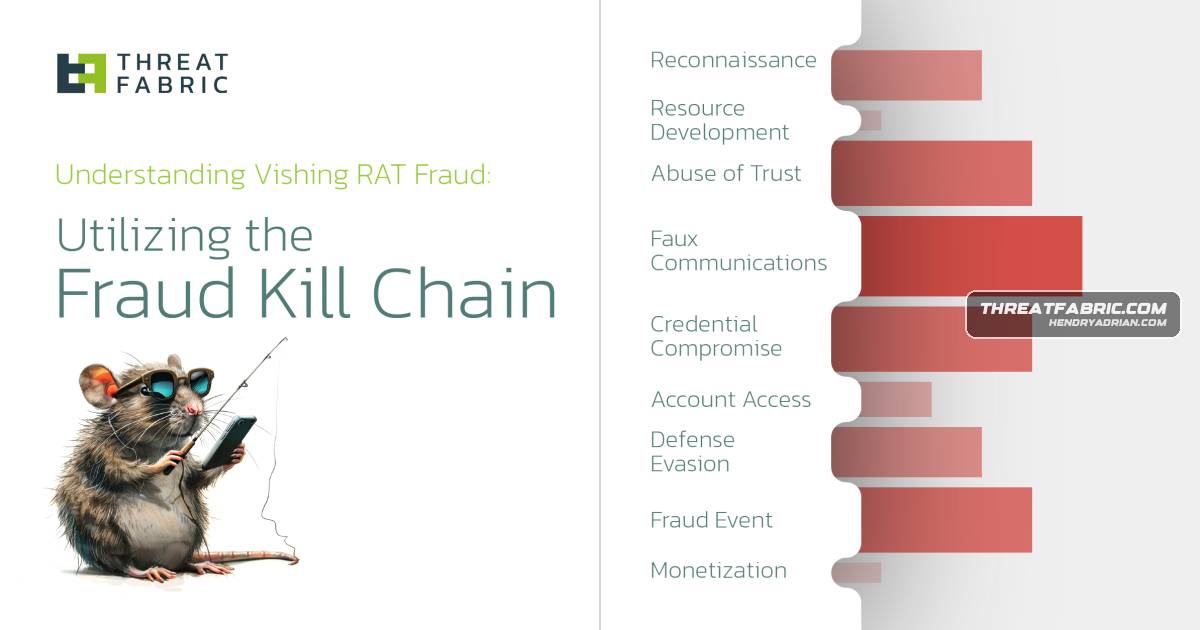
How Anti-Fraud Teams Can Detect Vishing Scams Using Remote-Access Tools

The article outlines how scammers use phone impersonation to persuade victims to install remote-access tools, then recommends mobile and device-risk visibility, behavioral biometrics, and cross-channel signal correlation to improve detection.

Mar 26, 2024
Detection & Defense · wiz.io

Wiz Introduces NamespaceHound to Assess Kubernetes Tenant-Isolation Risks

Wiz’s NamespaceHound analyzes Kubernetes clusters for potential cross-namespace access paths and anonymous access. The article also outlines practical controls for strengthening tenant isolation.

Mar 13, 2024
Detection & Defense · hunt.io

Hunt IO Details Techniques for Detecting Exposed PrismX Deployments

Hunt IO demonstrates how to identify PrismX login pages using certificate, HTTP-header, and HTML fingerprints, and reports finding servers also associated with Cobalt Strike.

Mar 12, 2024
Detection & Defense · team-cymru.com

Team Cymru Outlines Octo Malware Risks and Defensive Measures

Team Cymru says Octo (also known as Coper) targets Android devices and poses risks including credential theft, fraud, and data loss. It recommends stronger endpoint security, non-SMS MFA, awareness training, and monitoring for Octo activity.

Mar 9, 2024
Detection & Defense · huntress.com

How to Detect Impossible Travel in Microsoft 365 Sign-Ins

Huntress explains a six-step approach to detecting impossible travel in Microsoft 365 sign-ins and reducing false positives from legitimate activity, high event volumes, and inaccurate geolocation data.

Mar 7, 2024
Detection & Defense · threatfabric.com

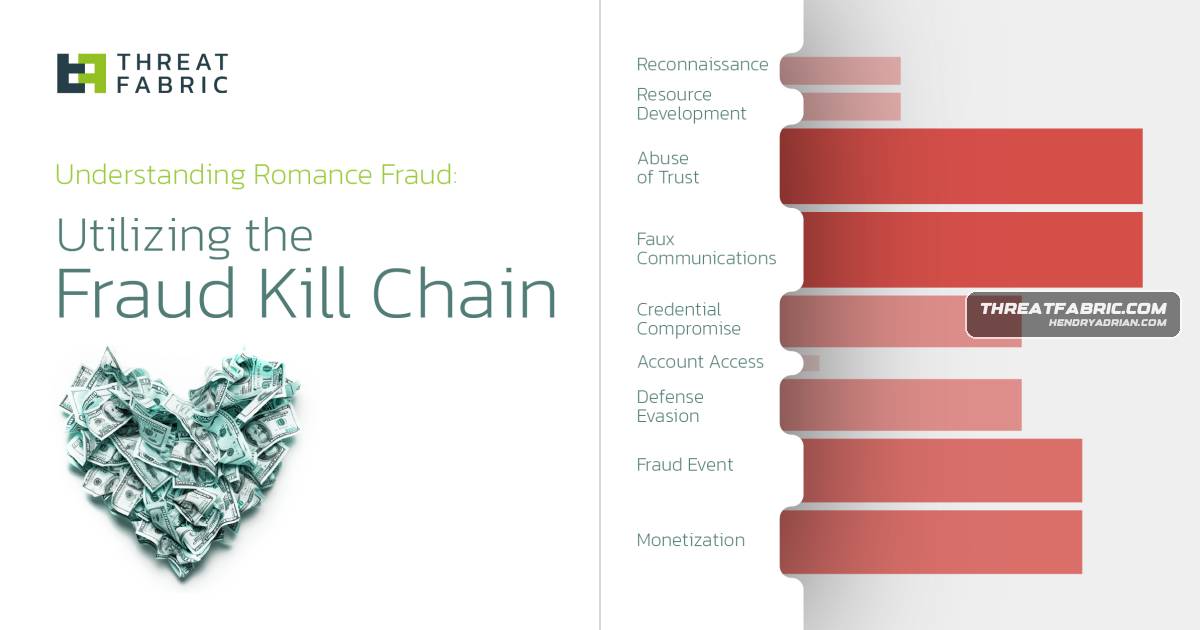
ThreatFabric Outlines Detection Gaps in Romance Scam Prevention

ThreatFabric describes romance scam tactics and recommends customer-journey visibility, monitoring across web and mobile channels, and behavioral biometrics to help anti-fraud teams detect social engineering.

Mar 6, 2024
Detection & Defense · threatfabric.com

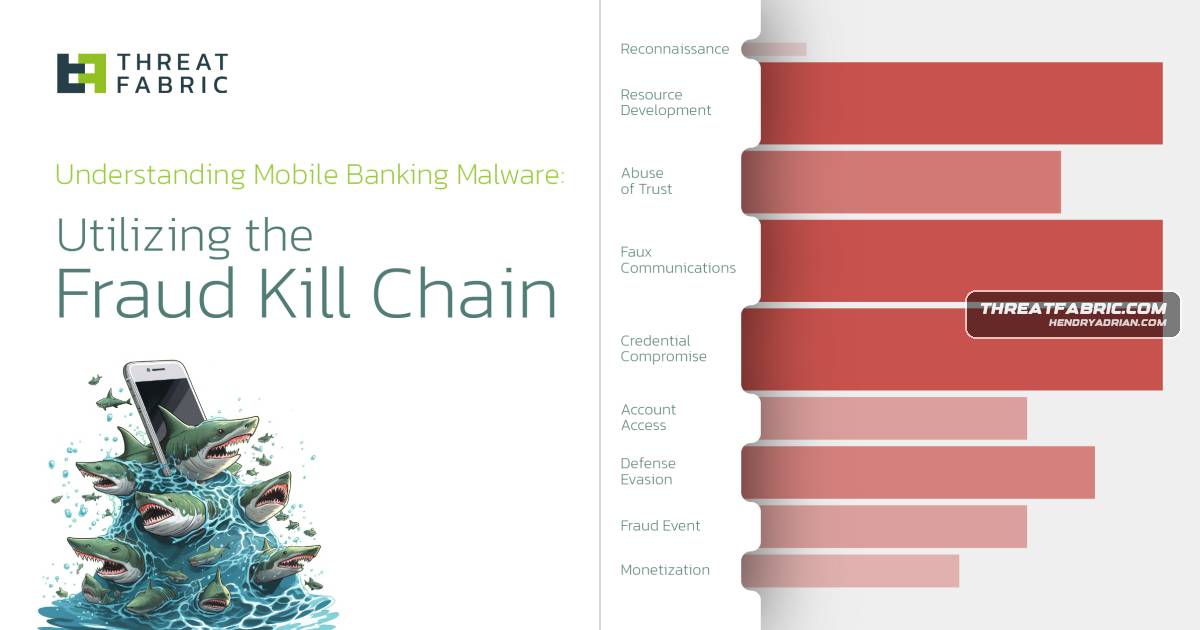
ThreatFabric Outlines Detection Gaps for Mobile Banking Malware

ThreatFabric says it spotted 75 mobile banking malware families in 2023, 26 with device-takeover capabilities. It urges anti-fraud teams to assess mobile, user-session, and device-risk visibility using the Fraud Kill Chain.

Feb 27, 2024
Detection & Defense · huntress.com

How to Check for ScreenConnect Compromise and Respond

Huntress outlines indicators of possible ScreenConnect compromise, affected on-premises hosts, and response steps. It urges users to isolate affected servers, reset exposed credentials, and patch to version 23.9.8 or newer.

Feb 23, 2024
Detection & Defense · huntress.com

Huntress Shares Detection Guidance for ConnectWise ScreenConnect Authentication Bypass

Huntress describes artifacts and Windows auditing that may help investigate exploitation of ConnectWise ScreenConnect’s CVE-2024-1709 authentication bypass, while warning that the available evidence may not definitively establish exploitation.

Feb 20, 2024
Detection & Defense · wiz.io

Wiz Analyzes Security Risks and Defenses for New Amazon EKS Identity Features

Wiz examines security implications of Amazon EKS access management and pod identity, recommending permission audits, token protections, safer service-account practices, and expanded detection using both Kubernetes and AWS CloudTrail data.

Feb 6, 2024
Detection & Defense · hunt.io

How Defenders Can Identify Malicious Command-and-Control Infrastructure

Hunt.io explains how defenders can identify malicious C2 servers using internet scanning and indicators such as TLS certificates, HTTP responses, protocol behavior, and code-derived patterns.

Jan 24, 2024
Detection & Defense · hunt.io

Hunt.io Details C2 Infrastructure Tracking Methods and Introduces Threat Feed

Hunt.io describes methods for identifying malicious C2 servers and introduces a JSON feed that uses internet scanning, focused monitoring, validation, and regularly updated signatures to provide near-real-time infrastructure intelligence.

Jan 15, 2024
Detection & Defense · huntress.com

Huntress Urges Healthcare Providers to Strengthen Layered Cyber Defenses

Huntress describes cyber threats facing healthcare providers and recommends layered defenses, broader visibility, staff training, risk assessments, and tested incident response plans.

Jan 12, 2024
Detection & Defense · huntress.com

Huntress Details Microsoft 365 Initial-Access Detection Using Login Enrichment

Huntress describes combining IP intelligence, user location patterns, and conditional-access events to identify suspicious Microsoft 365 logins, while noting that detections require investigation and impossible-travel detection remains challenging.

Dec 27, 2023
Detection & Defense · wiz.io

How to Enforce Safer Security Defaults Across AWS Accounts

The article provides AWS hardening guidance, including SCPs and configuration steps to restrict public exposure, disable risky features, enforce IMDSv2 and EBS encryption, and limit network and administrative access.

Dec 21, 2023
Detection & Defense · wiz.io

How eBPF Can Detect Kubernetes Container Escapes and Runtime Attacks

A walkthrough shows how eBPF-based runtime monitoring can surface Kubernetes attack activity, including privileged-pod escapes, reverse shells, pod creation, and access to /etc/shadow, alongside prevention measures.

Nov 19, 2023
Detection & Defense · hunt.io

How Hunt Uses Predictive Scanning to Find Services on Non-Standard Ports

Hunt describes using GPS predictive scanning to identify services on non-standard ports, then investigate them for malware. The approach found a short-lived Cobalt Strike cluster on ports 1788 and 1799 and preserved its infrastructure history.

Oct 25, 2023
Detection & Defense · hunt.io

Hunt.io Guide Shows How to Detect Gophish Phishing Infrastructure

Hunt.io describes detecting Gophish infrastructure using HTTP fingerprints such as _gorilla_csrf cookies and /login?next= URL patterns, alongside aggregated threat data and machine learning.

Oct 12, 2023
PreviousPage 24 of 27 Next
© 2026 cyber.hendryadrian.com