Hijacked Documentation Placeholder Domain Delivers ClickFix Lure to Windows Users
Summary
Manifold Security says third-party[.]com has served a ClickFix lure since at least June 2026, targeting Windows users with a clipboard-poisoning command. The domain appears in over 1,700 GitHub repositories; researchers found 13 other abused placeholder domains.
Key points
- Windows visitors to third-party[.]com saw a fake Cloudflare check that poisoned the clipboard with a command designed to run a remote PowerShell payload.
- The domain has reportedly served the lure since at least June 2026; macOS visitors instead saw an unsupported-browser message or other content.
- Manifold Security found the non-reserved domain referenced in over 1,700 public GitHub repositories, including AI agent skill and MCP-server documentation.
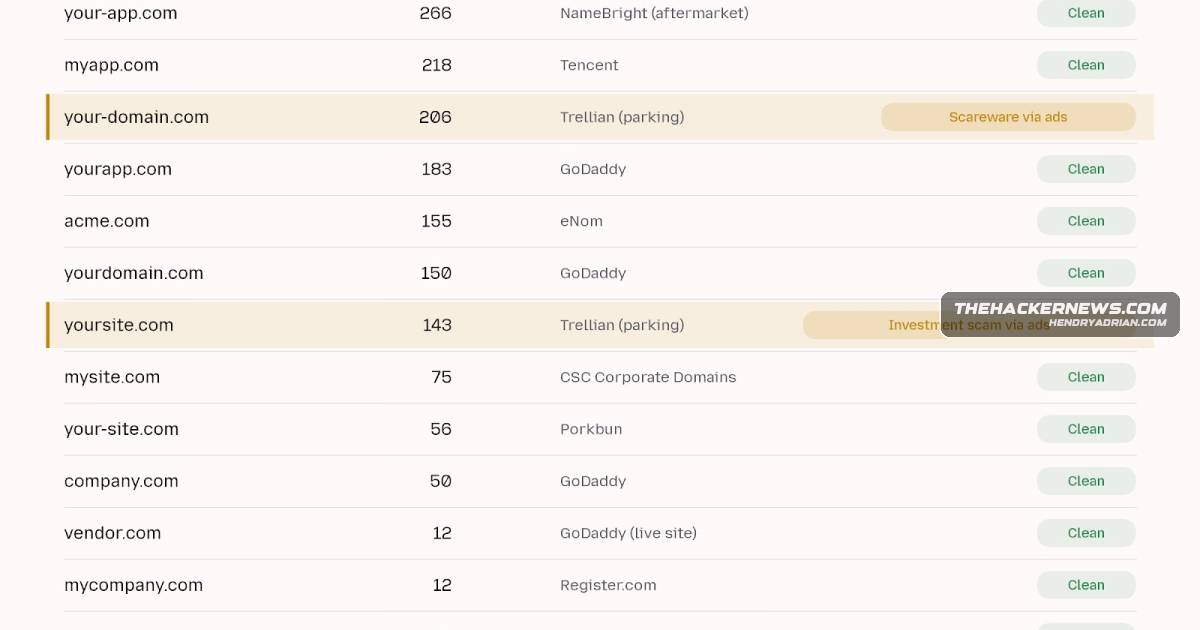
- Researchers identified 13 additional non-reserved placeholder domains; yoursite[.]com and your-domain[.]com reportedly showed investment-fraud and scareware content to macOS visitors.
- The researchers recommend auditing documentation and using reserved placeholders such as example[.]com rather than plausible domains not controlled by the organization.
Article Details
- Event Type
- Hijacked placeholder domain used to deliver a ClickFix lure and other scams
- Impact
- Windows visitors to third-party[.]com were shown a fake Cloudflare check that poisoned the clipboard with a command designed to run a remote PowerShell payload. macOS visitors saw a fake unsupported-browser message or scam content. Two other placeholder domains, your-domain[.]com and yoursite[.]com, served scareware or investment-fraud content to macOS visitors. The article reports that third-party[.]com is referenced in over 1,700 public repositories.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | third-party[.]com | Reportedly hijacked and serving a ClickFix lure that poisons Windows users’ clipboards with a command designed to run a remote PowerShell payload. |
| DOMAIN | your-domain[.]com | Reportedly served macOS visitors fake security alerts and a counterfeit McAfee renewal offer. |
| DOMAIN | yoursite[.]com | Reportedly served macOS visitors a counterfeit ZDF article advertising an investment scheme. |
MITRE ATT&CK
People
Products
macOSmacOS users saw a fake unsupported-browser message or scam content instead.Microsoft WindowsThe third-party[.]com domain, long used as a documentation placeholder, has been hijacked to deliver a ClickFix lure to Windows users while showing benign content to others.PowerShellThe pasted command was designed to run a remote PowerShell payload.