
Versioned Gmail Addresses Link Four Malicious npm Packages to Acevatex
Summary
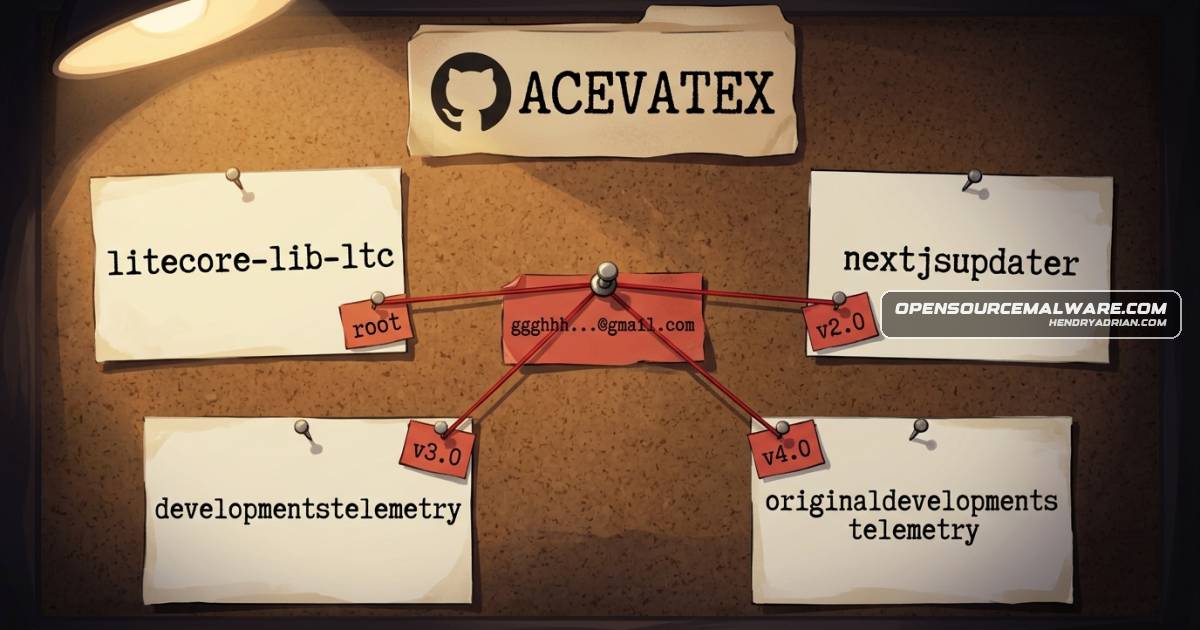
An investigation links four malicious npm packages and earlier GitHub malware to operator Acevatex through versioned Gmail addresses, detailing credential theft, a loader chain delivering PureRAT, and defensive steps. The authors report no identified victims.
Key points
- Four npm accounts used variants of the same Gmail address root. The three August loader packages also share code, a GitHub URL, and closely timed publication; the email root is the only direct link between litecore-lib-ltc and the other activity.
- From version 1.9.10, litecore-lib-ltc sent each newly created Litecoin wallet’s private key to a Discord webhook. The investigation says it found no evidence that anyone was affected.
- Three August 2026 npm packages formed a loader chain that downloaded an HTA, launched it with mshta, and ultimately delivered PureRAT. The chain used WMI, process injection, and persistence through scheduled tasks.
- A modified Exodus wallet archive sent plaintext passphrases and a machine fingerprint to a Discord webhook. The article says it found no evidence showing how the patcher would reach a victim’s machine.
- Other activity included a cookie-stealing SVG and the npm loader packages. The authors connect the activity to Acevatex while distinguishing confirmed account links from weaker identity leads.
- At publication, litecore-lib-ltc and developmentstelemetry remained available despite OSV records. The article advises treating keys or credentials exposed by affected packages as compromised and provides host and network indicators for investigation.
Article Details
- Attack Vectors
- From version 1.9.10, the litecore-lib-ltc npm package sends each newly created Litecoin wallet's private key to a Discord webhook.
- The image.svg artifact embeds JavaScript that reads document.cookie and posts the cookie value to a Discord webhook; whether it steals cookies depends on where the SVG is rendered and browser behavior.
- The npm loader packages download an HTA from GitHub and run it with mshta. The HTA downloads additional stages with curl.exe and launches a stage through WMI.
- The loader chain uses an obfuscated batch script, encrypted payloads, process injection into explorer.exe, and a .NET loader to load PureRAT.
- The Exodus patcher modifies app.asar to send the wallet passphrase in plaintext, together with a machine SHA-256 fingerprint, to a Discord webhook.
- Defensive Notes
- For litecore-lib-ltc version 1.9.10 or later, treat private keys for wallets created with the library as stolen and move funds to a new wallet generated on a clean machine.
- If one of the three loader packages ran on Windows, treat the machine as compromised; rotate browser-saved passwords, re-enroll authenticator apps, move wallet funds, and log out Telegram Desktop sessions.
- Check for the scheduled task fMug, the hidden C:\ProgramData\IntelDriver\ folder, and the hidden %USERPROFILE%\Downloads\HslPrompt.exe artifact.
- Check network connections to 79.110.49.129 on port 8080 and 217.60.77.60 on ports 56001–56003.
- Compare Exodus resources\app.asar with a clean copy. If modified and the passphrase was entered, treat it as compromised and move funds using a new seed generated on a clean device.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
ggghhh1122334455667788@gmail[.]com | Email root used by the npm account associated with the malicious litecore-lib-ltc package. | |
ggghhh1122334455667788v2[.]0@gmail[.]com | Versioned email address associated with the npm account that published the malicious nextjsupdater package. | |
ggghhh1122334455667788v3[.]0@gmail[.]com | Versioned email address associated with the npm account that published the malicious developmentstelemetry package. | |
ggghhh1122334455667788v4[.]0@gmail[.]com | Versioned email address associated with the npm account that published the malicious originaldevelopmentstelemetry package. | |
| IPV4 | 217[.]60[.]77[.]60 | PureRAT command-and-control server, reported open on ports 56001–56003. |
| IPV4 | 79[.]110[.]49[.]129 | Payload server reported to serve the HTA chain's next-stage files on port 8080. |
| SHA256 | 2e14391fb40b601c91a73c823c574d1c286bf4dc359184c33d42384eb3b40bcd | SHA-256 hash of image.svg, identified as the cookie-stealing SVG artifact. |
| SHA256 | 2f1b131b90f2231bd90caf0c8241e82fe968ff1f651a4061376bc960bc882d0e | SHA-256 hash of Donut shellcode decoded from HHLzY.png in the loader chain. |
| SHA256 | 71b6879c6b18901c9282fa56a84cc5efd6fe8ace17878e6caf6a6f99c254ff21 | SHA-256 hash of update.hta, identified as the HTA loader. |
| SHA256 | 7cf480b860e23e003bbcb544805e8e1d39846ba05f26174b21747a5481b59ee5 | SHA-256 hash of TestSwapper.exe, the tool used with the Exodus passphrase patcher. |
| SHA256 | 84815f65986c2a9e4d8db836dcde6c328f14f31cd219834e231ce0f04f5fa9d6 | SHA-256 hash of the PureRAT client DLL. |
| SHA256 | a64819733a85f798b5ebbfabcd94da6fa04c7e669f9a41a67aeaaa7e63337cfb | SHA-256 hash of purelast.exe, the PyInstaller first-stage payload. |
| SHA256 | bfbd808732407090d6cf58a7c5462cb154a0978675c0f0744cc9a536724bc353 | SHA-256 hash of the Exodus patcher source identified as replaces. |
| SHA256 | c5b9257e62d7844f09744bf37fd6f705d0e4069da6cc840652061f16bd2cbfb3 | SHA-256 hash of Loader.exe, the .NET loader that decrypts and loads PureRAT. |
| SHA256 | d7fe3fe6cd6d89b0575d95fa223669ce2551b1750b7bd81851d5ea52601116e2 | SHA-256 hash of the decrypted PowerShell injector stage. |
| URL | hxxp[:]//79[.]110[.]49[.]129:8080/ayan/p5wPgZnWF3LGjsEbYryf[.]exe | Payload URL for the executable saved by the HTA as o.exe. |
| URL | hxxp[:]//79[.]110[.]49[.]129:8080/ayan/QFOltCgLKA0nGRcz6YmJ[.]dat | Payload URL for the data file saved by the HTA as ov.dat. |
| URL | hxxp[:]//79[.]110[.]49[.]129:8080/ayan/RuLnbcv9dlmEX7F6ez10[.]exe | Payload URL for the executable saved by the HTA as purelast.exe. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/Acevatex/Testprogram/main/update[.]hta | Current GitHub-hosted name for the HTA loader used in the malicious package chain. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/Acevatex/Testprogram/main/updater[.]hta | GitHub-hosted HTA loader URL hardcoded in the malicious npm packages. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe batch script hides commands behind 1,778 variables and Greek homoglyphs, and the chain includes encrypted payloads.T1036.003 · Rename Legitimate UtilitiesThe chain copies powershell.exe to a hidden file named HslPrompt.exe.T1047 · Windows Management InstrumentationThe HTA launches a downloaded stage through WMI.T1053.005 · Scheduled TaskPersistence includes a scheduled task named fMug and a PureRAT task that relaunches every five minutes.T1055 · Process InjectionThe AES-encrypted PowerShell injector injects the next stage into explorer.exe.T1059.001 · PowerShellA copied powershell.exe, renamed HslPrompt.exe, is used for subsequent stages.T1059.003 · Windows Command ShellThe loader uses an obfuscated batch script to run commands and stage files.T1059.005 · Visual BasicThe fMug scheduled task runs wscript.exe against fMug.vbs.T1105 · Ingress Tool TransferThe HTA uses curl.exe to download subsequent payload stages from the payload server.T1140 · Deobfuscate/Decode Files or InformationThe loader extracts base64 payloads and decrypts stages using AES and TripleDES.T1218.005 · MshtaThe npm loader runs the downloaded HTA with mshta.T1539 · Steal Web Session CookieThe SVG's embedded JavaScript reads document.cookie before sending the value to a Discord webhook.T1562.001 · Disable or Modify ToolsDonut shellcode patches AMSI, ETW, and WLDP.T1564.001 · Hidden Files and DirectoriesThe loader hides HslPrompt.exe and uses a hidden IntelDriver directory.T1567.004 · Exfiltration Over WebhookThe cookie stealer, Litecoin key stealer, and Exodus patcher send stolen data to Discord webhooks.
People
Chi TranAnalyzed nextjsupdater and documented the loader chain and payload infrastructure.Sam LindoresThe name appears in the build path recorded in RunTest.exe. The article assesses with high confidence that the build machine used this identity but does not treat it as a verified identity or confirm who controlled the machine.
Threat Actors
Malware
Vendors
DiscordFrom version 1.9.10 it sends every new wallet's private key to a Discord webhook.GitHub"Acevatex" is the threat actor behind a burst of three malicious npm packages from August 2026. They're named that way because it's their consistent handle across GitHub and numerous online platforms.npm"Acevatex" is the threat actor behind a burst of three malicious npm packages from August 2026. They're named that way because it's their consistent handle across GitHub and numerous online platforms.
Products
ExodusThe Exodus patcher, August 4 to 6Microsoft WindowsThe HTA: Hides its window, creates %TEMP%\WinSAT and uses Windows' own curl.exe to fetch the next stage.PowerShellIt copies itself to C:\ProgramData\IntelDriver\LwWN.cmd and copies powershell.exe to a hidden HslPrompt.exe, which it uses for everything that follows.